
 United States Governance, Risk and Compliance Platform Market | 2026-2036
United States Governance, Risk and Compliance Platform Market Size, Share, and Industry Trends Forecast 2026-2036
United States Governance, Risk and Compliance Platform Market Intelligence
Cloud-native architecture is reshaping how GRC platforms are built and delivered across the United States. IBM leverages its hybrid cloud infrastructure to anchor enterprise-grade compliance workflows in regulated industries. Oracle sustains competitive positioning through deep integration with its database and ERP ecosystems. ServiceNow differentiates by extending IT service management capabilities into operational risk and audit orchestration.
United States Governance, Risk and Compliance Platforms are integrated software systems that automate policy management, control testing, incident tracking, and regulatory reporting through configurable workflows and real-time data connectors. These platforms aggregate risk signals across financial, operational, and cyber domains to enable continuous compliance monitoring and board-level accountability. Cloud-based deployment now leads solution uptake as enterprises prioritize scalability and remote accessibility over capital-intensive on-premises installations. Financial compliance and data privacy modules represent the fastest-expanding segments, reflecting SEC enforcement priorities and the patchwork of state consumer protection laws. Audit management functionality remains a mature margin pool, with established vendors competing on pre-configured control libraries and industry-specific templates.
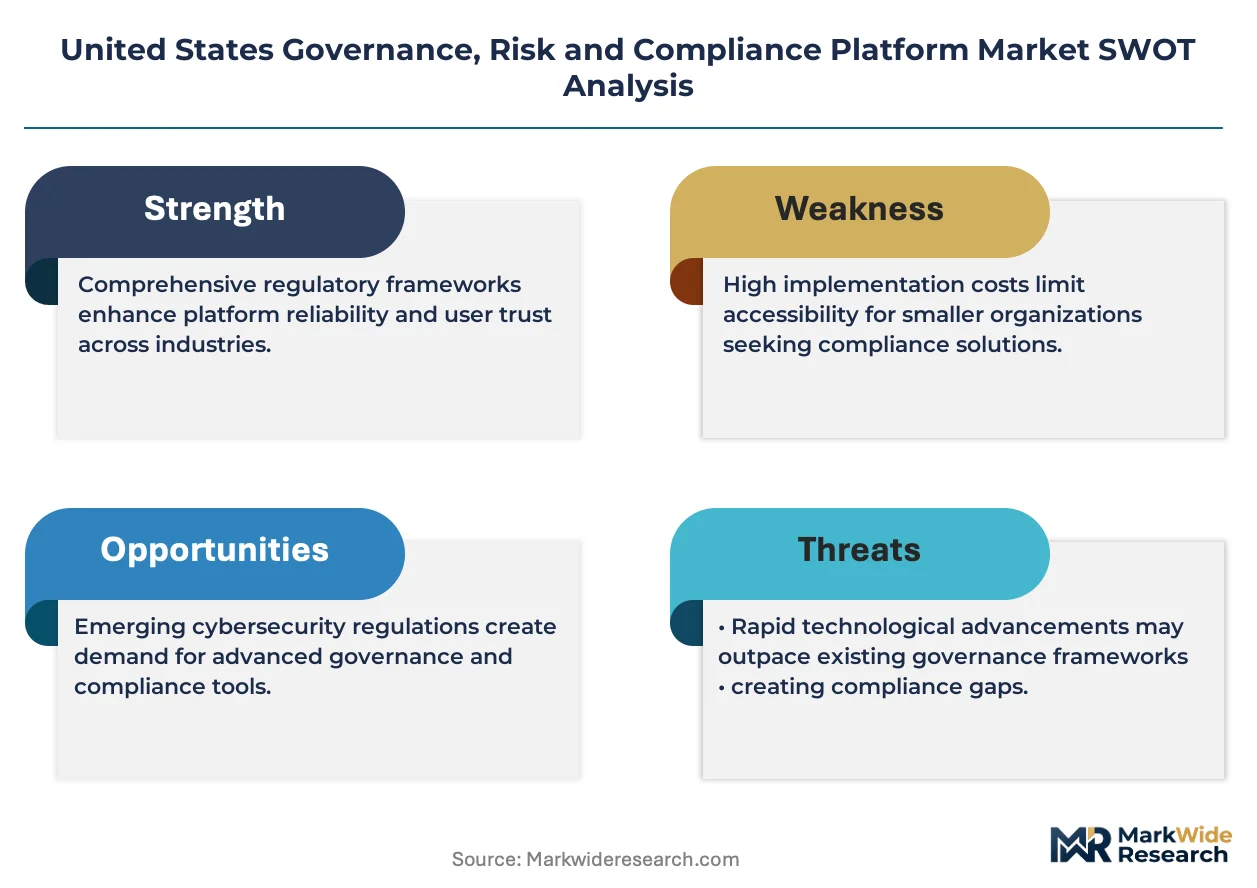
The SEC, state attorneys general offices, and HIPAA enforcement by the Department of Health and Human Services collectively shape product requirements and procurement urgency across the United States market. NIST cybersecurity frameworks and SOX mandates further standardize control architectures that platforms must support to maintain market access. Stakeholders should monitor how fragmented state privacy legislation consolidates or diverges, as this trajectory determines whether unified or modular platform strategies prevail.
Market Dynamics
Cloud-native GRC architectures are compressing deployment cycles from quarters to weeks, forcing legacy on-premise vendors to re-platform or lose enterprise accounts to API-first competitors.
Growth Catalysts
- SEC Climate Disclosure Mandates:Public companies must now integrate climate risk into financial filings, driving demand for ESG data aggregation modules that automate carbon accounting and scenario modeling.
- Financial Services:Banks and insurers face overlapping state privacy laws plus federal banking regulations, compelling consolidation of siloed compliance tools into unified governance platforms.
- API Ecosystems:Pre-built connectors to SAP, Salesforce, and Workday slash implementation timelines, accelerating procurement decisions among mid-market enterprises previously priced out of enterprise GRC.
Market Restraints
- Implementation Complexity:Multi-module deployments require 12-18 month timelines with dedicated change management, freezing budget allocation during economic uncertainty.
- Specialized Talent Scarcity:Shortage of professionals combining regulatory expertise with cloud architecture skills inflates professional services costs and extends project risk.
- Fragmented State Privacy Regimes:California's CPRA, Virginia's VCDPA, and Colorado's CPA create conflicting compliance obligations that unified platforms struggle to automate without costly customization.
Strategic Opportunities
- Mid-Market Penetration:Companies with 500-5,000 employees remain underserved by enterprise-focused vendors, presenting white space for modular, per-user pricing models.
- Healthcare Vertical:HIPAA enforcement by the Department of Health and Human Services intensifies audit frequency, creating demand for automated control testing and breach response workflows.
- AI Governance Modules:NIST AI Risk Management Framework adoption is creating new product categories for algorithmic bias detection and model inventory management.
Industry Challenges
- Legacy System Integration:Mainframe-based core banking and insurance policy administration systems resist API connectivity, forcing expensive middleware development.
- Continuous Control Monitoring:Real-time data ingestion from hundreds of enterprise systems strains platform architecture and drives up infrastructure costs.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | United States Governance, Risk and Compliance Platform Market |
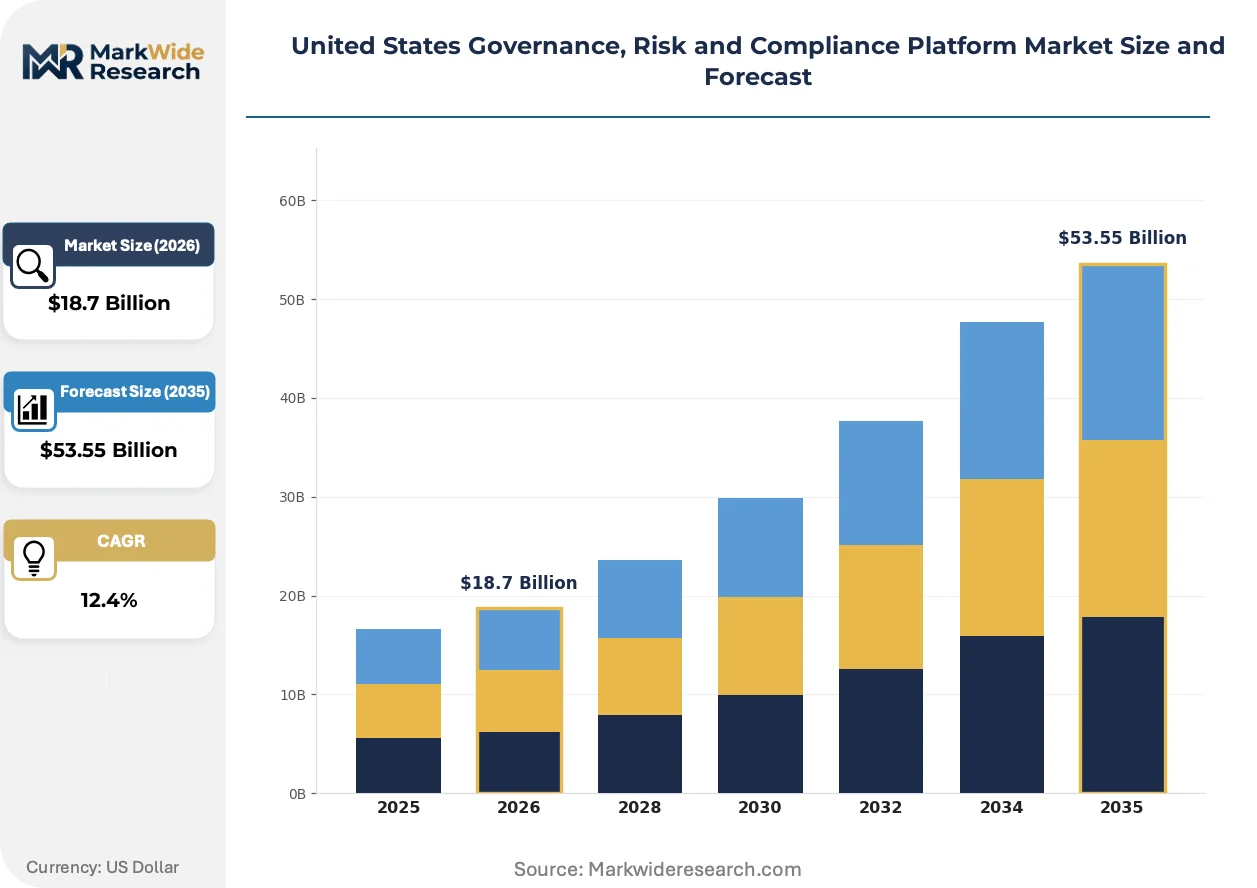
| Market Size in 2026 | $18.7 Billion |
| Market Size in 2035 | $53.55 Billion |
| CAGR (2026 – 2036) | 12.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Financial Services, Healthcare, Manufacturing, Energy Compliance Type: Financial Compliance, Data Privacy, Risk Management, Security Standards Solution Type: Monitoring Tools, Reporting Software, Risk Assessment, Audit Management |
| Companies Covered | IBM, Oracle, MetricStream, NAVEX Global, LogicManager, AuditBoard, Archer, ServiceNow, RSA Security, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
United States Governance, Risk and Compliance Platform Market Strategic Shifts & Innovations
Artificial intelligence is rewriting how risk signals are detected and prioritized, shifting GRC platforms from reactive documentation tools to predictive orchestration engines.
Continuous control monitoring technology is virtualizing the traditional audit cycle. Embedded sensors within ERP and CRM systems stream transaction data directly into risk engines, eliminating quarterly sampling. Fortune 500 internal audit functions are adopting these capabilities fastest, compressing control testing from weeks to hours while redirecting staff toward exception investigation rather than routine verification.
The SEC's cybersecurity disclosure rules finalized in 2023 mandate material incident reporting within four business days. Public companies must now maintain real-time breach assessment capabilities, accelerating procurement of integrated incident response modules. Financial services and critical infrastructure operators face the steepest compliance cliffs, with regional banks racing to close gaps before examination cycles intensify.
Subscription pricing models now dominate procurement decisions, displacing perpetual licenses with usage-based tiers tied to employee count or transaction volume. Mid-market buyers in Texas and Florida are driving this shift, preferring operational expenditure treatment and rapid scaling without capital committee approvals. Vendors responding with true consumption metering capture disproportionate share in these high-growth state markets.
United States Governance, Risk and Compliance Platform Market Segmentation
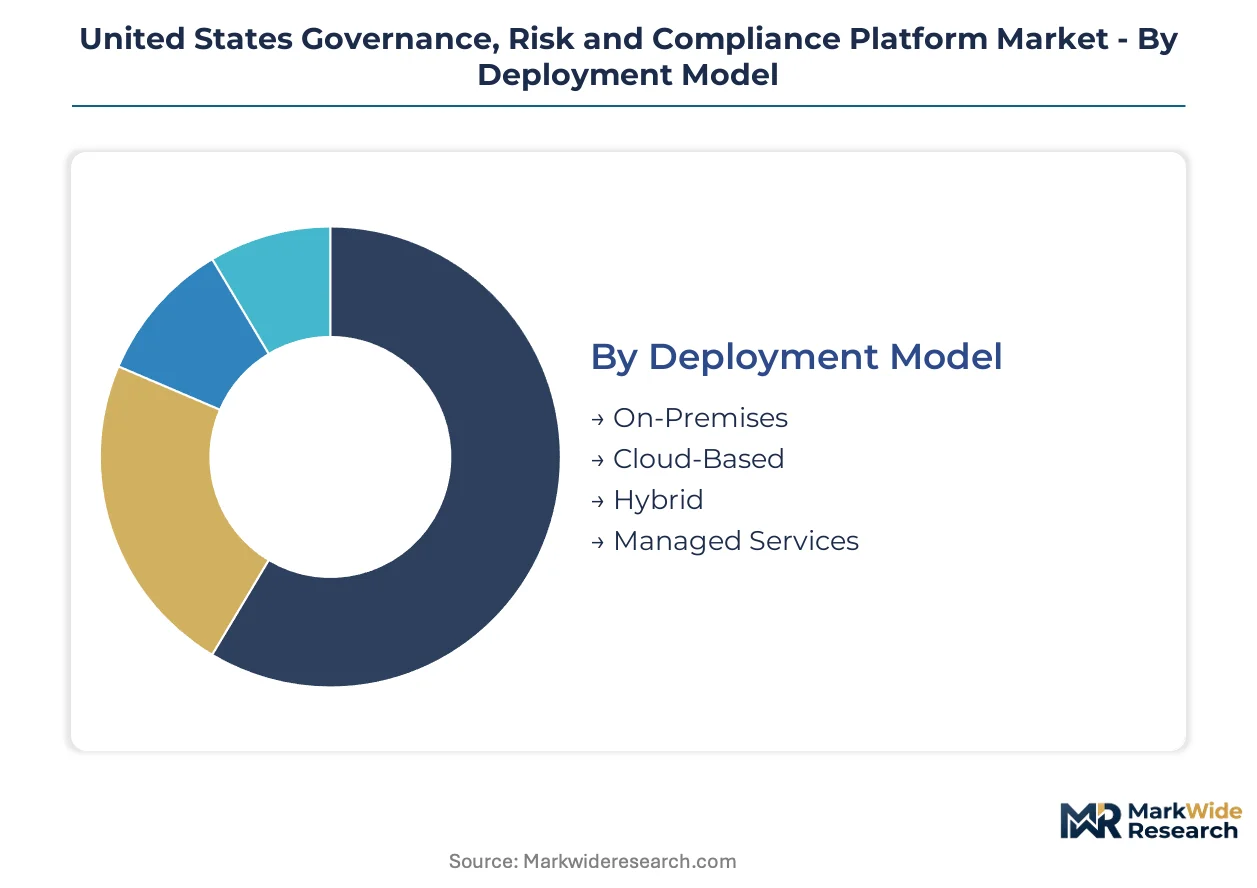
Platform segmentation reveals divergent deployment strategies across enterprise maturity levels. Procurement patterns cluster around regulatory exposure intensity and existing IT infrastructure commitments.
Deployment Model:
Mature on-premise installations coexist with rapidly maturing cloud-native alternatives across the United States.
- Cloud-Based:Multi-tenant architectures with elastic compute provisioning dominate new procurement in California and New York. Banks and insurers prioritize remote accessibility and automatic patch deployment to satisfy SEC examination timelines.
- Hybrid:Split configurations segregate sensitive audit trails on-premise while routing operational workflows through cloud instances. Energy sector operators favor this model to isolate SCADA-adjacent systems from external connectivity.
- On-Premises:Perpetual-license installations persist among defense contractors and certain HIPAA-covered entities with air-gapped security mandates.
- Managed Services:Outsourced platform administration with bundled compliance expertise appeals to mid-market manufacturers lacking dedicated GRC staff.
Cloud-Based retains volume leadership; Managed Services holds the steepest expansion curve.
End User:
Regulatory density directly shapes procurement sophistication and module configuration requirements.
- Financial Services:Tier-1 banks deploy integrated SOX, BSA/AML, and stress-testing modules with real-time regulatory reporting. State-chartered institutions in Texas and Florida accelerate adoption to preempt federal examination findings.
- Healthcare:Hospital systems and payers automate HIPAA security rule compliance and breach notification workflows. OCR enforcement intensification drives replacement of manual spreadsheet tracking.
- Manufacturing:Discrete and process manufacturers implement environmental compliance and supply chain risk modules to satisfy EPA reporting and CTPAT security criteria.
- Energy:Utilities and oil-and-gas operators integrate NERC CIP cybersecurity standards with enterprise risk frameworks. FERC audit preparation consumes substantial professional services capacity.
Financial Services dominates absolute spend; Healthcare delivers the steepest expansion trajectory.
Compliance Type:
Module demand correlates with enforcement visibility and penalty severity across federal and state jurisdictions.
- Financial Compliance:SOX internal control documentation, SEC disclosure management, and Basel capital adequacy tracking form the core revenue base. Public company mandatory adoption sustains pricing power.
- Data Privacy:CPRA automated consumer rights fulfillment and multi-state consent management emerge as critical differentiators. Conflicting Virginia VCDPA and Colorado CPA requirements strain unified platform architectures.
- Risk Management:Enterprise risk registers with quantitative scenario modeling spread from financial services into industrial conglomerates. Board-level risk appetite dashboards drive C-suite procurement sponsorship.
- Security Standards:NIST CSF alignment and ISO 27001 certification support attract technology sector buyers with vendor security questionnaire obligations.
Financial Compliance anchors revenue concentration; Data Privacy climbs the fastest.
Solution Type:
Functional modules span operational execution through strategic oversight with varying integration depth.
- Audit Management:Workpaper automation, control testing scheduling, and finding remediation tracking represent the most penetrated category. Internal audit department budgets fund majority of initial platform acquisitions.
- Monitoring Tools:Continuous control monitoring with ERP-embedded sensors virtualizes traditional sample-based testing. Fortune 500 deployment compresses testing cycles from quarters to hours.
- Risk Assessment:Heat mapping, KRIs, and scenario analysis modules consolidate operational and financial risk visibility. Quantitative modeling capabilities separate enterprise-grade from mid-market offerings.
- Reporting Software:Regulatory filing preparation, board dashboards, and external disclosure automation complete the workflow stack. SEC climate disclosure rules expand addressable market for ESG-specific reporting.
Audit Management sustains installed base dominance; Monitoring Tools gains share fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Enterprise procurement clusters in states with the densest regulatory exposure and highest litigation risk. Financial institutions, healthcare systems, and energy operators drive platform adoption through regional headquarters concentration.
California
The California Privacy Rights Act mandates automated consumer rights fulfillment for businesses processing personal data. The state's Attorney General office enforces CPRA violations with substantial penalties. San Francisco Bay Area technology firms deploy GRC platforms to manage vendor security questionnaires and ISO 27001 certification workflows.
New York
Wall Street banks require integrated SOX, BSA/AML, and stress-testing modules with real-time regulatory reporting. The New York Department of Financial Services cybersecurity regulations impose strict breach notification timelines. Manhattan financial services firms anchor the highest per-seat platform spending in the nation.
Texas
State-chartered banks accelerate adoption to preempt federal examination findings from the Office of the Comptroller of the Currency. The Texas economy's diversification into energy and technology creates multi-industry compliance demand. Dallas-Fort Worth mid-market enterprises prefer subscription pricing models and rapid scaling without capital committee approvals.
Florida
Healthcare systems automate HIPAA security rule compliance as OCR enforcement intensifies across the Southeast. The state's insurance sector faces overlapping state privacy statutes plus federal NAIC model regulations. Miami healthcare clusters replace manual spreadsheet tracking with automated control testing platforms.
Illinois
Manufacturing headquarters implement environmental compliance modules to satisfy EPA reporting and supply chain security criteria. The Illinois Biometric Information Privacy Act creates unique litigation exposure requiring specialized data governance workflows. Chicago industrial conglomerates deploy enterprise risk registers with quantitative scenario modeling for board-level oversight.
United States Governance, Risk and Compliance Platform Market Key Industry Players
Channel-controlling players compete with product-specialist players across deployment models and vertical segments. The market exhibits tiered concentration with enterprise-grade vendors anchoring financial services and healthcare while mid-market specialists penetrate underserved 500-5,000 employee segments. Three archetypes dominate: hybrid cloud infrastructure providers, ERP-integrated platform vendors, and IT service management extenders. M&A activity concentrates on API-first compliance automation startups, while incumbents defend position through pre-configured industry control libraries.
Within the infrastructure-anchored tier, IBM leverages hybrid cloud capabilities to anchor enterprise-grade compliance workflows. Oracle sustains positioning through database and ERP ecosystem integration. ServiceNow exemplifies the IT service management extension archetype, differentiating through operational risk and audit orchestration capabilities.
| Leading Market Players |
|---|
| IBM |
| Oracle |
| MetricStream |
| NAVEX Global |
| LogicManager |
| AuditBoard |
| Archer |
| ServiceNow |
| RSA Security |
| Others |
Cost & Logistics Intelligence
The I-95 freight corridor's congestion-driven cost volatility directly shapes how GRC platform vendors structure subscription pricing and where they locate cloud infrastructure. Rising logistics expenses for on-premise hardware shipments compress margins on perpetual-license deals, pushing vendors toward SaaS delivery that eliminates physical distribution. This cost dynamic concentrates pricing power with cloud-native providers while forcing legacy vendors to absorb freight inflation or surrender mid-market accounts.
Pricing Analysis
Cost-plus contracts with CPI indexation dominate enterprise procurement above 5,000 seats, while per-user SaaS tiers capture the 500-5,000 employee segment. Price differentiation hinges on ISO 27001 certification tier and API connector depth, with premium bundles commanding 40-60% spreads over baseline configurations. Pricing pressure stems from mid-market buyers in Texas and Florida demanding consumption metering without capital committee approvals. Financial services institutions show lowest price sensitivity due to regulatory penalty exposure, while state-chartered banks in secondary markets negotiate hardest on per-seat rates.
Supply Chain Analysis
Upstream cloud infrastructure feeds from hyperscale data centers concentrated in Northern Virginia, Oregon, and Iowa, with secondary nodes expanding in Texas and Arizona. Compute provisioning draws from Intel and AMD server architectures, while storage arrays rest on Samsung and Western Digital components. Single-source vulnerability runs through AWS and Azure control planes for multi-tenant GRC deployments, creating concentration risk during regional outages. Distribution runs through direct enterprise sales teams with certified implementation partners handling mid-market onboarding.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The United States GRC platform market represents a high-growth disruption as SEC climate disclosure mandates and NIST AI Risk Management Framework adoption force replacement cycles across Fortune 500 compliance stacks.
For Market Incumbents: Pre-empt API-first competitors by acquiring specialized compliance automation startups with pre-built connectors to Workday and Salesforce. Consolidate position through backward integration into managed security services, addressing the talent scarcity that extends implementation timelines. Defend against Oracle and SAP's ERP-embedded GRC modules by deepening vertical-specific control libraries for healthcare HIPAA and energy NERC CIP workflows.
For New Entrants and Emerging Players: Establish a beachhead in the 500-5,000 employee mid-market through modular, per-user pricing that bypasses enterprise procurement cycles. Target state-chartered banks in Texas and Florida with rapid-deployment SOX and BSA/AML packages. Lead with AI governance modules aligned to NIST AI RMF, capturing early-adopter technology firms facing algorithmic audit requirements.
For Investors and Strategic Acquirers: Cloud-native compliance automation specialists with healthcare and financial services vertical depth present the strongest acquisition profile. Long-term viability rests on recurring revenue durability through regulatory complexity expansion rather than macroeconomic cyclicality. Monitor state privacy law consolidation trajectories as the signal indicating whether unified-platform or best-of-breed strategies will dominate procurement.
| Strategic Initiative | Industry Significance |
|---|---|
| API-First Platform Architecture | Pre-built connectors to SAP and Workday slash implementation timelines for mid-market buyers. |
| Vertical Control Library Expansion | Pre-configured HIPAA and NERC CIP templates defend against ERP-embedded competitors. |
| AI Governance Module Launch | NIST AI RMF alignment captures technology sector demand for algorithmic bias detection. |
| Consumption Metering Pricing | Per-transaction tiers unlock Texas and Florida mid-market procurement without capital approval. |
| Managed Services Bundling | Outsourced platform administration addresses talent scarcity extending project risk. |
Research Approach
Two parallel data streams informed the analysis: structured interviews with CISOs, compliance officers, internal audit directors, and GRC platform procurement leads; and secondary validation against SEC enforcement actions, state attorney general filings, NIST framework publications, and vendor pricing disclosures. Primary fieldwork captured implementation timeline data and module adoption patterns across financial services, healthcare, and energy verticals. Bottom-up sizing of vendor-reported seat counts and top-down triangulation against enterprise IT spending benchmarks anchored volume estimates.
Forecast inputs considered deployment model migration rates, regulatory mandate effective dates, and API ecosystem maturity across the projection horizon. Segmentation dimensions modeled include organization size tier, vertical industry, compliance type intensity, and cloud-native versus hybrid architecture preference. CAGRs derived from regression analysis of historical procurement velocity against enforcement event frequency. Industry-specific inputs incorporated SEC examination cycle timing and state privacy law enactment trajectories.
Stress conditions across interest rate environments, regulatory enforcement intensity, and cloud infrastructure cost inflation were modeled; outcomes outside those bands fall beyond the analytical envelope. Forecasts reflect documented assumptions about vendor consolidation pace and mid-market penetration rates. Cross-checking against Gartner and Forrester enterprise software spending benchmarks is advised before commitment-grade decisions.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Risk Management and Compliance
Revenue Assurance Market
Risk Management and Compliance
Disclosure Management Market
Risk Management and Compliance
Southeast Asia Credit and Risk Management Market
Risk Management and Compliance
Global Patient Safety and Risk Management Softwares Market
Risk Management and Compliance
Asia-Pacific Compliance and Traceability Solutions Market
Risk Management and Compliance
Third Party Risk Management Market
Risk Management and Compliance
Loan Compliance Management Software Market
Risk Management and Compliance
Financial Services Security Software Market
Risk Management and Compliance
Europe Strategic Consulting Services Market
Risk Management and Compliance
Stress Testing Solutions Market
Risk Management and Compliance
Global Financial Crime and Fraud Management Solutions Market
Risk Management and Compliance
Regtech Market
Risk Management and Compliance
Europe BFSI Biometrics Market
Risk Management and Compliance
Anti-Money Laundering (AML) Market
Risk Management and Compliance
UK Anti Money Laundering Solutions Market
Risk Management and Compliance
Asia-Pacific BFSI Biometrics Market