
 UK Cybersecurity Market | 2026-2036
UK Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
UK Cybersecurity Market Analytics
Mid-market enterprises are bifurcating the UK Cybersecurity Market as they shift from basic antivirus to managed detection and response. Darktrace plc leverages autonomous AI to anchor premium positioning in self-learning threat detection. Sophos Group plc competes through integrated endpoint and firewall bundles tailored to resource-constrained IT teams. BAE Systems Digital Intelligence dominates public-sector and defence-adjacent contracts through cleared-personnel delivery models.
Cybersecurity encompasses technologies, processes, and controls designed to protect systems, networks, and data from digital attacks, with specifications typically requiring sub-100-millisecond threat detection latency and AES-256 encryption at rest. Its primary purpose is ensuring confidentiality, integrity, and availability of information assets across commercial and governmental operations. Cloud Security within the Solution Type dimension is absorbing disproportionate investment as UK organisations migrate workloads to distributed environments. Managed Security Services across the Service Type category is expanding fastest, driven by skills shortages that push internal SOC build-outs toward third-party operators.
The National Cyber Security Centre publishes mandatory minimum standards for critical national infrastructure operators, while the Product Security and Telecommunications Infrastructure Act imposes baseline security duties on connected device manufacturers selling into the UK. These frameworks elevate compliance-driven procurement and disqualify vendors lacking certified assurance schemes. Stakeholders must monitor whether NCSC evolves toward formal product certification mandates that would reshape vendor qualification barriers.
Market Dynamics
The Product Security and Telecommunications Infrastructure Act is compressing vendor qualification timelines as connected device manufacturers face mandatory baseline security duties before UK market entry.
Growth Catalysts
- Critical national infrastructure mandates:The National Cyber Security Centre publishes mandatory minimum standards that elevate compliance-driven procurement across energy, water, and transport operators.
- Cloud workload migration:UK enterprises are absorbing disproportionate investment into cloud security solutions as distributed environments expand attack surfaces.
- Skills shortages:Internal SOC build-outs are pushing mid-market enterprises toward managed security services operators.
Market Restraints
- Cleared-personnel scarcity:Defence-adjacent contracts require security-cleared delivery teams that concentrate among a handful of suppliers.
- Certification timeline friction:NCSC assurance schemes impose multi-month validation periods that delay product launches.
- Legacy integration costs:On-premise security stacks require substantial reconfiguration to interface with cloud-native platforms.
Strategic Opportunities
- Autonomous AI convergence:Self-learning threat detection systems are penetrating mid-market accounts previously served by signature-based tools.
- Managed detection and response expansion:Resource-constrained IT teams are abandoning basic antivirus for outsourced monitoring services.
- Scottish and Northern English clusters:Corporate security demand is dispersing beyond London toward regional financial services hubs.
Industry Challenges
- Threat analyst talent gaps:Security operations centres face persistent vacancies in incident response and forensics functions.
- Multi-vendor orchestration complexity:Enterprises struggle to unify telemetry across endpoint, network, and identity platforms.
- Supply chain attestation burdens:Software bill of materials requirements are forcing vendors to map third-party component provenance.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | UK Cybersecurity Market |
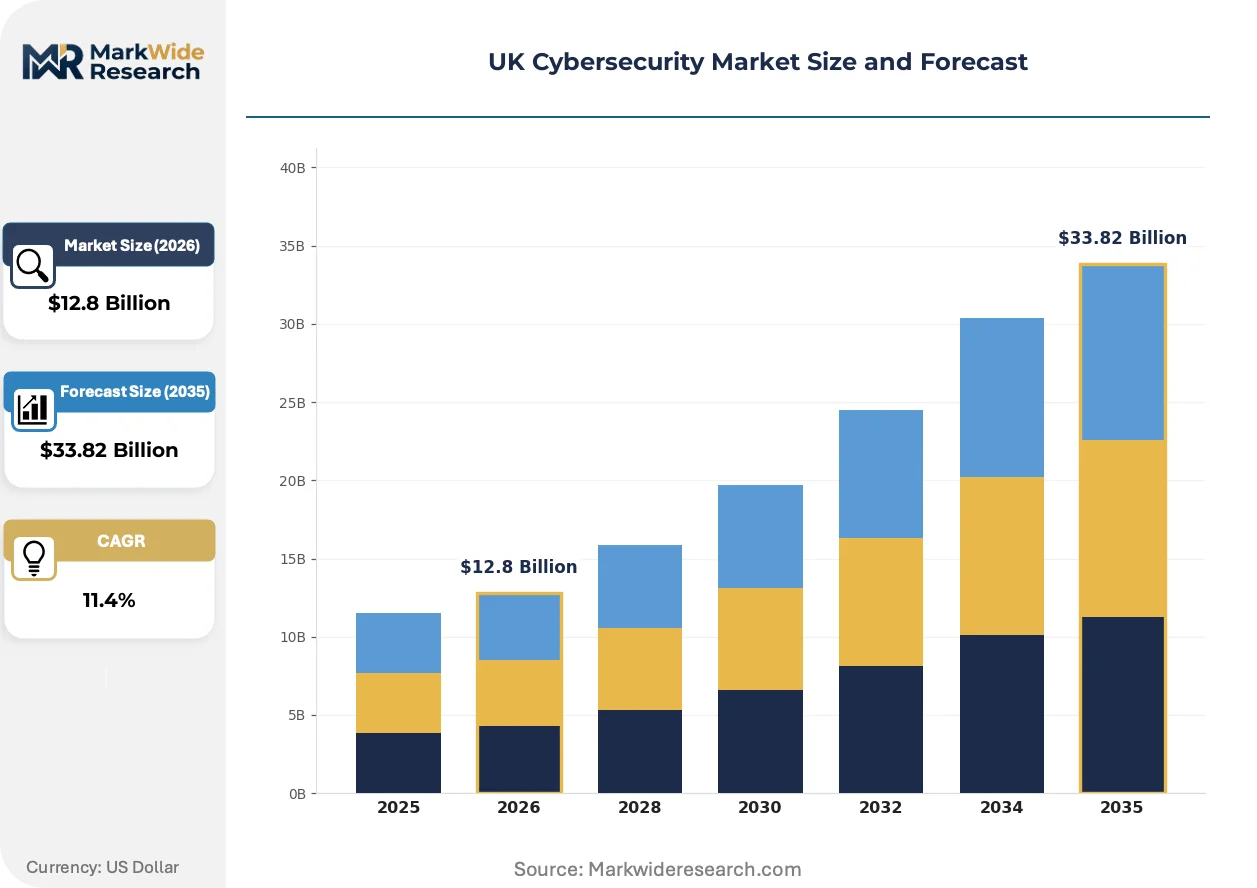
| Market Size in 2026 | $12.8 Billion |
| Market Size in 2035 | $33.82 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Endpoint Protection, Network Security, Cloud Security, Application Security Deployment Model: On-Premises, Cloud, Hybrid, Managed Services Industry Vertical: Finance, Healthcare, Retail, Government Service Type: Consulting, Managed Security Services, Incident Response, Training |
| Companies Covered | Darktrace plc, Sophos Group plc, NCC Group plc, BAE Systems Digital Intelligence, BT Group plc, Clearswift Ltd, Immersive Labs Ltd, Tessian, Becrypt Ltd, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
UK Cybersecurity Market Evolving Landscape
Zero-trust architecture principles are displacing perimeter-based security models across UK enterprise estates. This shift is compressing incumbent firewall vendors while elevating identity-centric and micro-segmentation specialists.
Extended detection and response platforms are fragmenting the security information and event management category. Mid-market enterprises are adopting these tools to collapse alert fatigue and automate tier-one triage. The technology is fragmenting procurement patterns as buyers consolidate previously separate endpoint, network, and cloud security budgets into unified platforms.
The Product Security and Telecommunications Infrastructure Act imposes baseline security duties on connected device manufacturers selling into the UK. Vendors must maintain vulnerability disclosure programmes and provide minimum security update periods. Consumer IoT and enterprise operational technology hardware categories face the steepest compliance ramps.
Outcome-based service contracts are displacing seat-based or device-count pricing in managed security engagements. Large enterprises are shifting risk to providers through guaranteed mean-time-to-detect clauses. This restructuring is most visible in London's financial services and insurance sectors where procurement teams demand measurable security outcomes.
UK Cybersecurity Market Segmentation
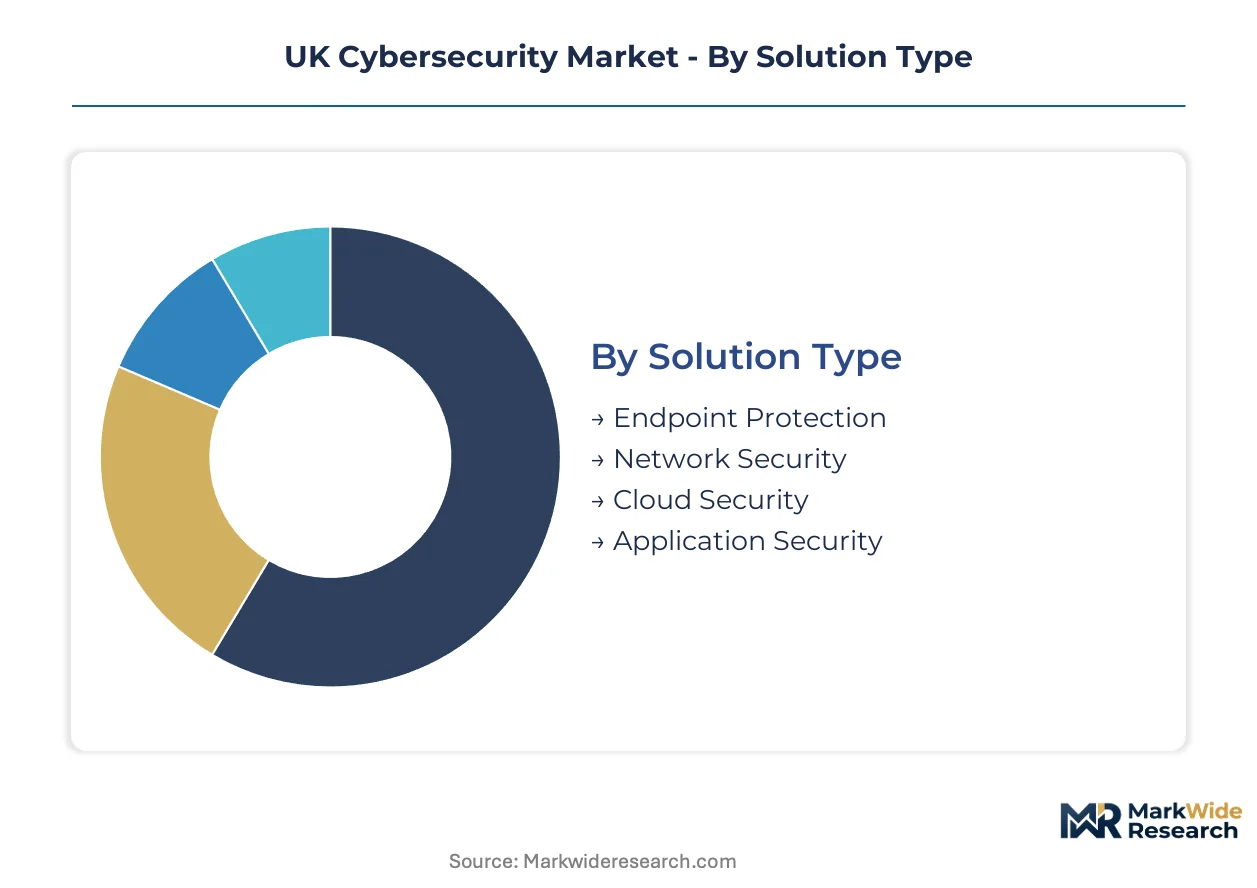
UK cybersecurity procurement patterns diverge sharply across solution architectures and delivery models. Organisations segment investments based on regulatory exposure, cloud migration status, and internal security operations maturity.
Solution Type:
Margin pools concentrate in cloud-native platforms as enterprises abandon hardware-centric refresh cycles.
- Endpoint Protection:Agent-based detection and response tools deploy across laptops, servers, and mobile devices with behavioural analysis engines. NHS trusts and local government authorities in England are consolidating fragmented antivirus contracts into unified endpoint detection platforms to meet NCSC minimum standards.
- Cloud Security:Cloud access security brokers and workload protection platforms secure distributed multi-tenant environments. Financial services firms in London's Square Mile are absorbing disproportionate spend here as trading infrastructure migrates off mainframe estates.
- Network Security:Next-generation firewalls and intrusion prevention systems filter traffic at perimeter and internal boundaries. Manufacturing clusters in the West Midlands maintain steady procurement despite slower cloud adoption.
- Application Security:Static and dynamic testing tools identify code vulnerabilities before production deployment. Fintech startups in Manchester and Edinburgh are driving subscription growth for software composition analysis.
Endpoint Protection holds installed capacity. Cloud Security is rotating up the share rankings.
Deployment Model:
Customer type dictates architecture choice — regulated incumbents favour control, mid-market seeks operational leverage.
- On-Premises:Hardware appliances and software licenses deployed within customer data centres retain stronghold in defence and intelligence sectors. BAE Systems and other cleared suppliers deliver exclusively through this model for classified networks.
- Managed Services:Third-party security operations centres monitor customer environments under outcome-based contracts. Skills shortages across Yorkshire and the North West are accelerating mid-market abandonment of internal SOC build-outs.
- Cloud:SaaS-delivered security tools eliminate infrastructure ownership. Sectors without legacy mainframe dependencies — professional services, digital media — default here.
- Hybrid:Split architectures preserve sensitive workloads on-premises while cloud-native tools secure distributed endpoints. Critical national infrastructure operators adopt this posture to satisfy NCSC guidance without full migration.
On-Premises retains the largest installed base. Managed Services is climbing the fastest as skills gaps persist.
Industry Vertical:
Regulatory intensity varies the compliance premium across sectors.
- Finance:Banks, insurers, and asset managers face Prudential Regulation Authority and Financial Conduct Authority cyber resilience requirements. London's underwriting syndicates at Lloyd's mandate specific controls for cyber insurance policyholders.
- Government:Central departments, devolved administrations, and local authorities procure through Crown Commercial Service frameworks. The NCSC's Cyber Essentials and Cyber Essentials Plus certifications gate supplier eligibility.
- Healthcare:NHS England's Data Security and Protection Toolkit mandates annual assessments. Trusts in the East Midlands and South West lag London and Manchester in security maturity.
- Retail:Payment Card Industry Data Security Standard compliance drives point-of-sale and e-commerce protection. Online grocery platforms accelerated cloud security investment post-pandemic.
Finance holds the highest per-employee security spend. Government is expanding fastest through framework centralisation.
Service Type:
Value capture shifts from hourly consulting toward recurring managed outcomes.
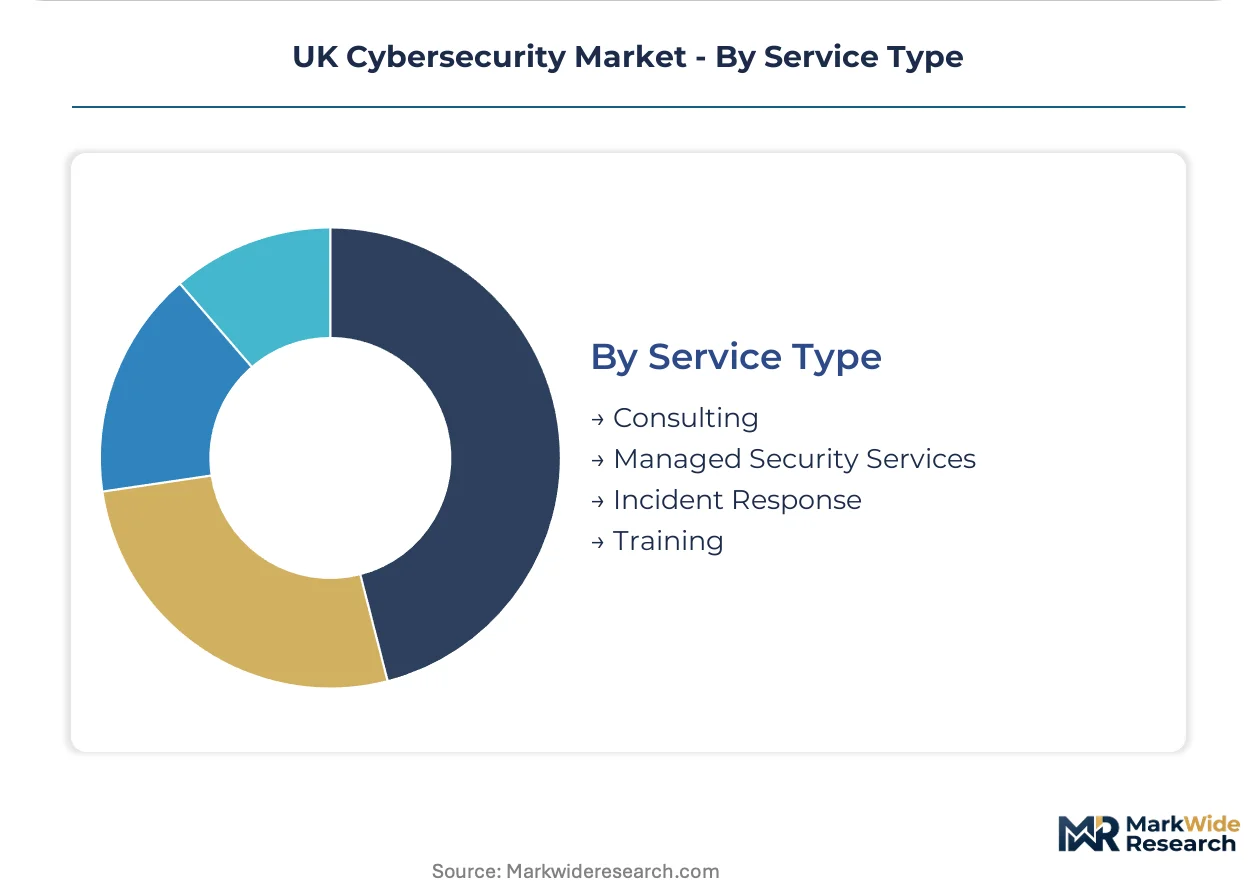
- Managed Security Services:Continuous monitoring, threat hunting, and incident response delivered under subscription. The National Cyber Security Centre's assured service provider scheme concentrates procurement among certified operators.
- Incident Response:Retainer and emergency engagement models for breach containment and forensic investigation. Ransomware frequency has doubled retainer penetration among FTSE 250 firms.
- Consulting:Advisory engagements for security strategy, architecture design, and compliance readiness. Big Four professional services firms dominate C-suite advisory relationships.
- Training:Security awareness programmes and technical certification preparation. Phishing simulation platforms are displacing classroom-based instruction in corporate budgets.
Managed Security Services commands the largest recurring revenue base. Incident Response is gaining share fastest through retainer model adoption.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
UK cybersecurity procurement concentrates in government security clusters, financial services headquarters, and regional technology hubs. Buyer archetypes span cleared defence contractors, regulated banks, and mid-market enterprises outsourcing security operations.
London and the Southeast
The Square Mile and Canary Wharf host the highest density of financial services security spending. Lloyd's underwriting syndicates mandate specific cyber controls for policyholders. The National Cyber Security Centre's Victoria headquarters anchors government procurement through Crown Commercial Service frameworks.
Scotland
Edinburgh's fintech sector and Glasgow's public-sector hubs drive cloud security adoption. The Scottish Government's digital strategy emphasizes Cyber Essentials Plus certification for suppliers. Financial services firms in Edinburgh's Exchange District are consolidating fragmented security contracts into unified platforms.
North England
Manchester's media and technology corridor plus Leeds' banking sector generate managed security services demand. Skills shortages across Yorkshire accelerate mid-market abandonment of internal SOC build-outs. The Northern Powerhouse investment programme funds cyber resilience initiatives for critical infrastructure operators.
Midlands
West Midlands manufacturing clusters maintain steady network security procurement despite slower cloud migration. Birmingham's professional services sector defaults to SaaS-delivered tools. The region's automotive supply chain faces NCSC minimum standards compliance deadlines for connected vehicle components.
Wales and Northern Ireland
Cardiff's public-sector technology hub and Belfast's cybersecurity research cluster attract framework contracts. Welsh Government procurement channels concentrate spend through centralised digital services. Northern Ireland's Queen's University Belfast spin-outs contribute to the UK's assured service provider ecosystem.
UK Cybersecurity Market Competitive Landscape
Player mix skews toward specialised autonomous AI vendors and integrated platform providers. The vendor base concentrates among cleared defence contractors serving classified networks and SaaS-native operators targeting mid-market accounts. Three strategic archetypes dominate: self-learning threat detection specialists, bundled endpoint-firewall providers, and assured public-sector suppliers. Competitive moves centre on outcome-based contract restructuring and regional SOC capacity expansion.
Within the autonomous AI tier, Darktrace plc and Tessian exemplify self-learning detection architectures. Among integrated platform providers, Sophos Group plc occupies a position serving resource-constrained IT teams through bundled offerings. On the assured public-sector vector, BAE Systems Digital Intelligence and NCC Group plc anchor cleared-personnel delivery models for defence and critical national infrastructure contracts.
| Leading Market Players |
|---|
| Darktrace plc |
| Sophos Group plc |
| NCC Group plc |
| BAE Systems Digital Intelligence |
| BT Group plc |
| Clearswift Ltd |
| Immersive Labs Ltd |
| Tessian |
| Becrypt Ltd |
| Others |
Value Network & Pricing Analysis
Managed security services substitution for in-house SOC build-outs simultaneously reshapes supply geography toward regional UK delivery centres and compresses pricing economics through outcome-based contract structures. This displacement concentrates procurement leverage among NCSC-assured service providers while fragmenting price discovery across subscription tiers.
Pricing Analysis
Cost-plus contracts with labour-rate indexation dominate cleared-personnel engagements for defence-adjacent contracts. Three-tier pricing structure across premium autonomous AI, standard integrated platforms, and economy antivirus tiers reflects certification grade and detection latency specifications. Pricing pressure stems from mid-market buyers consolidating fragmented tool spend into unified platforms. Resource-constrained IT teams exhibit highest price sensitivity; financial services firms with regulatory mandates show lowest.
Supply Chain Analysis
Israel and the United States anchor threat intelligence feed production and AI/ML model development for UK cybersecurity vendors. Semiconductor components for hardware security modules draw from Taiwan and South Korea fabrication facilities. Single-source vulnerability in cloud infrastructure dependencies creates concentration risk. Distribution runs through direct enterprise sales teams and Crown Commercial Service frameworks for public-sector accounts.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The UK cybersecurity market tracks a cyclical recovery as post-pandemic cloud migration normalisation restores enterprise IT security budget growth. NCSC assurance scheme expansion amplifies compliance-driven procurement waves.
For Market Incumbents: Shield installed base relationships through NCSC Cyber Essentials Plus certification maintenance against emerging SaaS-native competitors. Deepen vertical integration into autonomous AI model training to defend margin position. Prioritise cleared-personnel pipeline investment for defence contract continuity.
For New Entrants and Emerging Players: Differentiate on Scottish and Northern English regional SOC capacity where skills shortages concentrate mid-market demand. Target Yorkshire manufacturing clusters with hybrid deployment expertise. Pursue channel partnerships with Crown Commercial Service framework holders for public-sector access.
For Investors and Strategic Acquirers: Secondary-cycle assets sit with PE-backed managed security services operators with assured service provider status. Five-to-ten-year viability hinges on outcome-based contract renewal rates. Monitor NCSC product certification mandate signals as inflection indicator for vendor qualification barrier restructuring.
| Strategic Initiative | Industry Significance |
|---|---|
| NCSC Assured Service Provider Accreditation | Framework eligibility gates Crown Commercial Service procurement access. |
| Regional SOC Capacity Expansion | Yorkshire and Scotland delivery centres capture mid-market outsourcing demand. |
| Autonomous AI Platform Integration | Self-learning detection architectures displace signature-based incumbent tools. |
| Outcome-Based Contract Restructuring | Guaranteed mean-time-to-detect clauses shift risk to service providers. |
| Cleared-Personnel Pipeline Investment | Defence-adjacent contracts require security-cleared delivery team concentration. |
Research Methodology
A spread of perspectives from CISOs at financial services firms, NCSC framework procurement officers, managed security services operations directors, and autonomous AI vendor product managers converged on the working assumptions. Primary fieldwork combined with secondary validation against SEC filings, Crown Commercial Service contract awards, and NCSC assurance scheme registers. Bottom-up sizing of segment deployments triangulated with top-down security IT spend allocation models.
Segmentation dimensions modeled span solution type, deployment model, organisation size tier, industry vertical, and regional security cluster across the analysis window. CAGRs derived from elasticity-adjusted technology adoption curves incorporating cloud migration velocity and regulatory compliance deadline phasing. Forecast inputs include NCSC guidance evolution timelines and Product Security and Telecommunications Infrastructure Act enforcement intensity.
Material uncertainties — regulatory certification mandate timing, threat actor sophistication escalation, cleared-personnel availability shocks — sit outside the modeled envelope. Forecasts reflect documented assumptions subject to revision from these vectors. Recalibration cycles align with material shifts in NCSC policy announcements and critical national infrastructure operator procurement waves.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
Nordics Cybersecurity Market
Cybersecurity
Enterprise Mobility Security Market
Cybersecurity
Global Quantum Cryptography Solutions Market
Cybersecurity
Big Data Security Market
Cybersecurity
V2X Cybersecurity Market
Cybersecurity
South Korea Cybersecurity Market
Cybersecurity
Corporate Web Security Market
Cybersecurity
Secure Socket Layer (SSL) Certification Market
Cybersecurity
Data Center Security Market
Cybersecurity
Hong Kong Cybersecurity Market
Cybersecurity
India Cybersecurity Market
Cybersecurity
Virtualization Security Tools Market
Cybersecurity
Global Cyber Situational Awareness Market
Cybersecurity
Cloud Authentication Market
Cybersecurity
Data Security Market