
 Sri Lanka Cyber (Liability) Insurance Market | 2026-2036
Sri Lanka Cyber (Liability) Insurance Market Size, Share, and Industry Trends Forecast 2026-2036
Sri Lanka Cyber (Liability) Insurance Market Analytics
Central Bank of Sri Lanka directives on operational resilience and cyber risk governance are shifting corporate insurance procurement patterns across the island. Ceylinco General Insurance leverages its established commercial lines infrastructure to anchor SME penetration in Colombo and Gampaha districts. Fairfirst Insurance competes through specialized first-party coverage modules tailored to manufacturing and logistics clients. HNB General Insurance extends its bancassurance network to distribute cyber policies alongside traditional commercial packages.
Cyber liability insurance constitutes a specialized risk transfer instrument designed to indemnify policyholders against financial losses stemming from data breaches, network intrusions, privacy violations, and operational technology failures; policies typically specify sub-limits for forensic investigation costs, regulatory defense expenses, and notification obligations. First-party coverage dominates premium volume as Sri Lankan enterprises prioritize direct loss mitigation over third-party liability transfer. Third-party coverage exhibits faster trajectory acceleration driven by vendor contract mandates in software procurement and cloud service agreements. Finance sector buyers generate the densest policy concentration, reflecting both regulatory scrutiny intensity and transactional data asset value.
Central Bank of Sri Lanka guidelines intersect with Insurance Regulatory Commission of Sri Lanka licensing requirements to shape product filing standards, capital adequacy treatment of cyber exposures, and mandatory disclosure frameworks for policyholders. ISO 27001 certification adoption among enterprise buyers creates parallel demand pressure for insurance instruments that validate control environments. Stakeholders must monitor evolving ransomware loss severity patterns and domestic court interpretations of cyber tort liability to calibrate coverage terms against emerging exposure vectors.
Market Dynamics
Central Bank of Sri Lanka operational resilience directives are compressing enterprise procurement cycles, forcing commercial banks and non-bank financial institutions to accelerate cyber risk transfer decisions ahead of formal compliance deadlines.
Growth Catalysts
- Digital Transaction Velocity:Real-time payment rails and mobile banking adoption among Sri Lankan retail and SME segments are expanding attack surface exposure. Financial institutions face quantifiable loss events from credential harvesting and authorized push payment fraud.
- ISO 27001 Certification Mandates:Enterprise procurement departments in Colombo's commercial district now require vendor cyber insurance certificates as contractual preconditions. This creates downstream policy demand across software development and cloud hosting supply chains.
- Cloud Migration Acceleration:Sri Lankan manufacturers and logistics operators migrating operational technology to Microsoft Azure and Amazon Web Services infrastructure are encountering shared responsibility gaps that insurance products must address.
Market Restraints
- Actuarial Data Scarcity:Domestic cyber loss history remains insufficient for Sri Lankan carriers to price tail risk with confidence, forcing reliance on international reinsurance markets and imported rating models.
- Concentrated Reinsurance Dependency:Lloyd's of London and Singapore-based reinsurers supply capacity for catastrophic cyber layers, exposing Sri Lankan primary carriers to global market hardening cycles beyond local control.
- Judicial Uncertainty:Sri Lankan courts have not yet established precedent on cyber tort liability apportionment between technology vendors and insured enterprises, creating coverage interpretation risk for policy drafters.
Strategic Opportunities
- Gampaha District SME Penetration:Manufacturing clusters north of Colombo exhibit sub-5% cyber insurance penetration despite operational technology deployments. Local broker networks can activate dormant commercial relationships.
- Parametric Ransomware Products:Index-based triggers tied to public incident databases or dark web monitoring services can bypass claims adjustment friction for small enterprises lacking forensic investigation budgets.
- Bancassurance Channel Expansion:Commercial banking relationships provide pre-qualified customer data and premium collection infrastructure that reduces customer acquisition costs below traditional broker channels.
Industry Challenges
- Underwriting Talent Gap:Sri Lankan insurance labor markets lack sufficient personnel conversant in both information security control frameworks and traditional casualty underwriting methodologies.
- Legacy Policy Administration Systems:Domestic carriers operate on core platforms designed for property and motor lines, requiring expensive middleware development to support cyber-specific rating variables and dynamic coverage endorsements.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Sri Lanka Cyber (Liability) Insurance Market |
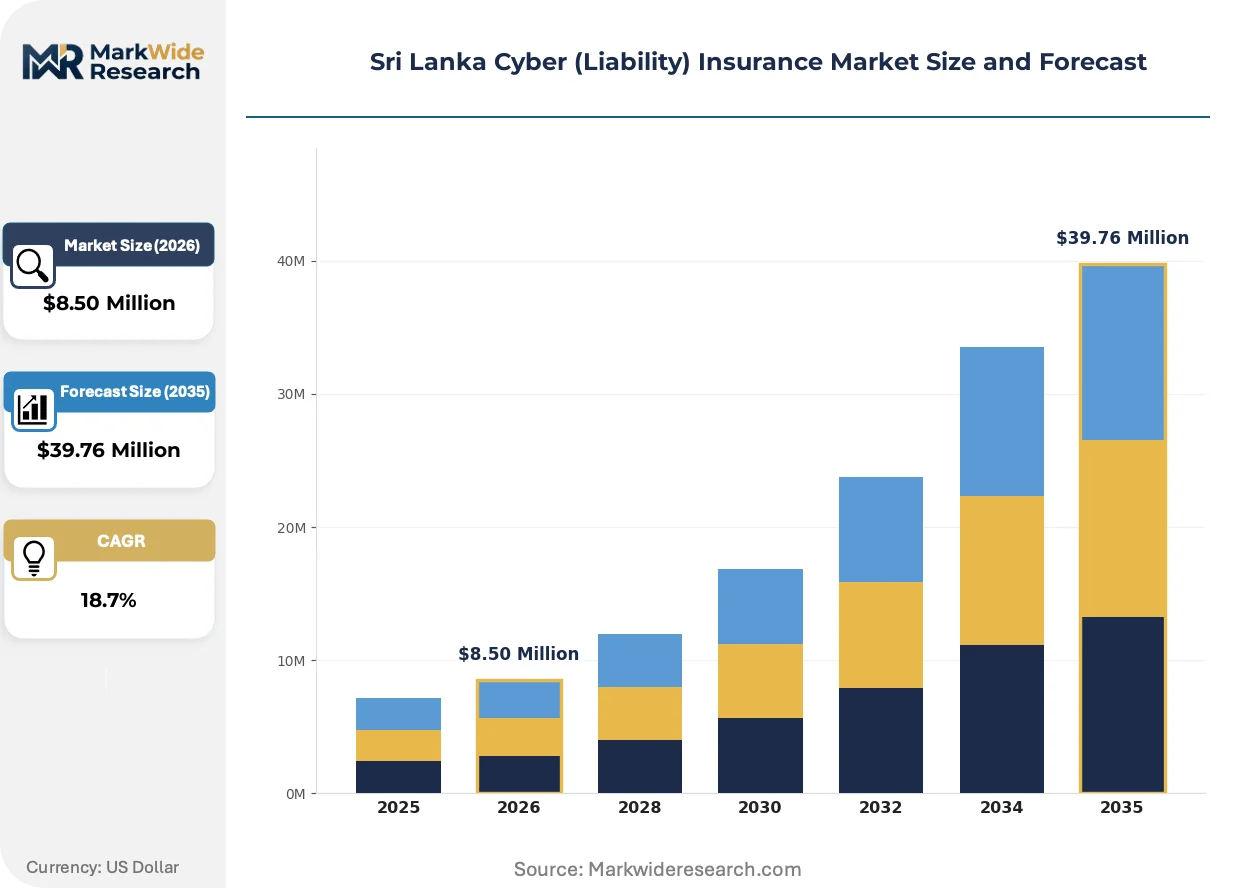
| Market Size in 2026 | $8.50 Million |
| Market Size in 2035 | $39.76 Million |
| CAGR (2026 – 2036) | 18.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Policy Type: First-Party Coverage, Third-Party Coverage, Data Breach Response, Business Interruption End User: SMEs, Large Enterprises, Government Agencies, NGOs Sector: Healthcare, Finance, Retail, Education Coverage Scope: Network Security, Privacy Liability, Media Liability, Cyber Extortion |
| Companies Covered | AXA XL, Ceylinco General Insurance, Fairfirst Insurance, Union Assurance, HNB General Insurance, Allianz Lanka, Milliman Insurance, Janashakthi Insurance, Sri Lanka Insurance Corporation, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Sri Lanka Cyber (Liability) Insurance Market Evolving Landscape
Security orchestration platforms and automated underwriting engines are compressing policy issuance timelines from weeks to hours, while regulatory pressure on operational resilience is forcing product design innovation beyond traditional indemnity structures.
Artificial intelligence-powered risk scoring engines are automating the ingestion of external attack surface data, dark web exposure indicators, and control environment telemetry. Sri Lankan commercial banks with dedicated information security functions are adopting these tools for pre-bind risk selection. This compression of assessment timelines is automating the displacement of manual security questionnaire processes that previously delayed coverage binding by 10-15 business days.
Insurance Regulatory Commission of Sri Lanka licensing requirements now explicitly address cyber liability product filings, capital treatment, and policyholder disclosure obligations. This regulatory scaffolding forces domestic carriers to maintain dedicated cyber product governance committees and file semi-annual exposure reports. Finance sector buyers face the most intensive scrutiny, with central bank examiners requesting evidence of insurance coverage during operational risk supervision.
Enterprise risk managers in Colombo's banking and telecommunications sectors now demand bundled first-party and third-party coverage modules with unified limits. Traditional standalone cyber policies with siloed sub-limits for forensic costs, business interruption, and regulatory defense are losing favor. This consolidation preference is most visible among organizations with ISO 27001-certified security programs that seek insurance validation for control environment investments already made.
Sri Lanka Cyber (Liability) Insurance Market Segmentation
Cyber insurance segmentation in Sri Lanka reflects distinct risk transfer priorities across policy structures, organizational scale, and sectoral exposure profiles. Carriers calibrate pricing engines and coverage modules around these dimensions to match premium adequacy with loss severity patterns.
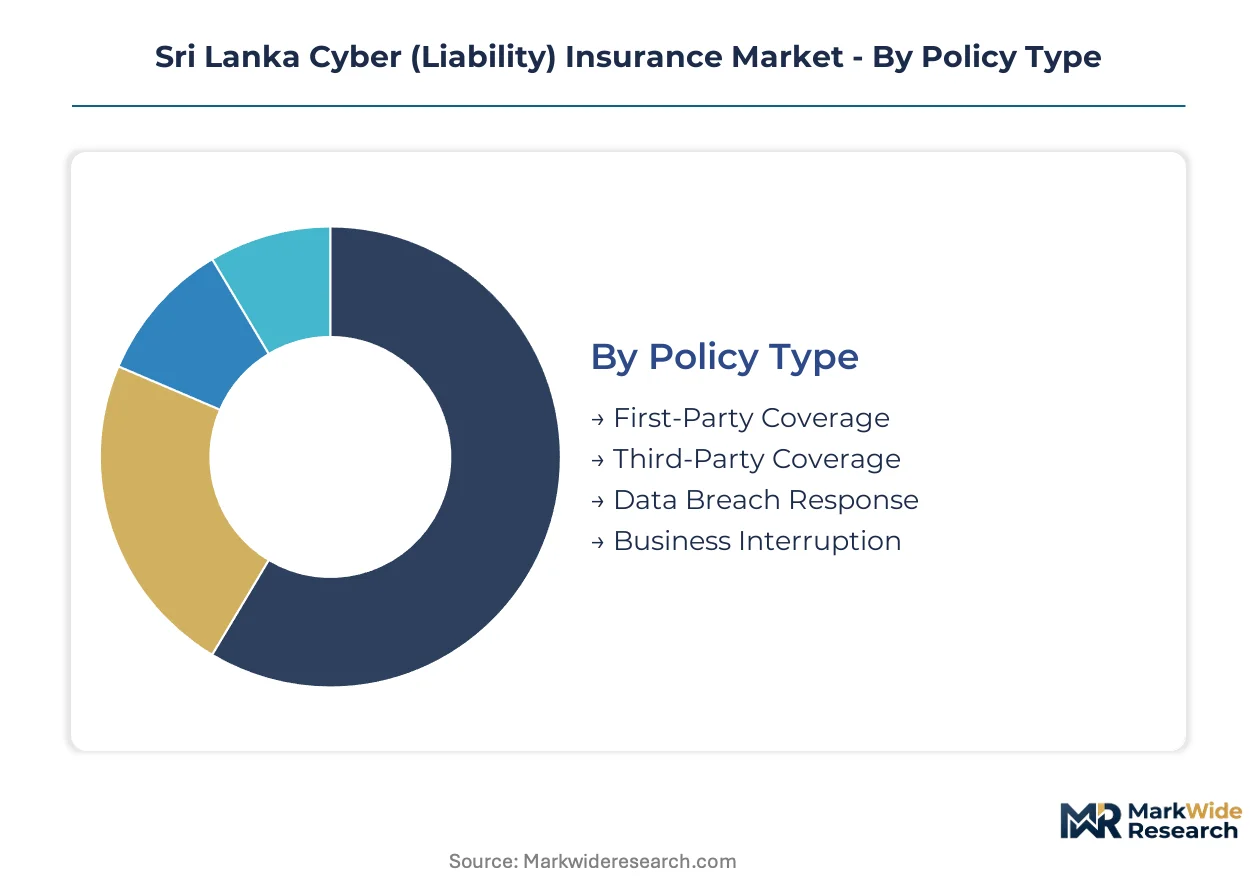
Policy Type:
Upgrade cycles from legacy commercial packages to dedicated cyber policies are accelerating as Central Bank operational resilience directives force explicit risk transfer documentation.
- First-Party Coverage:Direct loss indemnification for forensic investigation costs, data restoration expenses, and business interruption losses following network intrusions or ransomware events. Colombo's banking sector generates concentrated demand as institutions seek balance sheet protection against operational technology failures.
- Third-Party Coverage:Liability transfer for privacy violations, regulatory defense costs, and damages to external parties from data breaches or network security failures. Manufacturing clusters in Gampaha district are procuring this coverage to satisfy vendor contract mandates from ISO 27001-certified enterprise buyers.
- Data Breach Response:Modular coverage for notification obligations, credit monitoring services, and crisis communications following confirmed data compromise incidents.
- Business Interruption:Income replacement and extra expense coverage triggered by network downtime or operational technology unavailability exceeding policy waiting periods.
First-Party Coverage sits at the top of the volume ranking, with Third-Party Coverage climbing the fastest as vendor contract mandates expand through software procurement supply chains.
End User:
Customer type segmentation reveals divergent procurement sophistication, with premium adequacy and coverage breadth scaling directly with organizational IT security maturity and regulatory exposure intensity.
- SMEs:Micro-enterprises and small businesses purchasing through bancassurance channels or broker networks, typically selecting bundled first-party modules with sub-limited forensic cost coverage. Gampaha district manufacturing SMEs exhibit sub-5% penetration despite operational technology deployments.
- Large Enterprises:Organizations with dedicated information security functions demanding unified limits across first-party and third-party coverage modules. Colombo commercial district enterprises with ISO 27001 certification drive bundled policy adoption.
- Government Agencies:Public sector entities subject to national cybersecurity framework compliance requirements, procuring coverage through centralized tender processes with extended regulatory defense sub-limits.
- NGOs:Non-governmental organizations managing donor data and beneficiary information, increasingly requiring coverage for privacy liability in international funding arrangements.
Large Enterprises command premium pricing tiers, while SME penetration represents the steepest expansion opportunity as carrier distribution infrastructure matures.
Sector:
Sectoral segmentation aligns coverage design with data asset value concentration and regulatory scrutiny intensity, with finance and healthcare exhibiting the most specialized underwriting requirements.
- Healthcare:Coverage for protected health information breaches, medical device network security failures, and patient notification obligations. Private hospital chains in Colombo are procuring dedicated cyber policies as electronic health record adoption expands.
- Finance:Banking, insurance, and non-bank financial institutions facing Central Bank operational resilience directives and quantifiable losses from credential harvesting and authorized push payment fraud.
- Retail:Point-of-sale system protection, e-commerce platform coverage, and payment card industry compliance-related incident response.
- Education:Student data privacy coverage for universities and private institutions managing international enrollment records and research intellectual property.
Finance dominates premium volume, with Healthcare gaining share fastest as private hospital digitization accelerates patient data exposure.
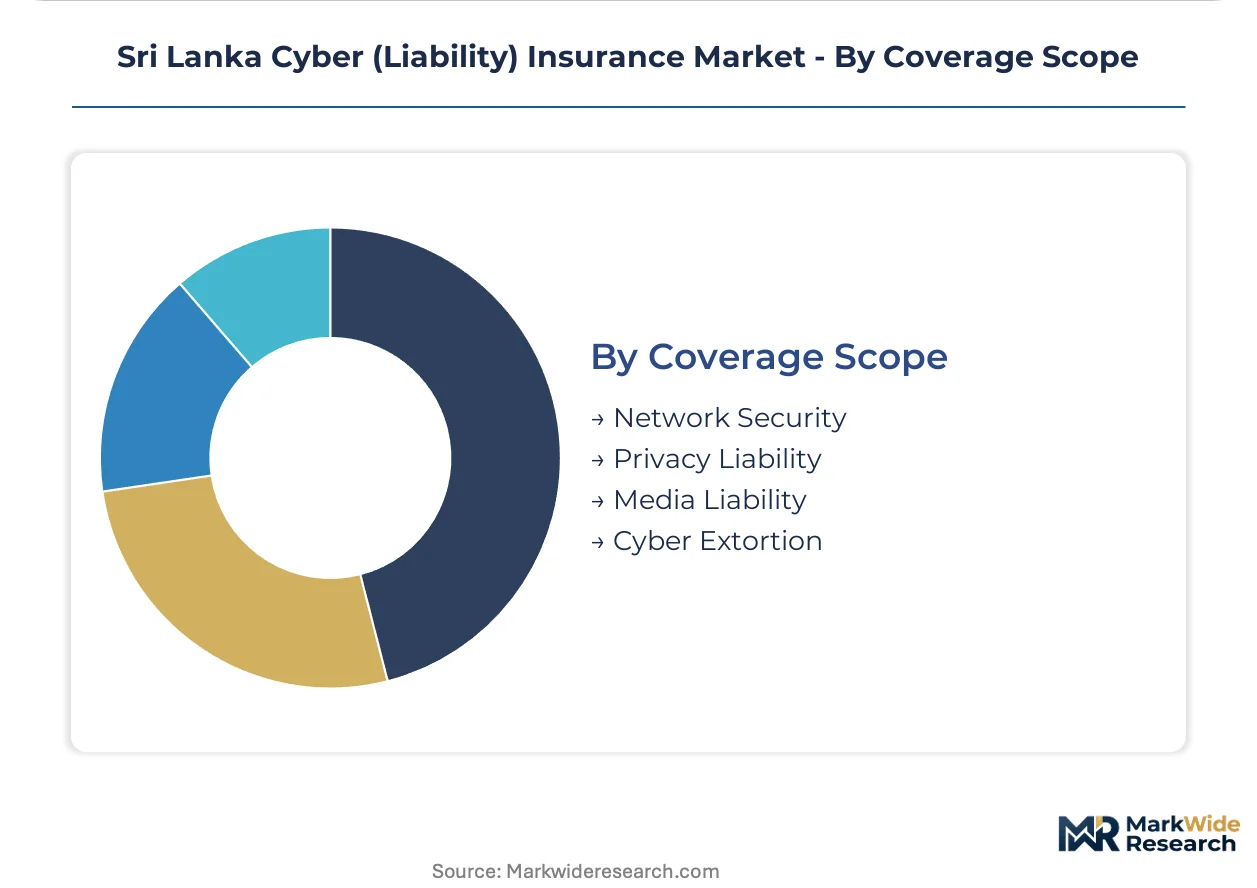
Coverage Scope:
Scope segmentation determines which peril categories trigger policy response, with carriers offering modular endorsements or packaged combinations based on enterprise risk profile assessments.
- Network Security:Coverage for unauthorized network access, malware deployment, and operational technology compromise. Manufacturing and logistics operators migrating to cloud infrastructure demand this scope to address shared responsibility gaps.
- Privacy Liability:Regulatory defense and damages for violations of data protection obligations, most heavily purchased by finance sector buyers facing Central Bank examination scrutiny.
- Media Liability:Coverage for intellectual property infringement, defamation, and advertising injury arising from digital content publication.
- Cyber Extortion:Ransom payment coverage, negotiation services, and business interruption during extortion events, with parametric trigger products emerging for SME segments lacking forensic investigation budgets.
Network Security anchors policy attachment rates, while Cyber Extortion is expanding most quickly as ransomware loss severity patterns drive demand for dedicated peril coverage.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Sri Lanka's cyber insurance infrastructure traces its commercial origins to the post-2009 financial sector liberalization, when multinational reinsurers first established Colombo-based facultative capacity for emerging liability lines. The market's geographic footprint now concentrates in the Western Province's commercial corridor, with regulatory mandates from the Central Bank and Insurance Regulatory Commission of Sri Lanka driving procurement standardization.
Colombo District
Financial institutions headquartered in the capital generate the densest policy concentration, with commercial banks procuring bundled first-party and third-party coverage to satisfy operational resilience directives. The Central Bank of Sri Lanka's examination protocols explicitly request evidence of cyber risk transfer during supervisory reviews. Colombo's enterprise IT infrastructure density creates exposure profiles that demand unified limits across forensic costs, business interruption, and regulatory defense sub-limits.
Gampaha District
Manufacturing clusters north of Colombo exhibit sub-5% cyber insurance penetration despite operational technology deployments in textiles and food processing. The Insurance Regulatory Commission of Sri Lanka's licensing requirements for product filings have not yet penetrated SME broker networks serving this industrial belt. Local carriers are activating dormant commercial relationships through bancassurance channels tied to working capital facilities.
Kalutara District
Logistics operators and port-related services in this coastal district face shared responsibility gaps from cloud migration to Microsoft Azure and Amazon Web Services infrastructure. The Central Bank's guidelines on operational risk management intersect with port authority cybersecurity frameworks to create compliance-driven procurement pressure. Rubber and tea export processors in the district's interior are encountering vendor contract mandates requiring cyber insurance certificates.
Kandy District
Healthcare digitization in this central province hub is accelerating demand for protected health information breach coverage as private hospital chains adopt electronic health record systems. The national cybersecurity framework compliance requirements apply to public sector entities procuring through centralized tender processes. Kandy's education sector, managing international enrollment records, is requiring privacy liability coverage for donor data protection.
Southern Province
Tourism and hospitality operators in Galle and Matara are procuring point-of-sale system protection and e-commerce platform coverage as digital payment adoption expands among international visitors. The Insurance Regulatory Commission of Sri Lanka's capital adequacy treatment of cyber exposures affects carrier willingness to underwrite seasonal revenue interruption risks. Coastal hotel chains are negotiating parametric trigger products tied to ransomware incident databases.
Sri Lanka Cyber (Liability) Insurance Market Competitive Landscape
Capital-heavy insurers with dedicated commercial lines infrastructure compete with asset-light specialists leveraging bancassurance distribution partnerships. The market structure exhibits moderate concentration, with established domestic carriers holding dominant positions in SME penetration while international reinsurers supply catastrophic capacity. Three strategic archetypes dominate: integrated composite insurers with multi-line commercial portfolios, specialist cyber underwriters with parametric product capabilities, and bank-affiliated carriers exploiting captive distribution networks. Competitive moves center on broker network expansion into underpenetrated manufacturing districts and middleware investments to modernize legacy policy administration systems.
Within the integrated composite tier, Ceylinco General Insurance and Sri Lanka Insurance Corporation occupy positions defined by established commercial lines infrastructure and Colombo-Gampaha district penetration. Among bank-affiliated specialists, HNB General Insurance exemplifies the bancassurance channel archetype, distributing cyber policies alongside traditional commercial packages through pre-qualified customer relationships. Fairfirst Insurance represents the specialist vector, competing through modular first-party coverage tailored to manufacturing and logistics client segments. These carriers collectively illustrate the market's segmentation between scale-driven integrated operations and targeted specialist offerings.
| Leading Market Players |
|---|
| AXA XL |
| Ceylinco General Insurance |
| Fairfirst Insurance |
| Union Assurance |
| HNB General Insurance |
| Allianz Lanka |
| Milliman Insurance |
| Janashakthi Insurance |
| Sri Lanka Insurance Corporation |
| Others |
Value Network & Pricing Analysis
Reinsurance capacity pricing at Lloyd's of London cascades through Sri Lankan primary carrier rate cards, compressing margins for domestic underwriters while elevating premium thresholds for enterprise buyers in Colombo's financial district.
Pricing Analysis
Three-tier pricing structure across premium, standard, and economy levels dominates Sri Lankan cyber insurance distribution. Premium tiers attach to ISO 27001-certified enterprises with unified limits across first-party and third-party modules; economy tiers serve micro-enterprises through bancassurance channels with sub-limited forensic coverage. Pricing pressure stems from actuarial data scarcity forcing reliance on imported international rating models. SME segments exhibit highest price sensitivity, while large enterprises with dedicated information security functions accept premium adequacy for coverage breadth.
Supply Chain Analysis
ISO 27001 certification requirements from enterprise procurement departments gate access to Sri Lankan cyber insurance distribution. Reinsurance capacity concentrates in London, Singapore, and Bermuda markets. Domestic carriers draw from international actuarial databases, Lloyd's syndicate capacity, and regional catastrophe modeling firms. Single-source vulnerability to Lloyd's market hardening cycles threatens primary carrier profitability. Distribution runs through broker networks in Colombo, bancassurance partnerships with commercial banks, and direct carrier relationships with large enterprises.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Sri Lanka's cyber insurance market functions as a geographic-arbitrage play where regulatory compliance costs in Colombo's financial district subsidize product development for underpenetrated manufacturing belts, exploiting the gap between Central Bank directive intensity and Insurance Regulatory Commission enforcement reach in peripheral districts.
For Market Incumbents: Deepen bancassurance channel control through exclusive partnerships with HNB and other commercial banks holding pre-qualified SME customer data. Invest in middleware modernization to displace legacy policy administration systems that delay dynamic coverage endorsements. The threat of international specialist carriers entering through parametric product routes demands accelerated proprietary capability building in automated underwriting engines. For New Entrants and Emerging Players: Commercial broker networks in Gampaha District offer the most penetrable entry vector, activating dormant manufacturing relationships with sub-5% cyber insurance penetration despite operational technology deployments. Target textile and food processing clusters with modular first-party coverage bypassing complex security questionnaire processes. A parametric ransomware product with index-based triggers tied to public incident databases captures SME segments lacking forensic investigation budgets. For Investors and Strategic Acquirers: Asymmetric upside sits with bank-affiliated carriers possessing captive distribution infrastructure and pre-qualified customer data pools. Long-term viability hinges on underwriting talent development and reinsurance relationship depth rather than pure scale. The signal to watch is Central Bank examination protocol expansion beyond finance sector buyers into telecommunications and healthcare verticals, which would compress procurement cycles and accelerate premium volume concentration.| Strategic Initiative | Industry Significance |
|---|---|
| Parametric Product Launch | Index-based ransomware triggers bypass claims friction for SME segments lacking forensic budgets. |
| Bancassurance Channel Expansion | HNB General Insurance's pre-qualified customer data reduces acquisition costs below traditional broker channels. |
| Middleware Modernization | Legacy core platforms designed for property and motor lines require expensive cyber-specific rating variable support. |
| ISO 27001 Certification Investment | Enterprise procurement departments now require vendor cyber insurance certificates as contractual preconditions. |
| Reinsurance Relationship Deepening | Lloyd's of London and Singapore-based reinsurers supply capacity for catastrophic cyber layers beyond local control. |
Research Methodology
Quantitative tracking and qualitative interviews ran in parallel throughout the study window, combining primary discussions with chief information security officers at Colombo commercial banks, insurance regulatory affairs leads at the Insurance Regulatory Commission of Sri Lanka, broker network principals in Gampaha District, and underwriting directors at domestic carriers. Secondary validation drew from Central Bank of Sri Lanka operational resilience guidelines, Insurance Regulatory Commission product filing records, ISO 27001 certification databases, and reinsurance market capacity reports. Bottom-up policy count and premium volume estimates triangulated against top-down carrier exposure disclosures.
Comparable-period anchoring tied projection assumptions to historical regulatory directive implementation timelines and cyber loss event severity patterns across the analysis window. Segmentation dimensions modeled include policy type, organizational scale, sectoral exposure, and coverage scope complexity. CAGRs were derived from carrier premium growth trajectories, reinsurance pricing trends, and enterprise procurement cycle compression rates. Forecast inputs incorporated Central Bank examination protocol expansion assumptions and ISO 27001 certification adoption curves among vendor supply chains.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to judicial precedent establishment on cyber tort liability apportionment and ransomware loss severity pattern shifts. Forecasts reflect documented assumptions on regulatory enforcement intensity and reinsurance market cycle positioning. A model refresh is warranted upon material change in Central Bank operational resilience directive scope or Lloyd's of London catastrophic cyber layer pricing.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Insurance
Marine Freight Insurance Market
Insurance
Insurance Protection Products Market
Insurance
Cannabis Crop Insurance Market
Insurance
China Liability Insurance Market
Insurance
Online Insurance Market
Insurance
India Dental Insurance Market
Insurance
India Health Insurance Market
Insurance
Greece Property and Casualty Insurance Market
Insurance
United States Bancassurance Market
Insurance
Europe Road Assistance Insurance Market
Insurance
Insurance Analytics Market
Insurance
Reinsurance Carriers Market
Insurance
Aviation Insurance Market
Insurance
Logistics Insurance Market
Insurance
Asia-Pacific Extended Warranty Market
Insurance
Critical Illness Insurance Market