
 Security Information and Event Management Software Market | 2026-2036
Security Information and Event Management Software Market Size, Share, and Industry Trends Forecast 2026-2036
Security Information and Event Management Software Market Analytics
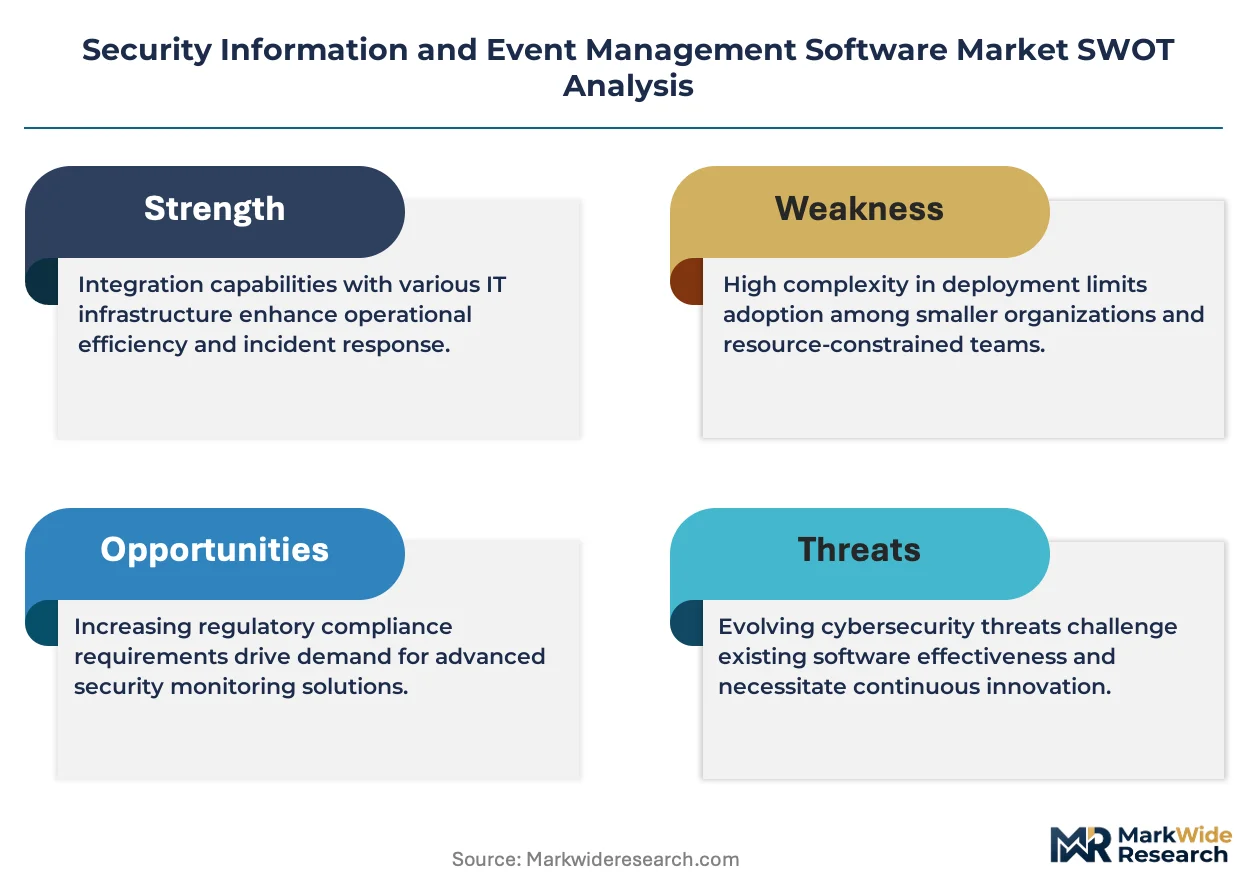
Channel dynamics between direct enterprise sales and managed security service providers is tilting toward hybrid delivery models. Splunk, Inc. leverages its data analytics heritage to anchor premium deployments in large financial institutions. Fortinet, Inc. competes by bundling SIEM with its broader security fabric, sustaining margin through integrated platform sales. IBM Corporation dominates in regulated industries with its QRadar portfolio, extending reach through extensive professional services networks.
Security Information and Event Management Software aggregates log data from network devices, servers, and applications to enable real-time threat detection, incident correlation, and compliance reporting through rule-based engines and machine learning algorithms. Cloud-based deployment is expanding fastest as organizations migrate security operations from capital-intensive data centers to elastic infrastructure, while on-premises solutions retain strongholds in government agencies with air-gapped requirements. Threat detection solutions capture the largest solution share, though compliance management is deepening integration with privacy frameworks as regulatory scope widens across jurisdictions.
The US SEC mandates cybersecurity incident disclosure under new rules, while the EU's GDPR and NIS2 Directive impose breach notification timelines that force enterprises to invest in automated SIEM response workflows. ISO 27001 certification requirements further shape product standards by demanding continuous monitoring capabilities that vendors must architect into core platforms. Stakeholders should monitor how AI-driven anomaly detection reshapes vendor differentiation and whether cloud-native SIEM architectures displace legacy installations in regulated sectors previously committed to on-premises control.
Market Dynamics
Cloud-native SIEM architectures are compressing deployment timelines from months to weeks, forcing incumbent vendors to re-engineer delivery models while enterprises abandon capital-intensive data center investments.
Growth Catalysts
- SEC Cybersecurity Disclosure Rules:US public companies must report material incidents within four business days, mandating automated detection workflows that SIEM platforms provide.
- Financial Services:Banks and insurers face Basel III operational risk frameworks and PCI-DSS 4.0 mandates that require continuous log correlation and real-time alerting infrastructure.
- Machine Learning Inference:Embedded anomaly detection reduces false-positive rates by orders of magnitude, justifying platform upgrades in security operations centers.
Market Restraints
- Skilled Analyst Scarcity:The global shortage of SOC engineers fluent in SPL and KQL query languages limits utilization rates of deployed platforms.
- Data Ingestion Cost Volatility:Cloud SIEM pricing tied to log volume creates unpredictable operational expenditure spikes during breach investigations.
- Air-Gapped Requirements:Defense and intelligence agencies in the United States, United Kingdom, and Australia prohibit cloud connectivity, fragmenting vendor addressable markets.
Strategic Opportunities
- NIS2 Directive:The EU's expanded critical infrastructure scope captures mid-market logistics and waste management operators previously exempt from mandatory monitoring.
- Extended Detection and Response Convergence:Native endpoint telemetry integration creates single-vendor procurement opportunities displacing point-tool stacks.
- India:RBI's cyber security framework for urban cooperative banks and SEBI's mandate for stockbrokers create first-wave SIEM adoption in a market with minimal legacy installation base.
Industry Challenges
- Multi-Cloud Telemetry Fragmentation:AWS CloudTrail, Azure Monitor, and Google Cloud Logging export incompatible schema formats, forcing costly normalization engineering.
- ISO 27001 Certification Timelines:The 12-18 month audit cycles for continuous monitoring clause implementation delay revenue recognition for compliance-focused deployments.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Security Information and Event Management Software Market |
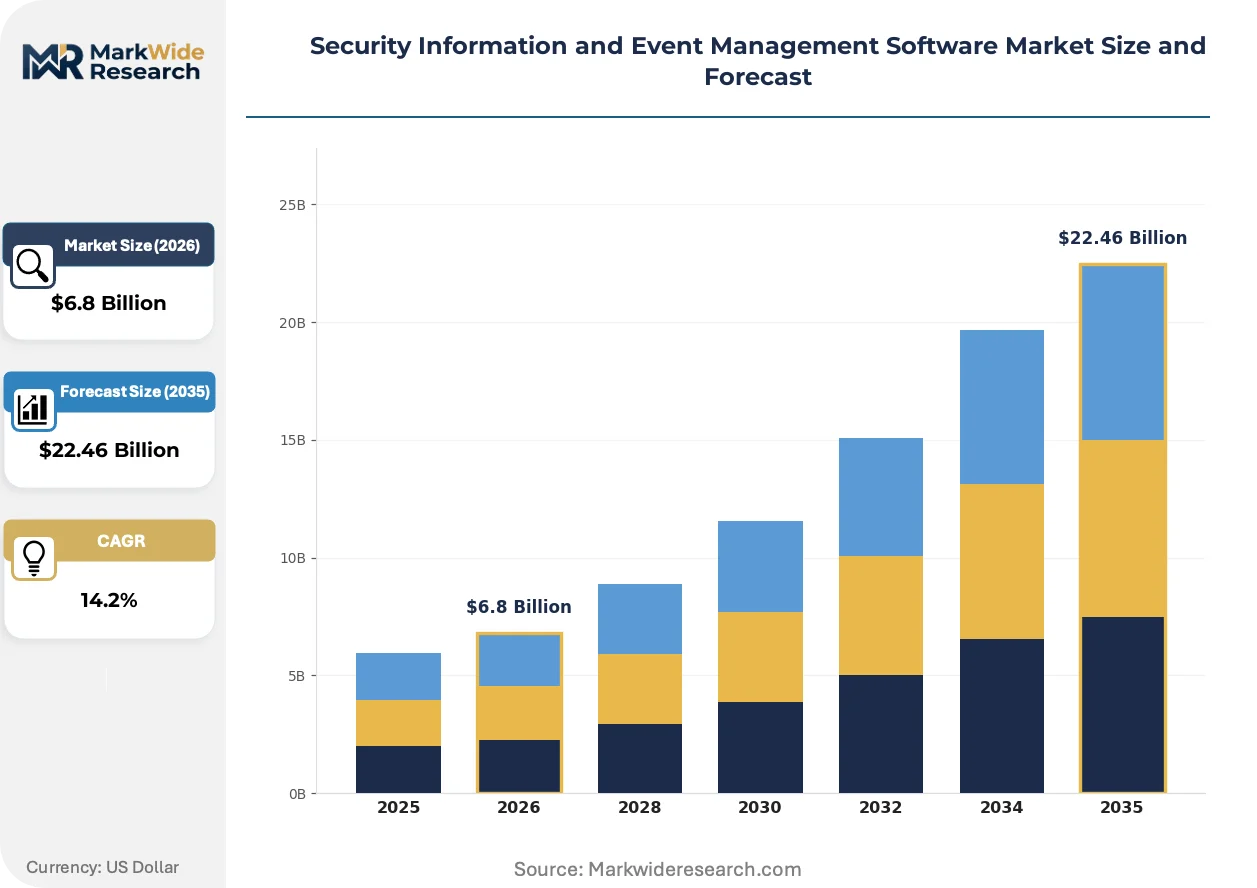
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $22.46 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-premises, Cloud-based, Hybrid, Managed Service End User: IT Services, Healthcare Providers, Financial Institutions, Government Agencies Solution: Threat Detection, Incident Response, Compliance Management, Data Privacy Integration Level: API Integration, SIEM Integration, Log Management, Security Orchestration |
| Companies Covered | IBM Corporation, Splunk, Inc., Hewlett Packard Enterprise, Fortinet, Inc., LogRhythm, Inc., Exabeam, Inc., Securonix, Inc., Rapid7, Inc., Datadog, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Security Information and Event Management Software Market Evolving Landscape
Artificial intelligence is compressing detection latency while regulatory jurisdictions race to mandate minimum response capabilities, reshaping how security operations centers architect their technology stacks.
Agentless network detection and response is collapsing the traditional boundary between network traffic analysis and log-based SIEM correlation. Large manufacturers with operational technology environments are adopting these hybrid platforms fastest, eliminating the need for endpoint agents on legacy industrial controllers. The technology is collapsing vendor category distinctions that previously separated NDR, SIEM, and SOAR procurement decisions.
The EU AI Act's risk classification system imposes documentation and human oversight requirements on automated threat scoring algorithms used by European financial institutions. Vendors must now maintain algorithmic audit trails and explainability interfaces that increase engineering overhead. French and German banking supervisors are inspecting these capabilities during authorization reviews, compressing product roadmaps for continental European deployments.
Consumption-based pricing for cloud SIEM is replacing perpetual licensing as the dominant procurement model among mid-market enterprises. Managed security service providers are capturing this transition by bundling platform costs into fixed monthly fees, displacing direct vendor relationships. The United Kingdom and Nordic countries exhibit the fastest migration to this structure, driven by CFO preference for operational expenditure treatment and reduced capital allocation friction.
Security Information and Event Management Software Market Segmentation
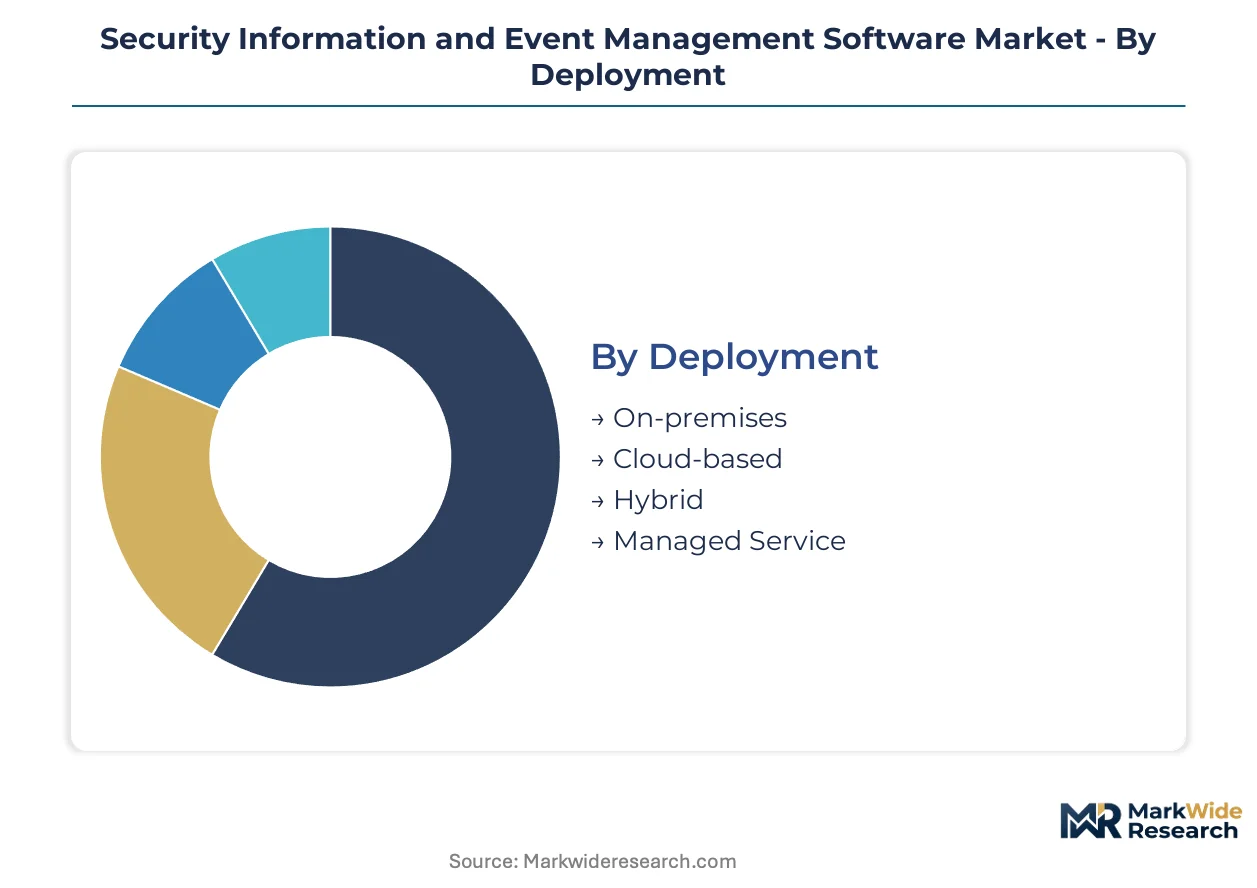
SIEM procurement patterns diverge sharply across deployment architectures, end-user compliance burdens, and integration complexity. Vendors must architect modular platforms that span air-gapped government installations through elastic cloud-native deployments without fragmenting their engineering roadmaps.
Deployment:
Cost tier determines deployment selection more than any other factor, with capital expenditure constraints and operational expenditure preferences splitting the addressable market into distinct procurement camps.
- On-premises:Hardware-anchored installations run on dedicated servers within client data centers, requiring substantial upfront licensing and infrastructure investment. United States defense agencies and intelligence services mandate air-gapped architectures that prohibit external connectivity, sustaining demand despite longer deployment cycles.
- Cloud-based:Elastic infrastructure provisioning eliminates data center capital requirements while enabling rapid scaling during breach investigations. Mid-market enterprises across Germany and the United Kingdom favor this model for CFO-preferred operational expenditure treatment and reduced procurement friction.
- Hybrid:Split architectures retain sensitive log processing on-premises while pushing analytics workloads to cloud infrastructure. Financial institutions in Switzerland and Singapore deploy hybrid models to satisfy data residency mandates without sacrificing computational elasticity.
- Managed Service:Third-party security operations centers assume platform operation and analyst staffing responsibilities. Nordic enterprises with limited SOC engineering talent increasingly procure SIEM as a fully managed utility rather than licensed software.
On-premises commands the established base. The steepest expansion runs through cloud-based deployment models.
End User:
Application-specific compliance mandates reshape feature requirements, with each vertical imposing distinct telemetry sources, retention periods, and reporting formats that vendors must accommodate.
- IT Services:Managed service providers and systems integrators deploy multi-tenant SIEM platforms to monitor client environments at scale. Indian IT services exporters building security operations centers for North American clients drive substantial platform licensing volume.
- Healthcare Providers:HIPAA-mandated audit trails and patient data access monitoring require specialized connectors for electronic health record systems. United States hospital networks face OCR enforcement actions that accelerate SIEM procurement for access pattern analysis.
- Financial Institutions:Basel III operational risk frameworks and PCI-DSS 4.0 mandates demand continuous transaction log correlation and real-time alerting infrastructure. United States banks and European insurers represent the most technically sophisticated buyer segment, driving premium pricing for advanced analytics.
- Government Agencies:Classified network requirements and sovereign data residency laws constrain vendor selection to cleared suppliers with domestic engineering presence. Australian and Canadian federal agencies maintain strict procurement preferences for domestically headquartered security vendors.
Financial institutions command the established base. The steepest expansion runs through healthcare providers facing intensified privacy enforcement.
Solution:
Customer maturity and security operations center staffing levels determine which functional modules deliver immediate value versus long-term platform stickiness.
- Threat Detection:Real-time correlation engines and machine learning anomaly detection identify intrusion attempts across network, endpoint, and identity telemetry. Large manufacturers with operational technology environments deploy these capabilities fastest to protect industrial control systems from ransomware.
- Incident Response:Automated playbook execution and case management workflows compress mean-time-to-remediation during active breaches. United Kingdom critical infrastructure operators subject to NIS2 Directive response timelines invest heavily in response automation.
- Compliance Management:Pre-built reporting templates map log data to regulatory frameworks including GDPR, SOX, and ISO 27001. French and German mid-market enterprises accelerating certification timelines drive modular compliance solution adoption.
- Data Privacy:Personal data discovery and consent tracking capabilities extend SIEM functionality into privacy program management. Brazilian and South Korean enterprises navigating new comprehensive privacy laws represent emerging demand centers.
Threat detection commands the established base. The steepest expansion runs through data privacy modules as regulatory scope widens.
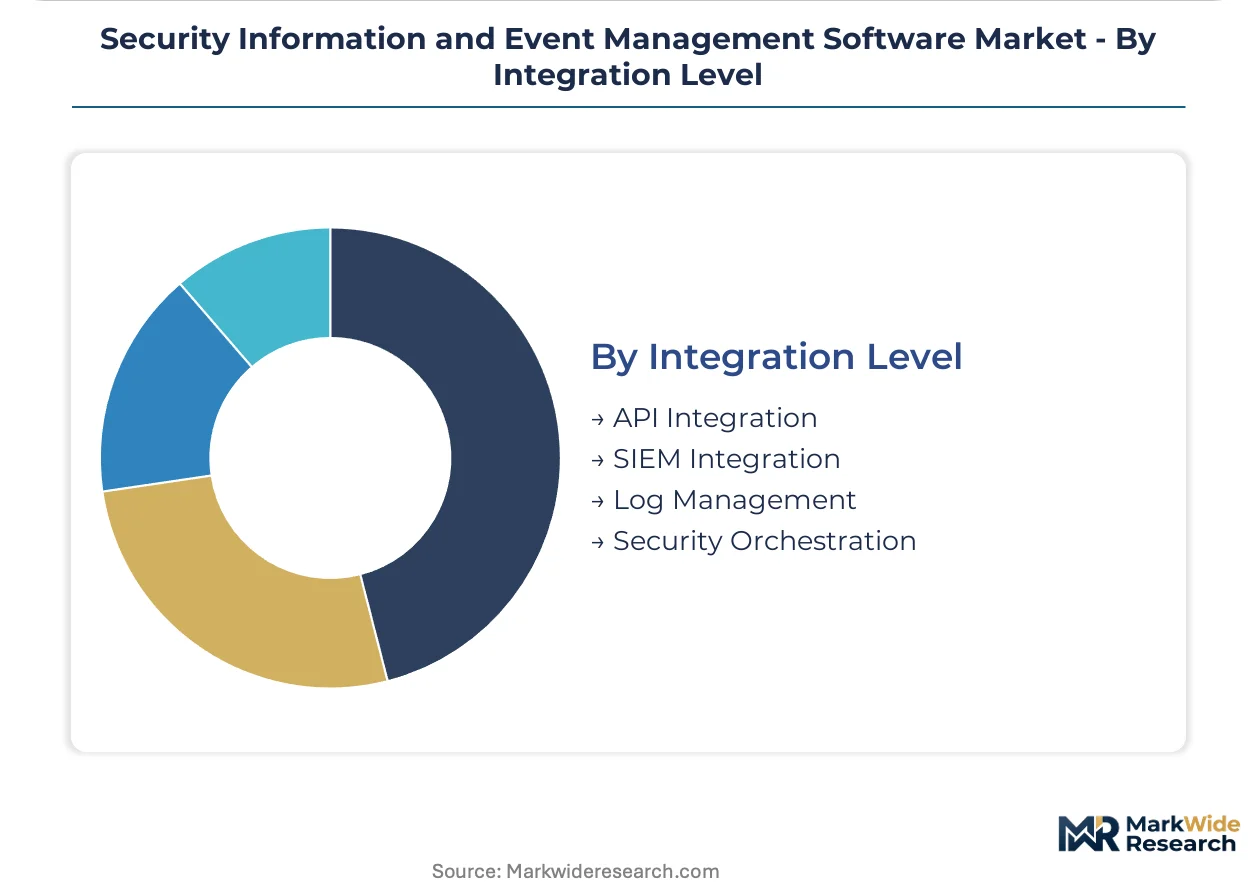
Integration Level:
Supply concentration among platform vendors and point-tool specialists creates procurement friction that integration depth resolves.
- API Integration:RESTful and GraphQL interfaces enable custom data ingestion from proprietary applications and niche security tools. Technology companies with extensive in-house development resources favor API-first architectures for maximum flexibility.
- SIEM Integration:Native connectors to competing platforms facilitate migration projects and multi-vendor environments. Large United States enterprises with legacy Splunk or QRadar installations require seamless data portability during platform consolidation.
- Log Management:Centralized collection, normalization, and storage infrastructure underpins all downstream analytics. Japanese manufacturing conglomerates with decades of operational data prioritize log management reliability over advanced detection features.
- Security Orchestration:SOAR capabilities automate cross-tool response actions and analyst workflow management. United Arab Emirates financial free zone operators building greenfield security operations centers procure orchestration as core platform requirements.
Log management commands the established base. The steepest expansion runs through security orchestration as staffing constraints intensify.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Pricing power concentrates in the United States while procurement friction dominates European compliance markets. German and French enterprises face longer sales cycles due to NIS2 Directive implementation timelines. The United Kingdom and Nordic countries accelerate fastest toward consumption-based cloud SIEM models.
United States
Financial institutions and defense agencies drive premium platform deployments with stringent air-gapped requirements. SEC cybersecurity disclosure rules mandate four-day incident reporting timelines that automate SIEM procurement decisions. New York and Washington DC metro areas host the densest concentration of security operations centers consolidating multi-tool stacks.
Germany
Mid-market manufacturers and critical infrastructure operators navigate NIS2 Directive expansion into logistics and waste management sectors. BSI technical guidelines shape certification requirements for continuous monitoring capabilities. Industrial clusters in Bavaria and Baden-Württemberg prioritize hybrid deployments satisfying data residency without sacrificing cloud analytics elasticity.
United Kingdom
NHS trusts and financial services firms accelerate toward managed security service provider delivery models. NIS2 transposition through UK cybersecurity regulations imposes response automation mandates on critical infrastructure. London's fintech corridor exhibits the fastest migration to consumption-based pricing structures among European financial centers.
India
RBI cyber security frameworks for urban cooperative banks and SEBI mandates for stockbrokers create first-wave SIEM adoption without legacy installation burdens. Bangalore and Hyderabad technology corridors drive multi-tenant platform demand from IT services exporters building North American security operations centers. Domestic data localization requirements favor hybrid architectures with local processing nodes.
Australia
Federal agencies maintain strict procurement preferences for domestically headquartered vendors with sovereign engineering presence. Critical infrastructure operators face tightened incident reporting timelines under Security of Critical Infrastructure Act amendments. Sydney and Melbourne financial centers concentrate demand for compliance management modules mapping to APRA CPS 234 requirements.
Security Information and Event Management Software Market Competitive Landscape
Platform consolidators and point-tool specialists split the market into distinct procurement camps with limited overlap. Incumbent vendors with data analytics heritage anchor premium enterprise deployments while network security fabric providers bundle SIEM for margin protection. Competitive moves concentrate on cloud-native re-engineering and managed service provider channel expansion.
Within the platform consolidation tier, IBM Corporation and Splunk, Inc. exemplify archetypes competing through professional services depth versus data analytics specialization. Fortinet, Inc. occupies a position representing network security fabric bundling strategies. These three entities anchor the competitive structure without exhausting the vendor landscape.
| Leading Market Players |
|---|
| IBM Corporation |
| Splunk, Inc. |
| Hewlett Packard Enterprise |
| Fortinet, Inc. |
| LogRhythm, Inc. |
| Exabeam, Inc. |
| Securonix, Inc. |
| Rapid7, Inc. |
| Datadog |
| Others |
Value Network & Pricing Analysis
United States-based hyperscaler infrastructure providers anchor cloud-native SIEM delivery, concentrating margin capture in the subscription tier while on-premises vendors absorb hardware procurement volatility. This upstream cloud concentration forces traditional software vendors to restructure licensing models or cede mid-market ground to consumption-based rivals.
Pricing Analysis
Configured-to-order enterprise deployments command substantial premiums over standardized SaaS tiers. Subscription-based SaaS pricing dominates procurement, with price differentiation resting on data ingestion volume scales and ISO 27001 certification tiers. Cost compression in the mid-market intensifies as managed security service providers bundle platform fees into flat monthly rates. Healthcare providers exhibit acute price sensitivity due to constrained IT budgets, while financial institutions accept premium pricing for air-gapped customization.
Supply Chain Analysis
United States export-control regimes restrict advanced encryption and machine-learning inference hardware flows to certain jurisdictions, fragmenting vendor engineering footprints. Supply concentrates in the United States, Ireland, and India for software development, with Taiwan and South Korea anchoring specialized security chip fabrication. The ecosystem draws from open-source telemetry libraries, proprietary correlation engines, and cloud compute instances. Single-source vulnerability runs through hyperscaler infrastructure dependencies. Distribution runs through direct enterprise sales teams and managed security service provider channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
SIEM procurement is recovering from cyclical budget freezes as SEC disclosure mandates and EU NIS2 enforcement create non-discretionary compliance spend. Regulatory deadlines function as the cyclical driver forcing platform refresh decisions.
For Market Incumbents: Entrench data analytics differentiation through embedded machine-learning inference capabilities that reduce false-positive rates. Fortify professional services depth to anchor regulated industry deployments against cloud-native challengers. Build vertical integration into threat intelligence feeds to defend margin position as point-tool consolidation accelerates. For New Entrants and Emerging Players: Pursue white-space opportunity in Indian urban cooperative banks and SEBI-regulated stockbrokers facing first-wave compliance mandates without legacy platform displacement costs. Target healthcare providers facing HIPAA enforcement actions with modular compliance management modules. Lead with API-first architectures that accommodate multi-cloud telemetry fragmentation. For Investors and Strategic Acquirers: Capital is best deployed toward cloud-native SIEM specialists with proven consumption-based pricing traction and managed security service provider channel density. Long-term viability favors platforms demonstrating elastic infrastructure economics and automated response workflow maturity. Monitor AI-driven anomaly detection accuracy benchmarks as the inflection signal separating sustainable differentiation from feature parity.| Strategic Initiative | Industry Significance |
|---|---|
| Cloud-Native Platform Migration | Elastic infrastructure provisioning compresses deployment timelines from months to weeks for mid-market enterprises. |
| Managed Security Service Provider Channel Expansion | Third-party SOC staffing resolves skilled analyst scarcity limiting platform utilization rates. |
| AI-Driven Anomaly Detection Investment | Embedded machine learning reduces false-positive rates justifying premium platform upgrades. |
| Compliance Module Diversification | Pre-built GDPR, NIS2, and ISO 27001 templates accelerate certification timelines for mid-market buyers. |
| Hybrid Architecture Development | Split on-premises and cloud processing satisfies data residency mandates without sacrificing computational elasticity. |
Research Methodology
Findings reconcile primary fieldwork against secondary review of SEC cybersecurity disclosure filings, EU NIS2 implementation guidance, vendor earnings statements, and hyperscaler capex disclosures. Primary interviews engaged CISOs at financial institutions, SOC engineering directors, managed security service provider procurement leads, and compliance officers at healthcare networks. Secondary validation drew from ISO 27001 certification databases, regulatory enforcement action records, and cloud infrastructure spending reports. Bottom-up deployment sizing and top-down market aggregation were cross-checked for consistency.
Forecast inputs span deployment architecture, organization size tier, vertical compliance burden, integration complexity level, and regional regulatory adoption pattern. The analytical framework projects value expansion across the modeling period by segmenting procurement behavior across cloud-native, hybrid, on-premises, and managed service delivery modes. CAGRs were derived from regression against compliance mandate enforcement timelines and cloud migration adoption curves. Industry-specific inputs include SEC four-day disclosure workflow automation rates and EU critical infrastructure operator NIS2 compliance deadlines.
Macroeconomic conditions sit as an overlay; deviation in enterprise IT budget cycles and cloud infrastructure pricing volatility would shift the trajectory. Forecasts reflect documented assumptions regarding regulatory enforcement consistency and hyperscaler capacity expansion. Material shifts in export-control regime stringency or sovereign data localization mandates would require updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Intrusion Detection System / Intrusion Prevention System (IDS / IPS) Market
Security Software
Software Protection Dongle Market
Security Software
Global Optical Encryption Market
Security Software
Public Cloud Management and Security Services Market
Security Software
Global Insider Threat Management ITM Software Market
Security Software
Unified Threat Management (UTM) Market
Security Software
Fraud Detection Software Market
Security Software
Enterprise Rights Management Solution Market
Security Software
Quantum Key Distribution System Market
Security Software
Automotive Endpoint Authentication Market
Security Software
Biometric POS Terminals Market
Security Software
AI in Security Market
Security Software
Global Automatic Number Plate Recognition (ANPR) System Market
Security Software
Global User Provisioning Market
Security Software
Europe Encryption Software Market
Security Software
Website Monitoring Software Market