
 Public Cloud in BFSI Market | 2026-2036
Public Cloud in BFSI Market Size, Share, and Industry Trends Forecast 2026-2036
Public Cloud in BFSI Market Analysis
Enterprise-grade security certification is reorganizing vendor selection criteria across financial institutions. Microsoft Corporation leverages its FedRAMP authorization to anchor government-facing banking contracts. Amazon.com Inc. sustains dominance in infrastructure scale, while Google LLC differentiates through AI-integrated analytics platforms for risk modeling.
Public Cloud in BFSI denotes third-party computing environments delivering on-demand infrastructure, platforms, and software services to banking, financial services, and insurance entities via multi-tenant architectures with API-based interoperability and encryption standards. Its primary purpose is replacing capital-intensive on-premise data centers with elastic, consumption-priced resources that support real-time transaction processing and regulatory reporting. SaaS offerings command the deepest margin pools due to recurring subscription structures and embedded workflow automation. Hybrid Cloud deployment is expanding fastest as institutions retain sensitive customer data on private nodes while bursting transactional workloads to public infrastructure. Retail Banks represent the most penetrated client type, though Insurance Companies are closing gaps through claims-processing modernization.
FDA guidelines on algorithmic decision-making, EU GDPR data-localization mandates, and SEC cybersecurity disclosure rules collectively elevate compliance architecture to a primary procurement filter. The EU AI Act adds algorithmic auditing requirements for automated credit-scoring tools deployed on cloud infrastructure. Stakeholders must monitor evolving cross-border data transfer agreements as jurisdictional fragmentation intensifies architectural complexity.
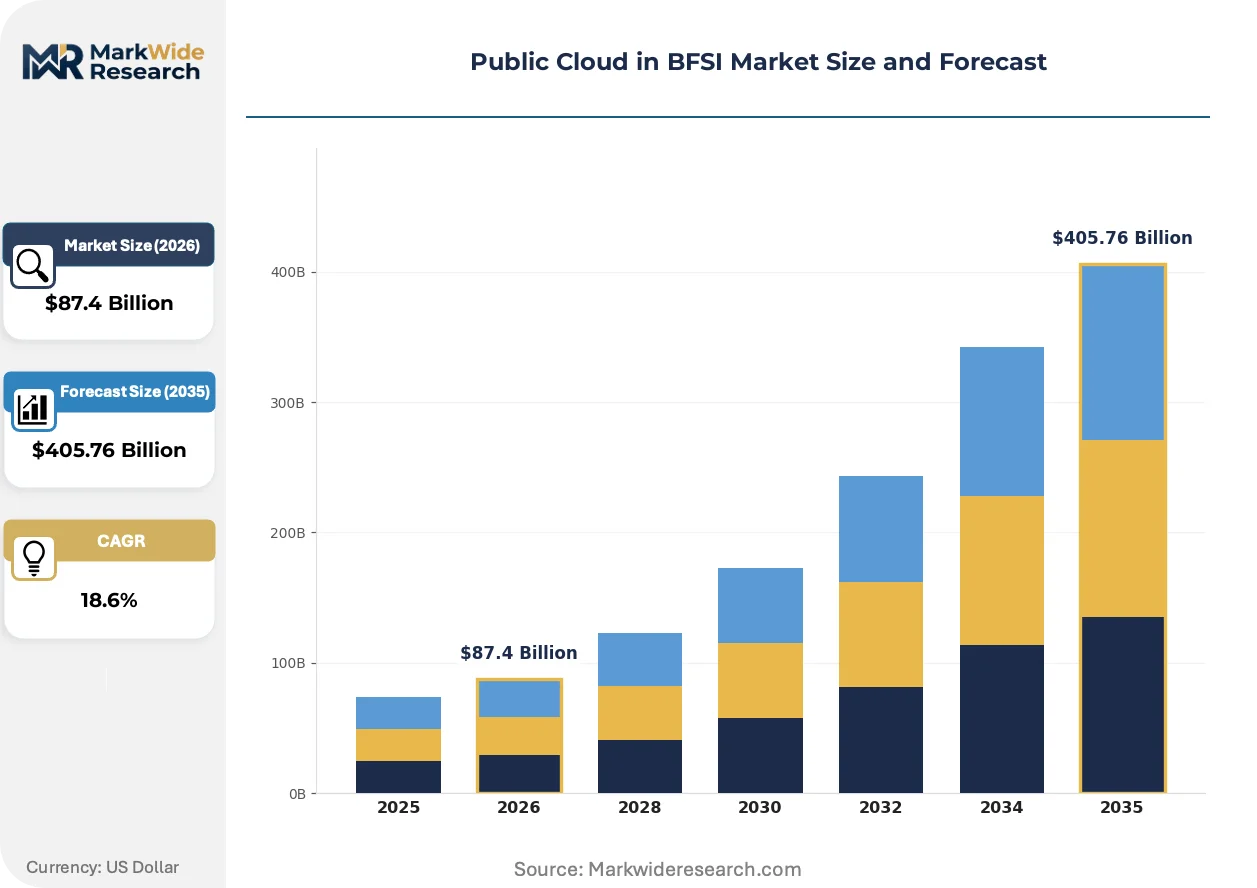
Market Dynamics
The EU Digital Operational Resilience Act is forcing financial institutions to rearchitect cloud deployments around data sovereignty requirements. This regulatory pressure is compressing vendor selection cycles and elevating compliance architecture above cost considerations in procurement decisions.
Growth Catalysts
- Algorithmic Auditing Mandates:The EU AI Act requires automated credit-scoring tools on cloud infrastructure to maintain explainability logs. Insurance carriers and retail banks are upgrading to compliant platforms preemptively.
- Core System Modernization:United States regional banks are replacing legacy mainframes with elastic cloud-native cores to reduce fixed data center costs and enable real-time transaction processing.
- API-First Architectures:Open banking frameworks in the United Kingdom and Australia are mandating standardized interfaces. Cloud providers with embedded API gateways capture embedded workflow automation contracts.
Market Restraints
- Cross-Border Data Fragmentation:Jurisdictional conflicts between GDPR localization rules and US CLOUD Act disclosure requirements create architectural complexity. Institutions must maintain redundant infrastructure across sovereignty zones.
- Specialized Talent Scarcity:Cloud security architects with financial services domain expertise command premium compensation. Smaller institutions face recruitment bottlenecks for FedRAMP and ISO 27001 certification management.
- Legacy Integration Friction:Decades-old COBOL-based core banking systems resist containerization. Migration projects require expensive parallel run periods that strain operational budgets.
Strategic Opportunities
- Claims Processing Modernization:Insurance companies lag retail banks in cloud penetration. Computer vision-enabled damage assessment and automated fraud detection represent greenfield deployment opportunities.
- Quantum-Resistant Cryptography:NIST post-quantum standards are mandating algorithm upgrades. Cloud providers offering managed cryptographic transitions will capture compliance-driven replacement cycles.
- Embedded Finance Expansion:Non-bank platforms deploying lending and payment services require regulated infrastructure. Banking-as-a-Service cloud stacks enable vendor capture of fintech middleware demand.
Industry Challenges
- Multi-Cloud Orchestration Complexity:Institutions deploying across AWS, Azure, and Google Cloud struggle with unified identity management and cost attribution. Kubernetes standardization remains incomplete.
- Third-Party Risk Attestation:Continuous monitoring of subcontractor security postures exceeds internal audit capacity. Supply chain transparency requirements under DORA and SEC rules strain governance frameworks.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Public Cloud in BFSI Market |
| Market Size in 2026 | $87.4 Billion |
| Market Size in 2035 | $405.76 Billion |
| CAGR (2026 – 2036) | 18.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: IaaS, PaaS, SaaS, BPaaS Deployment Model: Multi-Cloud, Hybrid Cloud, Community Cloud, Vertical Cloud Client Type: Retail Banks, Investment Firms, Insurance Companies, Credit Unions Security Level: High Compliance, Standard Compliance, Low Compliance, Custom Compliance |
| Companies Covered | IBM Corporation, Salesforce.com Inc., Amazon.com Inc., Cisco Systems Inc., Hewlett Packard Enterprise Company, Microsoft Corporation, Oracle Corporation, Fujitsu Ltd., Google LLC, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Public Cloud in BFSI Market Emerging Trajectories
Generative AI integration is restructuring how financial institutions evaluate cloud platforms. Risk modeling, customer service automation, and regulatory report generation are converging on infrastructure with native machine learning accelerators.
Confidential computing with hardware-based trusted execution environments is supplanting software-only encryption for high-sensitivity workloads. Tier-1 banks in Germany and Switzerland are adopting Intel SGX and AMD SEV-enabled instances for anti-money-laundering analytics. The technology compresses data residency compliance costs by eliminating cleartext exposure even from cloud administrators.
The EU AI Act's risk-based classification system is mandating algorithmic documentation for automated lending decisions. Cloud providers must now embed model lineage tracking and bias detection APIs into their machine learning platforms. Retail banks deploying credit-scoring tools are prioritizing vendors with pre-certified compliance modules to accelerate deployment timelines.
Consumption-based pricing for infrastructure is displacing reserved instance commitments among mid-size institutions. Regional banks in the United States are adopting FinOps practices to attribute cloud spend to individual product lines. This behavioral shift is most visible in the Southeast, where de novo banks lack legacy procurement processes and negotiate purely on per-transaction economics.
Public Cloud in BFSI Market Segmentation
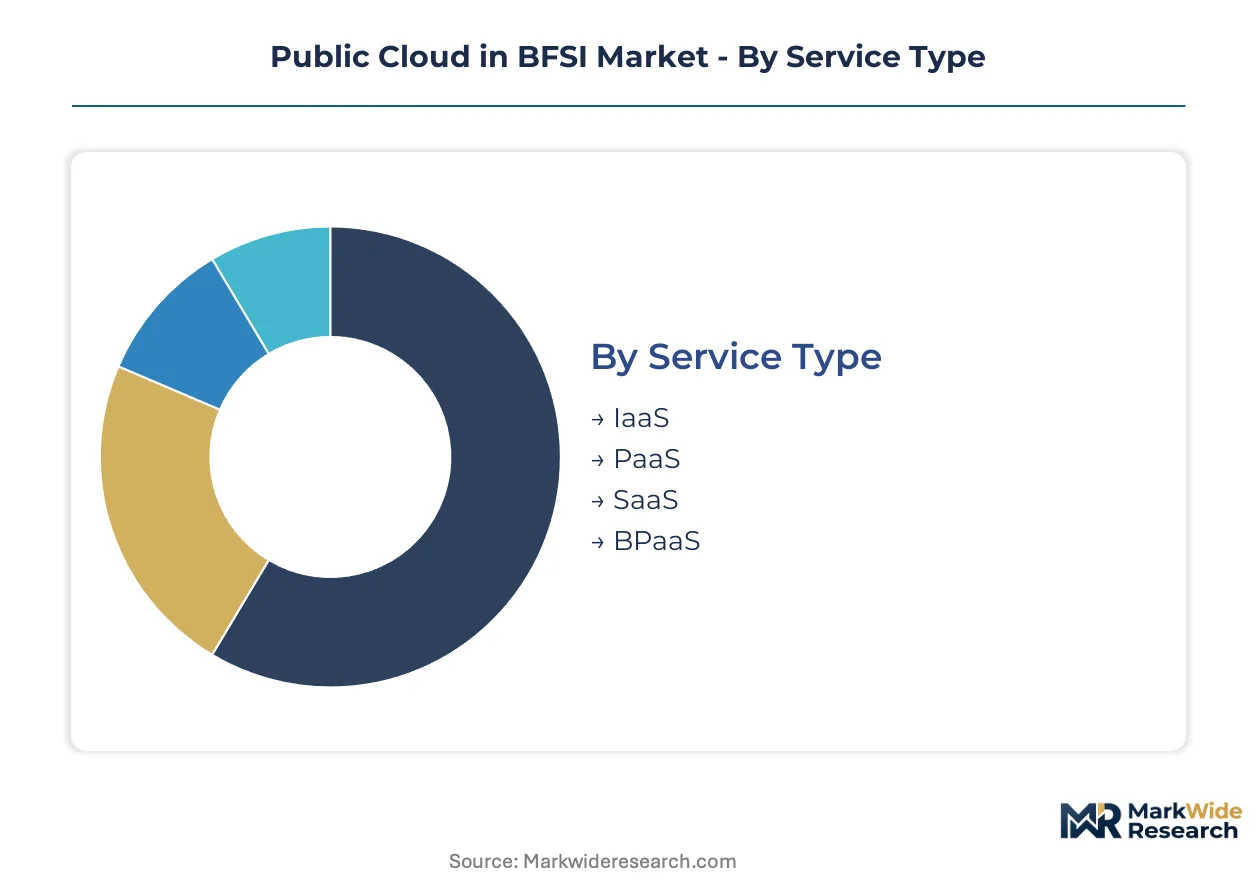
Cloud procurement in banking and financial services fragments across four critical dimensions. Service type determines margin capture and vendor lock-in intensity. Deployment model shapes data sovereignty compliance and workload elasticity. Client type drives customization depth and regulatory scrutiny. Security tier filters vendor eligibility and pricing premiums.
Service Type:
SaaS faces the strongest substitution pressure from vertically integrated fintech platforms building proprietary stacks. IaaS confronts containerization and serverless abstraction threatening commoditization.
- SaaS:Pre-configured applications delivered via subscription with embedded workflow automation for loan origination, compliance reporting, and customer relationship management. Demand concentrates among United States regional banks modernizing core banking without internal development capacity, constrained by EU AI Act algorithmic auditing requirements for automated credit-scoring modules.
- IaaS:Raw compute, storage, and networking resources provisioned on-demand with API-driven orchestration. Investment firms in Frankfurt and Singapore drive consumption for high-frequency trading infrastructure, limited by cross-border data fragmentation between GDPR localization mandates and US CLOUD Act disclosure obligations.
- PaaS:Managed development environments with integrated middleware and database services enabling rapid application deployment.
- BPaaS:Business process outsourcing delivered via cloud infrastructure covering claims processing, payment operations, and regulatory reporting functions.
SaaS retains volume leadership; BPaaS holds the steepest expansion curve as insurers outsource legacy operations.
Deployment Model:
Cost tier segmentation separates capital-intensive private infrastructure from consumption-priced public alternatives. Hybrid Cloud commands premium pricing for sovereignty-compliant architectures.
- Hybrid Cloud:Integrated public-private infrastructure enabling sensitive data retention on private nodes with transactional workload bursting to public capacity. German Tier-1 banks adopt Intel SGX-enabled confidential computing instances for anti-money-laundering analytics, driven by Bundesbank operational resilience guidelines and BaFin data localization enforcement.
- Multi-Cloud:Distributed workloads across AWS, Azure, and Google Cloud to mitigate vendor concentration risk and optimize service-specific capabilities. Large United States money-center banks deploy multi-cloud Kubernetes orchestration for unified identity management, constrained by SEC cybersecurity disclosure rules requiring continuous third-party risk attestation across disparate environments.
- Community Cloud:Shared infrastructure exclusive to regulated financial entities with mutualized compliance costs.
- Vertical Cloud:Industry-specific platforms pre-certified for BFSI regulatory requirements with embedded financial services workflows.
Hybrid Cloud dominates procurement budgets; Vertical Cloud is climbing the fastest as niche vendors capture embedded finance middleware demand.
Client Type:
Application-based segmentation distinguishes transaction-intensive retail operations from risk-analytics-heavy investment activities. Insurance modernization lags, creating greenfield deployment opportunities.
- Retail Banks:Full-service deposit and lending institutions with the deepest cloud penetration and most mature procurement processes. Southeast United States de novo banks negotiate purely on per-transaction economics without legacy procurement friction, though FedRAMP authorization requirements compress vendor shortlists for government-facing contracts.
- Insurance Companies:Property, casualty, and life carriers modernizing claims processing and actuarial systems. Japanese insurers deploy computer vision-enabled damage assessment on cloud infrastructure, constrained by specialized talent scarcity for cloud security architects with financial services domain expertise.
- Investment Firms:Asset managers and broker-dealers requiring low-latency infrastructure for algorithmic trading.
- Credit Unions:Member-owned cooperative banks with limited IT budgets and heightened cybersecurity exposure.
Retail Banks retain volume leadership; Insurance Companies hold the steepest expansion curve through claims-processing modernization.
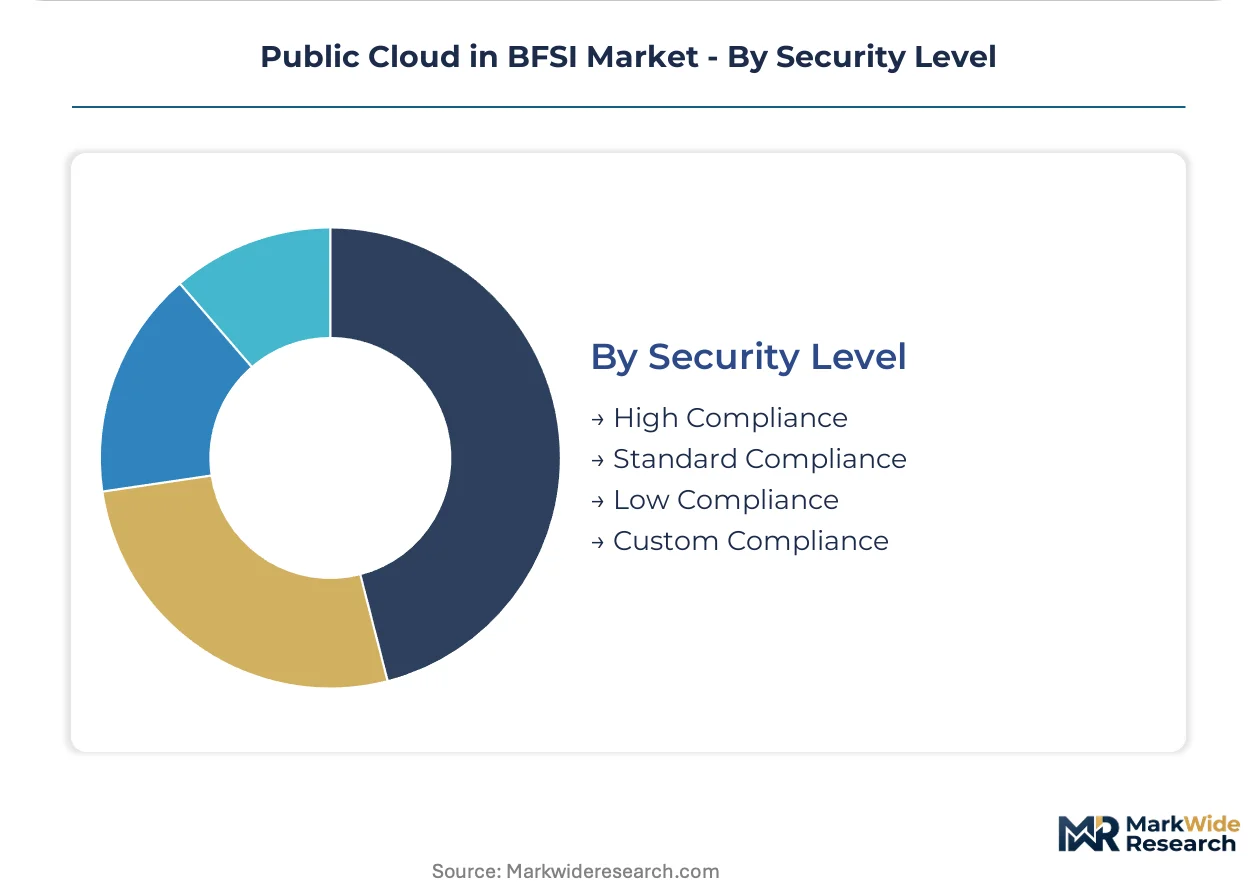
Security Level:
Customer-type segmentation separates regulated institutions with mandatory certification from smaller entities with discretionary compliance investment. High Compliance tiers filter vendor participation and justify pricing premiums.
- High Compliance:Infrastructure meeting FedRAMP High, ISO 27001, and SOC 2 Type II standards with continuous monitoring and audit logging. United States government-facing banking contracts require FedRAMP authorization, with Microsoft Corporation leveraging this certification to anchor federal credit union and treasury services deployments.
- Standard Compliance:Baseline encryption and access controls satisfying regional regulatory minimums without specialized certifications.
- Low Compliance:Basic security configurations appropriate for non-sensitive development and testing environments.
- Custom Compliance:Tailored architectures addressing jurisdiction-specific requirements such as Swiss FINMA outsourcing guidelines or Singapore MAS Technology Risk Management notices.
High Compliance dominates vendor selection criteria; Custom Compliance is gaining share fastest as jurisdictional fragmentation intensifies architectural complexity.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States cloud providers export infrastructure services to financial institutions across Germany, Japan, and Singapore, creating a trade-flow corridor that concentrates procurement decisions in North American headquarters while compliance localization occurs in destination markets.
United States
Regional banks in the Southeast negotiate per-transaction cloud economics without legacy procurement friction. FedRAMP authorization requirements compress vendor shortlists for federal credit union contracts. Dallas and Atlanta financial technology clusters drive de novo bank cloud-native core deployments.
Germany
BaFin data localization enforcement and Bundesbank operational resilience guidelines accelerate confidential computing adoption. Tier-1 banks in Frankfurt deploy Intel SGX-enabled instances for anti-money-laundering analytics. The Rhine-Main financial center concentrates vendor certification investments.
United Kingdom
Open banking frameworks mandate standardized API interfaces for retail payment services. Prudential Regulation Authority outsourcing guidelines elevate continuous monitoring requirements. London's fintech corridor captures embedded finance middleware demand from challenger banks.
Japan
Property and casualty insurers modernize claims processing through computer vision-enabled damage assessment. Financial Services Agency guidelines on third-party risk management constrain vendor selection cycles. Tokyo's insurance district hosts greenfield cloud deployments lagging retail bank penetration.
Singapore
Monetary Authority of Singapore Technology Risk Management notices shape cross-border data architecture decisions. Investment firms consume low-latency infrastructure for algorithmic trading connectivity to Asian markets. The Marina Bay financial center anchors regional cloud procurement for Southeast Asian expansion.
Public Cloud in BFSI Market Vendor Landscape
Listed leaders compete with private specialists across security certification tiers, creating a bifurcated structure where scale advantages concentrate in publicly traded entities while compliance depth differentiates private operators. The vendor base organizes around three strategic archetypes: hyperscale infrastructure providers with government authorization portfolios, enterprise software incumbents with embedded financial services workflows, and specialized security vendors with confidential computing capabilities. Dominant competitive moves include strategic partnerships for multi-cloud orchestration and portfolio diversification into quantum-resistant cryptographic services.
Within the hyperscale tier, Amazon.com Inc., Microsoft Corporation, and Google LLC exemplify divergent positioning strategies. Amazon.com Inc. anchors infrastructure scale dominance through elastic compute provisioning. Microsoft Corporation occupies a position defined by FedRAMP-authorized government-facing banking contracts. Google LLC represents the AI-integrated analytics vector for risk modeling workloads. These three entities collectively illustrate how certification depth, computational scale, and machine learning specialization create non-overlapping competitive territories within financial services cloud procurement.
| Leading Market Players |
|---|
| IBM Corporation |
| Salesforce.com Inc. |
| Amazon.com Inc. |
| Cisco Systems Inc. |
| Hewlett Packard Enterprise Company |
| Microsoft Corporation |
| Oracle Corporation |
| Fujitsu Ltd. |
| Google LLC |
| Others |
Supply Flow & Price Mechanics
Consumption-based pricing contracts anchor procurement decisions for mid-size institutions, locking in supply access through elastic capacity reservations while compressing margin visibility for vendors competing on per-transaction economics. This structure concentrates pricing power with hyperscale providers in the United States while fragmenting procurement leverage across regional banks and insurers.
Pricing Analysis
Next-generation confidential computing instances command substantial premiums over standard encryption tiers, while prior-generation reserved instance commitments face displacement by FinOps-attributed consumption models. Three-tier pricing structure across FedRAMP-authorized premium, ISO 27001-certified standard, and baseline economy levels separates vendor eligibility tiers. Pricing pressure stems from containerization commoditizing raw compute resources as serverless abstraction spreads. Regional banks in the United States Southeast exhibit highest price sensitivity through pure per-transaction negotiation, while Tier-1 German banks show lowest sensitivity given BaFin-mandated compliance investments.
Supply Chain Analysis
Inventory lead times for specialized financial services cloud architects extend substantially beyond standard infrastructure provisioning cycles, constraining rapid deployment capacity. Supply concentrates in the United States, Germany, and Singapore as primary infrastructure hubs, with secondary specialization clusters in Japan for insurance workloads. The ecosystem draws from scarce talent pools in cryptography, regulatory compliance, and legacy system integration. Single-source vulnerability permeates FedRAMP authorization pathways where only select vendors qualify for federal contracts. Distribution runs through direct enterprise sales teams supplemented by systems integrators with financial services domain expertise.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Incumbents face substitution pressure from vertically integrated fintech platforms building proprietary cloud stacks, requiring defensive repositioning around compliance depth and sovereign infrastructure control.
For Market Incumbents: Consolidate certification portfolios around FedRAMP High and EU DORA-aligned architectures to anchor government-facing contracts against emerging sovereign cloud alternatives. Deepen vertical integration into confidential computing hardware partnerships with Intel and AMD to differentiate from commodity infrastructure providers. This counters fintech platforms bypassing third-party cloud entirely through captive infrastructure development.
For New Entrants and Emerging Players: Claims processing modernization in Japanese and Southeast Asian insurance markets represents an under-served service layer where hyperscale providers lack localized actuarial workflow expertise. Target this segment through pre-configured BPaaS modules with embedded computer vision and fraud detection APIs. A channel partnership strategy with regional systems integrators accelerates compliance navigation without direct certification investment.
For Investors and Strategic Acquirers: Capital is best deployed toward specialized security vendors with confidential computing capabilities and existing FedRAMP authorization, positioned for quantum-resistant cryptographic transition cycles. Long-term viability rests on algorithmic auditing infrastructure mandated by EU AI Act enforcement timelines. The signal to watch is Bundesbank operational resilience guideline adoption rates as a proxy for confidential computing demand inflection.
| Strategic Initiative | Industry Significance |
|---|---|
| Confidential Computing Deployment | Intel SGX-enabled instances satisfy BaFin data localization for Frankfurt Tier-1 banks. |
| FedRAMP Authorization Expansion | Microsoft leverages High certification to anchor federal credit union contracts. |
| Algorithmic Auditing Platform Integration | EU AI Act compliance modules accelerate retail bank credit-scoring deployments. |
| Multi-Cloud Orchestration Partnership | Kubernetes standardization addresses SEC cybersecurity disclosure attestation burdens. |
| Quantum-Resistant Cryptography Service Launch | NIST post-quantum standards drive managed cryptographic transition demand. |
Methodological Framework
Cross-validation between primary executive interviews and secondary regulatory filings anchors the qualitative findings in documented compliance trajectories. Chief technology officers at regional banks, cloud security architects with FedRAMP certification experience, insurance claims modernization directors, and regulatory affairs specialists at EU financial institutions provided operational perspective. Secondary sources include SEC cybersecurity disclosure filings, BaFin outsourcing guidance documents, EU AI Act implementation texts, and hyperscaler infrastructure capex disclosures. Bottom-up service-type demand modeling and top-down regional macroeconomic triangulation constrain estimate variance.
Sensitivity analysis around regulatory enforcement timelines and technology adoption curves shapes the analytical framework across the projection horizon. Segmentation dimensions encompass service type, deployment model, client type, security compliance tier, and regional regulatory cluster. CAGRs derive from fitted adoption curves against historical cloud migration patterns in adjacent regulated industries. Forecast inputs incorporate EU DORA implementation pacing and NIST post-quantum standard finalization schedules.
Material uncertainties — regulatory fragmentation acceleration, quantum computing timeline advancement, and sovereign cloud mandate expansion — sit outside the modeled envelope. Forecasts reflect assumptions about cross-border data transfer agreement stability and legacy system containerization feasibility. Outputs are directional rather than point-estimates.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cloud Computing
Cloud Based-Batch Processing Market
Cloud Computing
Global Cloud Based ITSM Market
Cloud Computing
Multi-Cloud Networking Market
Cloud Computing
Germany Cloud Computing Market
Cloud Computing
Cloud Database Market
Cloud Computing
Cloud VPN Market
Cloud Computing
Government Cloud Market
Cloud Computing
Cloud-Managed LAN Market
Cloud Computing
India Cloud Computing Market
Cloud Computing
Japan Cloud Computing Market
Cloud Computing
Bare Metal Cloud Service Market
Cloud Computing
Multi-Cloud Architecture Market
Cloud Computing
Middle East and Africa Cloud Infrastructure Services Market
Cloud Computing
Cloud Enablement Market
Cloud Computing
Hadoop-As-A-Service (Haas) Market
Cloud Computing
Cloud Computing Market