
 Incident Response System Market | 2026-2036
Incident Response System Market Size, Share, and Industry Trends Forecast 2026-2036
Incident Response System Market Outlook
Modular bundling of threat detection with automated remediation is rebalancing how enterprises evaluate vendor proposals. Cisco Systems leverages its network hardware footprint to embed response capabilities directly into routing infrastructure. CrowdStrike Holdings anchors its growth in cloud-native endpoint protection with integrated incident workflows. Rapid7 specializes in vulnerability management platforms that feed directly into prioritized response queues.
An incident response system comprises software platforms, hardware appliances, and managed service workflows engineered to detect, analyze, contain, and eradicate cybersecurity breaches against defined recovery time objectives. These systems integrate with SIEM pipelines, SOAR orchestration layers, and forensic analysis tools to minimize business disruption from advanced persistent threats. Software solutions dominate current revenue as organizations prioritize scalable detection logic over capital-intensive hardware refresh cycles. Cloud-based deployment expands fastest among mid-market buyers seeking elastic compute for behavioral analytics. Managed services capture expanding margin pools as skills shortages push internal security teams toward outsourced tier-1 response handling.
The U.S. SEC mandates public companies disclose material cybersecurity incidents within four business days under its 2023 disclosure rules, compressing response timelines and elevating demand for automated classification tools. The EU NIS2 Directive extends incident reporting obligations to critical sectors including energy, transport, and digital infrastructure across member states. ISO 27035 provides the foundational framework for national regulators in Japan and South Korea to benchmark organizational response maturity. Stakeholders must weigh vendor consolidation against best-of-breed interoperability as regulatory fragmentation intensifies across jurisdictions.
Market Dynamics
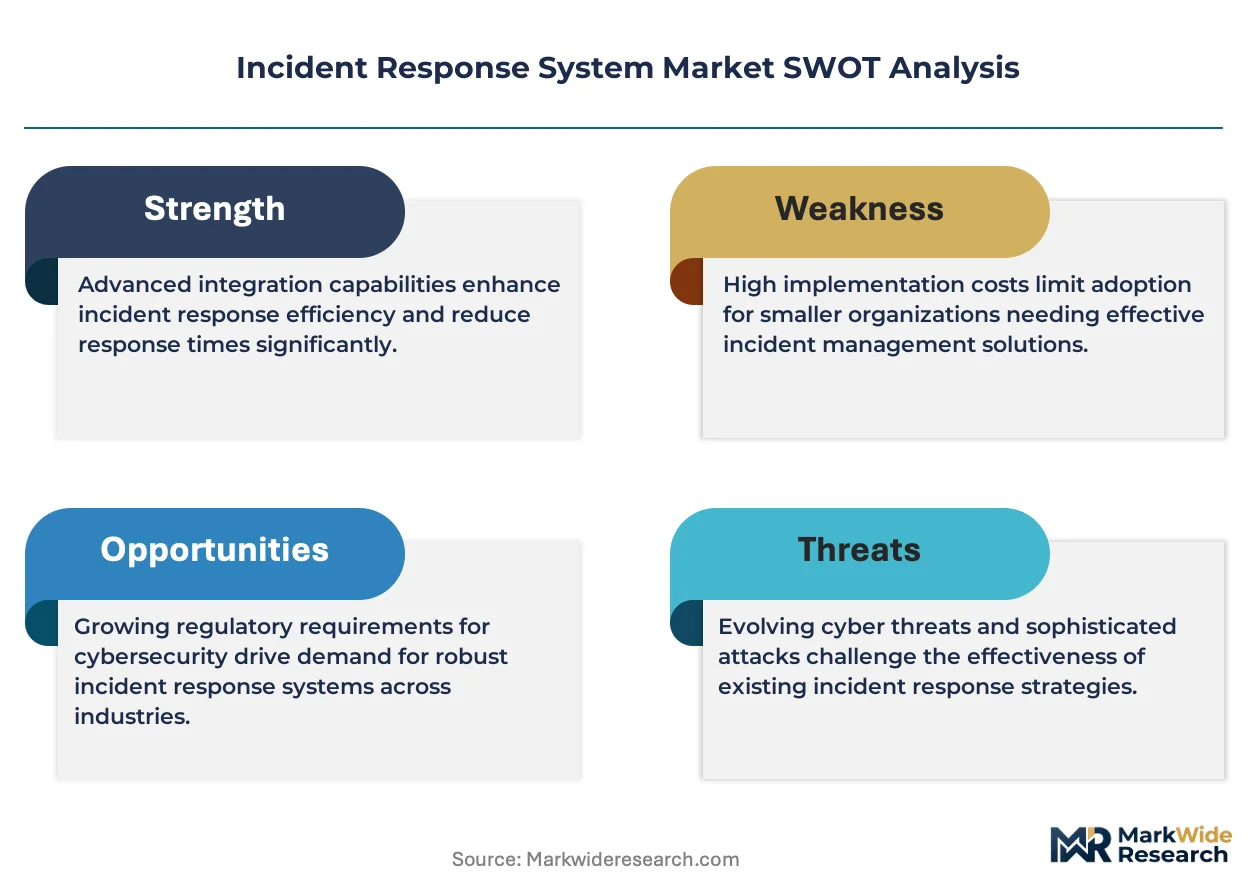
Automated orchestration layers are compressing mean-time-to-response from hours to minutes across enterprise security stacks. SOAR platforms now embed machine learning classifiers that trigger containment workflows without human intervention, fundamentally altering staffing models and vendor evaluation criteria.
Growth Catalysts
- EU NIS2 Directive:Mandatory 24-hour incident reporting windows for critical infrastructure operators are forcing procurement of real-time detection pipelines. Energy and transport operators in Germany, France, and Italy face the tightest compliance deadlines.
- Healthcare digitization:Hospital systems deploying connected medical devices generate attack surfaces requiring automated response protocols. Patient safety regulations now tie clinical system availability to cybersecurity maturity benchmarks.
- Cloud-native architectures:Containerized workloads and serverless functions demand response tools that operate at API speed rather than host-agent latency. Mid-market enterprises bypass on-premise SIEM investments entirely.
Market Restraints
- Specialized talent scarcity:Certified incident responders command premium compensation that exhausts security budgets at organizations below 5,000 employees. Training pipelines produce fewer qualified analysts than replacement demand requires.
- Vendor consolidation risk:Three platform providers control the majority of SOAR orchestration engines. Buyers face lock-in costs when switching between incompatible playbook formats.
- False positive fatigue:Detection engines generating excessive alerts degrade analyst attention and delay genuine threat response. Tuning automated systems demands scarce expertise.
Strategic Opportunities
- Operational technology convergence:Manufacturing and utility sectors merge IT response workflows with industrial control system monitoring. Converged platforms address the air-gap erosion between enterprise networks and SCADA environments.
- Japan's critical infrastructure hardening:METI guidelines for supply chain cybersecurity create demand for managed detection and response services among second-tier industrial conglomerates.
- API-first integration architectures:Open response playbooks allowing custom webhook triggers enable vertical-specific solutions without full platform replacement. Insurance underwriters increasingly mandate demonstrable automation.
Industry Challenges
- Forensic evidence preservation:Automated containment actions often destroy volatile memory artifacts required for attribution and legal proceedings. Balancing speed with evidentiary integrity demands architectural trade-offs.
- Multi-cloud complexity:Response coordination across AWS, Azure, and Google Cloud environments requires normalized telemetry formats that no single vendor fully provides. Cross-cloud playbooks remain manually intensive.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Incident Response System Market |
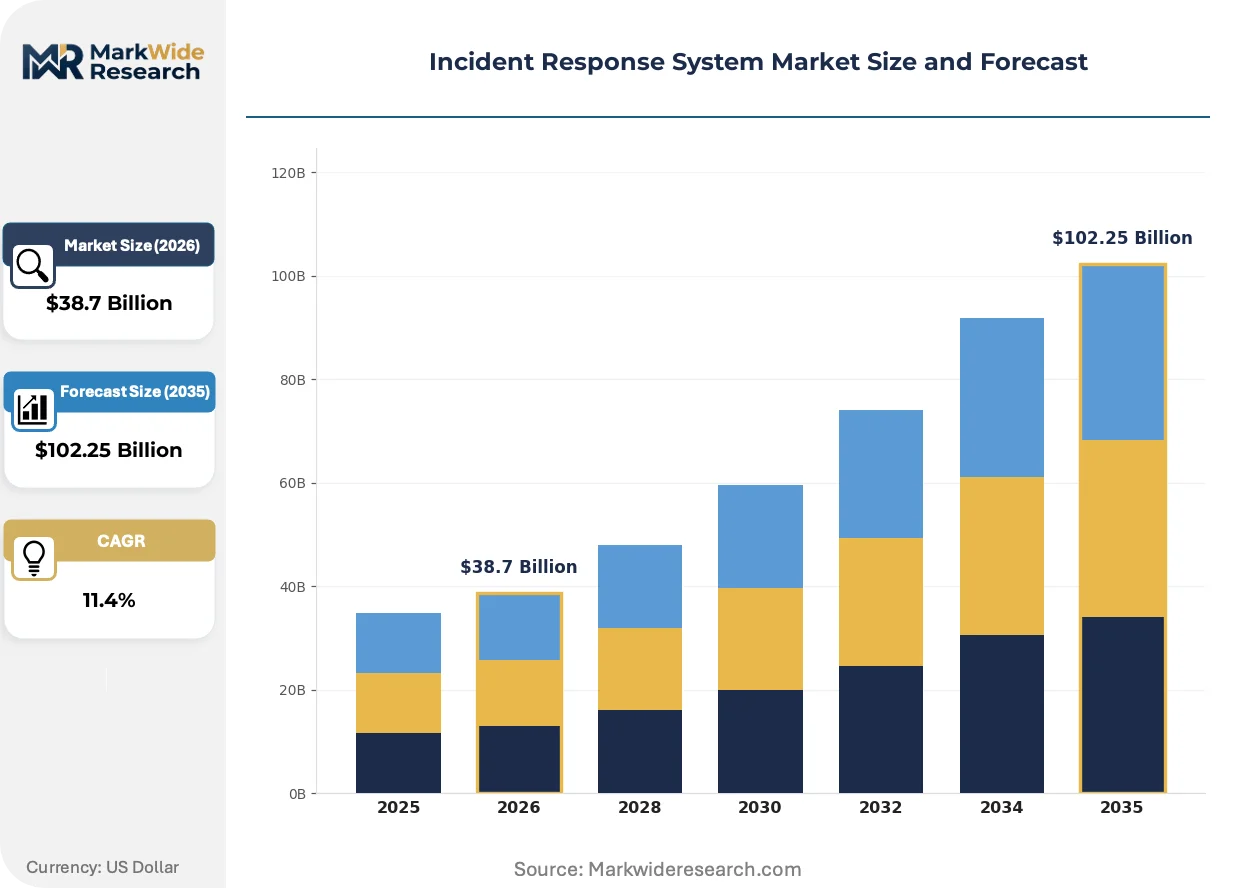
| Market Size in 2026 | $38.7 Billion |
| Market Size in 2035 | $102.25 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Software Solutions, Hardware Devices, Managed Services, Consulting Services End User: Government Agencies, Healthcare Institutions, Financial Services, Educational Organizations Deployment: On-Premise, Cloud-Based, Hybrid, Virtualized Application: Threat Intelligence, Network Security, Incident Management, Compliance Management |
| Companies Covered | IBM, Cisco Systems, CrowdStrike Holdings, Check Point Software Technologies, Rapid7, LogRhythm, Swimlane, Resolve Systems, FireEye, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Incident Response System Market Strategic Shifts
Extended detection and response architectures are dissolving the boundary between endpoint agents and network telemetry. Vendors now compete on the depth of automated remediation rather than detection sophistication alone.
Autonomous response engines are expanding into mid-market security stacks. These systems execute predefined containment actions—isolate hosts, revoke credentials, block IPs—without analyst approval during off-hours. Small and medium enterprises in the United States and Germany adopt these capabilities fastest, trading control for coverage gaps. The technology is expanding into managed service provider portfolios as a differentiated tier.
The EU AI Act imposes risk classification requirements on security automation tools using machine learning for threat scoring. High-risk systems must maintain human oversight mechanisms and audit trails for automated decisions. Financial services institutions across the Netherlands, Spain, and Sweden are rebuilding response workflows to satisfy explainability mandates before the 2025 enforcement window.
Security teams now purchase incident response retainers as standalone budget line items separate from annual software licensing. Large enterprises in Japan negotiate multi-year managed service contracts with guaranteed analyst response times. This unbundling pressures pure-play software vendors to build service delivery capabilities or cede margin to consulting partners.
Incident Response System Market Segmentation
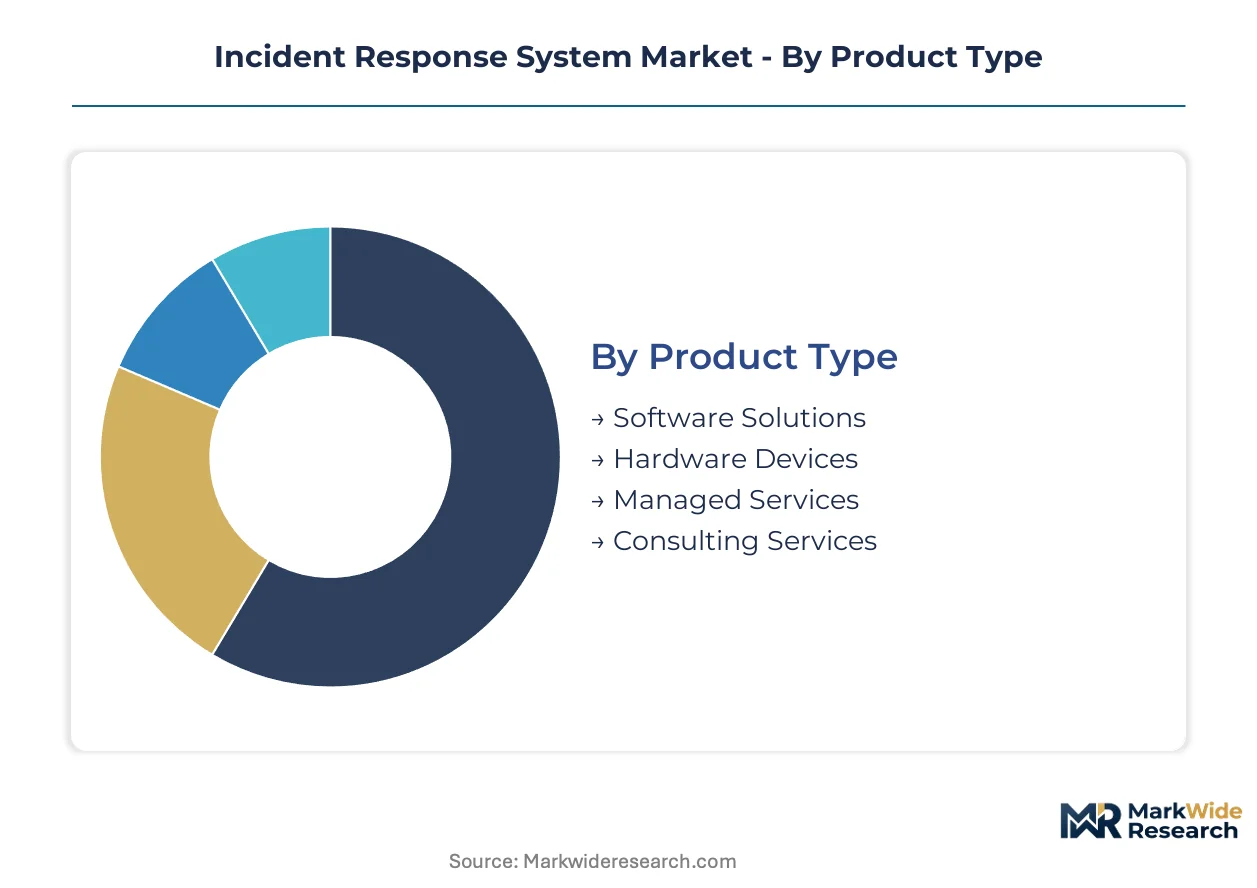
Segmentation in the incident response market reveals how procurement priorities diverge across compliance maturity levels and infrastructure complexity. Buyers select product configurations based on regulatory exposure, existing security stack investments, and internal analyst capacity rather than uniform feature comparisons.
Product Type:
Certification burdens vary sharply across product categories, with hardware appliances facing the most stringent Common Criteria and FIPS 140-2 validation requirements for government deployment.
- Software Solutions:Cloud-deployed detection engines and SOAR platforms dominate procurement volumes among enterprises prioritizing scalable logic over capital expenditure. Healthcare institutions in Germany and the United States favor subscription models that align spending with patient data protection mandates. Software Solutions sits at the top of the volume ranking, with Managed Services climbing the fastest.
- Hardware Devices:Network-tap appliances and forensics workstations require physical installation and air-gapped operation for sensitive environments. Defense contractors and critical infrastructure operators in Japan specify tamper-evident hardware for SCADA-adjacent deployments.
- Managed Services:Outsourced tier-1 response handling addresses certified analyst shortages at mid-market enterprises. Financial services firms in the Netherlands contract guaranteed response-time SLAs to satisfy DNB supervisory expectations.
- Consulting Services:Retainer-based advisory supports tabletop exercises and breach readiness assessments. Educational organizations leverage consulting to bridge capability gaps without permanent security hires.
Software Solutions sits at the top of the volume ranking, with Managed Services climbing the fastest.
End User:
Cost tier segmentation separates buyers by security budget scale and regulatory penalty exposure, with financial services allocating the highest per-employee spending on automated response capabilities.
- Government Agencies:National cybersecurity centers and defense ministries mandate sovereign data processing and domestic vendor preferences. German federal agencies align procurement with BSI technical guidelines for critical infrastructure protection.
- Healthcare Institutions:Hospital systems and pharmaceutical manufacturers balance patient safety continuity with HIPAA and GDPR breach notification timelines. Connected medical device proliferation expands attack surface monitoring requirements across European and Japanese health networks.
- Financial Services:Banks and insurers face the steepest regulatory automation mandates under SEC disclosure rules and EU AI Act risk classifications. Dutch and Spanish institutions rebuild workflows to satisfy explainability requirements before enforcement windows.
- Educational Organizations:Universities and research institutions operate with constrained budgets and distributed IT governance. Ransomware targeting student records drives demand for affordable managed detection services in the United States.
Financial Services commands the highest per-endpoint spending, with Healthcare Institutions expanding procurement most aggressively.
Deployment:
Maturity-stage segmentation distinguishes early cloud adopters from organizations maintaining legacy on-premise investments for data residency compliance.
- On-Premise:Air-gapped installations persist in defense, intelligence, and nuclear energy sectors where external connectivity is prohibited. Japanese utilities specify on-premise SOAR to satisfy METI supply chain cybersecurity guidelines.
- Cloud-Based:Serverless detection architectures eliminate host-agent latency for containerized workloads. Mid-market enterprises in Germany bypass on-premise SIEM investments entirely in favor of elastic compute for behavioral analytics.
- Hybrid:Split architectures preserve sensitive data on-premise while leveraging cloud analytics for threat intelligence correlation. Large manufacturers converge IT response workflows with industrial control system monitoring across hybrid estates.
- Virtualized:Software-defined security stacks enable rapid playbook replication across distributed environments. Managed service providers deploy virtualized response nodes to serve multiple tenants from shared infrastructure.
Cloud-Based deployment gains share fastest among new buyers, though Hybrid retains dominance in regulated sectors with legacy infrastructure.
Application:
Application segmentation tracks functional priority shifts as buyers reallocate budget from perimeter defense toward automated remediation and compliance documentation.
- Threat Intelligence:Real-time indicator feeds and attribution databases accelerate classification decisions. Energy operators in Italy integrate threat intelligence with automated containment to satisfy NIS2 directive timelines.
- Network Security:East-west traffic monitoring and microsegmentation enforcement contain lateral movement. Cisco embeds response capabilities directly into routing infrastructure, rebalancing vendor evaluation criteria.
- Incident Management:Case management workflows and forensic evidence preservation balance speed with legal admissibility. Automated containment actions often destroy volatile memory artifacts, demanding architectural trade-offs in financial services.
- Compliance Management:Audit trail generation and regulatory reporting automation compress disclosure preparation. SEC four-day material incident rules elevate demand for automated classification tools at US public companies.
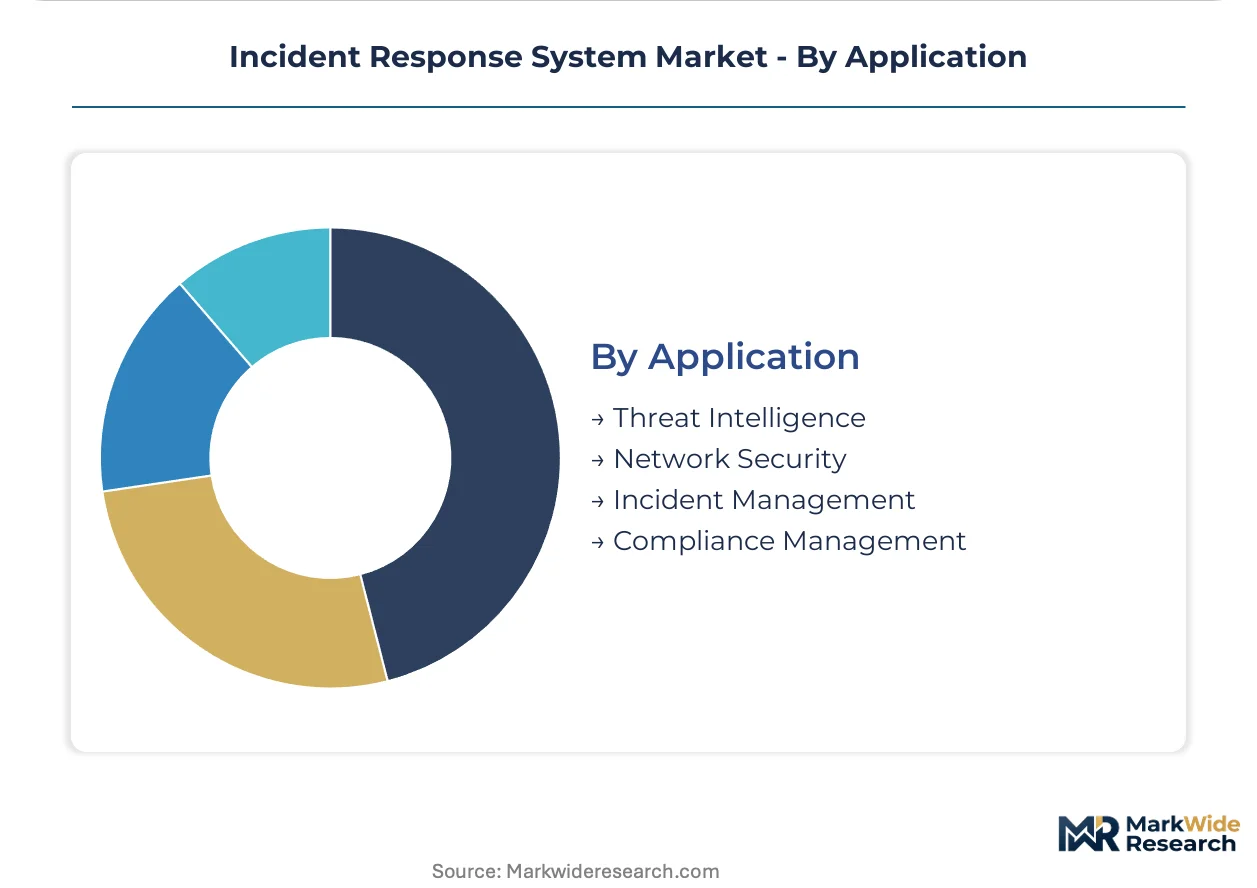
Incident Management captures the largest current revenue share, with Compliance Management expanding most quickly under tightening regulatory timelines.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Incident response systems originated in United States defense and intelligence infrastructure before commercializing through financial services compliance mandates. The technology diffused to European critical infrastructure operators under NIS Directive obligations. Japanese industrial conglomerates adopted managed detection services following METI supply chain security guidelines.
United States
SEC disclosure rules compressing material incident reporting to four business days drive automated classification procurement. HIPAA breach notification timelines push hospital systems toward subscription-based detection platforms. Financial services clusters in New York and Chicago anchor the highest per-endpoint spending on integrated response workflows.
Germany
BSI technical guidelines for critical infrastructure protection mandate sovereign data processing for federal agencies. Energy and transport operators face the EU NIS2 Directive's tightest 24-hour reporting compliance deadlines. Industrial manufacturing concentration in Bavaria and North Rhine-Westphalia accelerates converged IT-OT response platform adoption.
Japan
METI supply chain cybersecurity guidelines create demand for managed detection and response among second-tier industrial conglomerates. Patient safety regulations tie clinical system availability to cybersecurity maturity benchmarks in hospital networks. Tokyo and Osaka metropolitan areas concentrate cloud-native response tool procurement for containerized workloads.
Netherlands
DNB supervisory expectations for financial services institutions mandate guaranteed response-time SLAs in managed service contracts. EU AI Act explainability requirements force rebuilding of automated threat scoring workflows before enforcement windows. Amsterdam's fintech cluster drives API-first integration architectures for cross-cloud response coordination.
Italy
NIS2 directive timelines pressure energy operators to integrate threat intelligence with automated containment systems. Healthcare digitization across Lombardy and Emilia-Romagna expands attack surface monitoring for connected medical devices. Rome-based government agencies specify hybrid deployment models preserving sensitive data on-premise while leveraging cloud analytics.
Incident Response System Market Competitive Environment
Premium-margin players sit above commodity-margin players across orchestration engine sophistication and analyst response time guarantees. Three platform providers control the majority of SOAR orchestration engines, creating vendor lock-in costs for buyers switching between incompatible playbook formats. Network hardware incumbents embed response capabilities directly into routing infrastructure, while cloud-native specialists anchor growth in endpoint protection with integrated workflows. Dominant competitive moves include M&A for SOAR engine consolidation and strategic partnerships bridging IT-OT convergence requirements.
Within the network-embedded tier, Cisco Systems exemplifies hardware footprint leverage for response capability distribution. Cloud-native specialists CrowdStrike Holdings and Rapid7 occupy positions at the detection-automation frontier, with the former representing endpoint-centric workflow integration and the latter exemplifying vulnerability-to-response pipeline specialization. These three anchors illustrate the strategic divergence between infrastructure-embedded, endpoint-native, and analytics-driven archetypes competing for enterprise procurement budgets.
| Leading Market Players |
|---|
| IBM |
| Cisco Systems |
| CrowdStrike Holdings |
| Check Point Software Technologies |
| Rapid7 |
| LogRhythm |
| Swimlane |
| Resolve Systems |
| FireEye |
| Others |
Value Chain & Pricing Dynamics
Semiconductor price indices for AI accelerators and memory modules cascade through incident response system manufacturing, compressing margins on hardware appliances while expanding pricing power for cloud-native software tiers that minimize silicon dependencies.
Pricing Analysis
Subscription-based SaaS tiers with usage-scaled compute pricing dominate procurement, separating enterprise-grade SOAR orchestration from mid-market detection-only packages. Price differentiation rests on SOC 2 Type II certification status and guaranteed analyst response SLAs. Cost compression in the hardware appliance tier intensifies as GPU shortages ease and buyers shift capital toward elastic cloud consumption. Educational organizations exhibit highest price sensitivity, while financial services institutions accept premium positioning for explainable automation under EU AI Act mandates.
Supply Chain Analysis
Domestic-content mandates under the EU Cybersecurity Act and Japan's METI supply chain guidelines are reshaping sourcing decisions for federal and critical infrastructure deployments. Component manufacturing concentrates in Taiwan for advanced semiconductors, the United States for specialized forensic workstations, and Germany for industrial-grade network appliances. Raw material dependencies span rare earth elements for magnetic storage, high-purity silicon for processing units, and specialized alloys for tamper-evident hardware enclosures. Single-source vulnerability in advanced node chip fabrication poses structural risk. Distribution runs through direct enterprise sales for large accounts and managed service provider channels for mid-market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Margin expansion in incident response systems stems from software-subscription scaling that decouples revenue growth from hardware bill-of-materials exposure.
For Market Incumbents: Acquire specialized SOAR playbook engines to consolidate orchestration market share against cloud-native challengers. Cisco Systems exemplifies network-embedded response capability distribution that hardware incumbents should replicate. Certification investment in Common Criteria and FIPS 140-2 validation preserves federal procurement access against emerging entrants lacking government sales infrastructure. For New Entrants and Emerging Players: Begin with API-first response automation targeting mid-market manufacturers in Germany and Japan seeking IT-OT convergence without full platform replacement. Healthcare institutions in Italy and the Netherlands represent the most penetrable segment due to patient-safety regulations mandating cybersecurity maturity benchmarks. Channel partnerships with regional managed service providers accelerate credibility without direct enterprise sales overhead. For Investors and Strategic Acquirers: Asymmetric upside sits with cloud-native endpoint specialists possessing integrated incident workflows rather than point-solution detection vendors. Long-term viability favors platforms demonstrating cross-cloud response coordination capabilities as multi-cloud complexity intensifies. Watch for EU AI Act enforcement triggering consolidation among machine-learning threat-scoring providers lacking human-oversight audit trails.| Strategic Initiative | Industry Significance |
|---|---|
| SOAR Engine Acquisition | Consolidates orchestration market share against fragmented playbook formats. |
| Federal Certification Investment | Unlocks BSI and NIST procurement pathways for critical infrastructure operators. |
| API-First Integration Architecture | Enables vertical-specific solutions without full platform replacement cycles. |
| Managed Service Provider Partnership | Extends reach into mid-market segments with certified analyst shortages. |
| IT-OT Convergence Platform Development | Addresses air-gap erosion between enterprise networks and SCADA environments. |
Study Parameters
Multiple input streams — primary interviews with CISOs and SOC directors, procurement data from healthcare and financial services GPOs, regulatory filing analysis — were reconciled against hyperscaler security capex disclosures and channel partner volume reports. Bottom-up triangulation across deployment model, organization size, vertical industry, and integration complexity dimensions validated top-down market sizing derived from vendor revenue disclosures and managed service contract value estimates.
Data-stream reconciliation anchored volume projections to elastic compute consumption patterns for cloud-based deployment and capital expenditure cycles for on-premise hardware refresh. Segmentation modeling spanned product type, end-user industry, deployment architecture, and application function across the analysis window. CAGRs were derived from regression analysis of historical procurement velocity against regulatory deadline compression. Forecast inputs incorporated NIS2 directive compliance timelines and SEC disclosure rule enforcement patterns.
Several conditions sit outside the modeled scope, including black-swan supply chain disruptions, sovereign data localization mandates beyond current EU and Japanese frameworks, and breakthrough quantum-computing threats rendering existing encryption-based response protocols obsolete. A small set of named triggers warrants ongoing watch: EU AI Act explainability enforcement actions, METI supply chain guideline expansion to additional industrial sectors, and hyperscaler security product bundling strategies.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Disaster Recovery Solutions
France Ransomware Protection Market
Disaster Recovery Solutions
Global Data Resiliency Market
Disaster Recovery Solutions
Rescue Pole Market
Disaster Recovery Solutions
Italy Ransomware Protection Market
Disaster Recovery Solutions
Rope Rescue Harness Market
Disaster Recovery Solutions
Global Data Protection and Recovery Solutions Market
Disaster Recovery Solutions
Disaster Preparedness Systems Market
Disaster Recovery Solutions
Incident Response Services Market
Disaster Recovery Solutions
Intelligent Emergency Response Systems and Infrastructure (IRIS) Market
Disaster Recovery Solutions
Spain Ransomware Protection Market
Disaster Recovery Solutions
Business Continuity Management Solutions Market
Disaster Recovery Solutions
Incident and Deviation Management Solution Market
Disaster Recovery Solutions
Global Incident Response Market
Disaster Recovery Solutions
Flood Protection Sandbags Market
Disaster Recovery Solutions
Latin America Incident Response Services Market
Disaster Recovery Solutions
Global Disaster Recovery Software Market