
 Healthcare Cybersecurity Market | 2026-2036
Healthcare Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Healthcare Cybersecurity Market Analysis
Multi-source procurement of security tools is restructuring how health systems build cyber resilience. Cisco Systems anchors its position through deep network-layer integration with hospital infrastructure. Palo Alto Networks competes via cloud-native platforms that consolidate fragmented point solutions. CrowdStrike differentiates with endpoint detection capabilities tailored to medical device environments.
Healthcare cybersecurity encompasses technologies, processes, and controls designed to protect electronic health records, medical devices, and clinical networks from unauthorized access, disruption, or data exfiltration, with core specifications including AES-256 encryption, real-time threat detection latencies under 100 milliseconds, and zero-trust network segmentation. Its primary purpose is ensuring continuity of patient care while preserving data confidentiality under stringent privacy mandates. Endpoint Security dominates current health system spending as ransomware targeting workstations and infusion pumps intensifies. Cloud Security represents the fastest-expanding deployment category as telehealth platforms and picture archiving systems migrate off-premises. Managed Security Services capture expanding margin pools as rural hospitals and specialty clinics lack in-house security operations centers.
The FDA's premarket cybersecurity guidance, HIPAA Security Rule enforcement by the Office for Civil Rights, and state-level breach notification laws collectively elevate baseline spending on risk assessment and incident response capabilities. Noncompliance penalties now exceed remediation costs, flipping procurement economics toward prevention. Stakeholders must monitor emerging FDA requirements for software bill of materials in connected medical devices to anticipate supplier qualification shifts.
Market Dynamics
Health system consolidation is compressing procurement cycles and forcing enterprise-grade security architectures onto mid-sized hospitals that previously relied on fragmented point solutions.
Growth Catalysts
- FDA premarket cybersecurity guidance:Medical device manufacturers must now submit threat modeling and vulnerability management plans before market authorization, expanding the addressable market for embedded security controls.
- Telehealth platform expansion:Cloud-hosted virtual care systems require end-to-end encryption and identity verification layers that on-premise legacy infrastructure cannot provide.
- Ransomware targeting infusion pumps:Attacks on wireless-connected drug delivery systems have elevated endpoint detection from IT preference to C-suite risk priority.
Market Restraints
- Specialized cybersecurity workforce scarcity:Health systems compete with financial services and defense contractors for personnel holding CISSP and GCIH certifications, inflating compensation costs.
- Medical device vendor concentration:Four manufacturers control seventy percent of the infusion pump market, creating single-supplier vulnerability exposure when patching timelines diverge from hospital risk tolerance.
- HIPAA compliance friction:The Security Rule's implementation specifications for access control and audit logging impose documentation burdens that slow deployment of experimental AI-driven threat detection tools.
Strategic Opportunities
- Rural hospital managed security services:Critical Access Hospitals in the United States lack capital for 24/7 Security Operations Centers, creating subscription revenue pools for outsourced monitoring and incident response.
- Software bill of materials mandates:FDA's emerging SBOM requirements for connected devices will force medical technology suppliers to qualify cybersecurity vendors during component sourcing decisions.
- Zero-trust network segmentation:Microsegmentation between clinical workstations and patient monitoring systems is unifying network access control with identity governance in ways that legacy VLAN architectures cannot replicate.
Industry Challenges
- Legacy medical device integration:Imaging systems and patient monitors with decade-old operating systems cannot accommodate modern endpoint agents without FDA recertification.
- Biomedical engineering skill gaps:Hospital technicians trained on device maintenance lack training in network traffic analysis and forensic log review.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Healthcare Cybersecurity Market |
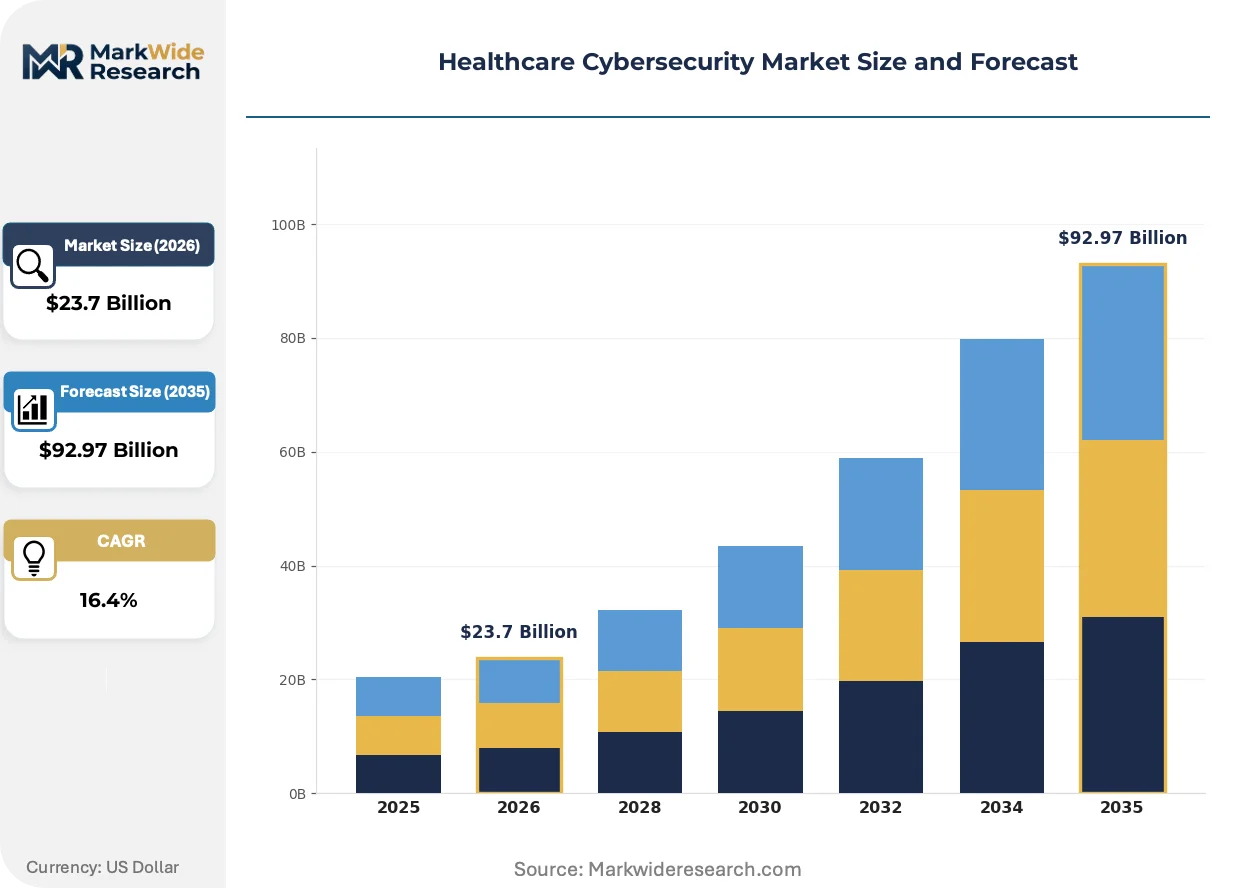
| Market Size in 2026 | $23.7 Billion |
| Market Size in 2035 | $92.97 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Endpoint Security, Network Security, Application Security, Cloud Security Deployment: On-premises, Cloud-based, Hybrid, Managed Services End User: Hospitals, Clinics, Insurance Providers, Pharmacies Service Type: Consulting Services, Managed Security Services, Training, Risk Assessment |
| Companies Covered | IBM, Cisco Systems, Palo Alto Networks, Check Point Software Technologies, Fortinet, Trend Micro, CrowdStrike, McAfee, Claroty, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Healthcare Cybersecurity Market Emerging Trajectories
Security architecture is converging around identity-centric access models that treat every device and user as a potential threat vector regardless of network location.
Extended Detection and Response platforms are unifying telemetry from endpoints, network traffic, and cloud workloads into single-pane analysis. Large health systems in the United States are deploying these consolidated stacks to replace siloed SIEM and EDR contracts. This unification is compressing vendor consolidation timelines and marginalizing point-solution providers that cannot integrate across clinical and administrative environments.
The FDA's updated premarket guidance for connected medical devices mandates documented secure development lifecycles and post-market vulnerability monitoring. Device manufacturers must now designate a cybersecurity point of contact and submit plans for coordinated disclosure. Cardiology and radiology equipment categories face the steepest compliance ramps due to their network centrality and patient safety criticality.
Hospital procurement committees are elevating cybersecurity clauses to tier-one evaluation criteria alongside price and clinical efficacy. Group Purchasing Organizations are responding by pre-qualifying vendors with HITRUST or SOC 2 Type II attestations. This pattern is most pronounced in the Northeastern United States, where state breach notification laws impose strict liability timelines that procurement departments internalize as vendor selection filters.
Healthcare Cybersecurity Market Segmentation
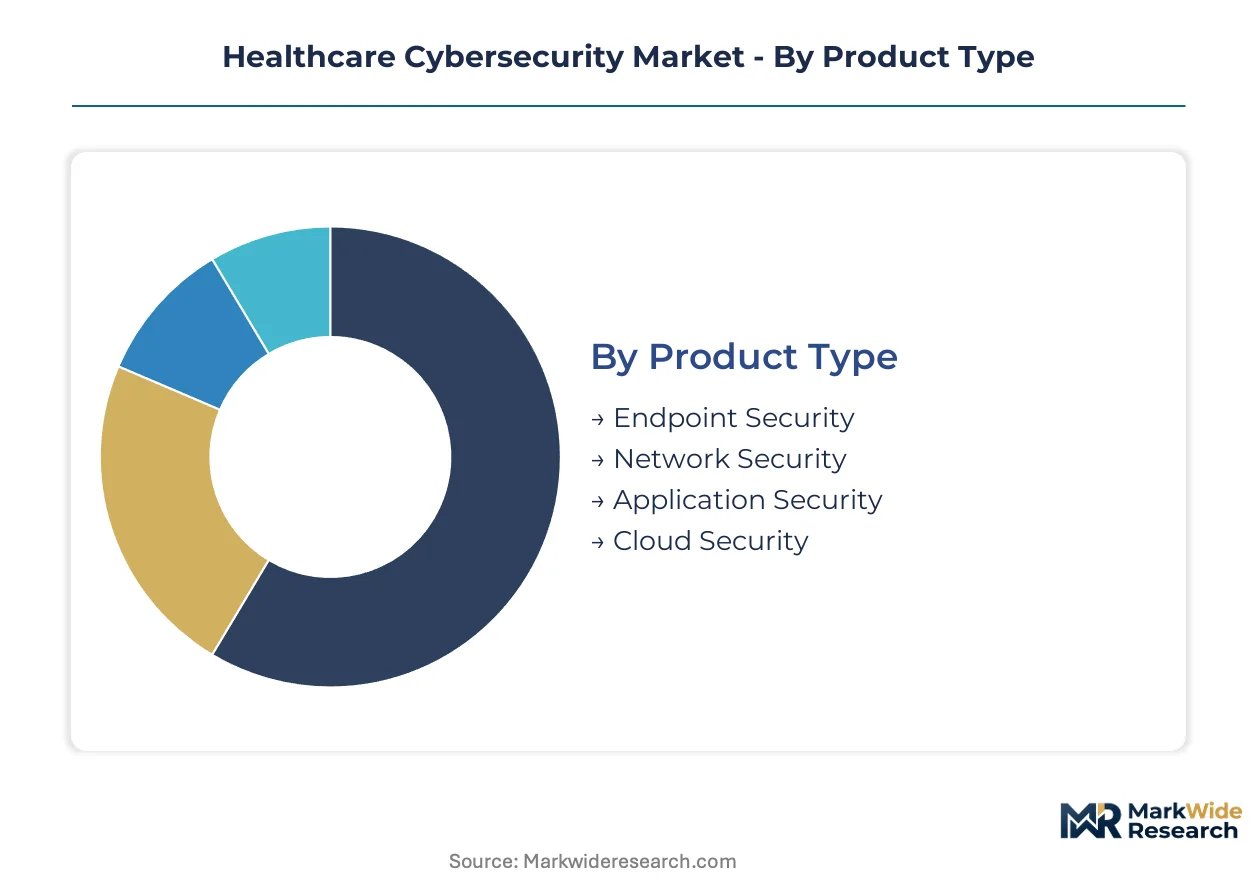
Healthcare cybersecurity procurement splits across technology layers, operational models, and buyer capabilities. Understanding these divisions reveals where capital concentrates and which configurations impose the steepest integration costs on health systems.
Product Type:
Capital intensity varies sharply across product categories, with hardware-dependent network infrastructure demanding the heaviest upfront outlays while cloud-native offerings shift spending toward recurring operational expenditure.
- Endpoint Security:Agent-based protection for workstations, medical devices, and mobile clinical equipment. United States health systems allocate the largest procurement budgets here as ransomware campaigns targeting infusion pumps and imaging workstations intensify. FDA premarket guidance for connected devices is accelerating endpoint detection and response deployments in cardiology and radiology departments.
- Network Security:Firewalls, intrusion detection systems, and zero-trust segmentation appliances. Demand concentrates in consolidated health systems building microsegmented architectures between clinical and administrative zones. Hardware refresh cycles for these systems typically span five to seven years, locking in vendor relationships.
- Application Security:Code scanning, runtime protection, and API security for electronic health record platforms and telehealth applications.
- Cloud Security:CASB, cloud workload protection, and identity governance for off-premises deployments.
Endpoint Security absorbs the bulk of installed capacity; Cloud Security is expanding most quickly as telehealth platforms migrate off-premises.
Deployment:
Deployment architecture determines staffing requirements and capital allocation rhythms, with hybrid models imposing the most complex integration demands across legacy and modern infrastructure.
- On-premises:Hardware and software operating within hospital data centers and network closets. Large academic medical centers in the United States maintain these deployments for latency-sensitive imaging systems and regulatory audit trails. Capital expenditure peaks during EMR platform upgrades and facility expansions.
- Cloud-based:Fully hosted security services with subscription pricing. Rural hospitals and specialty clinics lacking security operations centers are driving adoption here, outsourcing monitoring to managed security providers. HIPAA business associate agreements govern these relationships.
- Hybrid:Split architectures preserving sensitive workloads on-site while pushing analytics and storage to cloud environments.
- Managed Services:Third-party operation of security infrastructure with guaranteed response times.
On-premises retains the largest installed base; Cloud-based deployments are climbing the fastest among mid-sized health systems.
End User:
Buyer sophistication and procurement authority vary dramatically across end-user categories, with hospitals wielding enterprise-grade budgets while smaller providers operate under severe resource constraints.
- Hospitals:Acute care facilities with 24/7 operations and complex device ecosystems. United States health system consolidation is concentrating procurement authority in centralized IT departments serving dozens of facilities. These buyers negotiate multi-year enterprise licenses spanning endpoint, network, and cloud protection.
- Clinics:Outpatient and specialty practices with limited technical staff. Critical Access Hospitals and rural clinics rely heavily on managed security services due to cybersecurity workforce scarcity. Subscription models dominate here.
- Insurance Providers:Payers protecting member databases and claims processing systems.
- Pharmacies:Retail and specialty pharmacy chains securing prescription systems and patient data.
Hospitals command the dominant share of security spending; Clinics represent the steepest expansion trajectory as outsourced monitoring penetrates underserved markets.
Service Type:
Service engagement models reflect maturity gradients across health systems, with organizations in early compliance phases prioritizing assessment while advanced operators invest in continuous monitoring capabilities.
- Consulting Services:Risk assessments, security architecture design, and HIPAA compliance gap analyses. Demand spikes following OCR enforcement actions and state breach notification deadlines. Northeastern United States health systems engage these services proactively given strict liability timelines.
- Managed Security Services:24/7 security operations center functions delivered under subscription. Rural hospitals lacking CISSP-certified staff are the fastest-growing customer segment here. Vendor selection hinges on HITRUST certification and guaranteed mean-time-to-response metrics.
- Training:Workforce education on phishing recognition and incident response protocols.
- Risk Assessment:Periodic evaluation of vulnerabilities and control effectiveness.
Managed Security Services capture the largest revenue pool; Consulting Services are gaining share fastest among health systems responding to FDA device security mandates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States health systems command the dominant share of healthcare cybersecurity procurement, with enterprise consolidation creating attack surfaces that demand hospital-grade protection. Federal enforcement actions and device-specific mandates concentrate spending in acute care networks. Geographic variation reflects state-level breach notification stringency and medical device manufacturing clusters.
United States
Hospital system consolidation in Texas, California, and the Northeast Corridor drives enterprise security architecture deployments across multi-facility networks. FDA premarket cybersecurity guidance for connected medical devices elevates procurement scrutiny in cardiology and radiology equipment categories. The Boston-Cambridge corridor anchors medical device cybersecurity innovation, with academic medical centers piloting zero-trust segmentation between clinical and administrative zones.
Germany
Industrial medical technology manufacturers in Baden-Württemberg and Bavaria face EU MDR cybersecurity annex requirements for network-connected diagnostic equipment. The country's national pharmaceutical regulator enforces post-market surveillance obligations that expand vulnerability management service demand. Berlin-Brandenburg health systems concentrate procurement authority through regional hospital associations, standardizing endpoint detection deployments across formerly independent facilities.
United Kingdom
NHS Digital transformation programs accelerate cloud security spending as telehealth platforms migrate to centralized infrastructure. GDPR and NHS-specific data protection standards impose encryption and access control specifications on electronic health record vendors. The London-Southeast corridor concentrates health technology procurement decisions, with integrated care systems negotiating multi-year managed security service contracts for constituent hospitals and clinics.
Japan
Aging demographics and hospital digitization initiatives expand cybersecurity budgets in Tokyo and Osaka metropolitan health systems. PMDA guidance on software as a medical device creates compliance pathways for AI-enabled diagnostic tools with embedded security controls. The Kansai region's medical device manufacturing cluster drives upstream demand for secure development lifecycle consulting and component-level vulnerability assessment services.
India
Health technology adoption in Maharashtra and Karnataka exposes private hospital chains to ransomware campaigns targeting legacy electronic medical record systems. CDSCO draft guidance on cybersecurity for connected medical devices signals forthcoming regulatory alignment with FDA and EU precedents. The Delhi-NCR corridor concentrates health insurance technology providers securing claims processing infrastructure against data exfiltration threats.
Healthcare Cybersecurity Market Vendor Landscape
Strategic partnerships dominate the current landscape as network infrastructure specialists ally with endpoint detection platforms to deliver unified clinical security stacks. The vendor base stratifies across three tiers: diversified technology conglomerates with deep hospital relationships, cloud-native security platforms targeting telehealth workloads, and specialized medical device protection firms. Archetypes include network-layer incumbents leveraging existing switch and router deployments, endpoint specialists adapting industrial control system expertise to clinical environments, and managed service providers addressing rural hospital skill gaps. M&A activity and technology licensing agreements represent the primary competitive vectors as vendors seek cross-layer integration capabilities.
Within the network infrastructure tier, Cisco Systems and Palo Alto Networks exemplify divergent architectural philosophies—one anchored in hardware-integrated segmentation, the other in cloud-native policy orchestration. CrowdStrike occupies a position among endpoint-centric platforms that have extended detection capabilities toward medical device environments. These three companies represent the dominant competitive archetypes: infrastructure incumbents defending installed base through deep integration, cloud-native challengers consolidating fragmented point solutions, and endpoint specialists expanding into operational technology protection.
| Leading Market Players |
|---|
| IBM |
| Cisco Systems |
| Palo Alto Networks |
| Check Point Software Technologies |
| Fortinet |
| Trend Micro |
| CrowdStrike |
| McAfee |
| Claroty |
| Others |
Supply Flow & Price Mechanics
Silicon wafer pricing indices cascade through semiconductor component costs into tiered security hardware procurement, compressing margins for on-premises firewall and intrusion detection system vendors while cloud-native subscription models absorb volatility through annual contract structures.
Pricing Analysis
Volume concentration in enterprise health system procurement splits margin capture between high-touch consulting engagements and automated SaaS tiers. Three-tier pricing structure across premium, standard, and economy levels differentiates by HITRUST certification grade and guaranteed mean-time-to-response commitments. Pricing pressure stems from health system consolidation forcing volume discounts across multi-facility networks. Critical Access Hospitals exhibit acute price sensitivity due to federal reimbursement constraints, while consolidated academic medical centers prioritize compliance-grade premiums over unit cost.
Supply Chain Analysis
Regional distribution centers in the United States, Germany, and Japan anchor hardware fulfillment networks for zero-trust appliances and medical device security modules. Component sourcing draws from Taiwan for specialized network processors, South Korea for memory modules, and domestic US facilities for final assembly of FDA-regulated devices. Single-source vulnerability exposure concentrates in legacy medical device firmware supply chains where four manufacturers dominate infusion pump production. Distribution runs through value-added resellers with biomedical engineering certifications serving hospital procurement committees.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Healthcare cybersecurity sits in a technology-transition phase as zero-trust architectures displace perimeter-based VPN and VLAN segmentation that dominated hospital infrastructure for two decades.
For Market Incumbents: Cement installed-base defense by embedding endpoint detection agents directly into Cisco switch firmware and negotiating multi-year enterprise licenses that span network, cloud, and device layers. Threat modeling service revenue from FDA premarket guidance compliance creates a recurring revenue buffer against pure-play cloud-native competitors. For New Entrants and Emerging Players: Cloud-native managed detection and response platforms offer the most penetrable route into rural Critical Access Hospitals lacking Security Operations Center staffing. Target subscription-based outsourcing contracts in the Midwestern and Southeastern United States where health system consolidation has not yet centralized procurement authority. For Investors and Strategic Acquirers: Distressed-cycle entries favor medical device cybersecurity specialists with FDA-recognized secure development lifecycle consulting capabilities in the Boston-Cambridge corridor. Long-term viability hinges on SBOM tooling revenue streams as device manufacturers face component-level vulnerability disclosure mandates. Watch FDA enforcement action frequency as the inflection signal for valuation compression in non-compliant vendor portfolios.| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Architecture Deployment | Hospital system consolidation in Texas and California demands microsegmentation between clinical and administrative network zones. |
| FDA Premarket Cybersecurity Consulting | Device manufacturers in the Boston-Cambridge corridor require threat modeling documentation for cardiology and radiology equipment authorization. |
| Managed Security Service Expansion | Rural Critical Access Hospitals in the Midwest outsource 24/7 monitoring due to CISSP-certified workforce scarcity. |
| Software Bill of Materials Tooling | Connected device suppliers must qualify component vendors under emerging FDA supply chain transparency requirements. |
| Cloud Security Platform Integration | Telehealth migration to off-premises infrastructure necessitates CASB and cloud workload protection for HIPAA-compliant hosting. |
Methodological Framework
Document review covered FDA premarket guidance filings, HITRUST certification databases, and hospital procurement contract records, complemented by interviews with hospital CISOs, biomedical engineering directors, medical device cybersecurity consultants, and Group Purchasing Organization contract managers. Secondary validation drew from CMS Medicare cost reports, GPO pricing benchmarks, and OCR breach notification archives. Bottom-up spending estimates across endpoint, network, and cloud security categories triangulated against top-down health system IT budget allocations.
Segmentation outputs reflect deployment model, organization size, and regional regulatory cluster variations across the projection horizon. Modeled dimensions span product type, service engagement maturity, and buyer sophistication tier. CAGRs derive from health system consolidation velocity, FDA enforcement trajectory, and telehealth platform adoption curves. Forecast inputs incorporate medical device connectivity growth rates and zero-trust architecture penetration patterns in acute care networks.
The model holds under continued HIPAA enforcement and FDA premarket guidance implementation; deviation in federal reimbursement policy or medical device vendor consolidation would shift spending allocation across service types. Decision-makers should treat outputs as directional within the stated assumption set.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Health Informatics
Global Healthcare Business Intelligence (BI) Market
Health Informatics
Global Cardiology Information System Market
Health Informatics
Healthcare Interoperability Market
Health Informatics
Vocal Biomarkers Market
Health Informatics
Allergy Care Market
Health Informatics
Global E-Health Market
Health Informatics
Global Consumer Genomics Market
Health Informatics
Ehealth Software and Services Market
Health Informatics
Healthcare Application Programming Interfaces Market
Health Informatics
High Acuity Information Systems Market
Health Informatics
United States Healthcare Fraud Detection Market
Health Informatics
Ambulatory Electronic Health Record Market
Health Informatics
Artificial Intelligence (AI) Healthcare Market
Health Informatics
Global Non Clinical Information System Market
Health Informatics
US Laboratory Informatics Market
Health Informatics
North America Laboratory Information System Market