
 Global Medical Device Security Market | 2026-2036
Global Medical Device Security Market Size, Share, and Industry Trends Forecast 2026-2036
Global Medical Device Security Market Foresight
The gap between premium integrated security platforms and commodity antivirus tools is realigning procurement patterns across health systems. Cisco Systems leverages its networking infrastructure to dominate hospital network segmentation. Palo Alto Networks sustains technology leadership in zero-trust architectures for clinical environments. ClearDATA anchors cloud-native security compliance for connected medical devices.
Medical device security encompasses hardware and software safeguards engineered to protect connected healthcare equipment from unauthorized access, data exfiltration, and operational disruption, with encryption protocols typically requiring AES-256 standards and real-time threat detection latency under 100 milliseconds. The primary purpose is ensuring patient safety continuity while preserving data integrity across regulated clinical workflows. Endpoint protection commands the largest revenue pool as hospitals prioritize agent-based monitoring for legacy devices with unpatchable operating systems. Identity and access management represents the fastest-expanding segment as multi-factor authentication becomes mandatory for clinical staff device interaction. Cloud-based deployment models are displacing on-premises installations in ambulatory surgical centers seeking reduced capital expenditure.
The FDA's premarket and post-market cybersecurity guidance shapes device manufacturer design obligations, while the EU Cyber Resilience Act imposes mandatory security updates across the product lifecycle. Japan's Ministry of Health, Labour and Welfare coordinates with METI to align medical device software standards with international cybersecurity frameworks. Stakeholders must monitor evolving national implementation timelines for harmonized standards to anticipate compliance-driven procurement waves.
Market Dynamics
Hospital procurement committees now mandate embedded security modules before network admission, forcing device manufacturers to redesign hardware architectures mid-lifecycle rather than patching software vulnerabilities post-deployment.
Growth Catalysts
- FDA Post-Market Cybersecurity Guidance:The guidance mandates ongoing vulnerability monitoring for networked devices, compelling manufacturers to build continuous security update capabilities into product roadmaps.
- Japan METI Healthcare Cybersecurity Framework:Coordination between METI and the Ministry of Health, Labour and Welfare accelerates domestic hospital procurement of threat detection systems for imaging equipment.
- Cloud-native security platforms:Ambulatory surgical centers in Germany adopt subscription-based endpoint protection to eliminate capital expenditure on on-premises security infrastructure.
Market Restraints
- Legacy device incompatibility:Infusion pumps and patient monitors running Windows XP cannot accommodate modern encryption protocols without complete hardware replacement.
- Concentrated semiconductor supply:Secure element chip fabrication depends on facilities in Taiwan and South Korea, creating vulnerability to regional supply disruptions.
- EU Cyber Resilience Act compliance costs:Mandatory security lifecycle documentation imposes documentation burdens that disproportionately strain mid-tier device manufacturers.
Strategic Opportunities
- India's hospital digitization:The country's Ayushman Bharat health infrastructure expansion creates first-mover advantage for vendors offering affordable endpoint protection bundles.
- Artificial intelligence and behavioral analytics convergence:Machine learning models trained on device telemetry patterns enable predictive threat detection before network infiltration occurs.
- Outcome-based security contracting:Risk-sharing agreements where vendors guarantee zero successful breaches are replacing traditional software licensing in US health systems.
Industry Challenges
- Embedded systems security expertise:The shortage of engineers trained in both medical device hardware and cryptography limits vendor R&D velocity.
- FDA 510(k) cybersecurity documentation:Pre-market submission requirements for software bill of materials extend approval timelines by four to seven months.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Medical Device Security Market |
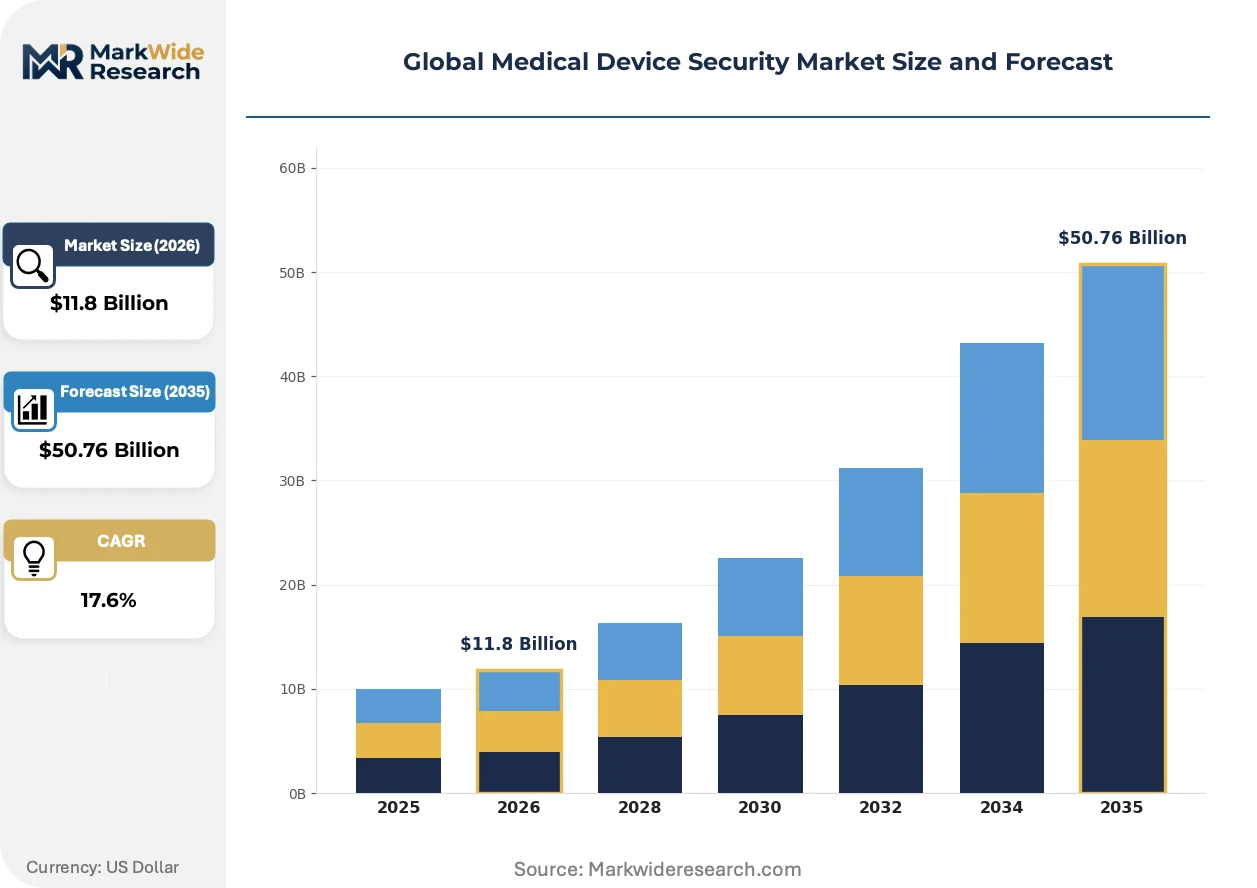
| Market Size in 2026 | $11.8 Billion |
| Market Size in 2035 | $50.76 Billion |
| CAGR (2026 – 2036) | 17.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Intrusion Detection, Encryption Software, Firewall Solutions, Endpoint Protection, Identity & Access Management Application: Patient Monitoring Systems, Diagnostic Imaging, Therapeutic Devices, Surgical Instruments, Hospital Information Systems End User: Hospitals, Ambulatory Surgical Centers, Diagnostic Laboratories, Clinical Research Organizations, Telehealth Providers Deployment: On-Premises, Cloud-Based, Hybrid, Managed Security Services |
| Companies Covered | Cisco Systems, Inc., Check Point Software Technologies, Palo Alto Networks, IBM Corporation, Fortinet, Inc., ClearDATA, Forescout Technologies, CrowdStrike Holdings, Armis Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Medical Device Security Market Shifts & Advancements
Zero-trust network architecture is migrating from enterprise IT into clinical environments, fundamentally altering how hospitals authenticate every device interaction rather than relying on perimeter defenses.
Hardware security modules with tamper-resistant key storage are consolidating trust anchor functions for implantable cardiac devices and insulin pumps. Cardiovascular device manufacturers in the United States embed these modules during production rather than retrofitting fielded units. This consolidation eliminates the patch management burden for devices with decade-long deployment horizons.
The EU Cyber Resilience Act mandates automatic security updates for the full product lifecycle of connected medical devices sold in Europe. Manufacturers must now provision twenty-year software maintenance infrastructure or withdraw from the European market. German notified bodies report certification backlogs exceeding fourteen months as device makers scramble to comply with the 2027 enforcement deadline.
Hospital purchasing departments now require proof of cyber insurance coverage before adding vendors to approved supplier lists. Group purchasing organizations in the United States embed security audit clauses into standard medical device contracts. This behavioral shift pressures smaller manufacturers to either absorb premium insurance costs or exit the hospital supply chain entirely.
Global Medical Device Security Market Segmentation
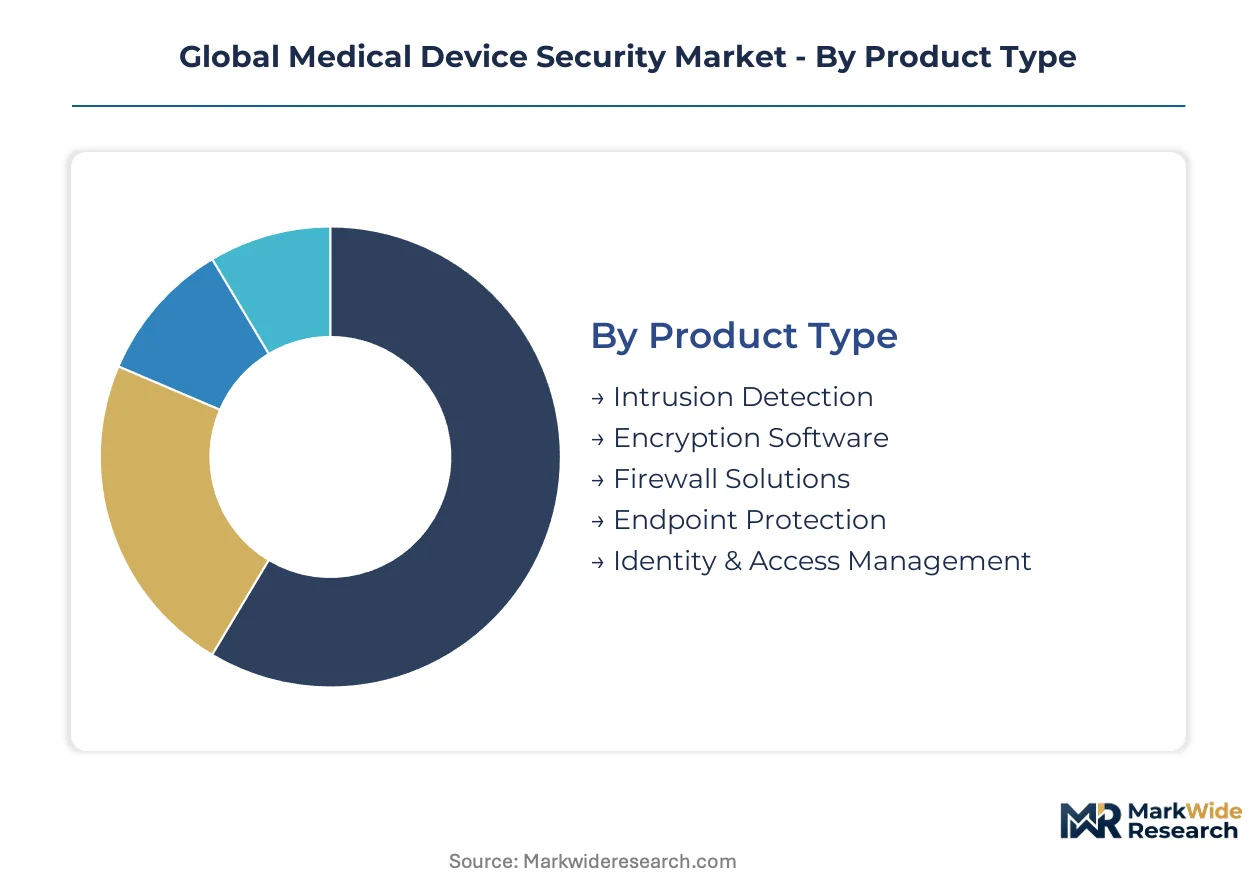
Medical device security procurement splits across four structural dimensions, each carrying distinct compliance obligations and budget allocation patterns. Understanding these fault lines clarifies why hospitals negotiate separate contracts for imaging equipment versus infusion pump networks.
Product Type:
FDA 510(k) submissions impose documentation requirements that vary sharply by product category, with endpoint protection demanding software bill of materials while encryption tools face FIPS 140-2 validation.
- Endpoint Protection:Agent-based monitoring platforms deploy lightweight software modules on legacy devices with unpatchable Windows XP or embedded Linux kernels. Hospital networks in the United States prioritize this segment for MRI and CT systems where hardware replacement cycles extend beyond fifteen years. FDA premarket guidance now mandates continuous update capabilities as a design input.
- Identity & Access Management:Multi-factor authentication systems govern clinical staff interactions with networked devices through biometric readers and smart card readers. German university hospitals drive demand here as the EU Cyber Resilience Act mandates role-based access controls for all connected equipment. The segment climbs fastest as zero-trust architectures displace perimeter-based security models.
- Intrusion Detection:Network traffic analyzers identify anomalous communication patterns from medical devices.
- Encryption Software:AES-256 implementations protect data at rest and in transit across hospital networks.
- Firewall Solutions:Segmentation appliances isolate device VLANs from administrative IT infrastructure.
Leading the category by volume: Endpoint Protection. Growing fastest: Identity & Access Management.
Application:
Capital equipment budgets determine security spending tiers, with diagnostic imaging commanding premium integrated platforms while surgical instruments rely on commodity network segmentation.
- Diagnostic Imaging:MRI and CT systems require hardware security modules with tamper-resistant key storage for DICOM image encryption. Japanese hospitals under METI coordination deploy these for imaging equipment connected to national health information exchanges. The segment concentrates procurement spend due to device longevity and patient data sensitivity.
- Patient Monitoring Systems:Continuous telemetry from bedside monitors demands real-time threat detection with sub-100 millisecond latency. US health systems prioritize this application after FDA warnings about infusion pump network vulnerabilities. Expansion here accelerates as wireless monitoring displaces hardwired installations.
- Therapeutic Devices:Insulin pumps and cardiac defibrillators need embedded cryptographic authentication.
- Surgical Instruments:Robotic surgery platforms integrate security at the control system level.
- Hospital Information Systems:EHR integration layers require API security and data loss prevention.
Dominant by procurement value: Diagnostic Imaging. Steepest expansion trajectory: Patient Monitoring Systems.
End User:
Operational scale shapes security architecture choices, with acute care hospitals building SOC capabilities while ambulatory centers outsource to managed service providers.
- Hospitals:Large health systems maintain 24/7 security operations centers with dedicated medical device threat intelligence feeds. German hospital networks under EU Cyber Resilience Act timelines accelerate procurement of integrated detection and response platforms. This end user anchors category revenue through multi-year enterprise agreements.
- Ambulatory Surgical Centers:Limited IT staffing drives subscription-based cloud security adoption for endpoint protection. Centers in India under Ayushman Bharat infrastructure expansion seek affordable bundled solutions. The segment gains share fastest as outpatient procedure volumes rise.
- Diagnostic Laboratories:High-throughput analyzers require isolated network segments for regulatory compliance.
- Clinical Research Organizations:Multi-site trials demand audit trails for 21 CFR Part 11 compliance.
- Telehealth Providers:Remote patient monitoring platforms need lightweight encryption for home-based devices.
Volume leader: Hospitals. Fastest-climbing segment: Ambulatory Surgical Centers.
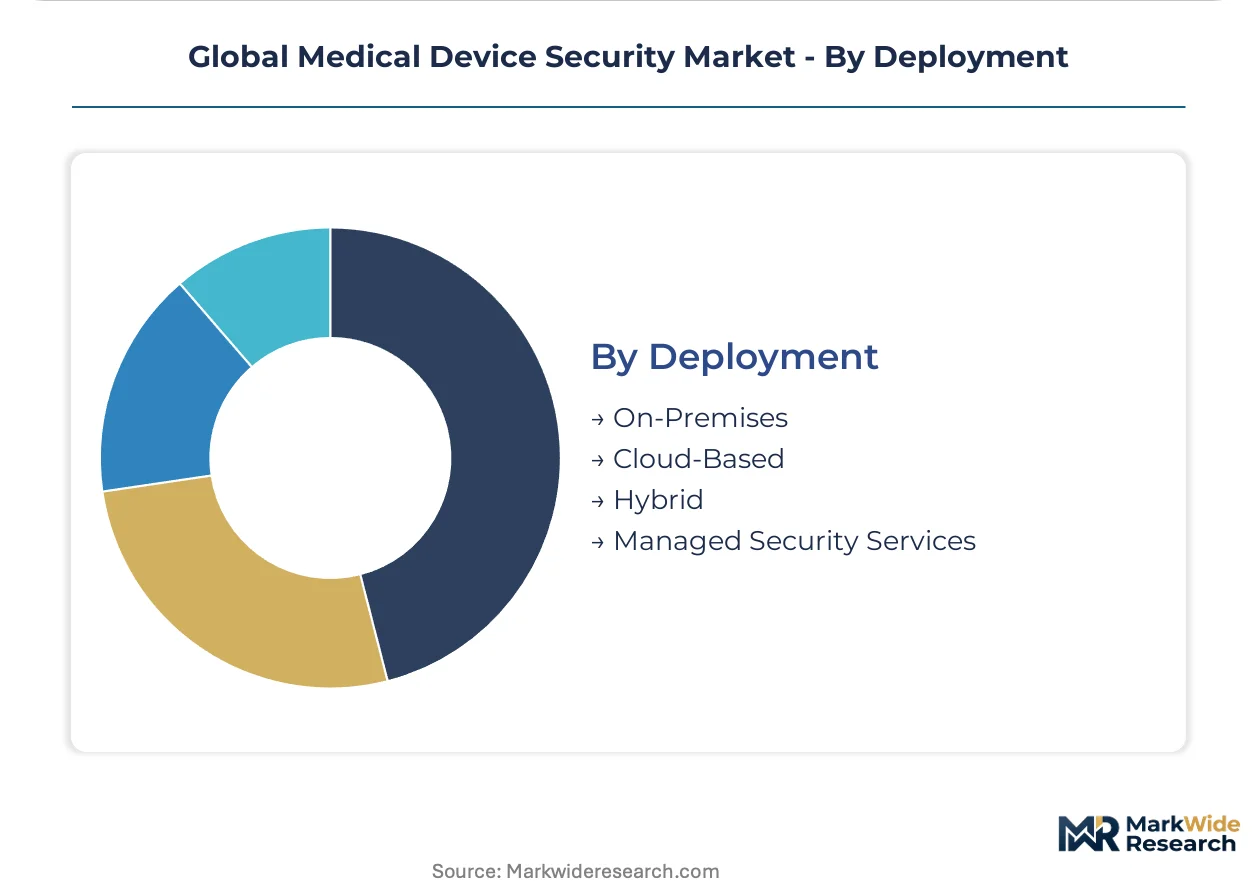
Deployment:
Capital expenditure constraints versus operational control preferences split procurement between ownership models and outsourced security operations.
- Cloud-Based:Subscription delivery eliminates hardware procurement cycles for security infrastructure. Ambulatory surgical centers in Germany adopt this model to convert capital expenditure to operational spending. The deployment mode displaces on-premises installations fastest among mid-sized health systems.
- Managed Security Services:Outsourced SOC operations provide 24/7 monitoring without internal staffing requirements. US rural hospitals under financial pressure contract these services for medical device threat detection. This segment expands as cybersecurity skill shortages persist.
- On-Premises:Air-gapped installations serve facilities with strict data sovereignty requirements.
- Hybrid:Split architectures keep sensitive imaging data local while outsourcing endpoint management.
Deployment volume leader: Cloud-Based. Gaining share fastest: Managed Security Services.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Boston's Longwood Medical Area anchors North American medical device security procurement, with Massachusetts General Hospital and Brigham and Women's Hospital driving early adoption of zero-trust network segmentation for imaging equipment.
United States
FDA post-market cybersecurity guidance compels device manufacturers to embed continuous monitoring capabilities. Hospital networks in the Texas Medical Center and Mayo Clinic Rochester accelerate procurement of endpoint protection platforms. The 2024 HPH Cybersecurity Performance Goals reshape procurement specifications for infusion pump networks.
Germany
EU Cyber Resilience Act enforcement deadlines concentrate compliance spending in Baden-Württemberg's medical technology corridor. Tübingen and Freiburg university hospitals deploy hardware security modules for MRI systems under BSI technical guidelines. Notified body certification backlogs exceed fourteen months as manufacturers race toward 2027 deadlines.
Japan
METI coordination with PMDA accelerates threat detection procurement for imaging equipment connected to national health information exchanges. Tokyo's Keiyō Industrial Zone hosts concentrated deployment of embedded security modules for cardiac devices. The Ministry of Health, Labour and Welfare mandates AES-256 encryption for all networked therapeutic equipment by 2026.
India
Ayushman Bharat health infrastructure expansion creates procurement windows for affordable endpoint protection bundles. Hyderabad's Genome Valley and Bengaluru's HealthTech corridor attract security vendors targeting ambulatory surgical centers. CDSCO draft cybersecurity guidelines for medical devices enter final consultation phase.
United Kingdom
NHS Digital's Device Security Requirements reshape procurement for imaging networks across London's Imperial College Healthcare and Manchester's NHS Foundation Trust. MHRA alignment with EU MDR cybersecurity annexes extends documentation obligations for legacy device manufacturers. Cambridge's biomedical cluster pilots behavioral analytics for predictive threat detection.
Global Medical Device Security Market Competitive Landscape
Premium-margin players sit above commodity-margin players across three structural dimensions: network infrastructure integration depth, cloud-native compliance automation, and zero-trust architecture maturity. The vendor base splits between networking incumbents with hospital segmentation expertise, cybersecurity pure-plays with medical device specialization, and cloud-native compliance platforms. Two strategic archetypes dominate: infrastructure-integrated security stacks and standalone endpoint protection specialists. Competitive moves concentrate on strategic partnerships with group purchasing organizations and technology licensing for embedded hardware security modules.
Within the infrastructure-integrated tier, Cisco Systems, Inc. and Palo Alto Networks exemplify networking-centric positioning that leverages existing hospital IT relationships. ClearDATA occupies a distinct position among cloud-native compliance specialists serving ambulatory surgical centers. These three anchors illustrate how vendor selection increasingly follows deployment architecture preferences rather than standalone security feature comparisons.
| Leading Market Players |
|---|
| Cisco Systems, Inc. |
| Check Point Software Technologies |
| Palo Alto Networks |
| IBM Corporation |
| Fortinet, Inc. |
| ClearDATA |
| Forescout Technologies |
| CrowdStrike Holdings |
| Armis Inc. |
| Others |
Supply & Pricing Matrix
Embedded systems security engineers concentrated in Boston's Route 128 corridor and Tel Aviv's cybersecurity cluster command compensation premiums that widen spreads between integrated platform pricing and commodity endpoint protection. Labor-cost differentials between these talent pools and Eastern European engineering centers force vendors to tier service bundles by technical sophistication.
Pricing Analysis
Value-based pricing anchored to breach-prevention outcomes now dominates US health system contracts, with vendors guaranteeing zero successful intrusions for premium-tier subscriptions. Three-tier pricing structure across premium, standard, and economy levels separates fully managed SOC services from software-only licenses and basic antivirus modules. Cost compression in the economy tier intensifies because Indian and Southeast Asian vendors compete on implementation labor rates. Ambulatory surgical centers exhibit highest price sensitivity, while academic medical centers prioritize outcome guarantees over license costs.
Supply Chain Analysis
Regional distribution centers in Singapore, Rotterdam, and Dubai handle hardware security module fulfillment for Asia-Pacific, European, and Middle Eastern hospital networks respectively. Taiwan and South Korea supply secure element chip fabrication, while Germany and Japan provide precision sensor components for tamper-resistant enclosures. Single-source vulnerability in Taiwan semiconductor foundries threatens delivery timelines for cardiac device manufacturers. Distribution runs through authorized medical device distributors with cold-chain capabilities for temperature-sensitive components.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Medical device security is becoming a vertical-integration race as platform vendors pursue captive control over hardware security module design to escape semiconductor supply bottlenecks.
For Market Incumbents: Acquire embedded cryptography engineering teams to bring hardware security module development in-house rather than licensing from semiconductor specialists. Cisco Systems and Palo Alto Networks should consolidate threat intelligence feeds from hospital SOC deployments to build proprietary medical device behavioral baselines. FDA premarket documentation requirements for software bill of materials extend approval timelines, favoring incumbents with established regulatory affairs infrastructure over emerging competitors. For New Entrants and Emerging Players: Launch via subscription-based endpoint protection bundles targeting India's Ayushman Bharat ambulatory surgical center expansion, where capital expenditure constraints favor operational spending models. White-space opportunity concentrates in behavioral analytics for wireless patient monitoring systems, a segment where legacy vendors lack telemetry-pattern training data. Partner with German notified bodies early to secure EU Cyber Resilience Act certification ahead of enforcement deadlines. For Investors and Strategic Acquirers: Re-rating potential sits with cloud-native compliance platforms given mandatory automatic update requirements across the European product lifecycle. Long-term viability favors vendors provisioning twenty-year software maintenance infrastructure rather than point-solution providers. Acquisition target archetype: managed security service providers with hospital SOC contracts and embedded device telemetry expertise. Watch FDA 510(k) cybersecurity documentation backlogs as an inflection signal for vendor consolidation pressure.| Strategic Initiative | Industry Significance |
|---|---|
| FDA Cybersecurity Submission | Premarket software bill of materials documentation accelerates hospital procurement approval timelines. |
| CE Marking Pathway | EU Cyber Resilience Act compliance opens access to German university hospital networks under BSI guidelines. |
| Hospital System Partnership | Group purchasing organization contracts embed security audit clauses that lock out uninsured competitors. |
| Hardware Security Module Integration | Tamper-resistant key storage eliminates patch management burden for decade-long cardiac device deployments. |
| Reimbursement Strategy | Cyber insurance coverage requirements in US health systems create procurement gatekeeper advantages. |
Research Methodology
Trade association data, regulatory filings, and customs records anchored secondary inputs for this analysis, supplemented by primary interviews with hospital CISOs, biomedical engineers, GPO contracts managers, and medical device regulatory affairs leads. FDA 510(k) submission databases, EU MDR technical documentation, Japanese PMDA approval records, and hospital procurement contract repositories provided demand-side validation. Bottom-up vendor revenue estimates triangulated against top-down health system security spending surveys.
Segment-level modeling tracked endpoint protection, identity and access management, intrusion detection, encryption software, and firewall solutions across deployment modes and end-user categories throughout the forecast period. CAGRs derived from regression analysis of historical procurement velocity against regulatory enforcement timelines and hospital digitization spending patterns. Input assumptions incorporated semiconductor supply constraints, cybersecurity workforce availability by region, and evolving FDA premarket guidance documentation burdens.
Regulatory timeline delays, semiconductor supply disruptions, and hospital capital expenditure freezes are the dominant revision risks to projection outputs. Decision-makers should treat outputs as directional within the stated assumption set.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Medical Devices
North America Electroencephalography Devices Market
Medical Devices
Radiofrequency (RF) Ablation System Market
Medical Devices
Veterinary Ultrasound Scanners Market
Medical Devices
Global Vaccine Delivery Devices Market
Medical Devices
Intrathecal Pumps Market
Medical Devices
Vortex Mixer Market
Medical Devices
Asia Pacific Portable X-Ray Devices Market
Medical Devices
Veterinary Catheters Market
Medical Devices
US Clear Aligners Market
Medical Devices
Pelvic Muscle Probes Market
Medical Devices
South Africa Neurology Devices Market
Medical Devices
Global Heart Valve Devices Market
Medical Devices
Global Robotic Assisted Surgery Systems Market
Medical Devices
Rib Fracture Repair Systems Market
Medical Devices
Europe Breast Implant Market
Medical Devices
Nonablative Laser Resurfacing Devices Market