
 Global Integration Security Services Market | 2026-2036
Global Integration Security Services Market Size, Share, and Industry Trends Forecast 2026-2036
Global Integration Security Services Market Analysis
Project finance for multi-year managed security contracts is fragmenting competitive dynamics by lowering upfront capital barriers for mid-sized providers. Cisco Systems, Inc. leverages its networking hardware installed base to bundle security integration at the infrastructure layer. IBM Corporation anchors enterprise credibility through its consulting-led security transformation practice. Honeywell International Inc. competes by extending building-automation expertise into converged physical-cyber security deployments.
Integration security services encompass the design, deployment, and orchestration of unified protection architectures spanning network perimeters, cloud workloads, endpoints, and physical access systems, typically incorporating SIEM orchestration, zero-trust segmentation policies, and automated threat-response playbooks to eliminate security silos across heterogeneous IT/OT environments. Cloud security within the service-type dimension is attracting disproportionate investment as enterprises migrate critical workloads, while hybrid deployment models command premium pricing due to complexity in orchestrating on-premise and cloud-native controls simultaneously. Large enterprises dominate the customer-type split, though SME demand is accelerating through packaged managed-security offerings that abstract integration complexity.
FDA cybersecurity guidance for connected medical devices, the EU AI Act's risk-classification requirements for automated security systems, and India's CERT-In mandatory incident-reporting rules are collectively elevating compliance-driven procurement standards across healthcare, critical infrastructure, and government verticals. These frameworks compel vendors to embed audit trails, encryption standards, and cross-border data governance into integration architectures from design phase forward. Stakeholders must evaluate whether their service portfolios align with emerging sector-specific certification mandates before competitive positioning hardens around compliance-proven delivery models.
Market Dynamics
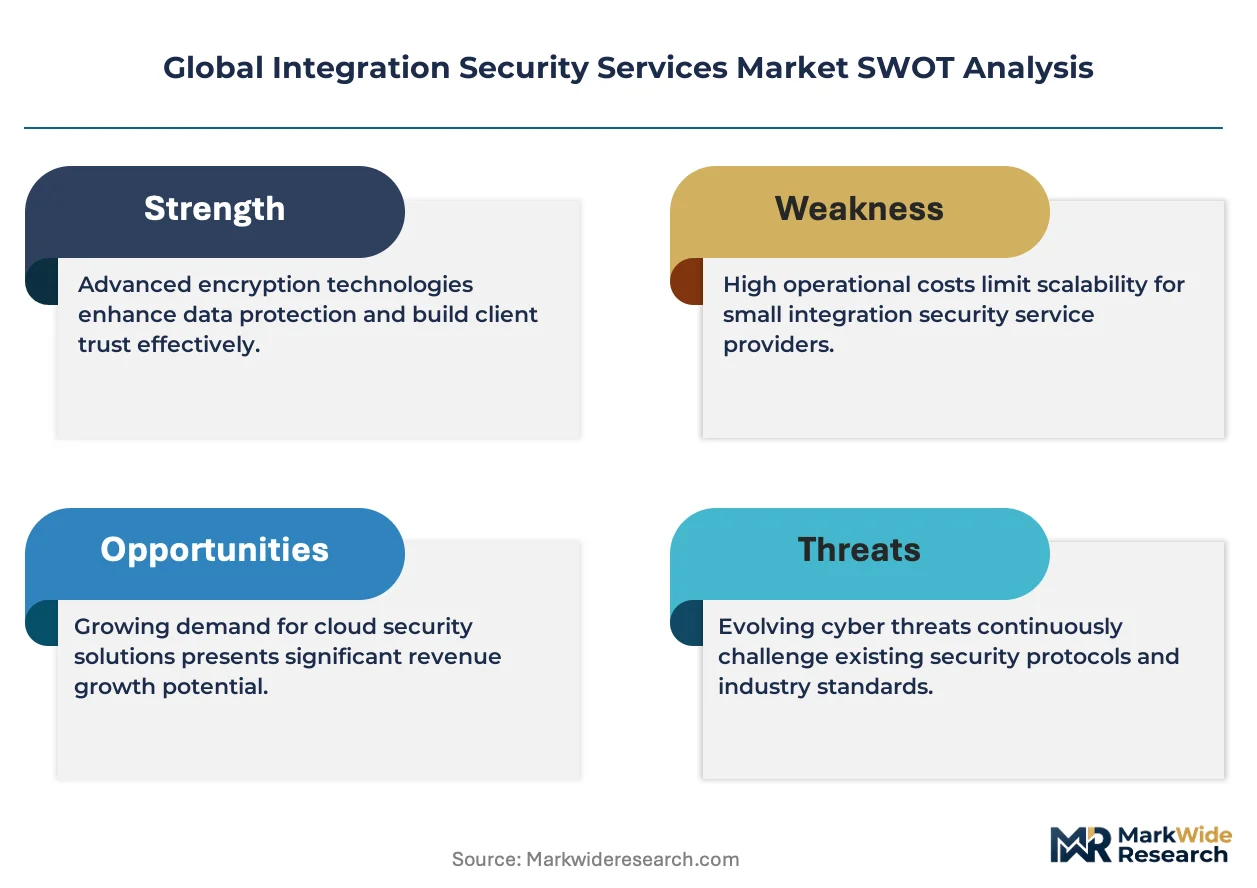
Zero-trust architecture mandates are fragmenting legacy perimeter-defense procurement, compelling enterprises to rebuild security stacks around identity-centric segmentation rather than network-boundary controls. This structural pivot favors vendors with native cloud workload protection and OT/IT convergence capabilities.
Growth Catalysts
- EU NIS2 Directive:Mandatory critical-infrastructure security audits across energy, transport, and digital services are accelerating multi-year integration contracts. Compliance deadlines force state-owned utilities and private operators to consolidate fragmented security vendors.
- Medical device connectivity:FDA cybersecurity guidance for connected diagnostics and infusion pumps is driving hospital procurement of unified endpoint detection and response platforms that span clinical networks and building management systems.
- India CERT-In rules:Mandatory six-hour incident reporting and designated security auditor requirements are expanding the addressable market for managed detection and response services among domestic fintech and SaaS providers.
Market Restraints
- Specialized talent scarcity:Shortages of SIEM engineers with cross-domain cloud and OT expertise are inflating implementation costs and extending deployment timelines for complex hybrid architectures.
- Vendor concentration risk:Dominance of three hyperscale cloud providers in native security tooling creates lock-in exposure for enterprises seeking multi-cloud orchestration capabilities.
- Encryption export controls:US EAR regulations and EU dual-use restrictions are fragmenting product availability for cross-border managed security operations centers serving multinational clients.
Strategic Opportunities
- German industrial Mittelstand:Mid-sized manufacturers with legacy OT environments represent underpenetrated demand for converged physical-cyber security integration around smart factory deployments.
- AI-powered threat hunting:Convergence of large language models with security orchestration is opening white space for automated playbook generation and adversary emulation services.
- US state-level privacy laws:Virginia, Colorado, and Connecticut consumer data protection acts are creating compliance-driven procurement tailwinds for data-loss prevention and encryption-key management integration.
Industry Challenges
- Multi-cloud policy orchestration:Enterprises struggle to maintain consistent zero-trust enforcement across AWS, Azure, and Google Cloud native controls without vendor-agnostic abstraction layers.
- OT security certification timelines:IEC 62443 industrial cybersecurity conformity assessments require twelve-to-eighteen-month validation cycles that delay revenue recognition for integration providers.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Integration Security Services Market |
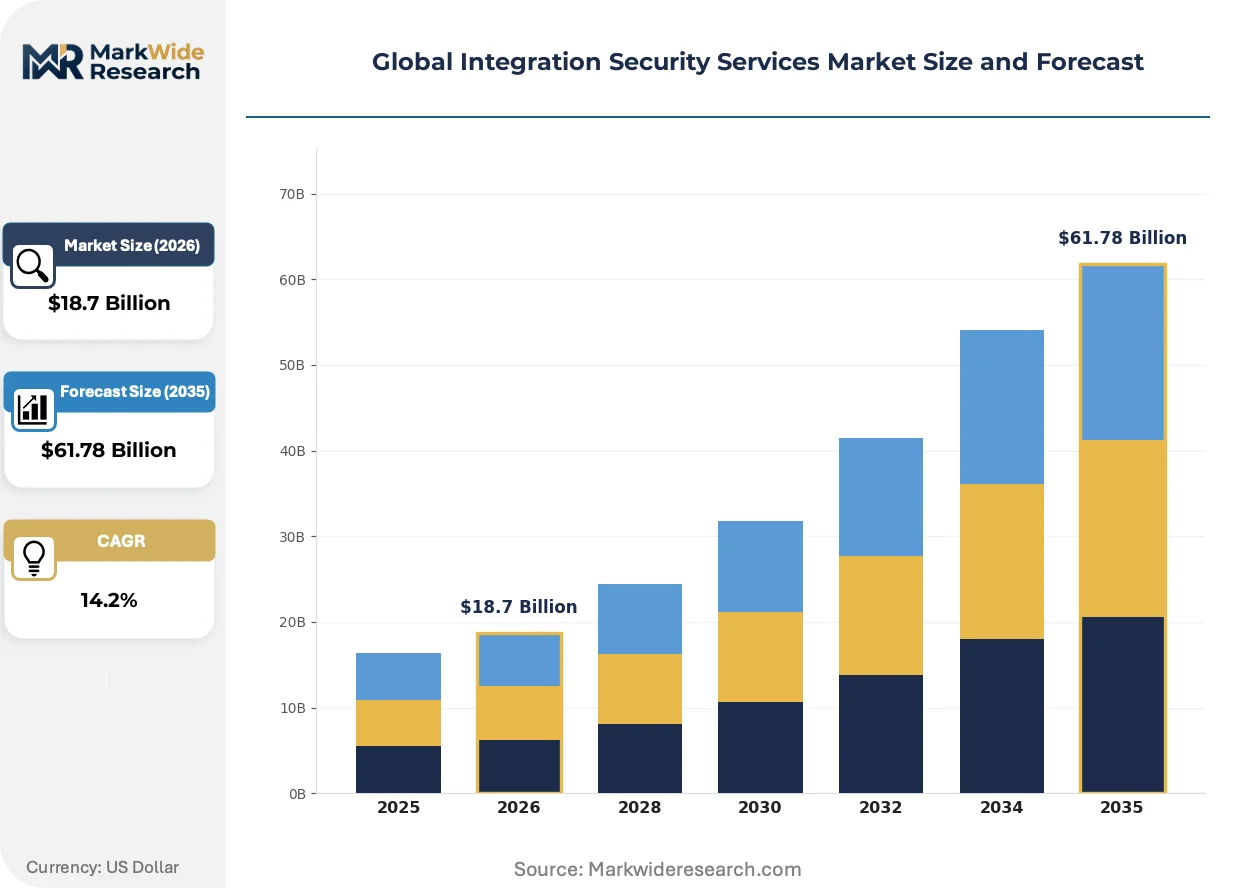
| Market Size in 2026 | $18.7 Billion |
| Market Size in 2035 | $61.78 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Network Security, Application Security, Cloud Security, Endpoint Protection Deployment Model: On-Premise, Cloud-Based, Hybrid, Managed Services Customer Type: SMEs, Large Enterprises, Government, Non-Profit Organizations Industry Vertical: Finance, Healthcare, Retail, Telecommunications |
| Companies Covered | Johnson Controls, Honeywell International Inc., Cisco Systems, Inc., IBM Corporation, Siemens AG, Schneider Electric, Microsoft, Optiv Security Inc., Bosch Security Systems, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Integration Security Services Market Emerging Trajectories
Security service delivery is pivoting from tool-centric implementation to outcome-based continuous validation, with buyers prioritizing measurable mean-time-to-detect metrics over technology stack breadth. This reorientation favors providers with native threat intelligence and automated response capabilities.
Extended detection and response platforms are hybridizing network, endpoint, and cloud telemetry into unified data lakes that enable cross-domain threat correlation. Financial services firms with mature security operations centers are adopting these architectures fastest, compressing procurement cycles for standalone point solutions. The technology is hybridizing vendor competitive dynamics around data ingestion scale rather than feature differentiation.
The EU AI Act's risk-classification framework for automated security decision systems is mandating human-in-the-loop governance and algorithmic transparency documentation. Industrial operators deploying AI-driven anomaly detection must now maintain audit trails and impact assessments. Manufacturing verticals with safety-critical OT environments are responding by segmenting high-risk AI applications from lower-risk automation tooling.
Enterprise buyers are consolidating vendor relationships around integrated security platforms rather than best-of-breed point solutions. Mid-market organizations with limited security staff are displacing multi-vendor stacks with packaged managed services that abstract integration complexity. This concentration is most visible in US healthcare, where hospital systems are reducing average security vendor counts from twelve to four to streamline incident response coordination.
Global Integration Security Services Market Segmentation
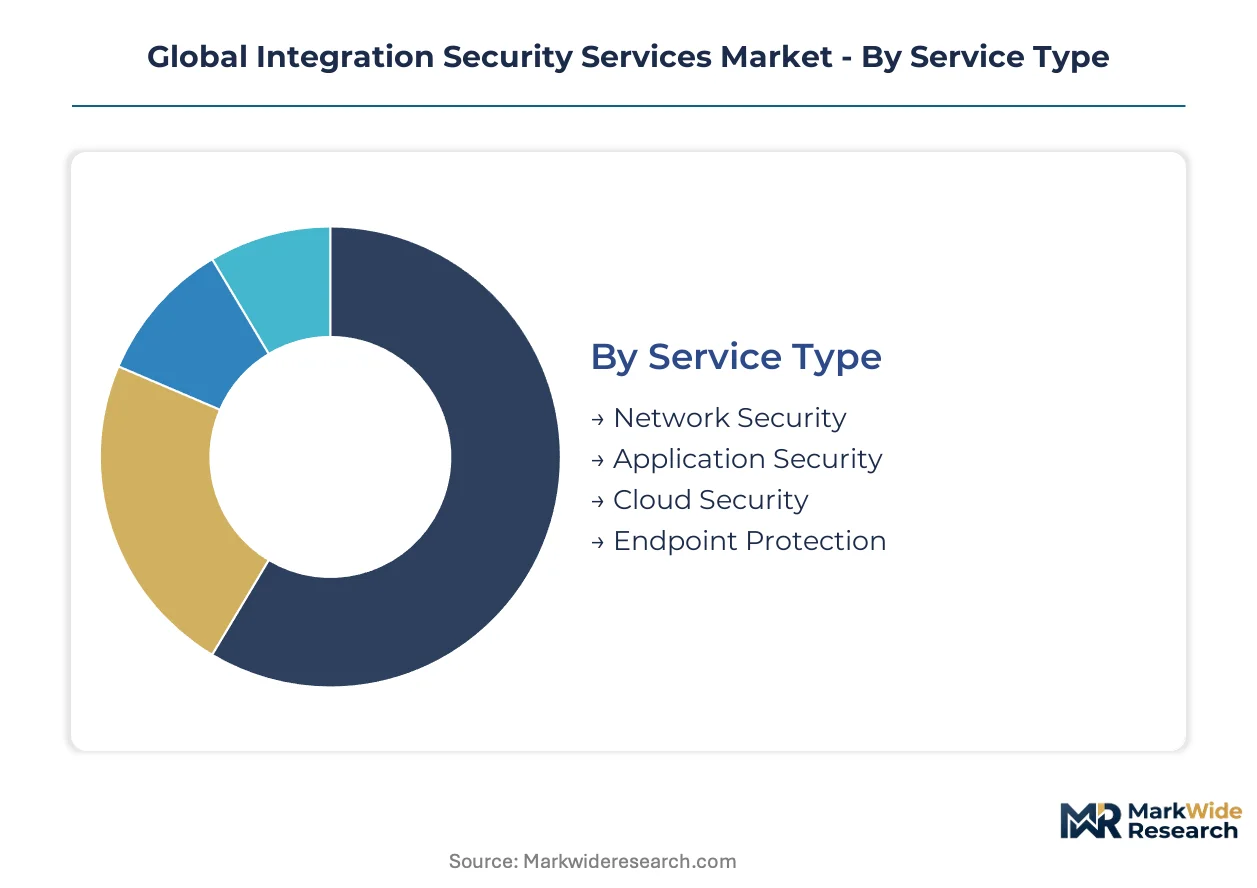
Segmentation in integration security services reveals how procurement patterns diverge across technical architectures, operational models, and compliance maturity. Buyers with heterogeneous IT/OT environments prioritize orchestration capabilities over point-solution depth, reshaping how vendors structure service portfolios.
Service Type:
Mature network security services coexist with rapidly maturing cloud protection offerings as enterprise workloads migrate.
- Network Security:Perimeter defense architectures incorporating next-generation firewalls, intrusion prevention systems, and zero-trust network access. Financial services firms in Frankfurt and Singapore retain substantial investment here due to legacy mainframe connectivity requirements and regulatory audit expectations.
- Cloud Security:Native workload protection, cloud access security brokers, and container security orchestration. India's domestic SaaS providers and Germany's industrial Mittelstand are expanding procurement fastest under CERT-In and NIS2 compliance pressures.
- Application Security:Secure software development lifecycle integration and runtime application self-protection.
- Endpoint Protection:Unified endpoint detection and response spanning traditional devices and IoT/OT assets.
Network Security handles the majority of throughput; Cloud Security is gaining share fastest as migration timelines compress.
Deployment Model:
Cost tier differentiation separates capital-intensive on-premise builds from operational-expense-driven managed alternatives.
- Managed Services:Fully outsourced security operations center functions with defined SLA metrics for detection and response. US healthcare systems and UK critical infrastructure operators favor this model to address SIEM engineer shortages and 24/7 coverage requirements.
- Hybrid:Orchestrated control planes spanning on-premise appliances and cloud-native security services. Japanese automotive manufacturers and Australian mining operators deploy this architecture to maintain data residency while leveraging scalable cloud analytics.
- On-Premise:Air-gapped or sovereign-controlled security infrastructure with localized threat intelligence.
- Cloud-Based:Fully cloud-delivered security services without local appliance footprint.
Managed Services commands the largest contract value; Hybrid deployments show the steepest expansion trajectory among regulated industries.
Customer Type:
Volume concentration varies sharply between compliance-mandated government procurement and efficiency-driven commercial adoption.
- Large Enterprises:Multi-domain integration programs spanning global footprints with dedicated security architecture teams. French energy utilities and Canadian banks are consolidating vendor relationships around integrated platforms to reduce coordination overhead.
- SMEs:Packaged managed security offerings that abstract integration complexity through standardized playbooks. Brazil's mid-market fintech sector and South Korea's semiconductor suppliers are adopting these services as regulatory requirements extend beyond large-firm thresholds.
- Government:Sovereign security frameworks with classified or sensitive data handling mandates.
- Non-Profit Organizations:Grant-funded or donor-supported security improvements with limited operational budgets.
Large Enterprises dominate absolute spending; SMEs are expanding most quickly as managed service packages democratize access.
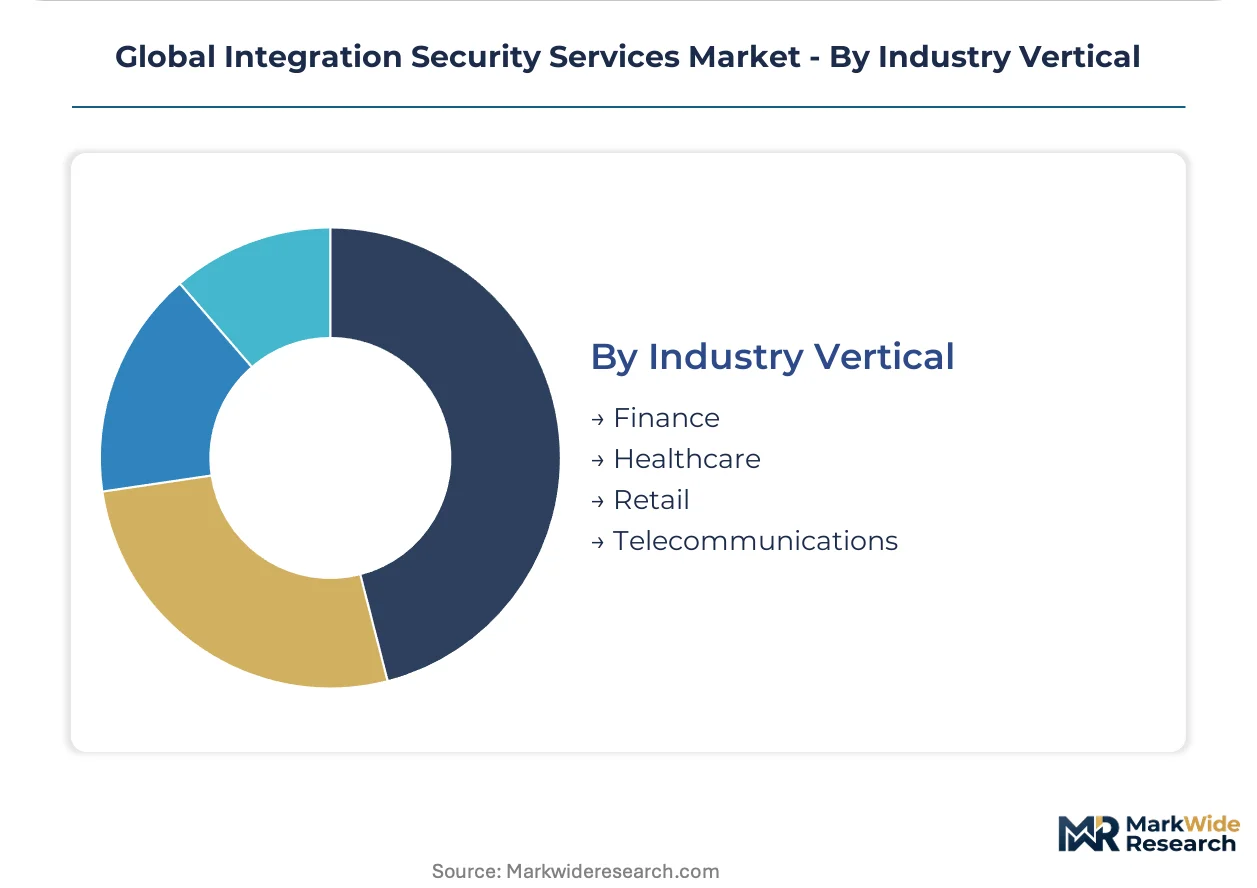
Industry Vertical:
Margin structures diverge between transaction-volume-driven finance and safety-critical healthcare with extended procurement cycles.
- Finance:Real-time fraud detection, SWIFT network protection, and open banking API security. UAE's financial free zones and Switzerland's private banking centers are prioritizing integrated architectures to satisfy FATF and FINMA expectations.
- Healthcare:FDA-aligned medical device security and HIPAA-compliant data loss prevention. US hospital systems and Saudi Arabia's healthcare privatization initiatives are converging physical access and clinical network security.
- Retail:Point-of-sale protection and e-commerce platform security with seasonal demand scaling.
- Telecommunications:5G network slicing security and subscriber data protection under national lawful access frameworks.
Finance generates the highest contract velocity; Healthcare shows the fastest climb in integration complexity requirements.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Export-import dynamics in security services reveal a services trade surplus in the United States and Germany against rising domestic capability building in India. Cross-border managed security operations face friction from encryption export controls and data localization mandates. Sovereign cybersecurity frameworks are reshaping where integration contracts originate and terminate.
United States
Federal zero-trust mandates and state-level privacy laws in Virginia and Colorado are accelerating procurement. The SEC cyber disclosure rules and FDA medical device guidance compel healthcare and financial firms toward unified architectures. Hospital systems in Texas and California are consolidating vendor relationships to streamline incident response.
Germany
The NIS2 Directive mandates critical infrastructure audits across energy and transport operators. Industrial Mittelstand manufacturers in Bavaria and North Rhine-Westphalia are procuring converged physical-cyber security for smart factory deployments. Frankfurt's financial center retains substantial network security investment due to legacy mainframe connectivity requirements.
India
CERT-In's six-hour incident reporting rule and designated security auditor requirements are expanding managed detection services. Domestic SaaS providers and fintech clusters in Bangalore and Hyderabad are adopting packaged integration offerings. Mumbai's financial institutions are building sovereign security operations centers under RBI guidance.
United Kingdom
Critical infrastructure operators favor managed services models to address SIEM engineer shortages and continuous coverage gaps. The National Cyber Security Centre's guidance shapes procurement standards for energy and healthcare verticals. London's financial services firms are compressing procurement cycles for extended detection platforms.
Japan
Automotive manufacturers deploy hybrid architectures to maintain data residency while leveraging cloud analytics. METI's industrial cybersecurity guidelines are converging IT and OT security procurement for smart manufacturing. Nagoya's automotive cluster and Osaka's industrial belt represent concentrated demand for converged integration services.
Global Integration Security Services Market Vendor Landscape
On the supply side, the industry is tiered between infrastructure-hardware bundlers, consulting-led transformation practices, and pure-play managed security specialists. Hyperscale cloud providers dominate native tooling, creating concentration risk for multi-cloud orchestration seekers. Strategic archetypes include network-equipment incumbents extending security layers, industrial-automation vendors converging physical-cyber domains, and IT services firms anchoring enterprise credibility through advisory-led engagements. Competitive moves center on portfolio consolidation around integrated platforms and geographic expansion through compliance-certified delivery centers.
Within the infrastructure-bundler tier, Cisco Systems, Inc. and Honeywell International Inc. occupy positions that leverage installed hardware bases for security integration attach. IBM Corporation anchors the consulting-led archetype through enterprise transformation practices. These three exemplify how vendor origin—networking, industrial automation, and IT services respectively—shapes competitive positioning without requiring identical capability builds.
| Leading Market Players |
|---|
| Johnson Controls |
| Honeywell International Inc. |
| Cisco Systems, Inc. |
| IBM Corporation |
| Siemens AG |
| Schneider Electric |
| Microsoft |
| Optiv Security Inc. |
| Bosch Security Systems |
| Others |
Supply Flow & Price Mechanics
Overcapacity in managed security operations centers across India and Eastern Europe is compressing margins for commoditized threat detection tiers while amplifying pricing power for specialized OT/IT convergence capabilities. This utilization asymmetry drives vendor consolidation toward premium service bundles and accelerates procurement of outcome-based contracts with defined SLA metrics.
Pricing Analysis
Industrial OEM buyers anchor a three-tier pricing structure across premium, standard, and economy levels. Premium tiers command differentiation through IEC 62443 certification depth and cross-domain SIEM orchestration, while economy tiers face compression from offshore SOC competition. Pricing pressure stems from hyperscale cloud providers bundling native security tooling at marginal cost. Mid-market manufacturers exhibit highest price sensitivity, whereas financial institutions with regulatory audit obligations demonstrate lowest.
Supply Chain Analysis
Extended payment terms from systems integrators to specialist engineering subcontractors are stretching working capital cycles across the vendor ecosystem. Component concentration centers on Israel for threat intelligence feeds, Ireland for EU data residency infrastructure, and Singapore for Asia-Pacific SOC delivery. Raw material dependencies span specialized semiconductors for hardware security modules, proprietary threat data licensing, and certified personnel pipelines. Single-source vulnerability runs through concentrated SIEM platform licensing. Distribution feeds from direct enterprise sales with managed service layering.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Platform economics are reshaping competitive boundaries as interoperability mandates under the EU AI Act and NIS2 Directive force vendor consolidation around integrated control planes rather than point-solution stacks.
For Market Incumbents: Pre-empt margin erosion from hyperscale bundling by deepening IEC 62443 certification coverage and acquiring boutique OT security specialists with smart factory deployment experience. Vertical integration into sovereign cloud infrastructure within Germany and India addresses data localization requirements before compliance deadlines harden procurement standards. For New Entrants and Emerging Players: Mid-market commercial buildings in Southeast Asia represent the most penetrable entry point for converged physical-cyber security integration, given lagging NIS2-equivalent mandates and fragmented incumbent presence. German industrial Mittelstand manufacturers with legacy OT environments offer secondary white-space opportunity. Channel partnerships with building automation distributors provide fastest go-to-market velocity. For Investors and Strategic Acquirers: Capital is best deployed toward managed security specialists with proven multi-cloud orchestration capabilities and existing CERT-In or NIS2 compliance certifications. Long-term viability hinges on differentiation from hyperscale commodity tiers. The signal to watch is consolidation velocity among hospital systems and critical infrastructure operators reducing vendor counts.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies network, endpoint, and cloud telemetry under single orchestration layer for financial services SOCs. |
| Acquisition of Specialist Firm | Captures IEC 62443-certified OT engineering talent scarce in open labor markets. |
| Geographic Expansion | Establishes sovereign delivery centers in Germany and India under NIS2 and CERT-In mandates. |
| Strategic Partnership | Links threat intelligence providers with SIEM vendors for automated playbook generation. |
| Product Launch | Introduces AI-powered anomaly detection with human-in-the-loop governance for EU AI Act compliance. |
Methodological Framework
Operator-level perspectives from CISOs, SOC managers, OT security engineers, and critical infrastructure procurement officers anchored the qualitative base. Primary fieldwork combined structured interviews with secondary validation against SEC filings, EU regulatory impact assessments, CERT-In compliance documentation, and hyperscaler security service disclosures. Bottom-up contract value analysis triangulated against top-down market sizing across service type, deployment model, and customer type segmentation dimensions.
Scenario-bracketing framed the analytical approach, with sensitivity testing across regulatory acceleration and delayed compliance adoption paths throughout the forecast period. Segmentation modeling incorporated service type, deployment architecture, customer scale tier, and vertical regulatory maturity. CAGRs derived from weighted average of historical contract velocity and projected procurement cycle compression. Industry-specific inputs included NIS2 audit timeline distributions and FDA medical device cybersecurity guidance implementation rates.
Macroeconomic conditions sit as an overlay; deviation in interest rate environments affecting project finance availability or escalation in encryption export control restrictions would shift the trajectory. Forecasts reflect documented assumptions regarding compliance deadline adherence and vendor consolidation velocity. Macroeconomic, regulatory, or technological deviation would prompt revision.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Crowdsourced Security Market
Security and Surveillance
Maritime Security Market
Security and Surveillance
Global Security Advisory Services Market
Security and Surveillance
Home Security Sensors Market
Security and Surveillance
Global Alarm Monitoring Market
Security and Surveillance
Sirens Market
Security and Surveillance
Shock Sensor Market
Security and Surveillance
Air Cargo Screening Systems Market
Security and Surveillance
Latin America Security Services Market
Security and Surveillance
Security Product Integration Services Market
Security and Surveillance
Security System Integrators Market
Security and Surveillance
Middle East and Africa Cargo and Vehicle Screening Market
Security and Surveillance
Explosive Trace Detection Market
Security and Surveillance
Latin America Electronics Security Market
Security and Surveillance
Global Acoustic Hailing Devices Market
Security and Surveillance
Smart Security in Healthcare Market