
 Global GDPR Services Market | 2026-2036
Global GDPR Services Market Size, Share, and Industry Trends Forecast 2026-2036
Global GDPR Services Market Foresight
The EU Green Deal's digital sustainability mandates are rebalancing procurement priorities across enterprise data governance programs. IBM Corporation leverages its consulting arm to anchor complex multi-jurisdiction implementations for Fortune 500 clients. Microsoft Corporation competes through native integration of compliance tooling within Azure's broader cloud stack. OneTrust, LLC dominates the dedicated privacy-software niche with specialized workflow automation for DPIA documentation.
Global GDPR Services encompass technical and advisory offerings that operationalize the European Union's General Data Protection Regulation across data lifecycle management, incorporating encryption protocols, pseudonymization techniques, and automated consent-tracking architectures. These services enable lawful processing of personal data while mitigating regulatory exposure for controllers and processors operating in or targeting EU resident populations. Audit and Compliance services currently occupy the largest revenue share as organizations face intensified supervisory authority scrutiny, while Cloud-Based delivery models represent the fastest-expanding structural segment due to elastic scalability for mid-market adopters. Software-as-a-Service configurations are concentrating margin pools among vendors achieving platform standardization across recurring subscription frameworks.
The European Data Protection Board coordinates enforcement consistency among national regulators including France's CNIL and Germany's federal data protection authorities, elevating compliance costs for non-EU service providers seeking market access. EDPB guidelines on cross-border data transfers directly shape vendor certification requirements and contractual liability allocations. Stakeholders must monitor evolving adequacy decisions and emerging sector-specific codes of conduct to anticipate binding compliance obligations before operational disruption materializes.
Market Dynamics
The EU AI Act's intersection with GDPR Article 22 automated decision-making rules is forcing financial services firms across Germany and France to rebuild consent architectures from the ground up. This regulatory collision is accelerating procurement of integrated compliance stacks that unify data governance with algorithmic accountability.
Growth Catalysts
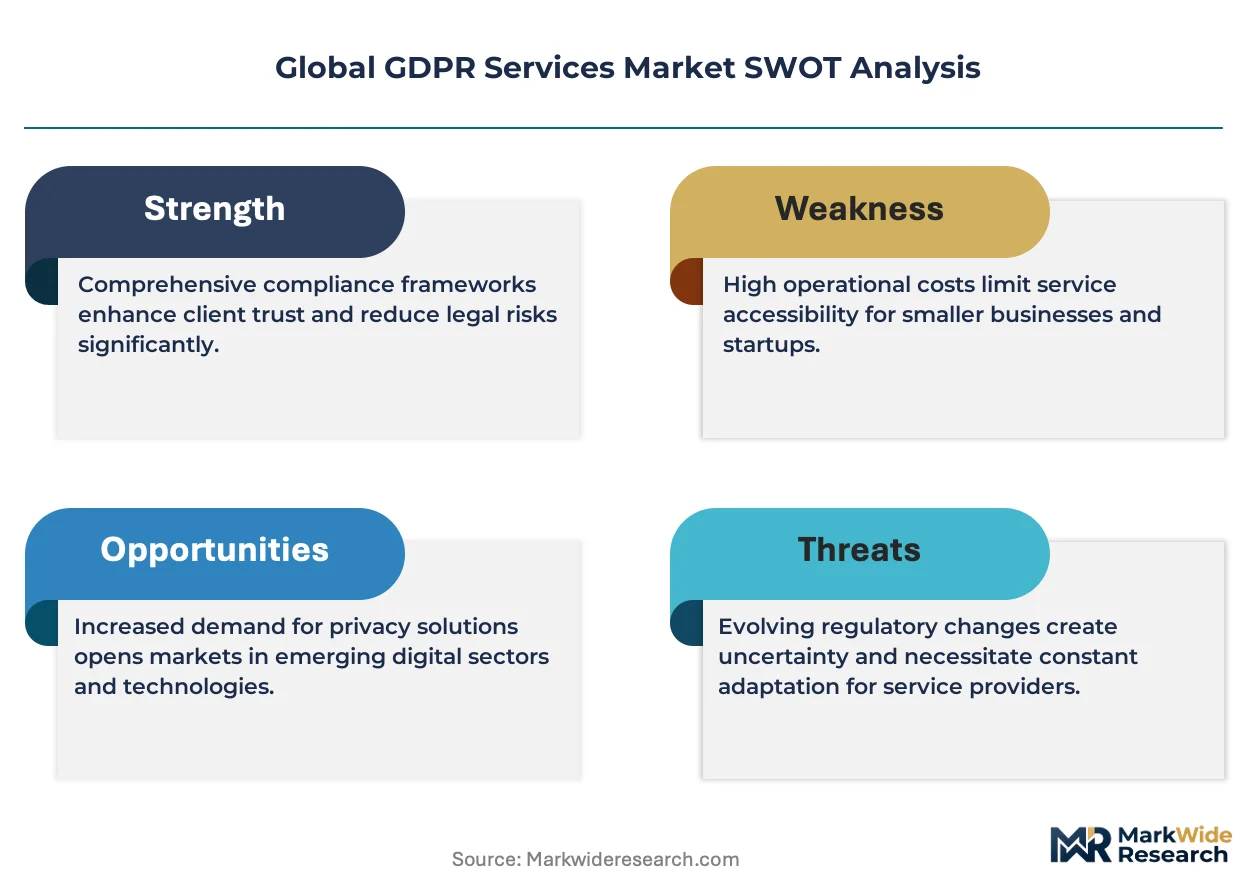
- Cross-border enforcement coordination:The European Data Protection Board's binding decisions on international data transfers are compelling non-EU cloud providers to adopt EU-standard contractual clauses. This creates captive demand for localization services.
- France's CNIL penalty escalation:Record administrative fines against ad-tech processors are driving mid-market retailers toward automated Data Protection Impact Assessment workflows.
- Quantum-resistant encryption mandates:Germany's federal data protection authorities are signaling future requirements for post-quantum cryptographic protocols in personal data processing systems.
Market Restraints
- Certification scarcity:Only a handful of EU-accredited bodies can issue ISO 27701 privacy management certifications, creating 6-9 month backlogs for processor validation.
- Input cost volatility:Specialized legal-technical hybrid talent commands premium compensation in London and Frankfurt, inflating implementation costs for boutique advisory firms.
- Technical limitation:Legacy mainframe systems at German universal banks lack API-native architectures, blocking real-time consent revocation capabilities required by GDPR Article 7.
Strategic Opportunities
- Underpenetrated mid-market:Spanish and Italian manufacturing SMEs with EU export exposure remain underserved by automated compliance tooling, presenting white-space for SaaS platforms.
- Regulatory tailwind:The EU Green Deal's digital sustainability reporting requirements are creating hybrid procurement budgets that combine CSRD and GDPR compliance spending.
- Technology convergence:Privacy-enhancing computation techniques including federated analytics and differential privacy are merging with established encryption services to enable new data-sharing revenue models.
Industry Challenges
- Skill bifurcation:The shortage of professionals fluent in both French regulatory interpretation and Azure cloud architecture is delaying multi-jurisdiction rollouts for Paris-headquartered multinationals.
- Integration friction:SAP ERP environments at German industrial conglomerates require custom middleware development to connect with modern consent-management platforms, extending project timelines.
- Certification complexity:Divergent national implementations of GDPR Article 83 penalty frameworks between Berlin and Rome create uncertainty in liability insurance pricing for cross-border processors.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global GDPR Services Market |
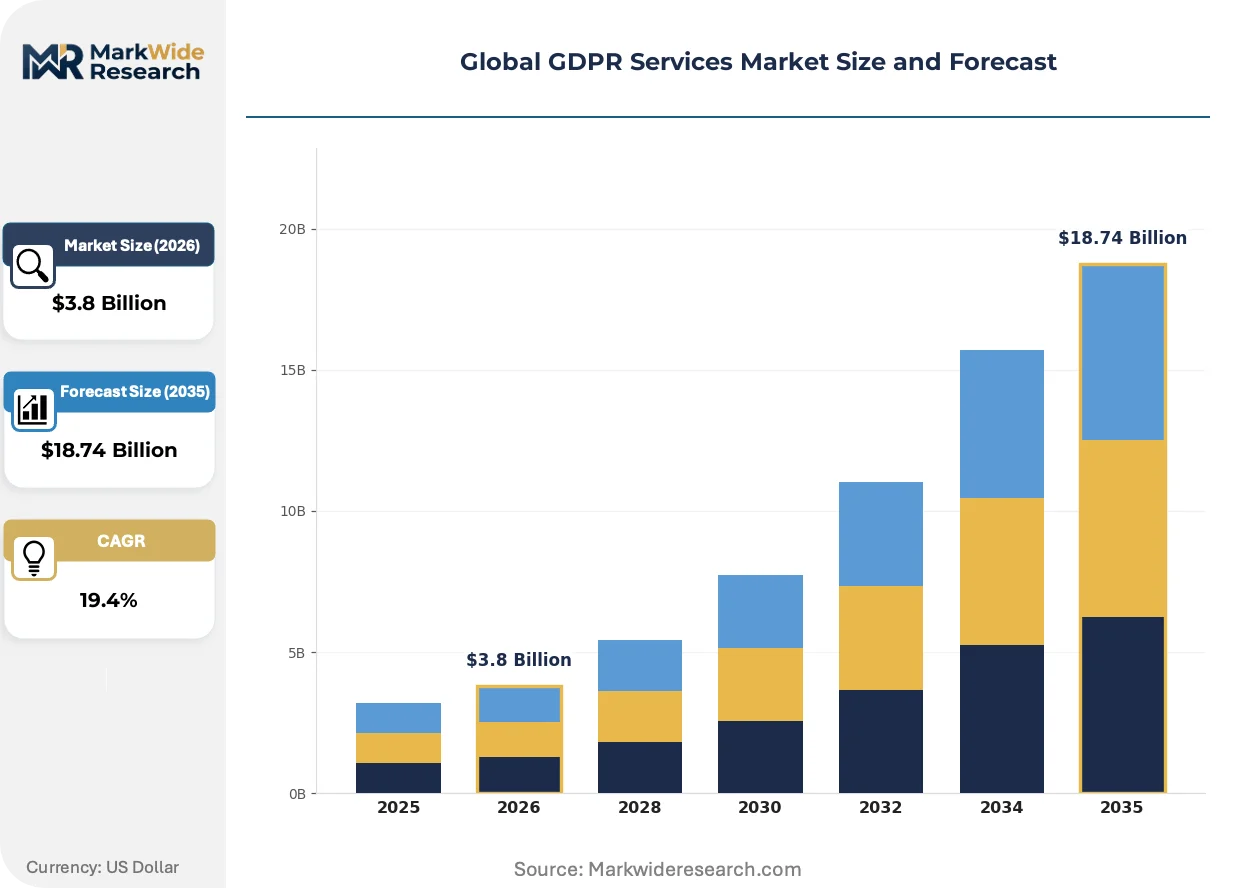
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $18.74 Billion |
| CAGR (2026 – 2036) | 19.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Audit & Compliance, Data Protection Impact Assessment, Training & Awareness, Consultation, Monitoring & Reporting Delivery Model: On-Premises, Cloud-Based, Hybrid, Software-as-a-Service End User: Financial Institutions, Technology Firms, Telecommunication Providers, Hospitality Chains, Educational Institutions Application Area: Customer Data Management, Employee Data Handling, Vendor Risk Management, Incident Response, Consent Management |
| Companies Covered | IBM Corporation, Microsoft Corporation, Oracle Corporation, Capgemini, Amazon Web Services, Inc., SAP SE, Informatica Inc., OneTrust, LLC, Accenture, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global GDPR Services Market Shifts & Advancements
Automated compliance orchestration is displacing point-solution procurement as enterprises seek unified control planes spanning data mapping, risk scoring, and regulatory reporting. Vendors are racing to embed artificial intelligence into workflow engines without triggering Article 22 scrutiny.
Privacy-enhancing technologies including secure multi-party computation and homomorphic encryption are converging with established tokenization services to enable analytics on encrypted personal data. Healthcare consortia in the Netherlands and Belgium are piloting these architectures for cross-hospital research. The structural consequence is a compression of traditional data-anonymization consulting margins as automation substitutes for manual risk assessments.
The EU AI Act's risk-classification framework is mandating algorithmic impact documentation that overlaps substantially with GDPR Data Protection Impact Assessments. Medical device manufacturers in Ireland and Sweden are consolidating compliance workflows to satisfy both regimes simultaneously. This regulatory layering is favoring vendors with pre-built template libraries spanning AI Act Annex III and GDPR Article 35 requirements.
Subscription-based compliance monitoring is replacing episodic audit engagements among mid-market data processors. Dutch e-commerce platforms and Danish logistics providers are adopting continuous-control validation models that stream telemetry to supervisory authorities. This shift is most visible in the Benelux region where CNIL and DPA coordination has normalized proactive disclosure expectations.
Global GDPR Services Market Segmentation
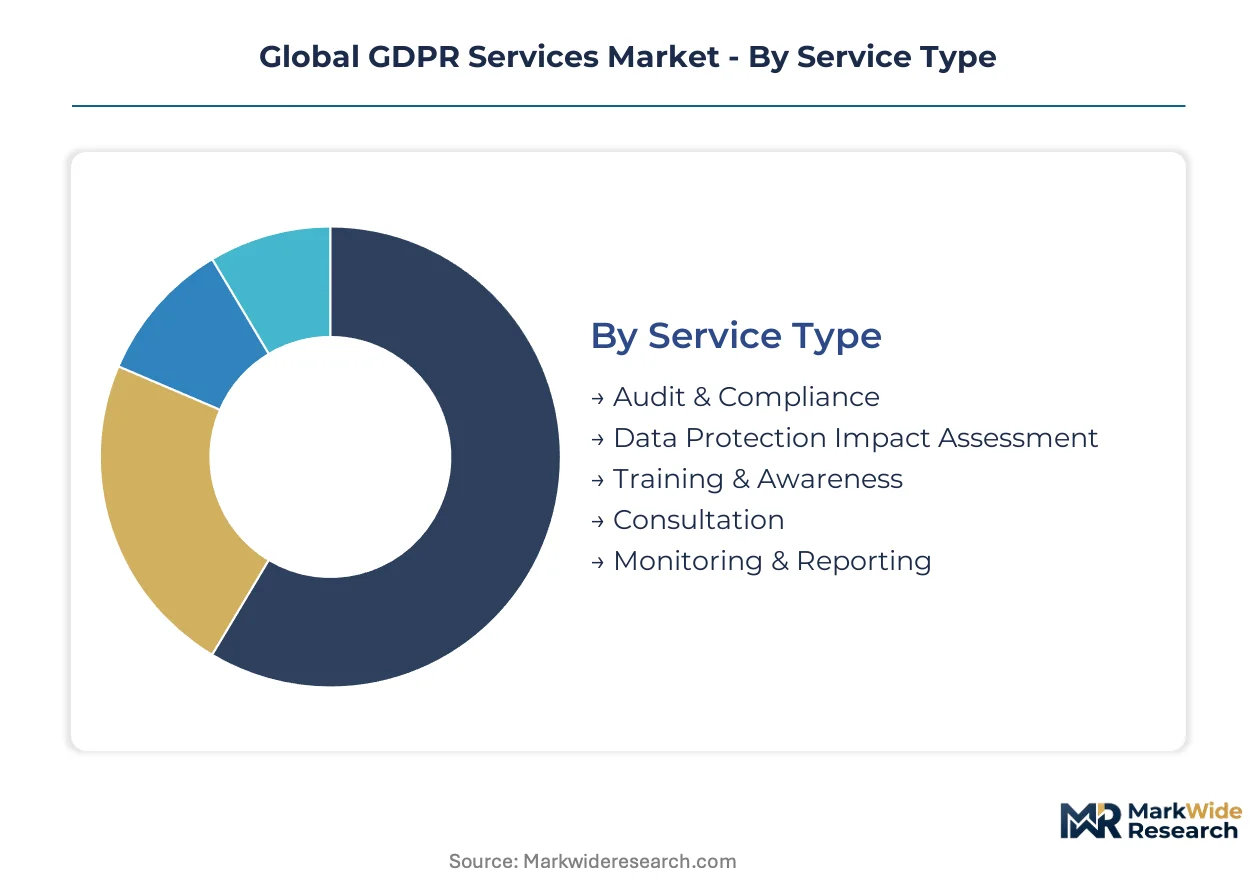
Service differentiation in GDPR compliance reflects divergent risk tolerances and technical maturity across data controllers. Procurement patterns cluster around audit intensity and automation readiness rather than uniform regulatory exposure.
Service Type:
Vendor capability concentrates most heavily in audit and documentation services, while specialized advisory functions remain fragmented across boutique legal-technical hybrids.
- Audit & Compliance:Systematic verification of controller and processor adherence to GDPR Articles 5-50 through documentation review, technical testing, and gap remediation planning. German automotive suppliers and French banking groups drive demand for integrated audit frameworks that satisfy both GDPR and sectoral supervisory requirements. This segment absorbs the bulk of installed capacity; Data Protection Impact Assessment is expanding most quickly.
- Data Protection Impact Assessment:Structured evaluation of high-risk processing operations per Article 35, encompassing necessity analysis, stakeholder consultation, and mitigation specification. Dutch healthcare consortia and Belgian research institutions are mandating automated DPIA workflows for cross-border data sharing. Healthcare consortia in the Netherlands and Belgium are mandating automated DPIA workflows for cross-border data sharing.
- Training & Awareness:Workforce education programs covering data subject rights, breach notification protocols, and role-specific accountability frameworks.
- Consultation:Advisory engagements on lawful basis selection, international transfer mechanisms, and supervisory authority negotiation strategies.
- Monitoring & Reporting:Continuous oversight services including regulatory horizon scanning, incident trend analysis, and board-level compliance dashboards.
Audit & Compliance captures dominant procurement budgets; Data Protection Impact Assessment climbs the fastest as automated tooling penetrates mid-market healthcare and research verticals.
Delivery Model:
Cost tiering separates enterprise-grade customization from standardized subscription offerings, with mid-market adopters gravitating toward elastic consumption models.
- Cloud-Based:Scalable infrastructure provisioned through hyperscaler or specialist vendor platforms, enabling rapid deployment without capital expenditure. Spanish manufacturing SMEs and Italian logistics providers favor cloud delivery for cross-border processor arrangements requiring EU data residency. Cloud-Based commands the largest addressable market; Software-as-a-Service gains share fastest.
- Software-as-a-Service:Pre-configured compliance platforms delivered via recurring subscription, emphasizing workflow automation and template libraries. Danish e-commerce platforms and Dutch professional services firms are consolidating consent management and incident response onto unified SaaS stacks. Danish e-commerce platforms and Dutch professional services firms are consolidating consent management and incident response onto unified SaaS stacks.
- On-Premises:Dedicated infrastructure deployment within client-controlled facilities for maximum data sovereignty assurance.
- Hybrid:Architectures combining on-premises sensitive data processing with cloud-based analytics and reporting layers.
Cloud-Based absorbs the bulk of installed capacity; Software-as-a-Service is expanding most quickly.
End User:
Application complexity varies sharply across sectors, with regulated industries demanding bespoke implementations versus standardized retail and hospitality deployments.
- Financial Institutions:Universal banks, insurers, and payment processors managing high-volume transactional data subject to overlapping GDPR, PSD2, and AML obligations. German and French financial services firms are rebuilding consent architectures to accommodate EU AI Act intersection with Article 22 automated decision-making rules. German and French financial services firms are rebuilding consent architectures to accommodate EU AI Act intersection with Article 22 automated decision-making rules.
- Technology Firms:Software vendors, cloud providers, and ad-tech platforms serving as processors for diverse controller ecosystems.
- Telecommunication Providers:Mobile and fixed-line operators handling location data, traffic metadata, and subscriber information under sector-specific ePrivacy overlays.
- Hospitality Chains:Hotel groups and travel platforms managing guest profiles, payment credentials, and loyalty program data across fragmented franchise structures.
- Educational Institutions:Universities and research organizations processing student records, biometric data, and international exchange participant information.
Financial Institutions anchor premium service consumption; Technology Firms are expanding most quickly as processor liability obligations intensify.
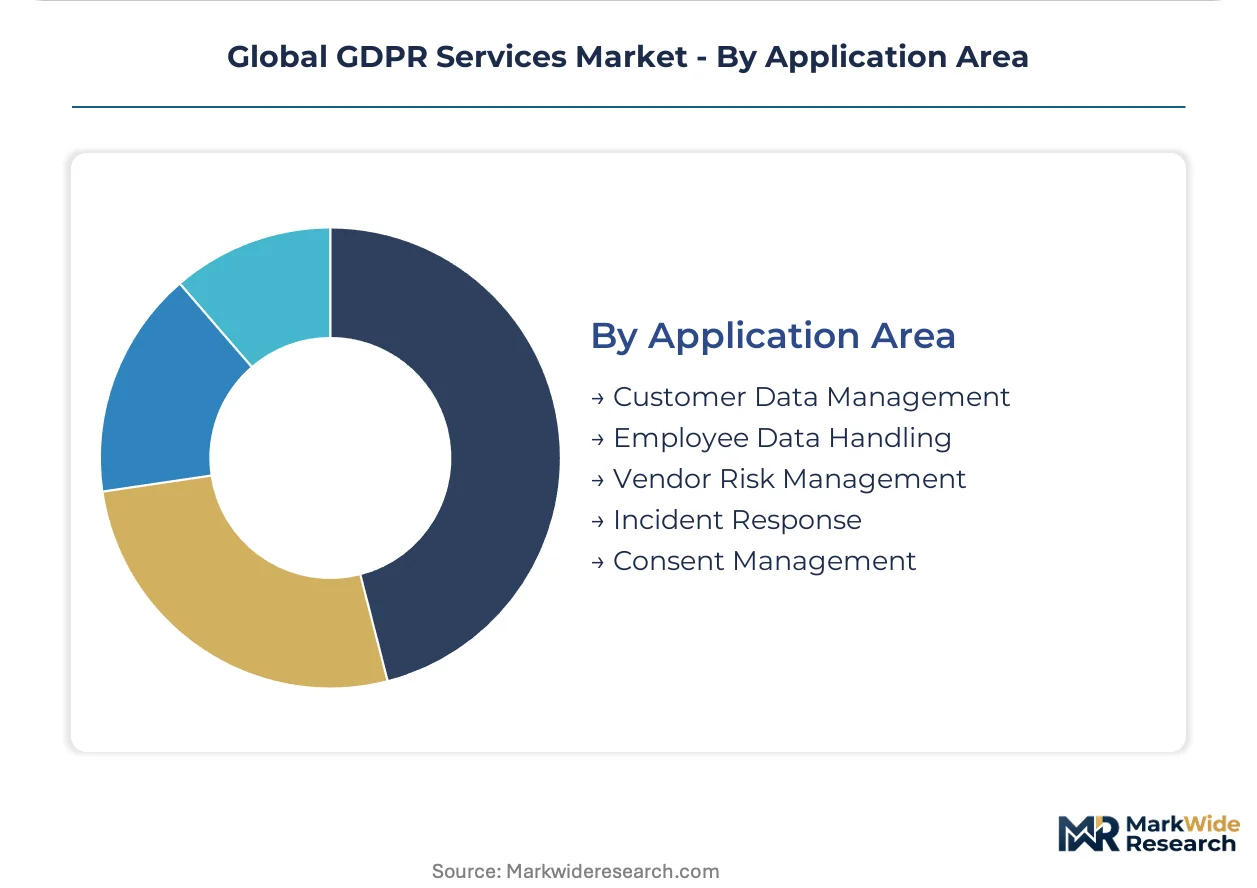
Application Area:
Maturity gradients separate established data governance functions from emerging automation frontiers, with consent management representing the most dynamic capability investment.
- Customer Data Management:Lifecycle governance of consumer personal data spanning collection, segmentation, retention scheduling, and deletion execution. Retail banking groups in France and digital marketplaces in the Netherlands are deploying unified customer data platforms with embedded GDPR compliance modules. Retail banking groups in France and digital marketplaces in the Netherlands are deploying unified customer data platforms with embedded GDPR compliance modules.
- Consent Management:Granular preference capture, withdrawal processing, and proof-of-consent documentation per Article 7 requirements. Irish medical device manufacturers and Swedish healthtech startups are consolidating GDPR consent workflows with EU AI Act risk classification documentation. Irish medical device manufacturers and Swedish healthtech startups are consolidating GDPR consent workflows with EU AI Act risk classification documentation.
- Employee Data Handling:Workforce information governance encompassing recruitment, performance monitoring, and cross-border HR system integration.
- Vendor Risk Management:Processor due diligence, contractual clause negotiation, and ongoing compliance verification across supply chains.
- Incident Response:Breach detection, supervisory authority notification, and data subject communication per Articles 33-34 timelines.
Customer Data Management absorbs the bulk of installed capacity; Consent Management is expanding most quickly.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Frankfurt's concentration of universal banks and supervisory authority headquarters generates concentrated demand for integrated compliance architectures spanning data governance and algorithmic accountability mandates.
Germany
Universal banks in Frankfurt and Munich are rebuilding consent frameworks to satisfy overlapping GDPR Article 22 and EU AI Act automated decision-making rules. Germany's federal data protection authorities are signaling post-quantum encryption requirements for personal data systems. Industrial conglomerates in Baden-Württemberg require custom middleware to connect SAP ERP environments with modern consent-management platforms.
France
CNIL's record administrative fines against ad-tech processors are driving mid-market retailers toward automated Data Protection Impact Assessment workflows. The EU Green Deal's digital sustainability mandates are rebalancing procurement priorities across Paris-headquartered enterprise data governance programs. Medical device manufacturers in Île-de-France are consolidating GDPR consent workflows with EU AI Act risk classification documentation.
United Kingdom
London's legal-technical hybrid talent scarcity inflates implementation costs for boutique advisory firms serving cross-border processor arrangements. The Information Commissioner's Office enforcement patterns are compelling non-EU cloud providers to adopt EU-standard contractual clauses for UK-EU data transfers. Fintech clusters in Canary Wharf are deploying unified customer data platforms with embedded GDPR compliance modules.
Netherlands
Dutch healthcare consortia are piloting privacy-enhancing computation techniques including federated analytics and homomorphic encryption for cross-hospital research. The European Data Protection Board's binding decisions on international data transfers are creating captive demand for localization services in Amsterdam's data center corridor. E-commerce platforms in Rotterdam are adopting continuous-control validation models that stream telemetry to supervisory authorities.
United States
Fortune 500 technology firms face intensified contractual liability allocations under evolving EDPB guidelines on cross-border data transfers. The absence of federal privacy legislation creates compliance fragmentation for US-based processors serving EU resident populations. Seattle and San Francisco Bay Area cloud providers are integrating compliance tooling within broader infrastructure stacks to capture mid-market GDPR procurement budgets.
Global GDPR Services Market Competitive Landscape
The competitive structure tilts toward diversified technology conglomerates with embedded compliance capabilities. Market concentration reflects tiered service differentiation between enterprise-grade consulting implementations and standardized SaaS subscriptions. Three archetypes dominate: hyperscaler cloud platforms with native governance modules, specialized privacy software vendors with workflow automation, and global consultancies anchoring multi-jurisdiction transformations. Strategic moves center on vertical capability integration and geographic expansion through regulatory expertise acquisition.
Within the diversified technology tier, IBM Corporation and Microsoft Corporation exemplify contrasting approaches to compliance service delivery. IBM's consulting arm anchors complex multi-jurisdiction implementations for enterprise clients requiring bespoke architectural integration. Microsoft competes through native embedding of compliance tooling within Azure's broader cloud infrastructure stack. OneTrust, LLC occupies the dedicated privacy-software niche, representing the specialized vendor archetype with concentrated workflow automation capabilities for Data Protection Impact Assessment documentation and consent management orchestration.
| Leading Market Players |
|---|
| IBM Corporation |
| Microsoft Corporation |
| Oracle Corporation |
| Capgemini |
| Amazon Web Services, Inc. |
| SAP SE |
| Informatica Inc. |
| OneTrust, LLC |
| Accenture |
| Others |
Supply & Pricing Matrix
Specialized legal-technical hybrid talent concentration in London and Frankfurt generates labor-cost differentials that widen pricing-tier spreads between boutique advisory engagements and standardized SaaS subscriptions. Premium implementation services command substantial markups over automated platform fees as firms compete for scarce professionals fluent in both French regulatory interpretation and Azure cloud architecture.
Pricing Analysis
Outcome-based pricing anchors enterprise engagements to audit completion and certification achievement rather than hourly rates. Three-tier pricing structure across premium, standard, and economy levels separates Fortune 500 multi-jurisdiction implementations from mid-market automated workflows and basic template libraries. Cost compression in the standard tier is intensifying because SaaS vendors are achieving platform standardization across recurring subscription frameworks. Mid-market data processors exhibit highest price sensitivity due to constrained compliance budgets, while universal banks demonstrate lowest sensitivity given regulatory penalty exposure.
Supply Chain Analysis
Returns and refurbishment flows for compliance tooling center on re-certification of audit documentation and update cycles for deprecated encryption protocols. Ireland and Sweden anchor software development for consent-management platforms, while Germany and France concentrate implementation services and regulatory advisory functions. The supply chain draws from cryptographic protocol libraries, cloud infrastructure provisioning, and specialized legal-technical workforce pipelines. Single-source vulnerability in EU-accredited ISO 27701 certification bodies creates 6-9 month validation backlogs. Distribution runs through direct vendor relationships for enterprise clients and hyperscaler marketplaces for mid-market adopters.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market constitutes a vertical-integration race where control over specialized legal-technical talent acquisition represents the decisive upstream lever. Players are pursuing captive workforce development to secure implementation capacity.
For Market Incumbents: Deepen backward integration into specialized training pipelines to lock in legal-technical hybrid talent before boutique competitors escalate compensation. Fortify certification pre-qualification with EU-accredited bodies to extend validation backlogs against emerging SaaS platforms. The threat of automated DPIA tooling from cloud-native entrants demands defensive capability investment in workflow automation.
For New Entrants and Emerging Players: Cloud-native distribution partnerships with hyperscaler marketplaces offer the lowest-friction customer acquisition path. Spanish and Italian manufacturing SMEs with EU export exposure represent the most penetrable white-space segment. Target automated consent-management platforms with pre-configured templates for mid-market healthcare and research verticals.
For Investors and Strategic Acquirers: The window for entry favors specialized privacy-software vendors with concentrated workflow automation capabilities and established template libraries. Long-term viability hinges on regulatory layering expertise spanning GDPR Article 35 and EU AI Act Annex III requirements. Monitor EDPB binding decisions on cross-border data transfers as the critical inflection signal for localization service demand.
| Strategic Initiative | Industry Significance |
|---|---|
| Acquisition of Specialist Firm | Captures regulatory expertise in French CNIL and German federal data protection authority interpretation. |
| Platform Integration | Unifies consent management with Azure or AWS native governance modules for seamless deployment. |
| Geographic Expansion | Establishes presence in Amsterdam's data center corridor to serve Benelux continuous-control validation demand. |
| Strategic Partnership | Links automated DPIA workflows with Irish and Swedish medical device manufacturer compliance programs. |
| Product Launch | Introduces quantum-resistant encryption modules ahead of Germany's anticipated post-quantum mandates. |
Research Methodology
Independent corroboration across data protection officers, compliance technology vendors, and supervisory authority representatives underwrites the qualitative findings in this study. Primary interviews with privacy software engineers, legal-technical implementation leads, and enterprise procurement officers combined with secondary validation against EDPB guidelines, CNIL enforcement decisions, and hyperscaler compliance disclosure filings. Bottom-up and top-down triangulation reconciled service-type demand patterns with cloud infrastructure provisioning trends.
Rate-of-change decomposition separated subscription renewal velocity from new-customer acquisition across the analysis window. Segmentation dimensions modeled encompass delivery model, service type, end-user vertical, and regional regulatory cluster. CAGRs derived from elasticity-adjusted adoption curves incorporating EU AI Act intersection effects and mid-market SaaS penetration rates. Forecast inputs included supervisory authority staffing levels and adequacy decision timelines.
The model holds under stable EDPB enforcement coordination; deviation in national penalty framework divergence or quantum-resistant mandate acceleration would shift trajectory. Forecasts reflect documented assumptions about regulatory layering and automation substitution rates. Practitioners should monitor EDPB binding decision frequency and ISO 27701 accreditation queue length for early signals.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Regulatory Compliance Technology
Regulatory Information Management System Market
Regulatory Compliance Technology
Anti-Money Laundering Systems Market
Regulatory Compliance Technology
Compliance Testing Solutions Market
Regulatory Compliance Technology
Nordic Regulatory Affairs Market
Regulatory Compliance Technology
United States Sales Tax Compliance Software Market
Regulatory Compliance Technology
Global Quality and Compliance Management Solution Market
Regulatory Compliance Technology
Global Regulatory Technology (Regtech) Market
Regulatory Compliance Technology
Global Anti- Money Laundering Solutions Market
Regulatory Compliance Technology
GDPR Assessment Tools Market
Regulatory Compliance Technology
Regulatory Change Management Software Market
Regulatory Compliance Technology
Regulatory Reporting Solutions Market
Regulatory Compliance Technology
Global AML Software Market
Regulatory Compliance Technology
General Data Protection Regulation (GDPR) Market
Regulatory Compliance Technology
Regtech Software Market
Regulatory Compliance Technology
US Anti Money Laundering Solution Market
Regulatory Compliance Technology
Compliance and Traceability Solutions Market