
 Global Embedded Security for Internet of Things Market | 2026-2036
Global Embedded Security for Internet of Things Market Size, Share, and Industry Trends Forecast 2026-2036
Global Embedded Security for Internet of Things Market Intelligence
Germany's industrial security infrastructure is narrowing the gap between legacy operational technology and modern IoT threat models. Arm leverages its TrustZone architecture to dominate semiconductor-level security integration across European device foundries. Bosch Global Software Technologies anchors its position through deep automotive embedded systems expertise and captive manufacturing scale.
Embedded security for Internet of Things encompasses hardware-rooted cryptographic modules, secure boot processes, and isolated execution environments that protect device integrity, data confidentiality, and authenticated communication across distributed sensor networks. These systems typically integrate tamper-resistant silicon, AES-256 encryption pipelines, and hardware security modules operating at sub-watt power envelopes to meet constrained edge device requirements. Hardware security modules currently lead solution offerings due to their immutable root-of-trust properties in critical infrastructure deployments, while edge computing security within deployment types captures expanding margin pools as latency-sensitive applications multiply. Secure elements sustain premium pricing in smart manufacturing and connected transportation where regulatory mandates enforce physical tamper evidence.
The EU Cyber Resilience Act imposes mandatory vulnerability disclosure and security update obligations on IoT device manufacturers selling into Europe, directly expanding demand for firmware protection and over-the-air secure update capabilities. The US NIST Cybersecurity Framework and FDA guidance on connected medical devices create parallel compliance pathways that shape product roadmaps across Atlantic markets. ISO/IEC 27400 standards for IoT security and privacy further harmonize baseline requirements that vendors must satisfy for cross-border procurement eligibility. Stakeholders must now weigh sovereign data residency rules against the economies of centralized security orchestration when architecting multi-national deployments.
Market Dynamics
The EU Cyber Resilience Act and AI Act are compressing certification timelines for IoT device manufacturers, forcing a wholesale re-architecture of firmware update pipelines and hardware trust anchors before products reach European distribution channels.
Growth Catalysts
- EU Cyber Resilience Act:Mandatory security update obligations and vulnerability disclosure requirements expand demand for over-the-air firmware protection across connected device portfolios.
- Automotive OEM mandates:Hardware-rooted trust anchors are becoming non-negotiable in connected vehicle platforms, pulling secure element volumes into seven-figure annual unit commitments.
- AES-256 encryption pipelines:Standardization around this cryptographic baseline is collapsing procurement friction for industrial buyers seeking interoperable security modules.
Market Restraints
- Silicon supply concentration:Foundry capacity for tamper-resistant security chips concentrates in Taiwan and South Korea, exposing procurement timelines to geopolitical friction.
- Certification cost structure:Common Criteria EAL4+ evaluation fees for hardware security modules exceed six figures per product variant, squeezing mid-volume device manufacturers.
- Power envelope limitations:Sub-watt operating requirements for edge devices constrain cryptographic acceleration, forcing trade-offs between security depth and battery life.
Strategic Opportunities
- India's industrial corridor:PLI scheme incentives for electronics manufacturing are drawing secure element packaging and test capacity away from traditional East Asian hubs.
- Post-quantum cryptography:NIST's finalized lattice-based standards create upgrade cycles for existing cryptographic modules in critical infrastructure deployments.
- Medical device convergence:FDA guidance on connected health devices is opening dedicated procurement channels for ISO/IEC 27400-certified security stacks.
Industry Challenges
- Firmware signing key management:Device manufacturers struggle to maintain hardware security module infrastructure for code signing across distributed engineering teams.
- Legacy OT integration:Brownfield industrial sites require protocol translation layers that expand attack surfaces while delivering regulatory-compliant monitoring.
- Common Criteria timeline compression:Evaluation lab backlogs are extending certification cycles, delaying product launches in regulated end-use verticals.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Embedded Security for Internet of Things Market |
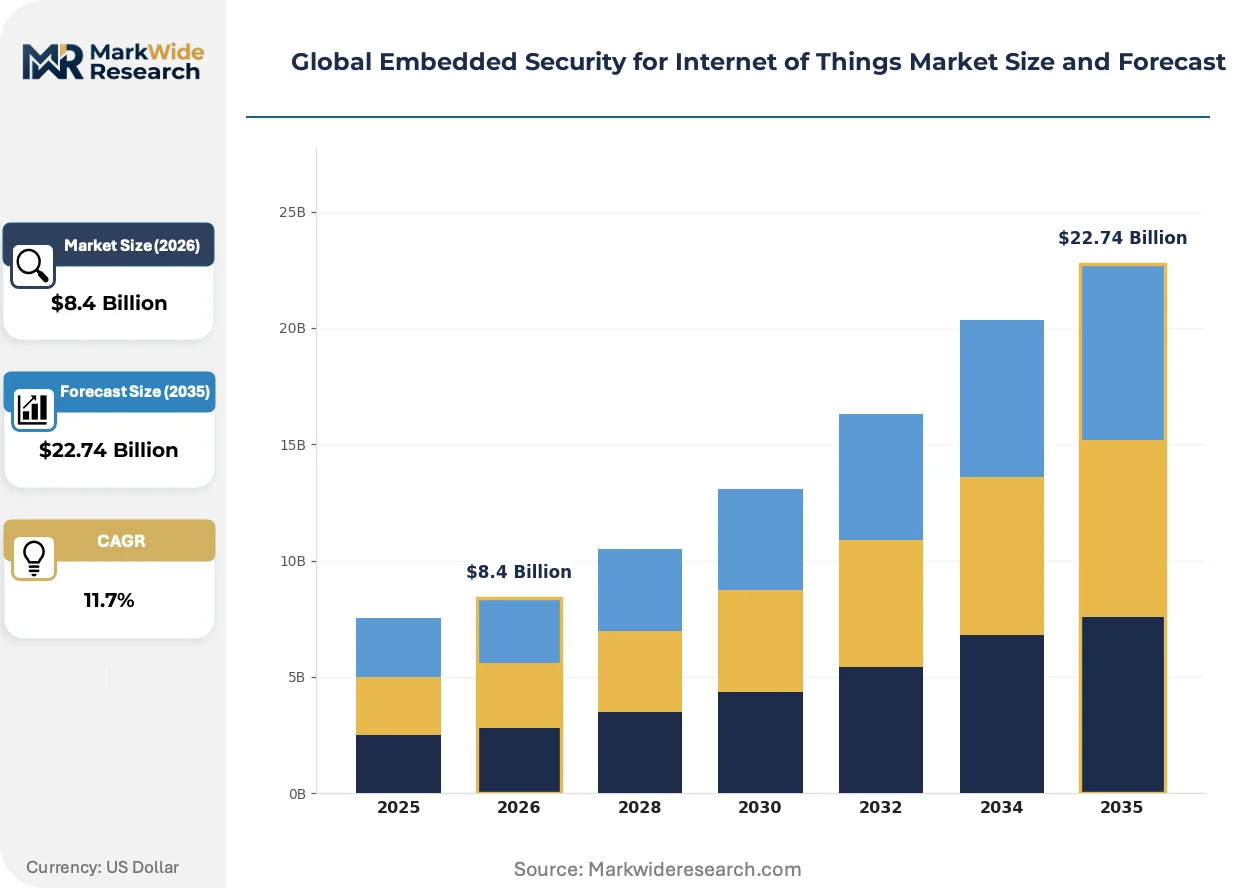
| Market Size in 2026 | $8.4 Billion |
| Market Size in 2035 | $22.74 Billion |
| CAGR (2026 – 2036) | 11.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Offering: Hardware Security Modules, Software Cryptography, Secure Element, Trusted Execution Environment, Biometric Authentication Deployment Type: Cloud-Based Security, On-Premises Protection, Hybrid Integration, Edge Computing Security, Network-Level Security Use Case: Access Control, Data Encryption, Device Authentication, Intrusion Detection, Firmware Protection End User Industry: Smart Manufacturing, Connected Transportation, Energy & Utilities, Smart Agriculture, Consumer Electronics |
| Companies Covered | Xage Security, Telit, Arm, Capgemini Engineering, Infosys, Claroty, Sierra Wireless, Bosch Global Software Technologies, Armis, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Embedded Security for Internet of Things Market Strategic Shifts & Innovations
Hardware security architectures are converging with cloud-native orchestration patterns, collapsing the traditional boundary between silicon-level trust and fleet-wide security policy management. This convergence is redrawing vendor competitive positions.
Physically unclonable functions are collapsing the cost structure of device-unique identity provisioning. Automotive tier-1 suppliers are adopting PUF-based secure boot at scale for ECU platforms. The technology is collapsing the historical trade-off between manufacturing volume and cryptographic individuality.
REACH restrictions on persistent organic pollutants are forcing substrate material transitions in secure element packaging. European device foundries are qualifying halogen-free laminates ahead of compliance deadlines. Medical device manufacturers face the steepest reformulation timelines due to FDA-EMA dual filing requirements.
Industrial buyers are consolidating vendor relationships around platforms offering unified firmware lifecycle management. Discrete component procurement is giving way to integrated security subscriptions bundling hardware, update infrastructure, and compliance documentation. German automotive and machinery OEMs are most advanced in this transition, using captive software subsidiaries to absorb integration complexity.
Global Embedded Security for Internet of Things Market Segmentation
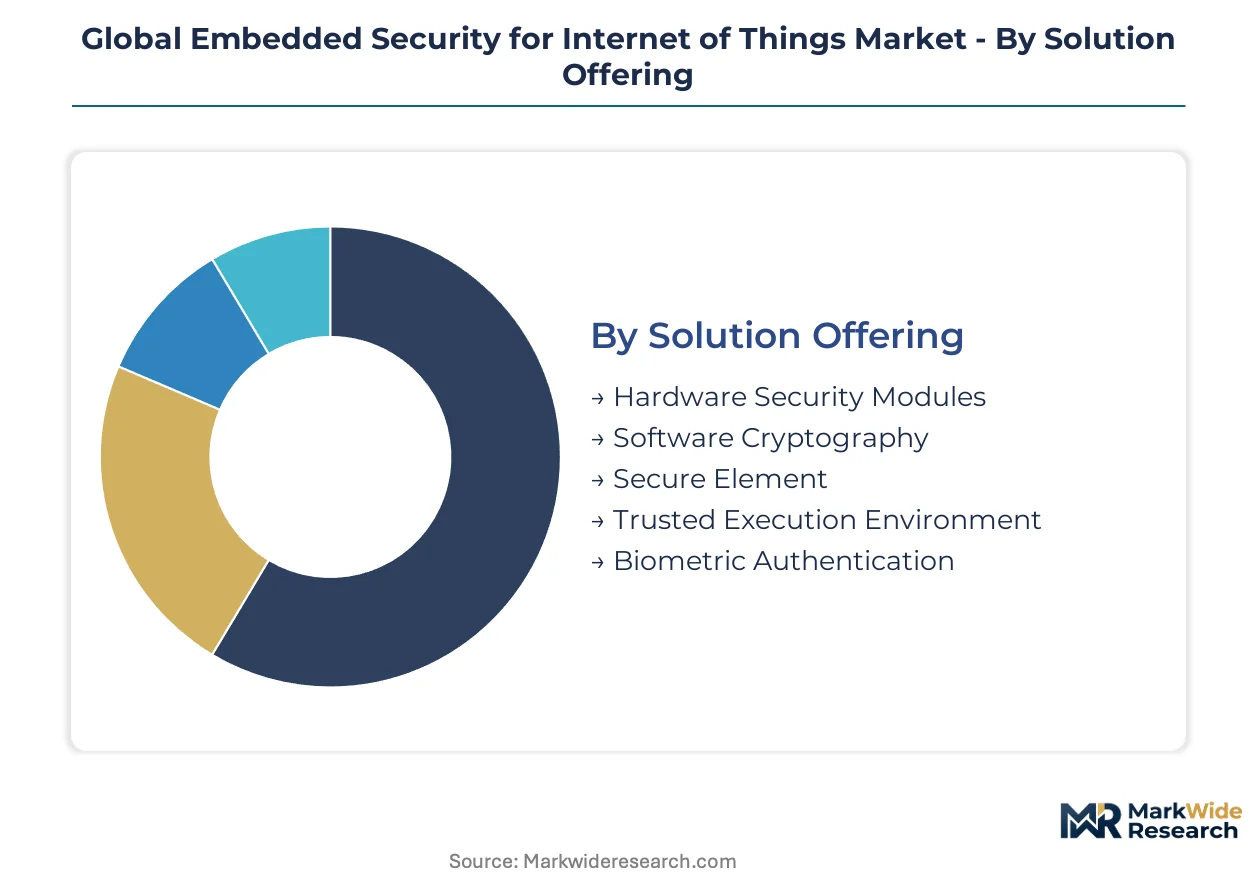
Segmentation in embedded IoT security reveals how procurement cycles, certification requirements, and power constraints fragment demand across hardware, software, and service layers. Understanding these divisions exposes where margin pools concentrate and which integration paths dominate customer purchasing decisions.
Solution Offering:
Replacement cycles vary dramatically across this category, with silicon-based solutions locking customers into multi-year hardware commitments while software layers refresh on quarterly release schedules.
- Hardware Security Modules:Tamper-resistant silicon enclosures with immutable root-of-trust properties anchor critical infrastructure deployments. Demand concentrates in Germany's automotive corridor where KBA regulations mandate physical tamper evidence for connected vehicle platforms.
- Secure Element:Dedicated cryptographic microcontrollers operating within sub-watt power budgets protect device identity and key storage. Smart manufacturing adoption in Stuttgart and Munich drives premium volumes as machinery OEMs enforce hardware-rooted trust anchors.
- Software Cryptography:Algorithm libraries executing on general-purpose processors enable flexible security updates without hardware replacement.
- Trusted Execution Environment:Isolated processing zones within SoC architectures protect sensitive operations from compromised host systems.
- Biometric Authentication:Fingerprint and facial recognition modules integrating liveness detection for high-assurance device access.
Hardware Security Modules anchor the volume base while Software Cryptography gains share at the steepest rate.
Deployment Type:
Cost structures stratify sharply here, with cloud orchestration subscriptions undercutting capital-intensive on-premises hardware while edge deployments capture latency-sensitive premiums.
- Edge Computing Security:Distributed cryptographic processing at network peripheries minimizes latency for real-time industrial control. Smart manufacturing lines in Bavaria and Baden-Württemberg prioritize these deployments to meet EU AI Act response-time requirements.
- Cloud-Based Security:Centralized policy orchestration and fleet-wide key management delivered through subscription models. Energy utilities across Texas and California adopt these solutions to simplify compliance with FERC cybersecurity directives.
- On-Premises Protection:Air-gapped security infrastructure for facilities with sovereign data residency mandates.
- Hybrid Integration:Split architectures combining local cryptographic operations with cloud-based policy management.
- Network-Level Security:Perimeter-focused protection for legacy OT environments lacking endpoint upgrade paths.
Cloud-Based Security dominates new procurement while Edge Computing Security expands most quickly in regulated industrial verticals.
Use Case:
Application maturity separates established compliance-driven functions from emerging threat-response capabilities still seeking standardization.
- Device Authentication:Cryptographic identity verification at boot and runtime prevents unauthorized network participation. Connected transportation platforms in Detroit and Wolfsburg require mutual authentication protocols meeting ISO/IEC 27400 baselines.
- Firmware Protection:Signed code verification and secure update pipelines defend against persistent compromise. EU Cyber Resilience Act mandates are accelerating procurement across consumer electronics supply chains.
- Data Encryption:AES-256 pipelines protecting data at rest and in transit across distributed sensor networks.
- Access Control:Policy enforcement restricting physical and logical device interactions to authorized entities.
- Intrusion Detection:Behavioral monitoring and anomaly flagging for zero-day threat identification.
Device Authentication represents the largest installed base while Firmware Protection climbs the fastest under regulatory pressure.
End User Industry:
Customer concentration patterns reveal how sector-specific certification requirements and production scales reshape vendor go-to-market economics.
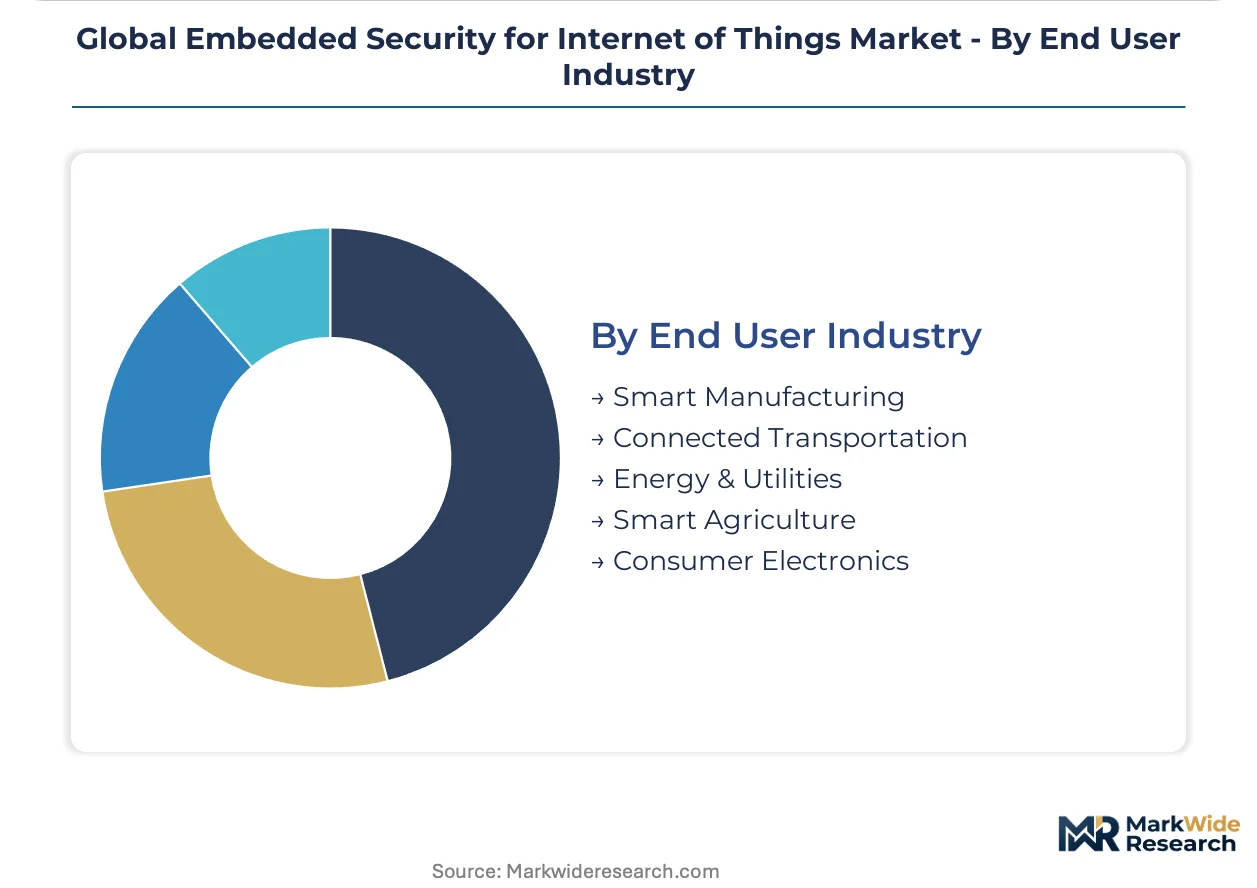
- Smart Manufacturing:Industrial IoT deployments integrating PLCs, robotics, and predictive maintenance sensors with unified security architectures. Germany's Industrie 4.0 initiatives in Saxony and North Rhine-Westphalia mandate Common Criteria EAL4+ certification for production line components.
- Connected Transportation:Vehicle-to-everything communication platforms requiring hardware security modules for over-the-air update integrity. Automotive OEMs in Stuttgart and Munich specify secure elements at seven-figure annual volumes.
- Energy & Utilities:Grid infrastructure protection spanning generation, transmission, and distribution systems.
- Consumer Electronics:Mass-market devices with cost-optimized secure elements and biometric integration.
- Smart Agriculture:Distributed sensor networks for precision farming with intermittent connectivity and battery constraints.
Smart Manufacturing anchors the volume base while Connected Transportation gains share at the steepest rate under OEM mandate acceleration.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Germany consumes embedded security solutions through automotive and machinery OEM mandates, while the United States prioritizes cloud-orchestrated fleet management and India builds domestic packaging capacity under electronics manufacturing incentives.
United States
FERC cybersecurity directives for energy utilities and FDA guidance on connected medical devices drive procurement concentration. NIST frameworks shape baseline requirements for cross-border procurement eligibility. Silicon Valley and Austin clusters host cloud-native security orchestration development for distributed device fleets.
Germany
KBA regulations mandate hardware-rooted trust anchors for connected vehicle platforms, pulling secure element volumes into seven-figure annual commitments. EU Cyber Resilience Act imposes mandatory vulnerability disclosure timelines on device manufacturers. Stuttgart and Munich machinery OEMs enforce Common Criteria EAL4+ certification for production line components.
China
MIIT standards for IoT security and dual carbon goals accelerate domestic semiconductor security integration. SAMR certification requirements compress product launch timelines for connected device manufacturers. Yangtze River Delta foundries expand tamper-resistant security chip capacity for industrial automation exports.
India
PLI scheme incentives for electronics manufacturing draw secure element packaging and test capacity from traditional East Asian hubs. BIS standards harmonize with ISO/IEC 27400 for cross-border procurement eligibility. Karnataka and Tamil Nadu industrial corridors host captive manufacturing scale for automotive embedded systems.
Japan
METI industrial security guidelines and JIS standards for connected devices shape procurement specifications for precision manufacturing. PMDA oversight of connected medical devices creates dedicated certification pathways. Kanto and Chubu regions concentrate semiconductor-level security integration for robotics and automotive tier-1 suppliers.
Global Embedded Security for Internet of Things Market Key Industry Players
Capability concentration sits with semiconductor architecture specialists; scale advantage sits with systems integrators and captive software subsidiaries of industrial conglomerates. The vendor base organizes around three strategic archetypes: silicon-level trust anchor providers, cloud-native security orchestration platforms, and industrial automation specialists with deep OT integration expertise. Dominant competitive moves include strategic partnerships between chip architects and device foundries, plus geographic expansion of secure element packaging capacity under sovereign manufacturing incentives.
Among semiconductor architecture specialists, Arm exemplifies the silicon-level trust anchor archetype through its TrustZone architecture penetration across European device foundries. Bosch Global Software Technologies occupies a position within the industrial automation specialist tier, leveraging captive manufacturing scale and automotive embedded systems heritage. Infosys sits within the systems integrator category, representing the scale-driven approach to cloud-native security orchestration for distributed device fleets.
| Leading Market Players |
|---|
| Xage Security |
| Telit |
| Arm |
| Capgemini Engineering |
| Infosys |
| Claroty |
| Sierra Wireless |
| Bosch Global Software Technologies |
| Armis |
| Others |
Cost & Logistics Intelligence
The Yangtze River Delta shipping corridor carries secure element substrates from Shanghai foundries to Stuttgart assembly plants at freight rates that compress margin structures for mid-volume device manufacturers while amplifying pricing power for automotive OEMs with captive logistics contracts.
Pricing Analysis
Long-term offtake contracts dominate procurement between automotive OEMs and secure element suppliers, locking in volume commitments that insulate premium tiers from spot-market volatility. Pricing stratifies across Common Criteria EAL4+ certified modules, uncertified commercial-grade alternatives, and royalty-based software cryptography licenses. Cost compression in the commercial-grade tier intensifies because Indian packaging facilities undercut Taiwanese labor rates. Automotive OEMs with seven-figure annual commitments exhibit the lowest price sensitivity; consumer electronics manufacturers purchasing sub-thousand-unit lots face the highest.
Supply Chain Analysis
Extended payment terms from German automotive OEMs to their Tier 1 suppliers cascade upstream, straining working capital for secure element packagers in Taiwan and South Korea. Raw silicon feedstock draws from Arizona polysilicon refineries, Japanese wafer manufacturers, and Belgian photoresist chemical suppliers. Single-source vulnerability concentrates in EUV lithography equipment anchored at ASML's Dutch headquarters. Distribution runs through authorized distributor networks serving industrial automation clusters in Bavaria and Baden-Württemberg.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Shortage of firmware signing infrastructure engineers constrains how quickly device manufacturers can satisfy EU Cyber Resilience Act update obligations, creating asymmetric advantage for vendors with pre-built hardware security module orchestration platforms.
For Market Incumbents: Pre-empt margin erosion from Indian packaging competitors by qualifying halogen-free laminate substrates ahead of REACH compliance deadlines. Capture Common Criteria evaluation lab capacity through multi-year retainers before backlog extends certification cycles further. Threat substitution from PUF-based secure boot architectures demands accelerated R&D in physically unclonable function integration. For New Entrants and Emerging Players: India's Karnataka industrial corridor offers the most penetrable geography for secure element test and packaging capacity, with PLI scheme subsidies offsetting capital equipment costs. Target medical device manufacturers facing FDA-EMA dual filing urgency with ISO/IEC 27400-certified security stacks delivered through compliance-documentation bundling. Go-to-market leverage rests on partnerships with German machinery OEMs seeking second-source alternatives to captive software subsidiaries. For Investors and Strategic Acquirers: Cloud-native security orchestration platforms with existing FERC-compliant utility customer bases represent the priority acquisition archetype for long-term infrastructure software consolidation. Monitor NIST post-quantum cryptography standard adoption rates as the inflection signal for upgrade cycle timing in critical infrastructure deployments. Macro deviation in sovereign manufacturing incentive structures would prompt forecast revision.| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Cryptography Migration | NIST lattice-based standards trigger replacement cycles for AES-256 modules in energy utilities. |
| Secure Element Packaging Expansion | PLI scheme subsidies in Tamil Nadu draw test capacity from traditional East Asian hubs. |
| Firmware Lifecycle Platform Integration | German automotive OEMs consolidate vendor relationships around unified update infrastructure subscriptions. |
| REACH Compliance Material Transition | Halogen-free laminate qualification ahead of deadlines captures medical device procurement channels. |
| Common Criteria Evaluation Lab Retainer | Multi-year capacity commitments compress certification timelines for regulated industrial verticals. |
Research Approach
Two parallel data streams informed the analysis: structured primary interviews with semiconductor architecture specialists, automotive embedded systems engineers, and industrial IoT procurement officers; and secondary validation against SEC filings from secure element manufacturers, EU Cyber Resilience Act regulatory texts, and NIST cybersecurity framework documentation. Bottom-up triangulation across device shipment estimates and top-down reconciliation against OEM security spending disclosures anchored volume projections.
Forecast inputs span hardware security module versus software cryptography solution splits, edge computing versus cloud-based deployment type trajectories, and smart manufacturing versus connected transportation end-use intensity. Segmentation dimensions modeled include solution offering tier, deployment architecture, use case maturity, and end-user industry regulatory exposure. CAGRs derive from regression analysis of historical certification timeline compression and OEM mandate acceleration patterns.
Practitioners should monitor EU AI Act enforcement intensity, Taiwan Strait logistics disruption indicators, and NIST post-quantum standard finalization for early signals of trajectory revision. Macroeconomic contraction in German automotive production, regulatory delay in Cyber Resilience Act implementation, or breakthrough in quantum computing timeline would prompt forecast reassessment.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Internet of Things (IoT)
Cellular M2M Market
Internet of Things (IoT)
Non-Terrestrial IoT Gateway Hardware and Software Market
Internet of Things (IoT)
IoT Data Governance Market
Internet of Things (IoT)
IoT Middleware Market
Internet of Things (IoT)
Intelligent IoT Market
Internet of Things (IoT)
North America IoT Software Market
Internet of Things (IoT)
Internet of Things (IoT) in Manufacturing Market
Internet of Things (IoT)
Narrowband IoT Enterprise Application Market
Internet of Things (IoT)
Global IoT in Aerospace and Defense Market
Internet of Things (IoT)
North America IoT Device Market
Internet of Things (IoT)
IIOT Gateway for Utility Market
Internet of Things (IoT)
Mobile-Connecting Smart Objects Market
Internet of Things (IoT)
Global Machine-To-Machine (M2M) Connections Market
Internet of Things (IoT)
Global IoT in Automobile Market
Internet of Things (IoT)
Internet of Things (IoT) in Utilities Market
Internet of Things (IoT)
IoT Gateway Hardware and Software Market