
 GDPR Assessment Tools Market | 2026-2036
GDPR Assessment Tools Market Size, Share, and Industry Trends Forecast 2026-2036
GDPR Assessment Tools Market Analysis
The EU AI Act is restructuring compliance economics for data processors across Europe. OneTrust leverages its integrated privacy-to-AI governance stack to anchor enterprise accounts in regulated sectors. IBM Corporation competes through embedded Watson discovery modules that map data lineage across hybrid cloud estates. BigID specializes in sensitive data intelligence, extending its scanner architecture to cover generative AI training datasets.
GDPR assessment tools comprise software platforms that automate data protection impact assessments, map personal data flows, score regulatory risk exposure, and generate audit-ready documentation for supervisory authority review. These systems typically integrate with SIEM, DLP, and identity management infrastructure to maintain continuous compliance posture. Cloud-based deployment leads the market as organizations prioritize scalable infrastructure without capital-intensive on-premise buildouts. Large enterprises represent the deepest margin pool given their complex multi-jurisdictional data architectures and dedicated privacy office staffing. Risk management solutions within the product type category show the fastest trajectory as breach notification obligations and cross-border transfer mechanisms intensify vendor scrutiny.
France's CNIL, Ireland's Data Protection Commission, and Germany's BfDI shape market access through divergent enforcement priorities and fining methodologies that force vendors into jurisdictional customization. The EDPB's binding decisions on international data flows further fragment product requirements across member states. Stakeholders must monitor how emerging AI-specific obligations layer onto existing GDPR accountability frameworks without duplicating tooling investments.
Market Dynamics
The EU AI Act is layering algorithmic accountability requirements atop existing GDPR frameworks, forcing assessment platforms to absorb new data governance protocols without fragmenting compliance workflows. Vendors must now architect unified privacy-AI governance stacks that satisfy overlapping supervisory mandates.
Growth Catalysts
- EU AI Act data governance obligations:Financial services firms in Germany, France, and the United Kingdom are expanding platform procurement to cover training dataset documentation and bias auditing requirements.
- Active enforcement regimes:France's CNIL, Ireland's Data Protection Commission, and Germany's BfDI maintain divergent fining methodologies that create sustained demand for jurisdictional customization capabilities.
- Hybrid cloud data architectures:Large enterprises operating multi-jurisdictional estates require continuous compliance posture monitoring across distributed SIEM, DLP, and identity management infrastructure.
Market Restraints
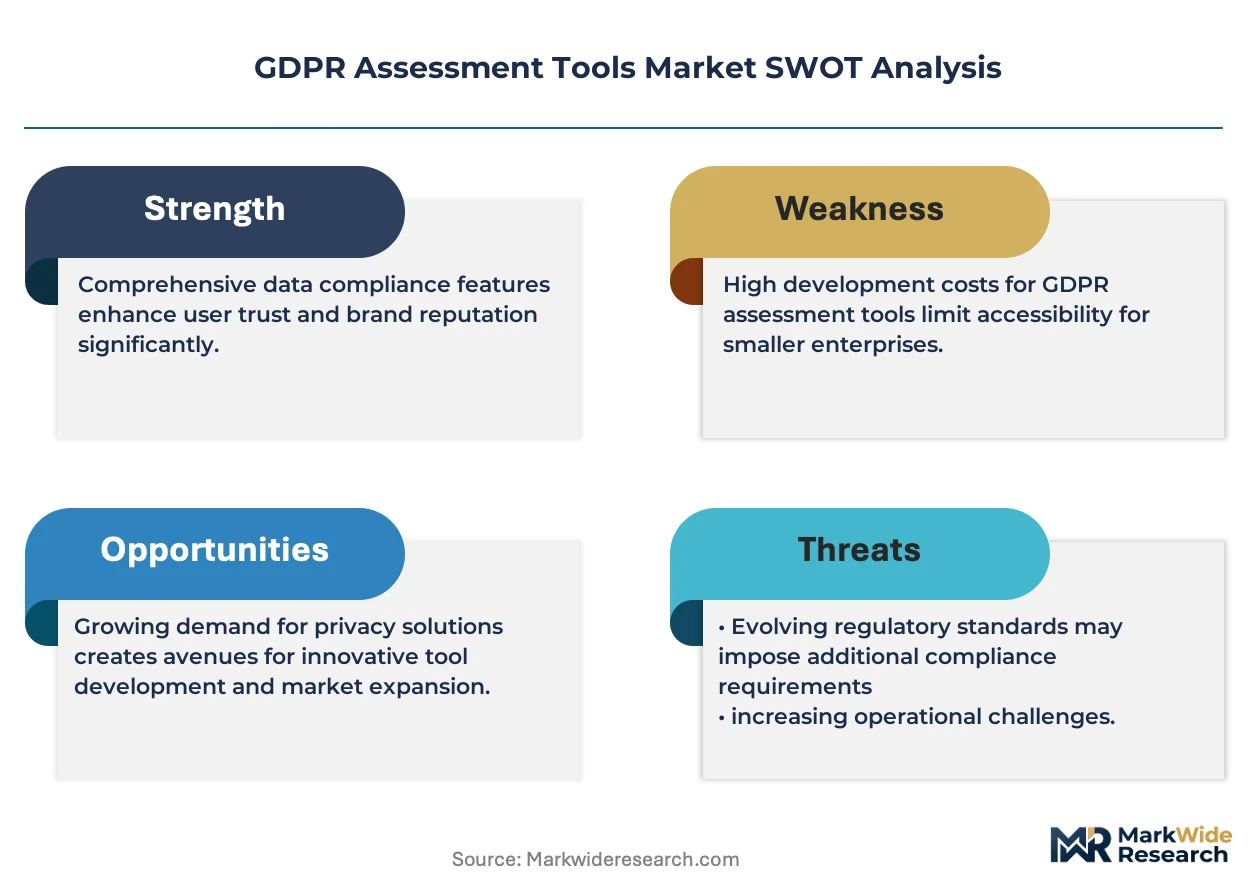
- Jurisdictional fragmentation:The EDPB's binding decisions on international data flows force vendors into product requirement customizations that inflate development overhead without proportional revenue capture.
- Technical integration complexity:Legacy on-premise compliance systems resist API-native connectivity, constraining cloud-first deployment timelines for established enterprises.
- Substitution by in-house legal tech:Well-capitalized multinational banks and insurers are building captive assessment modules through internal privacy office staffing rather than vendor procurement.
Strategic Opportunities
- Generative AI training dataset coverage:Assessment platforms can extend scanner architectures to map sensitive data flows into foundation model development pipelines.
- Underpenetrated mid-market segment:Small and medium enterprises in Spain, Italy, and Poland lack dedicated privacy offices and represent greenfield demand for automated documentation generation.
- Convergence with ESG reporting infrastructure:The CSRD's data quality requirements create cross-selling pathways into sustainability disclosure platforms.
Industry Challenges
- Cross-functional talent scarcity:Vendors struggle to hire engineers with simultaneous expertise in privacy law, cloud architecture, and machine learning operations.
- Certification timeline compression:ISO 27701 and SOC 2 Type II attestations require 6-12 month audit cycles that delay enterprise sales cycles.
- Legacy system integration friction:Mainframe-resident personal data repositories in banking and insurance resist automated lineage mapping without expensive middleware layers.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | GDPR Assessment Tools Market |
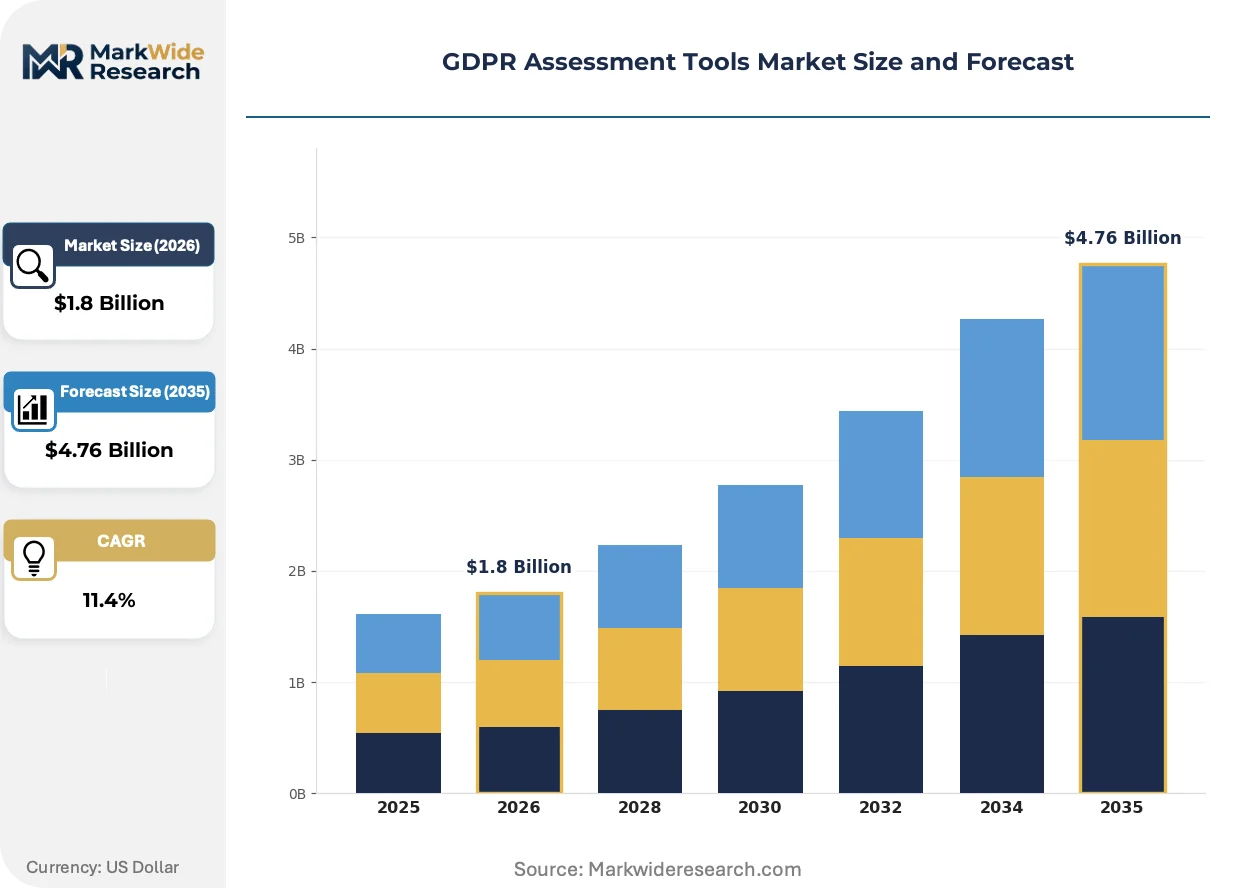
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $4.76 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Assessment Platforms, Compliance Software, Data Mapping Tools, Risk Management Solutions End User: Small Enterprises, Medium Enterprises, Large Enterprises, Government Entities Deployment: Cloud-Based, On-Premise, Virtual Private Cloud, Hybrid Industry Vertical: Financial Services, Healthcare, Retail, Technology |
| Companies Covered | OneTrust, IBM Corporation, Microsoft Corporation, TrustArc, BigID, Securiti.ai, Commvault Systems Inc., Mimecast Services Limited, Softcat Plc, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
GDPR Assessment Tools Market Emerging Trajectories
Assessment platforms are absorbing adjacent compliance functions as regulatory boundaries blur between privacy, AI governance, and cybersecurity mandates. Vendors that architect unified control planes capture disproportionate enterprise expansion revenue.
Automated data lineage mapping is unifying privacy impact assessments with AI model documentation workflows. Cloud-native financial services firms in the Netherlands and Sweden are deploying these integrated stacks within 90-day implementation windows. This convergence compresses vendor consolidation timelines by eliminating redundant tooling procurement cycles.
The EU AI Act's risk classification system for algorithmic applications is mandating documentation standards that overlap with existing GDPR Article 35 data protection impact assessments. High-risk AI deployers in healthcare diagnostics and credit scoring must now maintain unified audit trails spanning both regulatory frameworks. German automotive suppliers and French healthcare technology providers are piloting combined assessment modules to avoid duplicate compliance investments.
Enterprise procurement of assessment capabilities is consolidating through managed security service providers rather than direct software licensing. Mid-market organizations in Belgium and Austria prefer subscription bundles that embed assessment tooling within broader cybersecurity service contracts. This channel shift compresses standalone vendor margins while expanding total addressable market penetration through distributor economies of scale.
GDPR Assessment Tools Market Segmentation
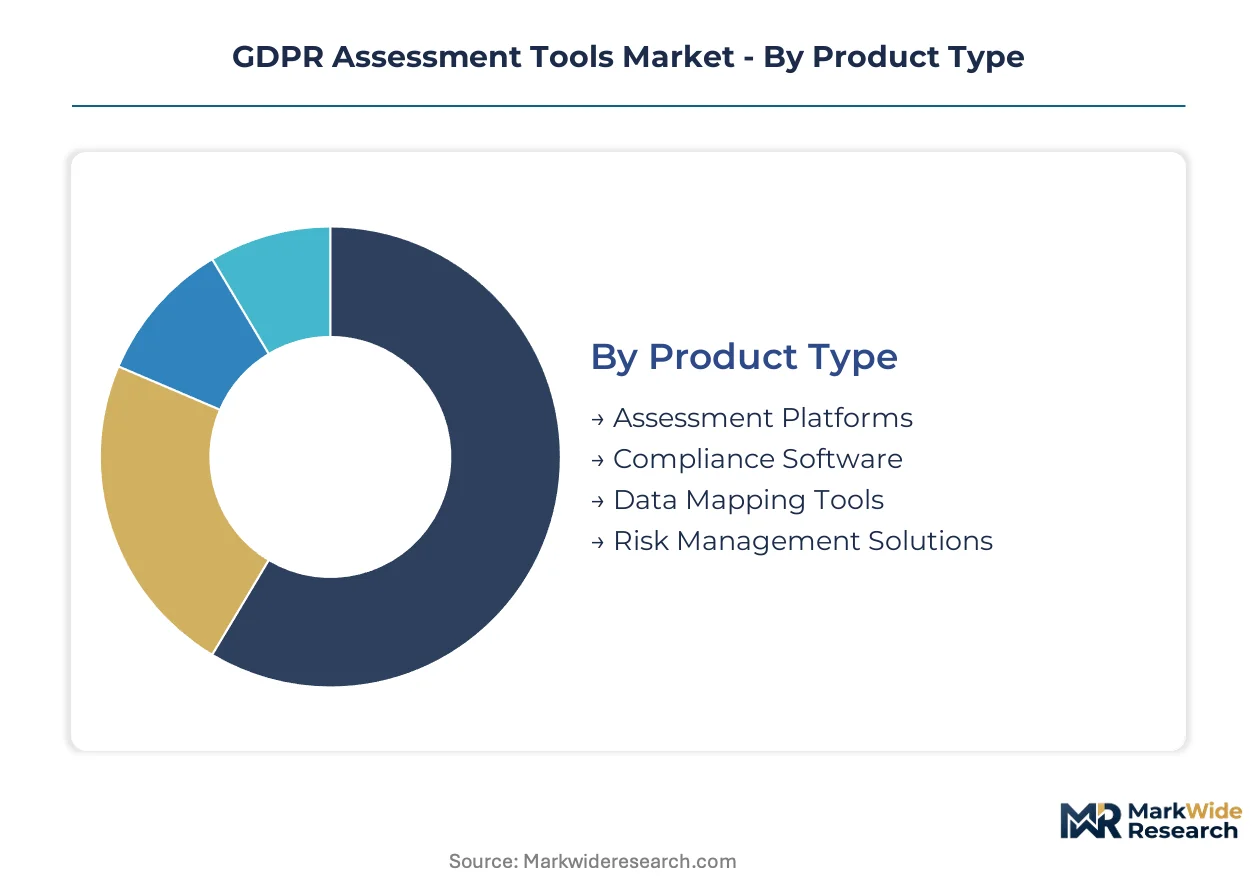
GDPR assessment tools fragment across four distinct dimensions that determine procurement economics. Product architecture, customer scale, infrastructure preference, and sector-specific risk exposure each reshape vendor pricing power and implementation complexity.
Product Type:
Risk Management Solutions command premium pricing while Assessment Platforms dominate unit volume across European deployments.
- Risk Management Solutions:Automated scoring engines quantify regulatory exposure across data processing activities and cross-border transfer mechanisms. Financial services procurement in Germany and France concentrates here as supervisory authority scrutiny intensifies on breach notification workflows.
- Assessment Platforms:Modular architectures host data protection impact assessments, vendor due diligence questionnaires, and audit documentation in unified control planes. Large enterprises with dedicated privacy offices in the United Kingdom favor these for multi-jurisdictional coverage.
- Compliance Software:Workflow engines automate policy distribution, training attestation, and incident response ticketing.
- Data Mapping Tools:Scanner architectures discover personal data repositories across cloud and on-premise estates.
Mature deployment sits with Assessment Platforms. Newer deployment is concentrated in Risk Management Solutions.
End User:
Enterprise scale determines feature depth requirements and sales cycle duration across the customer base.
- Large Enterprises:Complex multi-jurisdictional data architectures demand continuous compliance posture monitoring with dedicated privacy office staffing. German automotive suppliers and French healthcare technology providers represent the deepest margin pool given their hybrid cloud estates and AI Act overlay requirements.
- Medium Enterprises:Organizations with 250-999 employees lack dedicated privacy offices but face identical supervisory authority scrutiny. Spain, Italy, and Poland show greenfield demand for automated documentation generation without internal legal tech buildouts.
- Small Enterprises:Subscription bundles through managed security service providers dominate procurement.
- Government Entities:Public sector procurement follows distinct tendering timelines with certification prerequisites.
Revenue concentration aligns with Large Enterprises. Fastest expansion is occurring in Medium Enterprises.
Deployment:
Infrastructure preference splits between capital efficiency priorities and data residency constraints.
- Cloud-Based:Scalable infrastructure without capital-intensive buildouts leads procurement preference among Netherlands and Sweden financial services firms. Ninety-day implementation windows are standard for cloud-native organizations.
- Hybrid:Distributed architectures maintain sensitive data on-premise while leveraging cloud analytics for risk scoring. German automotive suppliers pilot these configurations to satisfy BfDI data localization expectations without sacrificing operational agility.
- On-Premise:Legacy mainframe-resident personal data in banking and insurance resists automated lineage mapping.
- Virtual Private Cloud:Isolated tenant environments address multi-tenant security concerns in healthcare and government.
Established procurement favors On-Premise. Cloud-Based deployment is gaining share fastest among new implementations.
Industry Vertical:
Sector-specific regulatory density reshapes feature requirements and pricing tolerance.
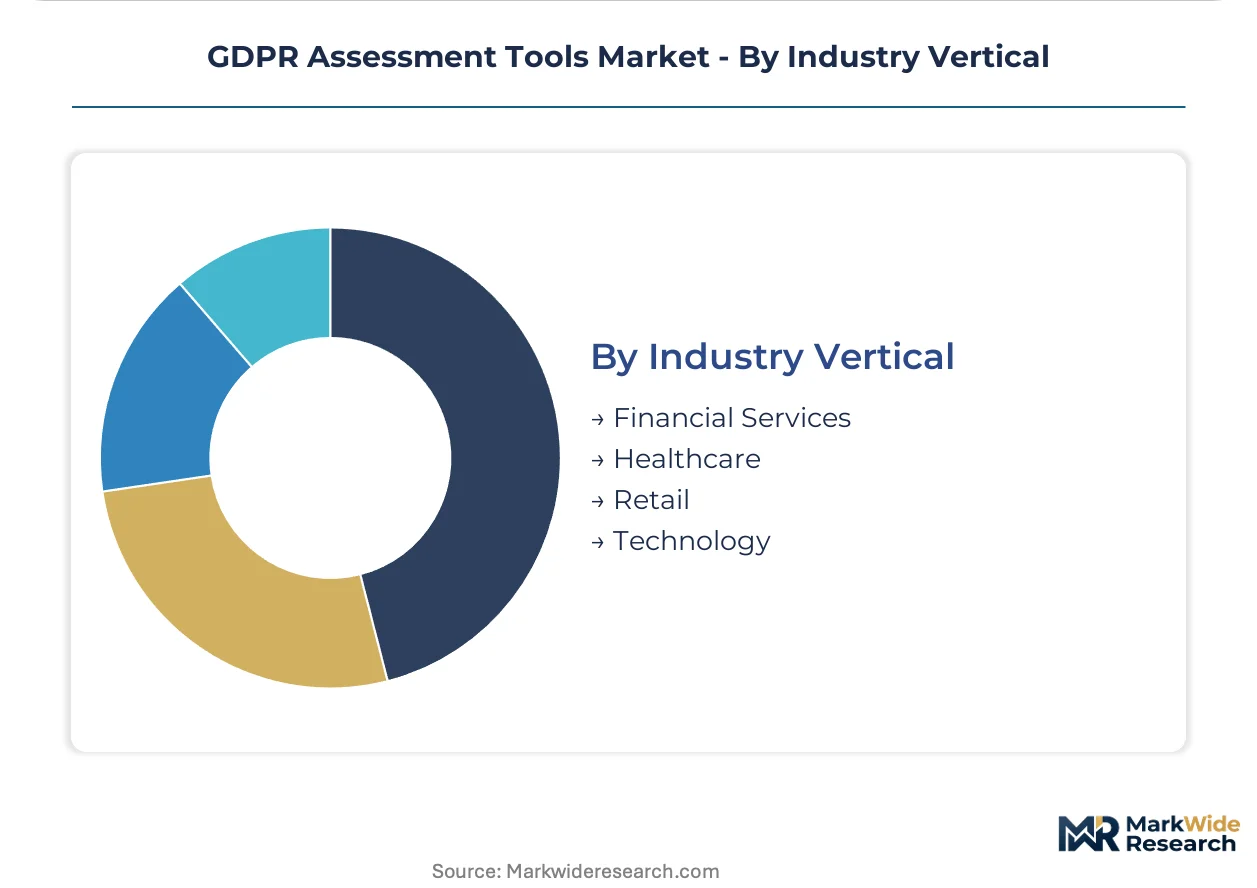
- Financial Services:Credit scoring algorithms trigger EU AI Act high-risk classification alongside existing GDPR obligations. Procurement concentrates in Germany, France, and the United Kingdom where supervisory authorities maintain active enforcement regimes.
- Healthcare:Diagnostics applications face overlapping EMA device regulations and GDPR health data protections. French healthcare technology providers pilot combined assessment modules to unify audit trails.
- Retail:Cross-border e-commerce data flows drive demand for transfer mechanism documentation.
- Technology:Generative AI training dataset governance is emerging as a specialized procurement trigger.
Deep incumbent penetration exists in Financial Services. Healthcare represents the steepest expansion trajectory as AI Act implementation accelerates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Enterprise zones in Frankfurt and Dublin concentrate data center investment, drawing assessment tool procurement toward regulatory hubs with established supervisory authority presence.
Germany
Automotive suppliers in Baden-Württemberg and financial institutions in Frankfurt drive demand for hybrid cloud compliance architectures. The BfDI maintains strict data localization expectations that favor on-premise sensitive data handling. Munich-based healthcare technology providers pilot combined GDPR-EU AI Act assessment modules to unify audit documentation.
France
Credit scoring algorithms in Parisian fintech clusters trigger high-risk AI classification alongside existing data protection obligations. The CNIL enforces divergent fining methodologies that necessitate jurisdictional customization capabilities. Lyon healthcare diagnostics firms require unified control planes spanning EMA device regulations and GDPR health data protections.
United Kingdom
London financial services firms with multi-jurisdictional estates demand continuous compliance posture monitoring across distributed infrastructure. The Information Commissioner's Office maintains active enforcement on breach notification workflows. Edinburgh and Manchester technology clusters show preference for cloud-native ninety-day implementation windows.
Ireland
Dublin's data center concentration hosts European headquarters for technology multinationals with complex cross-border transfer mechanisms. The Data Protection Commission shapes market access through binding decisions on international data flows. Cork and Galway mid-market enterprises lack dedicated privacy offices and represent greenfield demand for automated documentation generation.
Netherlands
Amsterdam financial services firms prioritize scalable cloud infrastructure without capital-intensive buildouts. The Dutch Data Protection Authority aligns with EDPB frameworks while maintaining sector-specific guidance for payment processors. Rotterdam logistics technology providers seek assessment platforms integrating with SIEM and DLP infrastructure for continuous monitoring.
GDPR Assessment Tools Market Vendor Landscape
United States-based vendors anchor the integrated platform tier; European specialists hold jurisdiction-specific customization positions. The vendor base splits between consolidated full-stack providers and fragmented point-solution developers. Three strategic archetypes dominate: privacy-to-AI governance integrators, sensitive data intelligence specialists, and managed security service bundlers. M&A activity concentrates on scanner architecture acquisitions, while geographic expansion targets underpenetrated mid-market segments in Southern and Eastern Europe.
Within the integrated governance tier, OneTrust and IBM Corporation exemplify full-stack positioning that absorbs adjacent compliance functions. BigID occupies a specialist position in sensitive data intelligence, representing scanner architecture vendors extending coverage toward generative AI training datasets. These three anchors demonstrate how competitive positioning stratifies between unified control plane breadth and deep technical specialization in automated lineage mapping.
| Leading Market Players |
|---|
| OneTrust |
| IBM Corporation |
| Microsoft Corporation |
| TrustArc |
| BigID |
| Securiti.ai |
| Commvault Systems Inc. |
| Mimecast Services Limited |
| Softcat Plc |
| Others |
Supply Flow & Price Mechanics
Cloud-native deployment architectures are compressing implementation timelines from twelve months to ninety days, simultaneously reducing vendor delivery costs and concentrating procurement power among hyperscaler-aligned distributors in Germany, France, and the Netherlands.
Pricing Analysis
Short lead-time premiums command 15-25% markups over standard deployment schedules, while spot inventory of pre-configured assessment modules trades at discounts in the mid-market channel. SaaS-tiered subscription models dominate enterprise procurement, with price differentiation anchored in ISO 27701 certification tier and jurisdictional customization depth. Cost compression in the mid-market tier is intensifying because managed security service providers bundle assessment tooling at compressed margins. Small enterprises exhibit highest price sensitivity, while large financial services firms in Frankfurt and London tolerate premium pricing for hybrid cloud architectures with dedicated implementation support.
Supply Chain Analysis
Engineering talent scarcity in Ireland, Poland, and Portugal constrains platform development velocity and inflates personnel costs across vendor R&D centers. Software development draws from cloud infrastructure services, open-source compliance libraries, and specialized data lineage mapping engines. Single-source vulnerability sits with hyperscaler compute dependencies, as AWS, Azure, and GCP outages cascade into assessment platform downtime. Distribution runs through managed security service providers and systems integrators rather than direct licensing, compressing standalone vendor margins while expanding market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Supply constraints in cross-functional engineering talent prop pricing power for vendors with established privacy-AI governance expertise, insulating premium tiers from mid-market commoditization pressure.
For Market Incumbents: Hedge against in-house legal tech substitution by embedding assessment modules within broader cybersecurity platform ecosystems. Acquire scanner architecture specialists to extend coverage into generative AI training dataset governance. Prioritize certification investment in ISO 27701 and SOC 2 Type II to maintain enterprise procurement eligibility against emerging cloud-native entrants. For New Entrants and Emerging Players: The EU AI Act in Germany and France opens a window for specialized assessment modules targeting high-risk algorithmic classification workflows. Target mid-market enterprises in Spain, Italy, and Poland lacking dedicated privacy offices with automated documentation generation at subscription price points below incumbent tiers. Pursue channel partnerships with regional managed security service providers to bypass direct enterprise sales cycle barriers. For Investors and Strategic Acquirers: Exit pathways concentrate in strategic acquisitions by hyperscalers and private equity roll-ups of fragmented point-solution vendors. Long-term viability hinges on unified privacy-AI governance stack breadth rather than standalone data mapping specialization. Monitor EDPB binding decisions on international data flows as inflection indicators for jurisdictional customization capability valuation premiums.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies GDPR assessment workflows with EU AI Act documentation requirements for German automotive suppliers. |
| Acquisition of Specialist Firm | Absorbs scanner architecture capabilities to map sensitive data flows into foundation model training pipelines. |
| Strategic Partnership | Embeds assessment tooling within managed security service provider bundles for Belgian and Austrian mid-market penetration. |
| Geographic Expansion | Establishes delivery presence in Warsaw and Madrid to capture greenfield demand from privacy-office-deficient enterprises. |
| Product Launch | Introduces combined GDPR-EU AI Act assessment modules for French healthcare diagnostics firms facing overlapping EMA obligations. |
Methodological Framework
Document review covered EDPB binding decisions, CNIL enforcement bulletins, and BfDI technical guidance documents, complemented by interviews with data protection officers, privacy technology procurement leads, and cloud architecture specialists. Secondary validation drew from SEC filings of listed vendors, hyperscaler partnership announcements, and ISO certification registries. Bottom-up sizing of deployment volumes across Germany, France, the United Kingdom, Ireland, and the Netherlands was cross-referenced against top-down market value estimates from supervisory authority fine revenue and vendor disclosed contract values.
Historical growth trajectories were cross-referenced against panel input from industry stakeholders to anchor projection assumptions across the analysis window. Segmentation modeling incorporated product architecture, enterprise scale tier, deployment infrastructure preference, and sector-specific regulatory density. CAGRs were derived from regression analysis of vendor revenue disclosures and procurement volume indicators. Forecast inputs included EU AI Act implementation timelines and supervisory authority staffing expansion plans.
Caveats apply where EDPB binding decisions on international data flows or divergent national enforcement methodologies could materially shift the outlook for jurisdictional customization requirements. Material deviation in AI Act secondary legislation timelines or hyperscaler partnership exclusivity terms warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Regulatory Compliance Technology
Management System Certification Market
Regulatory Compliance Technology
Compliance and Traceability Solutions Market
Regulatory Compliance Technology
Global Regulatory Technology (Regtech) Market
Regulatory Compliance Technology
Compliance Testing Solutions Market
Regulatory Compliance Technology
Regulatory Information Management System Market
Regulatory Compliance Technology
Regtech Software Market
Regulatory Compliance Technology
Anti-Money Laundering Systems Market
Regulatory Compliance Technology
Nordic Regulatory Affairs Market
Regulatory Compliance Technology
US Anti Money Laundering Solution Market
Regulatory Compliance Technology
General Data Protection Regulation (GDPR) Market
Regulatory Compliance Technology
Aviation Compliance Monitoring Software Market
Regulatory Compliance Technology
Regulatory Change Management Software Market
Regulatory Compliance Technology
Global AML Software Market
Regulatory Compliance Technology
Cross-Border Customs and Trade Compliance Orchestration Platforms Market
Regulatory Compliance Technology
United States Sales Tax Compliance Software Market
Regulatory Compliance Technology
Global GDPR Services Market