
 Digital Risk Management Market | 2026-2036
Digital Risk Management Market Size, Share, and Industry Trends Forecast 2026-2036
Digital Risk Management Market Outlook
North American cybersecurity vendor capacity is restructuring as cloud-native architecture investments reshape platform economics. Palo Alto Networks leverages integrated security stacks to dominate enterprise firewall-to-SOAR pipelines. Rapid7 anchors vulnerability management workflows through continuous attack surface monitoring. BlueVoyant specializes in managed detection and response, competing for mid-market accounts against legacy MSSP incumbents.
Digital risk management encompasses software solutions, services, and analytical frameworks that identify, quantify, and mitigate threats across cyber, operational, and third-party domains, typically employing real-time telemetry ingestion, probabilistic scoring models, and automated remediation orchestration. Its primary purpose is to protect revenue continuity, regulatory standing, and stakeholder trust in digitally dependent organizations. Software solutions lead segment value generation as enterprises prioritize autonomous threat detection over human-dependent consulting engagements. Cloud-based deployment is expanding fastest among financial institutions seeking elastic compute for stress-testing risk scenarios. Monitoring platforms occupy concentrated margin pools due to recurring subscription structures and high switching costs.
FDA cybersecurity guidance for connected medical devices, SEC disclosure rules for material cyber incidents, and EU NIS2 requirements for critical entities are reshaping procurement specifications and vendor qualification criteria across healthcare and financial end users. HIPAA enforcement actions in the United States and GDPR cross-border data governance in Europe further constrain architecture choices for multinational deployments. Stakeholders must evaluate whether their current vendor ecosystems satisfy emerging cross-jurisdictional attestation requirements before renewal cycles commit capital to incompatible platforms.
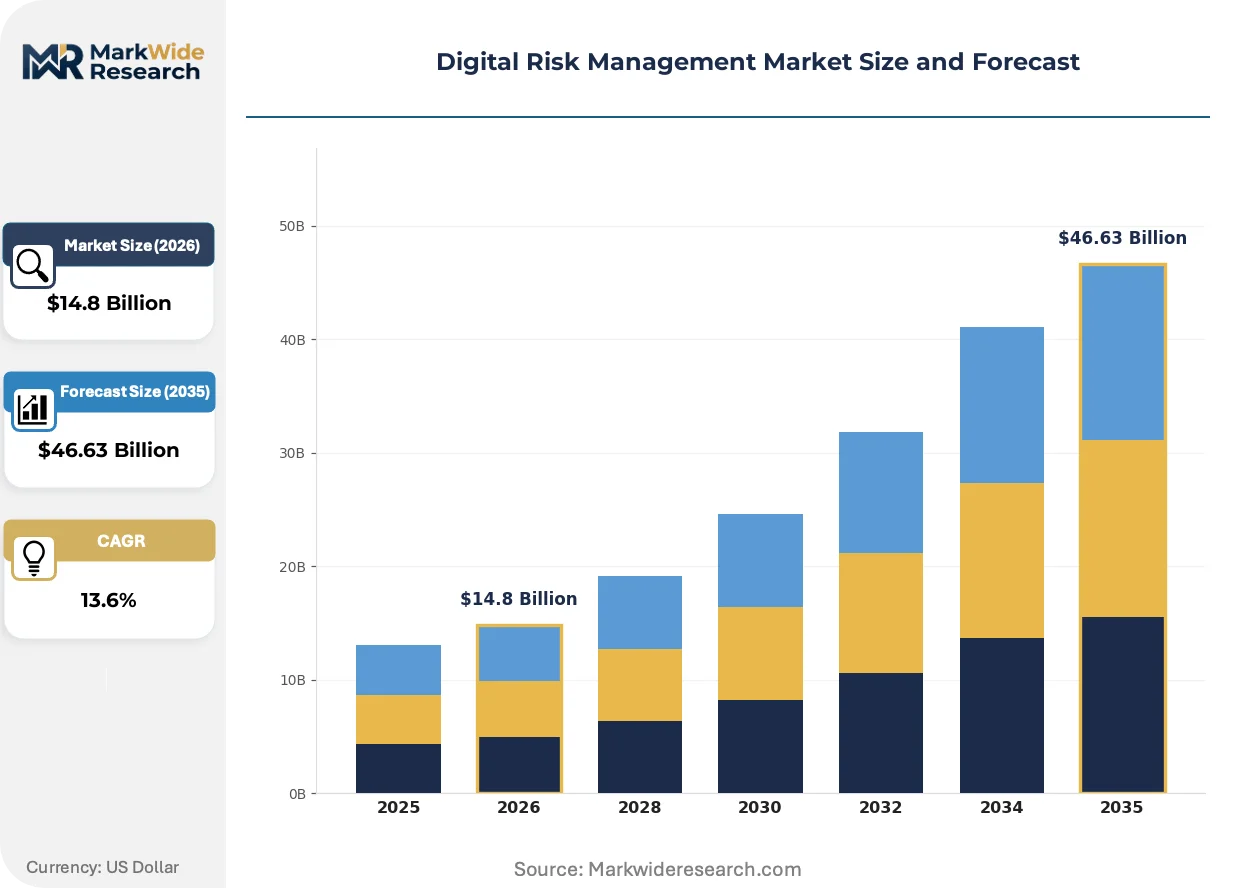
Market Dynamics
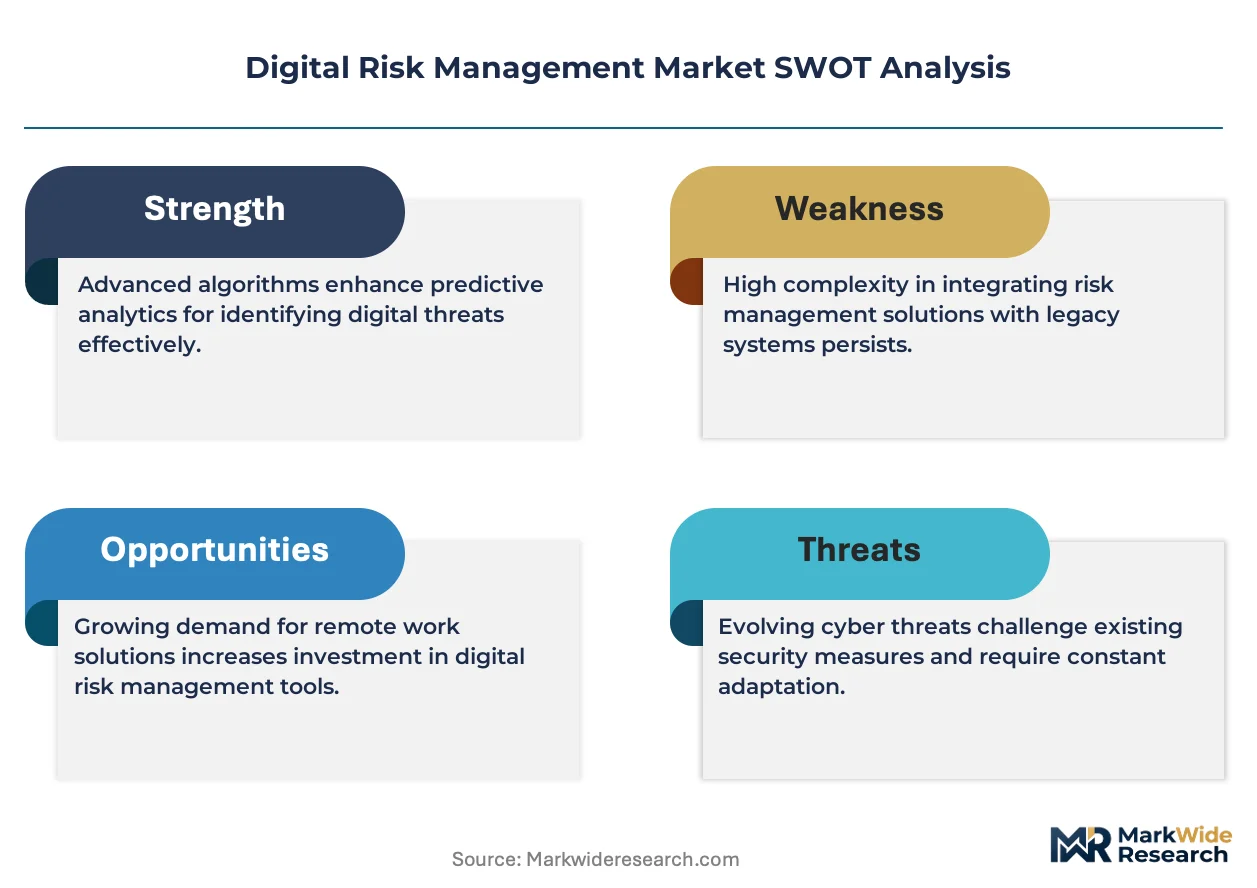
Cloud-native security architecture is compressing platform economics and forcing incumbent vendors to rebuild telemetry pipelines around elastic compute fabrics rather than on-premise appliance stacks.
Growth Catalysts
- EU NIS2 Directive:Critical infrastructure operators across energy, transport, and finance must deploy continuous monitoring capabilities by 2024 deadlines, mandating procurement of autonomous threat detection platforms.
- Attack surface expansion:Remote work architectures and IoT device proliferation multiply vulnerability vectors beyond traditional perimeter defenses, forcing enterprise security teams toward unified risk quantification tools.
- Ransomware economics:Criminal syndicates targeting US healthcare and municipal sectors have elevated cyber resilience to board-level priority, accelerating budget allocation toward integrated response orchestration.
Market Restraints
- Talent scarcity:Shortage of certified security architects and threat intelligence analysts inflates implementation costs and extends deployment timelines for complex SOAR integrations.
- Vendor consolidation risk:Dominance of Palo Alto Networks, CrowdStrike, and Microsoft in enterprise accounts creates interoperability friction for specialized point-solution vendors seeking channel access.
- False positive fatigue:Alert overload from poorly tuned detection engines erodes security team trust in automated platforms, driving churn toward managed detection and response services.
Strategic Opportunities
- India's digital public infrastructure:UPI expansion and health stack digitization create demand for sovereign cloud security frameworks compliant with RBI cybersecurity guidelines and CERT-In incident reporting mandates.
- Convergence of GRC and cyber:Unified platforms integrating governance, risk, and compliance workflows with real-time threat intelligence are displacing siloed point solutions in Fortune 500 procurement cycles.
- SEC disclosure rules:Material incident reporting requirements for US public companies create advisory services attach rates and sustained demand for forensic documentation capabilities.
Industry Challenges
- Legacy SIEM migration complexity:Decades of on-premise log aggregation infrastructure in financial services and government sectors resists cloud-native replacement due to data residency requirements and custom correlation rule dependencies.
- Cross-border data governance:GDPR adequacy decisions, China's data localization laws, and US CLOUD Act tensions fragment architecture choices for multinational enterprises seeking unified risk visibility.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Digital Risk Management Market |
| Market Size in 2026 | $14.8 Billion |
| Market Size in 2035 | $46.63 Billion |
| CAGR (2026 – 2036) | 13.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Software Solutions, Consulting Services, Risk Assessment Tools, Monitoring Platforms End User: Financial Institutions, Corporate Enterprises, Government Agencies, Healthcare Providers Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services Service Type: Training Services, Technical Support, Implementation Services, Auditing Services |
| Companies Covered | Appgate, BlueVoyant, Palo Alto Networks, Allgress, Everbridge, eSentire, Verizon, Unisys, Rapid7, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Digital Risk Management Market Strategic Shifts
Artificial intelligence is embedding into detection and response workflows, compressing mean-time-to-containment while forcing architectural decisions about model training data sovereignty and explainability requirements.
Extended detection and response platforms are converging with cloud security posture management to deliver unified visibility across endpoint, network, and infrastructure layers. Financial institutions in London, Singapore, and New York are piloting these converged stacks to eliminate telemetry gaps between siloed security operations centers. The structural consequence is consolidation of vendor relationships around integrated platforms rather than best-of-breed point solutions.
EU AI Act risk classification rules are mandating human oversight for high-risk AI systems used in critical infrastructure cybersecurity applications. Vendors must now document training data provenance and model performance metrics to satisfy conformity assessment requirements. Healthcare and energy operators in Germany, France, and the Netherlands are prioritizing vendors with established EU notified body certifications.
Security procurement is fragmenting as mid-market enterprises bypass traditional reseller channels to source directly from cloud marketplaces. AWS Marketplace and Azure Marketplace transactions for cloud-native security tools are displacing three-year enterprise license agreements in the 500-5,000 employee segment. This pattern is most pronounced among software-as-a-service companies in the US Pacific Northwest and Indian technology corridors.
Digital Risk Management Market Segmentation
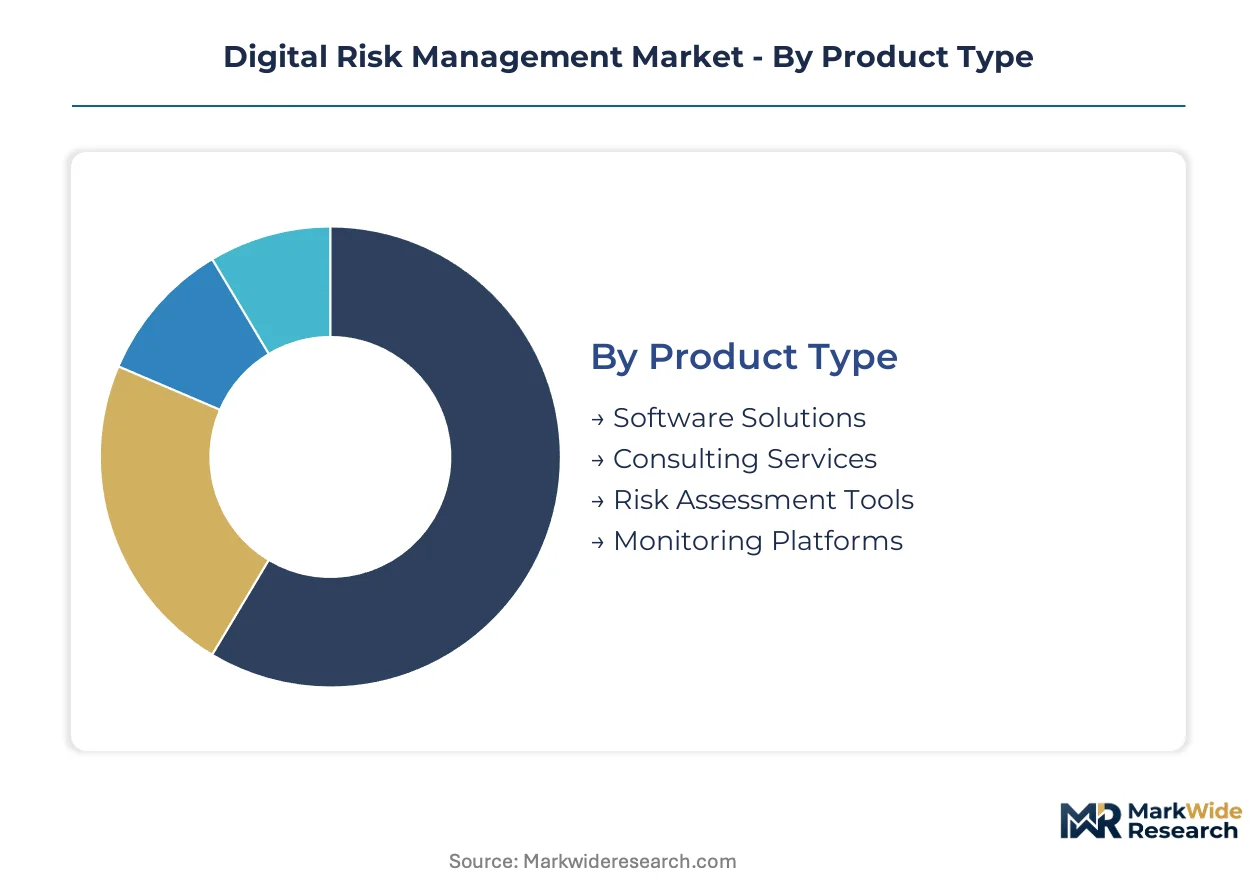
Segmentation in digital risk management reveals how procurement priorities diverge across compliance maturity, infrastructure legacy, and threat exposure profiles. Understanding these fault lines enables vendors to align platform architectures with buyer readiness and regulatory timelines.
Product Type:
EU AI Act conformity assessments and FDA cybersecurity guidance impose distinct certification burdens across product categories, with high-risk AI systems requiring notified body validation and connected medical device platforms demanding 510(k) documentation.
- Software Solutions:Autonomous threat detection engines with embedded probabilistic scoring models process real-time telemetry for automated remediation orchestration. Financial institutions in the United States prioritize these for SEC cybersecurity disclosure compliance, compressing procurement cycles for cloud-native architectures.
- Monitoring Platforms:Continuous attack surface visibility systems with recurring subscription structures and high switching costs capture concentrated margin pools. Healthcare providers facing HIPAA enforcement actions demand these for connected medical device oversight, particularly in hospital networks with dispersed IoT deployments.
- Consulting Services:Human-dependent advisory engagements for risk quantification and regulatory attestation.
- Risk Assessment Tools:Point solutions for vulnerability scoring and third-party risk scoring workflows.
Software Solutions sits at the top of the volume ranking, with Monitoring Platforms climbing the fastest.
End User:
Cost tier stratification separates enterprise-grade integrated stacks from mid-market managed services, with budget concentration determining whether buyers pursue autonomous platforms or outsourced detection and response.
- Financial Institutions:Banks, insurers, and capital markets firms deploying elastic compute for stress-testing risk scenarios and satisfying RBI cybersecurity guidelines in India alongside SEC rules in the United States. These buyers command premium pricing for sovereign cloud frameworks with cross-jurisdictional attestation capabilities.
- Corporate Enterprises:Mid-market and large enterprises across manufacturing, retail, and technology verticals. Procurement is fragmenting as 500-5,000 employee companies bypass resellers for AWS Marketplace and Azure Marketplace transactions, displacing three-year license agreements.
- Government Agencies:Federal, state, and municipal entities with data residency constraints and legacy SIEM migration complexity.
- Healthcare Providers:Hospital systems and clinic networks managing FDA cybersecurity guidance for connected devices and HIPAA enforcement exposure.
Financial Institutions captures the largest revenue share, while Corporate Enterprises expands most quickly through cloud marketplace channel shift.
Deployment:
Customer type segmentation maps to infrastructure maturity, with cloud-native adopters prioritizing elastic telemetry pipelines and regulated entities defending on-premise appliance investments.
- Cloud-Based:Elastic compute fabrics enabling real-time scenario modeling and autonomous threat containment. Financial institutions in London, Singapore, and New York pilot these for unified visibility across endpoint, network, and infrastructure layers, eliminating telemetry gaps between siloed security operations centers.
- Hybrid:Architectures blending on-premise log aggregation with cloud-native analytics for data sovereignty compliance. Germany, France, and Netherlands healthcare operators favor these for EU AI Act high-risk system oversight with human-in-the-loop requirements.
- On-Premises:Appliance-based stacks resisting migration due to custom correlation rule dependencies in financial services and government sectors.
- Managed Services:Outsourced detection and response for talent-constrained security teams.
Cloud-Based leads deployment volume, with Hybrid gaining share fastest among EU critical infrastructure operators.
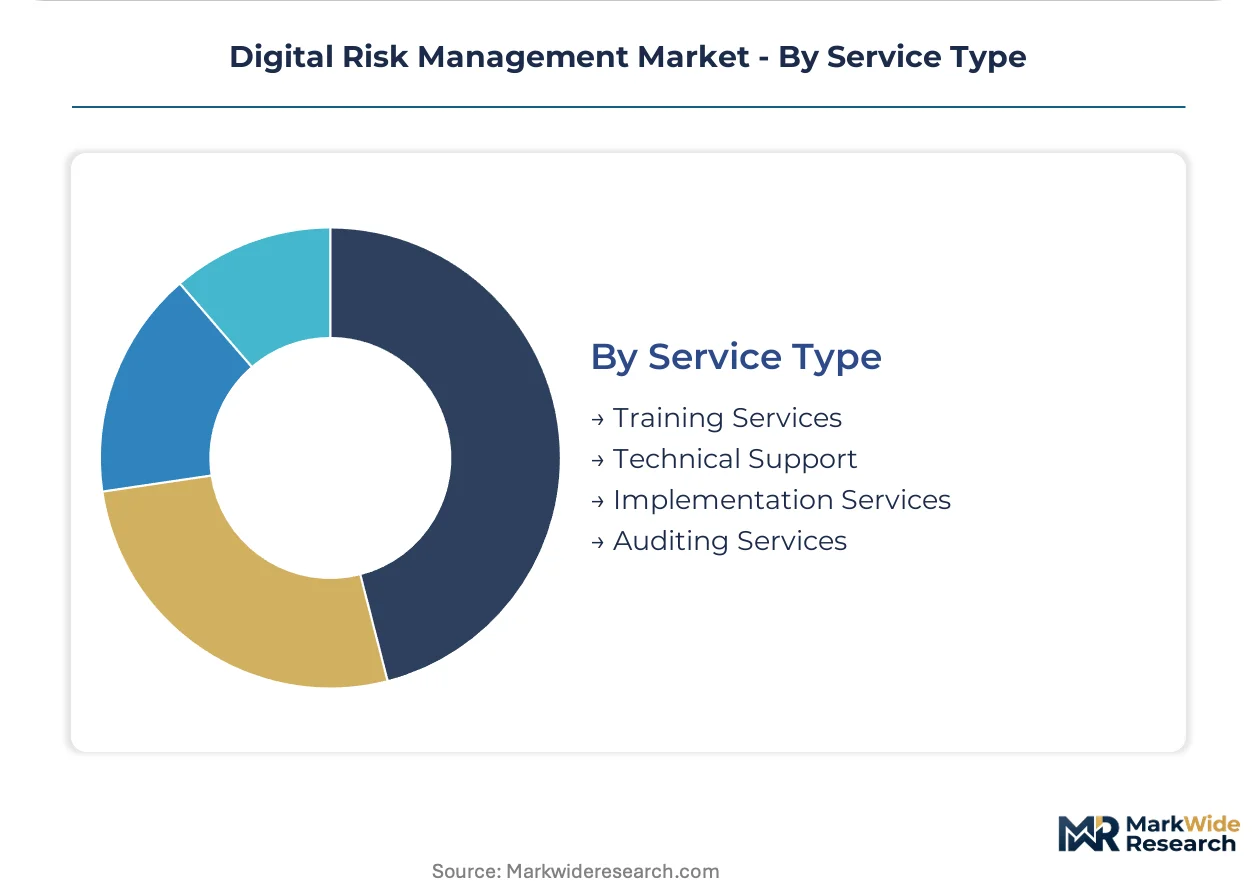
Service Type:
Supply concentration in certified implementation partners creates margin pressure for advisory and technical support categories, with forensic documentation capabilities commanding premium attach rates.
- Implementation Services:SIEM migration, SOAR integration, and telemetry pipeline reconstruction for cloud-native transitions. These services face extended timelines due to certified security architect scarcity, particularly for complex multi-vendor environments.
- Auditing Services:Forensic documentation and material incident reporting for SEC disclosure compliance. United States public companies sustain demand for these capabilities following mandatory cyber incident disclosure rules.
- Technical Support:Ongoing platform maintenance and detection engine tuning to reduce false positive fatigue.
- Training Services:Certification programs for threat intelligence analysts and security operations staff.
Implementation Services holds the top volume position, with Auditing Services ascending fastest on regulatory enforcement tailwinds.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Compliance cost differentials between jurisdictions are redirecting procurement budgets toward regions with harmonized regulatory frameworks. Enterprises in high-enforcement geographies absorb premium pricing for certified platforms, while mid-market buyers in emerging markets prioritize cloud-native solutions that bypass legacy infrastructure burdens.
United States
SEC cybersecurity disclosure rules and FDA guidance for connected medical devices drive procurement of forensic documentation capabilities. HIPAA enforcement actions against hospital networks sustain demand for continuous monitoring platforms. Financial institutions in New York and technology clusters in the Pacific Northwest pilot converged XDR-CSPM stacks for unified visibility.
Germany
EU NIS2 Directive deadlines and EU AI Act conformity assessments mandate human-in-the-loop oversight for high-risk cybersecurity systems. Critical infrastructure operators in energy and transport verticals prioritize sovereign cloud frameworks. Industrial security demand concentrates in Baden-Württemberg manufacturing corridors and Frankfurt financial centers.
India
RBI cybersecurity guidelines and CERT-In incident reporting mandates shape procurement specifications for financial institutions deploying UPI infrastructure. Health stack digitization creates demand for compliant monitoring platforms. Technology corridors in Karnataka and Maharashtra anchor cloud-native security adoption among SaaS providers.
United Kingdom
Financial Conduct Authority operational resilience requirements and cross-border GDPR adequacy constraints influence architecture choices for multinational enterprises. London-based insurers and capital markets firms stress-test risk scenarios using elastic compute fabrics. Scottish energy operators evaluate hybrid deployments for data sovereignty compliance.
Singapore
Monetary Authority of Singapore technology risk management guidelines and Project Guardian digital asset initiatives accelerate adoption of autonomous threat detection. Maritime and logistics operators in the Port of Singapore cluster deploy unified risk quantification tools. Regional headquarters for multinational banks drive premium pricing for integrated GRC-cyber convergence platforms.
Digital Risk Management Market Competitive Environment
United States vendors anchor the enterprise tier through integrated security stacks; European specialists hold compliance-centric positioning for regulated industries. Market structure tilts toward consolidation as cloud-native architectures compress platform economics and force rebuilds of telemetry pipelines. Three archetypes dominate: full-stack platform providers, managed detection and response specialists, and point-solution vendors seeking channel partnerships. Dominant competitive moves include strategic acquisitions to fill capability gaps and geographic expansion into India's digital public infrastructure markets.
Among network-centric platform providers, Palo Alto Networks exemplifies the full-stack archetype through firewall-to-SOAR pipeline dominance. Rapid7 occupies a position within the vulnerability management specialist tier, anchoring continuous attack surface monitoring workflows. BlueVoyant represents the managed detection and response category, competing for mid-market accounts against legacy MSSP incumbents.
| Leading Market Players |
|---|
| Appgate |
| BlueVoyant |
| Palo Alto Networks |
| Allgress |
| Everbridge |
| eSentire |
| Verizon |
| Unisys |
| Rapid7 |
| Others |
Value Chain & Pricing Dynamics
Cloud-native platform consolidation anchors both supply positioning and pricing power for digital risk management vendors, compressing margins for point-solution providers while full-stack incumbents capture premium attach rates through integrated telemetry pipelines.
Pricing Analysis
Direct-to-enterprise subscription tiers dominate cloud-native security procurement, displacing legacy three-year license agreements. Pricing stratifies across enterprise-grade integrated stacks, mid-market managed services, and entry-level monitoring platforms, with certification burden for EU AI Act conformity assessments widening spreads between compliant and non-compliant tiers. Cost compression in mid-market SaaS subscriptions is intensifying because AWS Marketplace and Azure Marketplace transactions bypass traditional reseller markups. Corporate enterprises with 500-5,000 employees exhibit highest price sensitivity, while financial institutions in New York and London absorb premiums for sovereign cloud frameworks with cross-jurisdictional attestation.
Supply Chain Analysis
Single-source vulnerability sits with Taiwan-based semiconductor fabrication for security appliance chipsets, constraining hardware-dependent vendors during foundry allocation cycles. Software supply chains draw from United States cloud infrastructure providers, Indian development centers for threat intelligence analytics, and Israeli cybersecurity research hubs for vulnerability signature generation. Tariff exposure on networking hardware components imported from China into North American and European markets elevates landed costs for hybrid deployment architectures. Distribution runs through hyperscaler marketplaces, managed security service providers, and direct enterprise sales teams, with channel friction rising as full-stack vendors restrict third-party integration access.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Digital risk management functions as a stable compounder, with regulatory enforcement velocity across SEC, EU NIS2, and RBI mandates sustaining durable procurement cycles regardless of macroeconomic conditions.
For Market Incumbents: Hedge against cloud-native displacement by rebuilding telemetry pipelines around elastic compute fabrics rather than defending on-premise appliance installed bases. Acquire specialized managed detection and response capabilities to capture mid-market accounts fleeing false-positive fatigue from poorly tuned autonomous platforms. Prioritize EU notified body certifications for high-risk AI system oversight to defend premium pricing in German and French critical infrastructure verticals. For New Entrants and Emerging Players: EU NIS2 Directive in Europe opens a window for sovereign cloud security frameworks targeting energy and transport operators facing 2024 compliance deadlines. India's RBI cybersecurity guidelines and CERT-In mandates create white-space demand among UPI infrastructure deployers and health stack digitization projects. Pursue AWS Marketplace and Azure Marketplace listing strategies to bypass channel conflict with established reseller networks and capture 500-5,000 employee corporate enterprises directly. For Investors and Strategic Acquirers: Consolidation pressure builds where point-solution vendors face interoperability friction against Palo Alto Networks, CrowdStrike, and Microsoft enterprise account dominance. Position for five-to-ten year holding periods as cloud-native architecture investments compress platform economics and force serial capability-gap acquisitions. Monitor EU AI Act enforcement patterns as the inflection signal distinguishing certified-platform premiums from compliance-discount valuations.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Converges XDR-CSPM stacks for unified visibility across London, Singapore, and New York financial institutions. |
| Acquisition of Specialist Firm | Fills managed detection and response gaps to compete for mid-market accounts against legacy MSSP incumbents. |
| Geographic Expansion | Targets India's UPI and health stack digitization with RBI-compliant sovereign cloud frameworks. |
| Strategic Partnership | Secures hyperscaler marketplace placement to displace three-year enterprise license agreements in mid-market segment. |
| Product Launch | Delivers EU AI Act-conformant platforms with documented training data provenance for German energy operators. |
Study Parameters
Coverage spans North America, Europe, and Asia-Pacific, with primary inputs from each region combined with secondary validation. Interviews with CISOs, IT procurement officers, platform engineers, and managed security service directors informed demand-side dynamics. Secondary sources include SEC cybersecurity disclosure filings, EU NIS2 implementation guidance, RBI circulars on payment infrastructure security, and hyperscaler capex disclosures. Bottom-up deployment estimates and top-down regulatory mandate sizing were triangulated against channel partner transaction data.
Rate-of-change decomposition across the analysis window separates baseline replacement demand from regulatory-driven incremental procurement. Segmentation dimensions modeled include deployment architecture, organization size tier, vertical regulatory exposure, integration complexity, and regional compliance maturity. CAGRs were derived from stress-testing scenario assumptions against historical enforcement patterns and technology substitution elasticities. Forecast inputs incorporate cloud marketplace transaction velocity and EU AI Act conformity assessment timelines.
Revisions become necessary when enforcement intensity diverges from modeled patterns or when hyperscaler marketplace terms shift channel economics materially. Forecasts reflect documented assumptions about regulatory deadline adherence and enterprise cloud migration cadence. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Risk Management and Compliance
AI in Fraud Management Market
Risk Management and Compliance
Medical Device Cyber Risk Quantification Market
Risk Management and Compliance
BFSI Security Market
Risk Management and Compliance
China Enterprise Risk Management Market
Risk Management and Compliance
Treasury and Risk Management Application Market
Risk Management and Compliance
Global Strategy Consulting Market
Risk Management and Compliance
Global Compliance Management Software Market
Risk Management and Compliance
Stress Testing Solutions Market
Risk Management and Compliance
United States Governance, Risk and Compliance Platform Market
Risk Management and Compliance
Global Patient Safety and Risk Management Softwares Market
Risk Management and Compliance
Global Credit Risk Rating Software Market
Risk Management and Compliance
Regtech Market
Risk Management and Compliance
Legal Advisory Service Market
Risk Management and Compliance
NPL Management Market
Risk Management and Compliance
Healthcare Safety and Risk Management Solutions Market
Risk Management and Compliance
Compliance As a Service Market