
 Cybersecurity Insurance Market | 2026-2036
Cybersecurity Insurance Market Size, Share, and Industry Trends Forecast 2026-2036
Cybersecurity Insurance Market Analysis
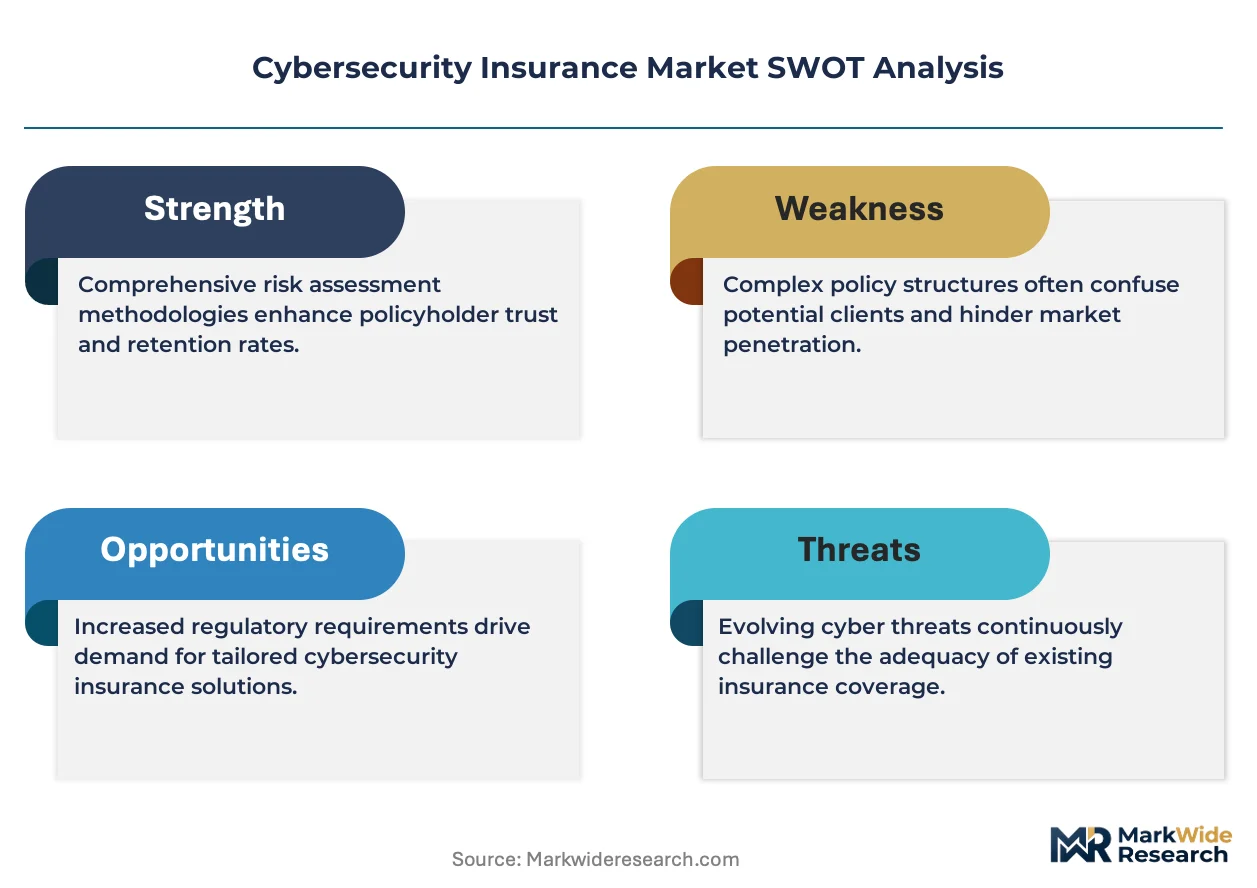
ISO/IEC 27001 certification is bifurcating the competitive landscape into qualified underwriters and excluded aspirants. Chubb leverages its proprietary risk-engineering platform to dominate Fortune 500 accounts with complex infrastructure exposures. Beazley sustains leadership in the Lloyd's syndicate model, anchoring its position through specialized cyber catastrophe response capabilities.
Cybersecurity insurance is a risk-transfer instrument that indemnifies policyholders against financial losses stemming from data breaches, network intrusions, and operational technology disruptions; underwriters price coverage using continuous vulnerability scanning, threat intelligence feeds, and actuarial models calibrated to incident frequency and severity metrics. First-party coverage segments command premium pricing as ransomware recovery costs and business interruption claims escalate, while third-party liability pools attract capacity from reinsurers seeking uncorrelated returns. The SME end-user segment represents the fastest-growing enrollment tier as managed security service providers bundle policies with detection and response services.
The US SEC, the EU's EIOPA, and the UK's Prudential Regulation Authority collectively shape market access through disclosure mandates, solvency capital requirements, and stress-testing protocols that elevate underwriting standards. HIPAA breach notification rules and the EU NIS2 Directive compel healthcare and critical infrastructure operators to maintain active coverage as a condition of regulatory compliance. Stakeholders must monitor how generative AI-enabled social engineering attacks recalibrate actuarial assumptions and coverage exclusions before renewal cycles tighten.
Market Dynamics
Ransomware frequency and severity are compressing underwriting margins while forcing carriers to embed continuous monitoring into policy terms. The EU Digital Operational Resilience Act and SEC disclosure mandates are converting discretionary coverage purchases into compliance-driven procurement.
Growth Catalysts
- EU DORA mandates:Financial entities across the European Union must demonstrate explicit cyber risk transfer mechanisms by 2025, creating compulsory purchase environments for operational resilience coverage.
- Healthcare ransomware exposure:HIPAA breach notification rules compel US providers to maintain active policies as patient data exfiltration incidents escalate recovery costs.
- SME bundled distribution:Managed security service providers are embedding cyber insurance into detection and response service tiers, expanding enrollment among previously uninsured small and medium enterprises.
Market Restraints
- Threat intelligence asymmetry:Attack surface scanning costs and dark web monitoring subscriptions inflate operational expenditure for underwriters without proprietary data feeds.
- Reinsurance capacity concentration:Alternative capital providers in Bermuda and London dominate catastrophe layer backing, creating single-point-of-failure exposure for primary carriers.
- Actuarial data scarcity:Limited historical claims severity distributions prevent accurate tail risk pricing, forcing conservative reserving that compresses returns.
Strategic Opportunities
- India's uninsured SME base:Digital payment penetration and data protection bill implementation are creating first-time buyer pools among mid-market technology services firms.
- OT-IT convergence coverage:Industrial control system endorsements for manufacturing and energy infrastructure represent an underserved premium segment with limited competition.
- Parametric triggers:Index-based settlement mechanisms using third-party breach verification are reducing claims adjustment friction and accelerating capital deployment.
Industry Challenges
- Cyber actuary scarcity:Qualified professionals capable of modeling correlated systemic events command compensation premiums that erode underwriting unit economics.
- Legacy policy administration:Core systems built for property-casualty lines lack API connectivity for real-time threat feed integration, delaying risk-engineering deployment.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cybersecurity Insurance Market |
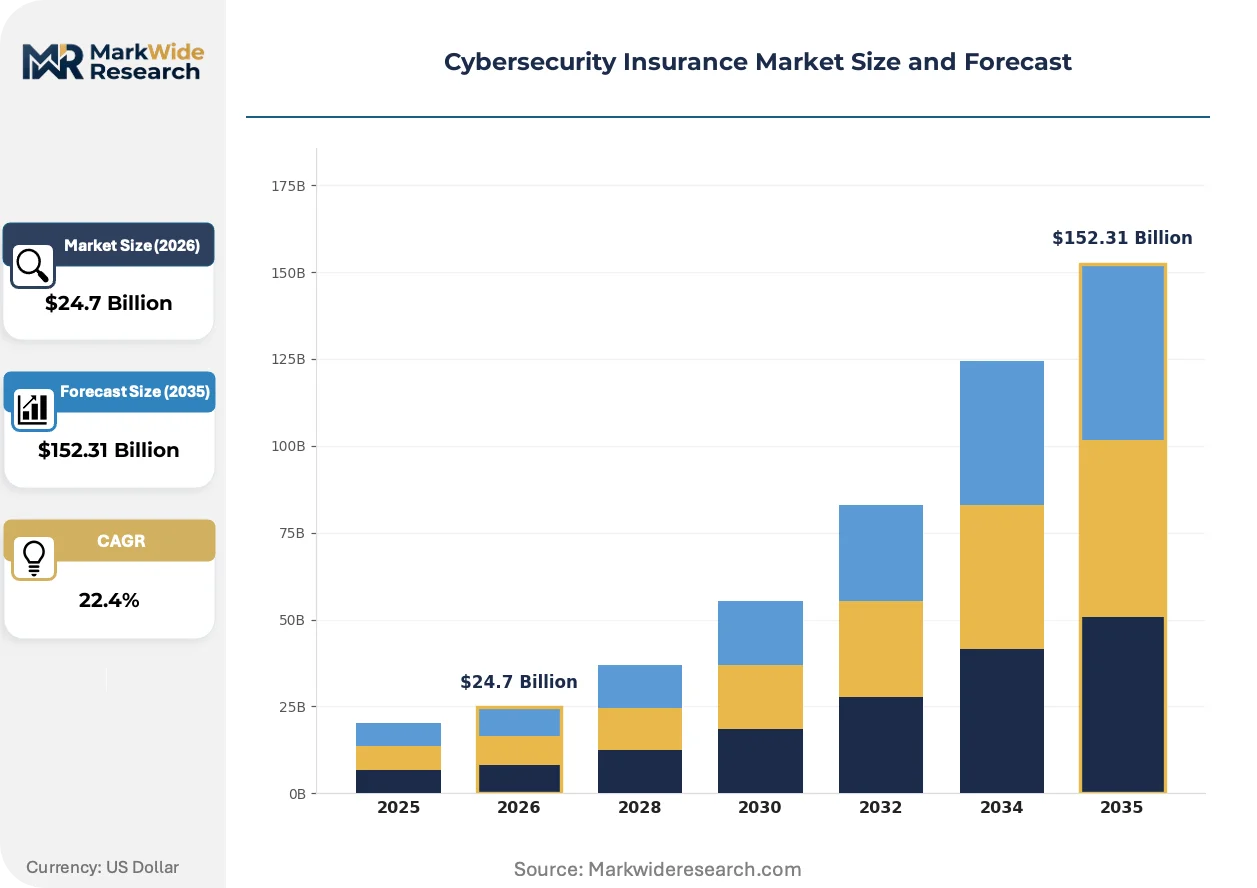
| Market Size in 2026 | $24.7 Billion |
| Market Size in 2035 | $152.31 Billion |
| CAGR (2026 – 2036) | 22.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Policy Type: First-Party Coverage, Third-Party Coverage, Comprehensive Coverage, Standalone Coverage End User: SMEs, Corporations, Government Entities, Non-Profits Industry Vertical: Healthcare, Finance, Education, Retail Geographical Market: North America, Europe, Asia-Pacific, Latin America |
| Companies Covered | Chubb, AIG, AXA XL, Travelers, Fairfax Financial, Beazley, CNA Financial, Arch Insurance Group, Zurich Insurance Group, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cybersecurity Insurance Market Emerging Trajectories
Generative AI-enabled attack vectors are forcing underwriters to rebuild risk-selection models around behavioral indicators rather than static control checklists. Continuous underwriting is replacing annual renewal cycles as the dominant policy architecture.
Attack surface management platforms are decomposing the traditional annual risk assessment into perpetual vulnerability monitoring. Mid-market enterprises are adopting these tools fastest, with deployment timelines compressing from twelve-month implementations to thirty-day integrations. This instrumentation is decomposing the information advantage that specialized underwriters previously held over standard commercial lines carriers.
The EU AI Act's risk classification framework is extending liability exposure to algorithmic decision systems used in claims processing and fraud detection. Insurers deploying automated underwriting engines must now maintain human-in-the-loop documentation for high-risk applications. European carriers are responding by segregating AI-driven pricing modules into separately capitalized entities to isolate regulatory contagion.
Corporate risk managers are consolidating cyber coverage procurement under enterprise-wide captives rather than decentralized department purchasing. This concentration is compressing commission structures for retail brokers while elevating fee-based advisory relationships with specialist intermediaries. The shift is most visible in Fortune 500 accounts, where chief risk officers now mandate centralized policy architecture across all operating subsidiaries.
Cybersecurity Insurance Market Segmentation
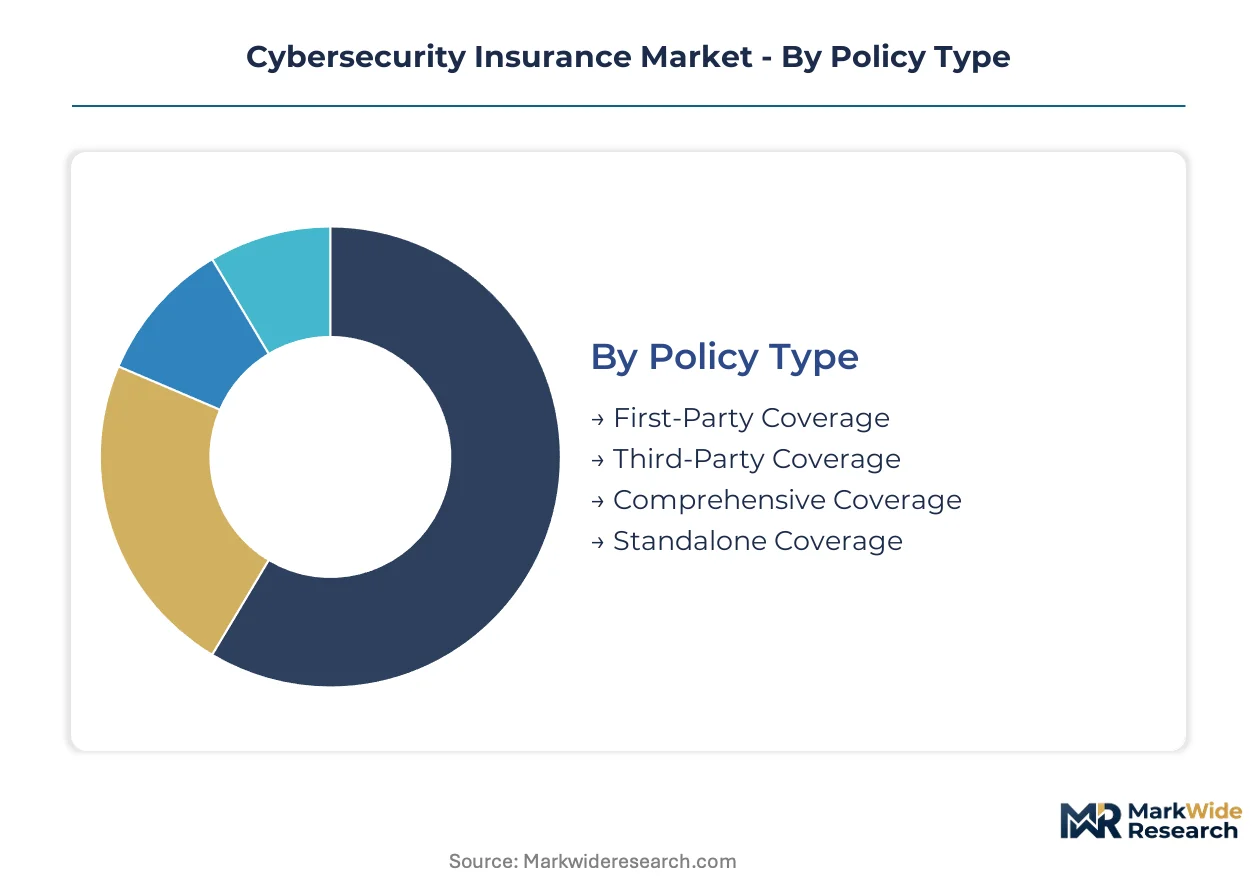
Cybersecurity insurance pricing varies dramatically across policy architectures and buyer profiles. Underwriters calibrate premiums using vulnerability scanning data, threat intelligence feeds, and claims severity histories specific to each segment combination.
Policy Type:
Domestic carriers dominate first-party and comprehensive offerings, while Lloyd's syndicates and Bermuda reinsurers anchor catastrophe layers for standalone coverage sold across multiple jurisdictions.
- First-Party Coverage:Indemnifies direct losses from ransomware recovery, business interruption, and forensic investigation costs. Demand concentrates among US healthcare providers facing HIPAA breach notification mandates as patient data exfiltration incidents escalate recovery expenditures.
- Third-Party Coverage:Shields against liability claims from customers, partners, and regulators following data breaches. European financial institutions under EU DORA compliance deadlines drive procurement as operational resilience frameworks mandate explicit risk transfer mechanisms.
- Comprehensive Coverage:Bundles first and third-party protection for complex infrastructure exposures.
- Standalone Coverage:Unbundled policies for specific risk categories or limited coverage periods.
Comprehensive coverage holds the largest share; momentum sits with first-party coverage as ransomware severity escalates.
End User:
Cost tier differentiation separates enterprise accounts with captive risk engineering from SME buyers purchasing through managed security service provider bundles.
- SMEs:Fastest-expanding enrollment tier purchasing through MSSP bundles with detection and response services. India's uninsured mid-market technology services firms represent emerging first-time buyer pools as digital payment penetration accelerates.
- Corporations:Fortune 500 accounts consolidate procurement under enterprise-wide captives with centralized policy architecture across operating subsidiaries. Chubb dominates this segment using proprietary risk-engineering platforms for complex infrastructure exposures.
- Government Entities:Federal, state, and municipal agencies with sovereign immunity considerations and public procurement rules.
- Non-Profits:Charitable organizations with limited security budgets and donor data protection obligations.
Corporations command premium pricing; SMEs are climbing the fastest as bundled distribution expands.
Industry Vertical:
Application-specific risk models differentiate healthcare's patient data exposure from finance's payment system vulnerabilities.
- Healthcare:HIPAA breach notification rules compel active coverage maintenance as ransomware incidents targeting patient records escalate. Recovery costs from data exfiltration events drive premium inflation in this vertical.
- Finance:EU DORA mandates and SEC disclosure rules create compulsory purchase environments for operational resilience coverage. Beazley anchors Lloyd's syndicate capacity for this segment through specialized cyber catastrophe response capabilities.
- Education:Universities and K-12 districts with limited security budgets and expansive attack surfaces.
- Retail:Payment card industry compliance requirements and seasonal revenue concentration.
Healthcare holds the largest share; momentum sits with finance as regulatory mandates tighten.
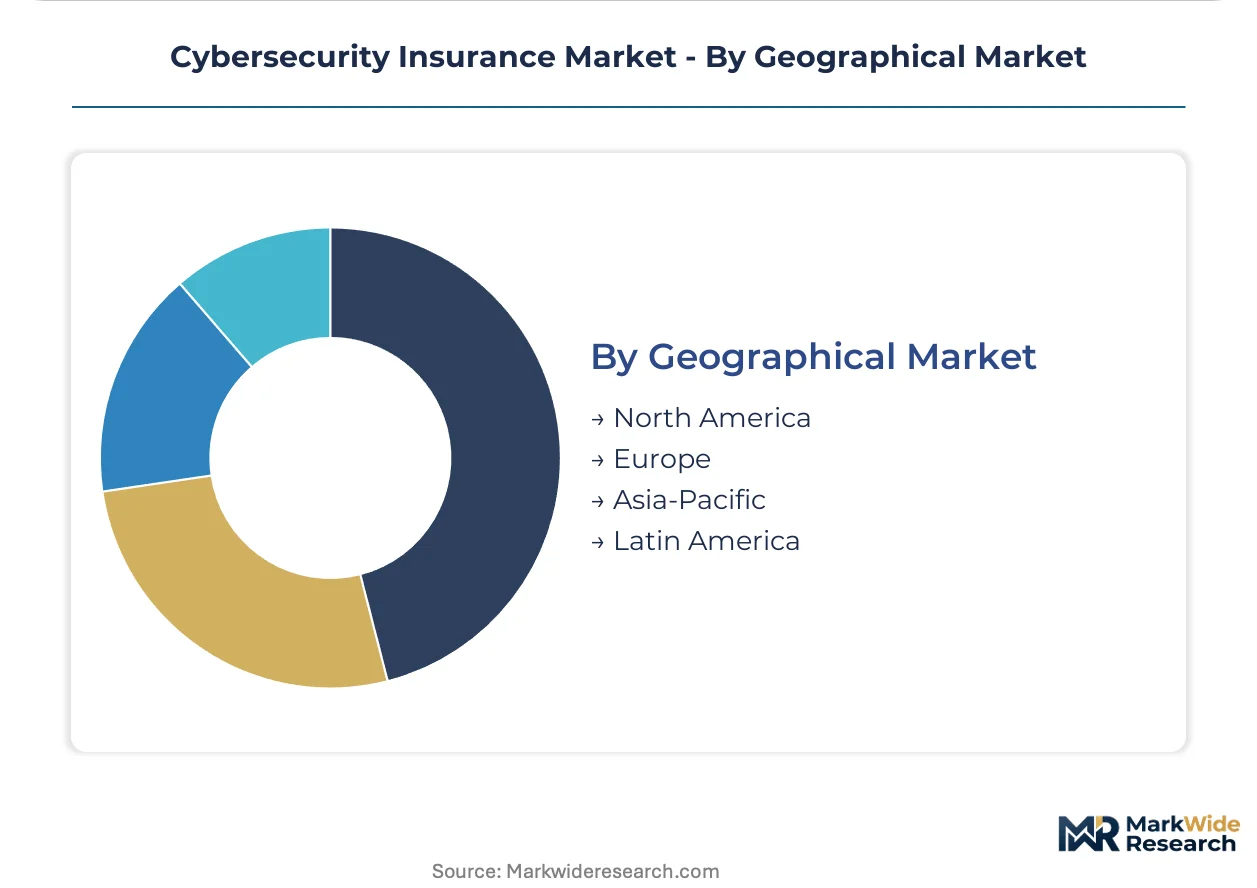
Geographical Market:
Volume concentration reflects breach notification law maturity and supervisory framework development.
- North America:US breach notification laws and SEC disclosure rules create compulsory purchase environments. Premium pricing reflects highest ransomware claim frequency and severity globally.
- Europe:EU DORA mandates and GDPR enforcement drive compliance-oriented procurement. EIOPA solvency capital requirements and stress-testing protocols elevate underwriting standards across the region.
- Asia-Pacific:Japan's METI cybersecurity guidelines and Australia's TGA medical device regulations shape coverage requirements. India's data protection bill implementation creates first-time buyer pools among mid-market technology services firms.
- Latin America:Brazil's LGPD data protection law and Mexico's fintech regulations establish emerging compliance frameworks.
North America holds the largest share; Asia-Pacific is gaining share fastest as digital payment penetration accelerates coverage adoption.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Enterprise buyers in the United States drive the highest premium volumes, while compliance mandates in Europe and digital payment expansion in Asia-Pacific create divergent growth trajectories across national markets.
United States
Fortune 500 risk managers consolidate procurement under enterprise-wide captives as ransomware severity escalates recovery costs. SEC disclosure rules and HIPAA breach notification mandates compel active coverage maintenance across healthcare and publicly traded entities. New York and California financial centers anchor demand concentration, with specialized underwriters deploying proprietary risk-engineering platforms for complex infrastructure exposures.
Germany
Industrial control system endorsements attract manufacturing conglomerates confronting OT-IT convergence vulnerabilities. EIOPA solvency capital requirements and stress-testing protocols elevate underwriting standards for operational resilience coverage. The Munich and Frankfurt insurance clusters host Lloyd's syndicate operations and domestic carriers competing for DORA-mandated financial institution accounts.
United Kingdom
Lloyd's syndicate capacity dominates catastrophe layer backing for international cyber programs. The Prudential Regulation Authority's disclosure mandates and operational resilience frameworks convert discretionary purchases into compliance-driven procurement. London's specialty insurance market anchors Beazley's catastrophe response capabilities and Bermuda reinsurer presence.
India
Mid-market technology services firms emerge as first-time buyer pools as digital payment penetration accelerates and data protection bill implementation advances. RBI cybersecurity guidelines for financial institutions and SEBI disclosure requirements shape coverage procurement patterns. Bangalore and Hyderabad technology corridors drive enrollment expansion among previously uninsured SME segments.
Japan
Manufacturing supply chain operators seek OT-IT convergence coverage as industrial control system exposures proliferate. METI cybersecurity guidelines and JIS standards frameworks establish baseline control expectations for policy eligibility. Tokyo and Osaka metropolitan areas concentrate demand from automotive and electronics conglomerates with complex cross-border infrastructure exposures.
Cybersecurity Insurance Market Vendor Landscape
Player mix skews toward diversified global carriers with established property-casualty infrastructure, tiered against specialized Lloyd's syndicates and regional mutuals. Market structure exhibits consolidation at the Fortune 500 tier alongside fragmentation in SME distribution through managed security service provider channels. Strategic archetypes include proprietary risk-engineering platforms, catastrophe response specialists, and bundled MSSP-affiliated underwriters. Dominant competitive moves encompass continuous underwriting technology deployment and geographic expansion into India's uninsured mid-market.
Within the diversified global carrier tier, Chubb and AIG occupy positions defined by complex infrastructure specialization and multinational program architecture. Among Lloyd's syndicate specialists, Beazley exemplifies catastrophe response capability anchoring. These named entities represent archetype anchors rather than exhaustive market coverage, with Zurich Insurance Group and Arch Insurance Group sitting within scale-driven segments serving cross-border enterprise accounts.
| Leading Market Players |
|---|
| Chubb |
| AIG |
| AXA XL |
| Travelers |
| Fairfax Financial |
| Beazley |
| CNA Financial |
| Arch Insurance Group |
| Zurich Insurance Group |
| Others |
Supply Flow & Price Mechanics
Reinsurance capacity utilization in Bermuda and London draws primary carriers toward catastrophe-layer dependency, compressing price floors for standalone coverage while elevating comprehensive policy minimums. Scale economies in threat intelligence aggregation separate qualified underwriters from excluded aspirants, bifurcating the competitive landscape into tiered pricing bands.
Pricing Analysis
Cost-plus contracts with threat-intelligence indexation dominate SME bundled distribution, where managed security service providers embed premiums into detection and response service tiers. Three-tier pricing structure across premium, standard, and economy levels separates Fortune 500 captives with proprietary risk-engineering platforms from mid-market accounts with continuous monitoring requirements and bare-bones first-party coverage. Cost compression in the standard tier is intensifying because dark web monitoring subscriptions inflate operational expenditure for underwriters without proprietary data feeds. SME buyers exhibit highest price sensitivity; Fortune 500 risk managers prioritize coverage breadth over premium minimization.
Supply Chain Analysis
Strait of Hormuz transit risk concentration underscores the vulnerability of reinsurance capacity flows from Bermuda and London to primary carriers in North America and Europe. Underwriting capacity concentrates in the United States, United Kingdom, and Bermuda; threat intelligence feeds rest on specialized vendors in Israel, the United States, and Singapore. Single-source vulnerability pervades the catastrophe-layer backing structure, where alternative capital providers dominate capacity for systemic event coverage. Distribution runs through Lloyd's syndicate networks for international programs and domestic carrier direct channels for standardized SME policies.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The acute shortage of cyber actuaries capable of modeling correlated systemic events constrains underwriting expansion and elevates compensation costs across the value chain. This capability gap rewards firms that secure specialized talent or acquire modeling technology ahead of renewal cycle tightening.
For Market Incumbents: Secure exclusive threat intelligence partnerships to defend information advantage against standard commercial lines carriers deploying attack surface management platforms. Deepen vertical integration into continuous underwriting technology to displace annual renewal architectures before competitors replicate Chubb's risk-engineering platform dominance. For New Entrants and Emerging Players: ISO/IEC 27001 certification fast-tracks entry into the SME bundled distribution channel, where managed security service providers seek underwriters with compliance-ready policy architectures. India's uninsured mid-market technology services firms represent the most penetrable geography; partner with domestic MSSPs to embed coverage into detection and response service tiers. For Investors and Strategic Acquirers: Mid-cycle technology positioning favors underwriters with deployed continuous underwriting infrastructure over legacy policy administration systems lacking API connectivity for real-time threat feed integration. Acquisition targets should demonstrate proprietary risk-engineering capabilities or established Lloyd's syndicate catastrophe response relationships. Monitor generative AI-enabled social engineering attack frequency as the inflection indicator for actuarial model recalibration and coverage exclusion tightening.| Strategic Initiative | Industry Significance |
|---|---|
| Continuous Underwriting Platform Deployment | Replaces annual renewal cycles with perpetual vulnerability monitoring integrated into policy terms. |
| Threat Intelligence Partnership | Secures proprietary data feeds that reduce operational expenditure and sharpen risk selection. |
| ISO/IEC 27001 Certification Investment | Qualifies underwriters for SME bundled distribution through MSSP channel partnerships. |
| India Market Expansion | Captures first-time buyer pools among mid-market technology services firms as data protection bill implementation advances. |
| OT-IT Convergence Coverage Development | Addresses underserved industrial control system endorsements for manufacturing and energy infrastructure. |
Methodological Framework
Desk research of regulatory filing databases, insurance supervisory authority stress-test disclosures, and Lloyd's syndicate capacity reports preceded structured interviews with chief underwriting officers, cyber actuaries, managed security service provider executives, and enterprise risk managers. Primary fieldwork combined with secondary validation against SEC disclosure patterns, EIOPA solvency capital requirement filings, and Bermuda Monetary Authority regulatory returns. Bottom-up enrollment data triangulated against top-down premium volume estimates across policy type, end user, and industry vertical segmentations.
Variance decomposition across the analysis window separates ransomware frequency trends, regulatory mandate implementation schedules, and reinsurance capacity availability into distinct forecast drivers. The modeling framework segments by policy architecture, buyer scale tier, industry vertical exposure, and geographic regulatory cluster. CAGRs derive from incident severity trajectory projections and compulsory purchase environment expansion rates calibrated to DORA and HIPAA enforcement patterns.
Decision-makers should treat outputs as directional under stable regulatory enforcement and reinsurance capacity availability assumptions; material deviation in systemic event correlation or generative AI attack proliferation would warrant model refresh. Practitioners should keep alternative scenarios live as EU AI Act liability extensions and SEC disclosure rule amendments evolve.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Insurance
Peer to Peer Insurance Market
Insurance
Digital Insurance Market
Insurance
France Property and Casualty Insurance Market
Insurance
Boiler Insurance Market
Insurance
Green Insurance Market
Insurance
Endowment Insurances Market
Insurance
India Life and Non-Life Insurance Market
Insurance
Cloud Computing in Insurance Market
Insurance
Sri Lanka Cyber (Liability) Insurance Market
Insurance
Asia-Pacific Group Health Insurance Market
Insurance
Online Insurance Market
Insurance
Greece Property and Casualty Insurance Market
Insurance
Marine Freight Insurance Market
Insurance
Cyber Liability Insurance Market
Insurance
Singapore Property and Casualty Insurance Market
Insurance
Drone Insurance Market