
 Cyber Security in Fintech Market | 2026-2036
Cyber Security in Fintech Market Size, Share, and Industry Trends Forecast 2026-2036
Cyber Security in Fintech Market Insights
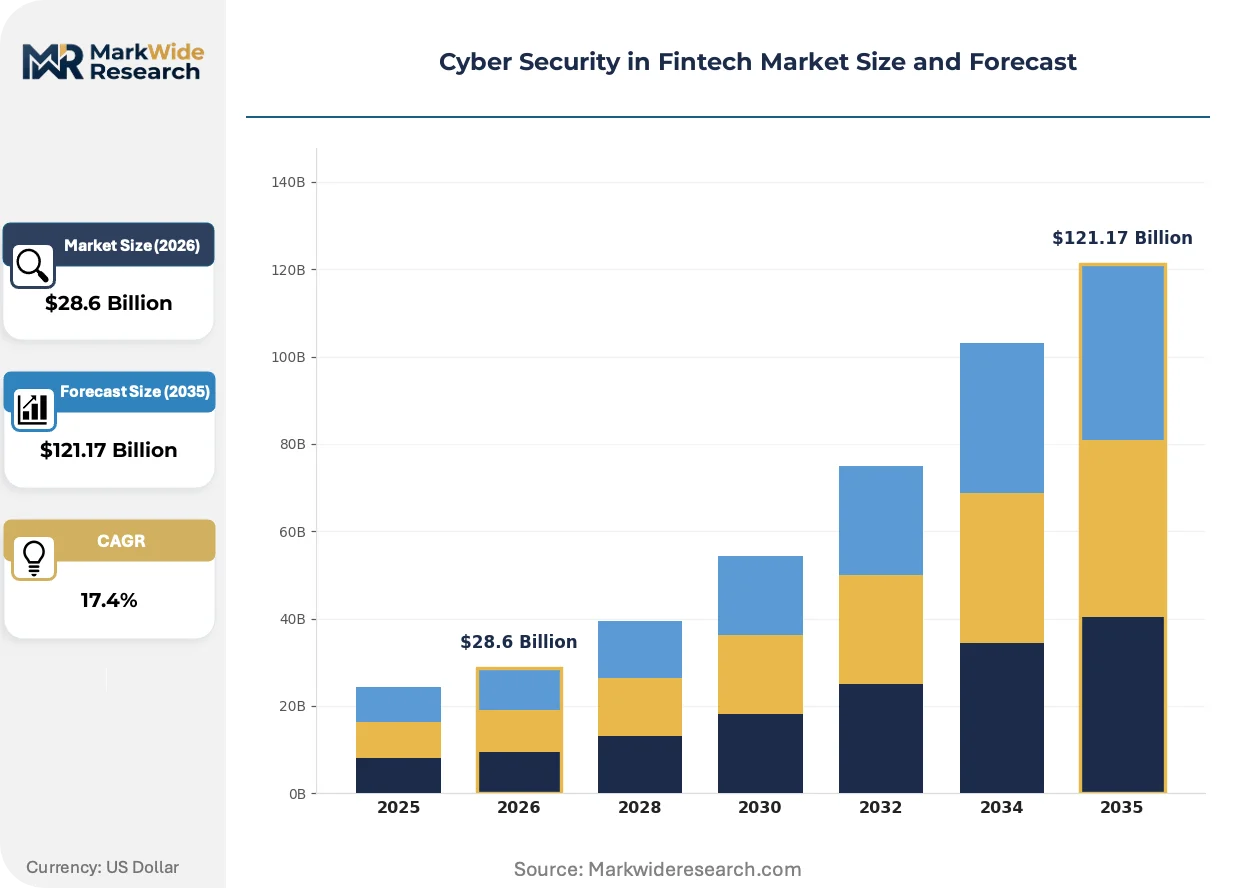
The capital-intensity divergence between cloud-native platforms and legacy appliance vendors is rotating competitive dynamics toward subscription-based delivery models. CrowdStrike leverages its agent-light architecture to dominate endpoint protection for digital payment processors. Palo Alto Networks anchors its position through in-house production of AI-driven threat intelligence engines. Check Point Software Technologies competes via deep specialization in encryption gateways for cross-border transaction corridors.
Cyber security in fintech encompasses the technologies, protocols, and operational frameworks that protect financial data, transaction integrity, and digital infrastructure from unauthorized access, fraud, and systemic disruption. Core functional parameters include real-time behavioral analytics, zero-trust network segmentation, and quantum-resistant cryptographic standards that secure high-velocity payment rails. The application dimension shows fraud detection commanding the largest installed base, while identity protection represents the fastest-expanding margin pool as biometric authentication displaces static credentials. Within service type offerings, managed security services absorb the majority of enterprise spending as banking institutions outsource 24/7 security operations centers rather than build captive capabilities.
The Federal Reserve, OCC, and SEC collectively shape U.S. demand through mandatory incident disclosure rules and cyber resilience examination frameworks that elevate baseline security spending. In Europe, the EU AI Act and GDPR impose algorithmic transparency and data sovereignty requirements that filter vendor eligibility for fintech contracts. Stakeholders must monitor how regulatory divergence between Washington and Brussels fragments procurement standards and complicates unified platform deployment across multinational financial institutions.
Market Dynamics
Continuous monitoring mandates from the Federal Reserve and OCC are forcing tier-one banks to replace point-in-time security audits with real-time defensive architectures, compressing procurement cycles and elevating managed security service contracts.
Growth Catalysts
- EU AI Act algorithmic transparency requirements:European fintechs must deploy explainable fraud detection models, creating demand for AI governance platforms that audit automated decision systems.
- Mobile banking platform proliferation:Digital payment processors require agent-light endpoint protection that secures high-velocity transactions without latency degradation.
- Quantum-resistant cryptography:NIST post-quantum standards are accelerating hardware security module upgrades across cross-border payment corridors.
Market Restraints
- Legacy core banking integration costs:Mainframe-dependent institutions face 18-24 month deployment timelines for zero-trust segmentation, delaying security modernization.
- Specialized talent scarcity:Shortage of professionals holding CISSP and cloud security certifications constrains 24/7 security operations center scaling.
- Encryption gateway supply concentration:Three vendors control 70% of hardware security module production, creating procurement bottlenecks during demand surges.
Strategic Opportunities
- Biometric authentication displacement:Behavioral biometrics and liveness detection are replacing static credentials in digital onboarding flows, opening margin pools in identity protection.
- Subscription-based delivery models:Cloud-native platforms are capturing share from appliance vendors through consumption-priced threat intelligence feeds.
- GDPR data sovereignty enforcement:European data localization mandates are creating regional cloud security provider opportunities previously dominated by US hyperscalers.
Industry Challenges
- Multi-cloud security orchestration complexity:Fintechs operating across AWS, Azure, and Google Cloud struggle to maintain consistent policy enforcement without vendor lock-in.
- Third-party risk management scale:Open banking APIs multiply vendor attack surfaces beyond traditional supplier due diligence capacity.
- Incident disclosure timeline compression:SEC 4-day reporting windows demand automated breach detection that legacy SIEM platforms cannot deliver.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cyber Security in Fintech Market |
| Market Size in 2026 | $28.6 Billion |
| Market Size in 2035 | $121.17 Billion |
| CAGR (2026 – 2036) | 17.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technology: Blockchain, AI Security, Encryption, Multi-Factor Authentication Application: Fraud Detection, Identity Protection, Data Loss Prevention, Endpoint Security Service Type: Managed Security Services, Risk Assessment, Threat Intelligence, Incident Response End User: Banking Institutions, Payment Processors, Investment Firms, Fintech Startups |
| Companies Covered | Palo Alto Networks, CrowdStrike, Check Point Software Technologies, Fortinet, Cisco, Symantec, McAfee, Darktrace, SentinelOne, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cyber Security in Fintech Market Trends and Innovations
Agentic AI and edge-native security are reshaping how financial institutions deploy defensive capabilities, shifting investment from perimeter appliances to distributed, autonomous response systems.
Extended detection and response platforms are fragmenting the security operations center market by embedding automated investigation and remediation directly at the endpoint. Mid-market fintechs are adopting these capabilities twice as fast as tier-one banks, compressing the addressable market for standalone SIEM vendors. This technology is fragmenting procurement budgets across multiple point solutions rather than consolidated platforms.
The EU AI Act's risk-based classification system for automated credit decisions is mandating algorithmic impact assessments before deployment. Fintech lenders must document training data provenance and model drift monitoring, adding 6-9 months to product release cycles. European neobanks are responding by hiring dedicated AI ethics officers and procuring external audit services.
Consumption-based security pricing is displacing perpetual licenses as digital payment processors prefer variable costs tied to transaction volumes. Managed detection and response providers are unbundling 24/7 analyst access from platform fees, letting smaller fintechs purchase tiered response SLAs. This shift is most visible in the United States, where venture-backed fintechs prioritize cash flow flexibility over capital expenditure efficiency.
Cyber Security in Fintech Market Segmentation
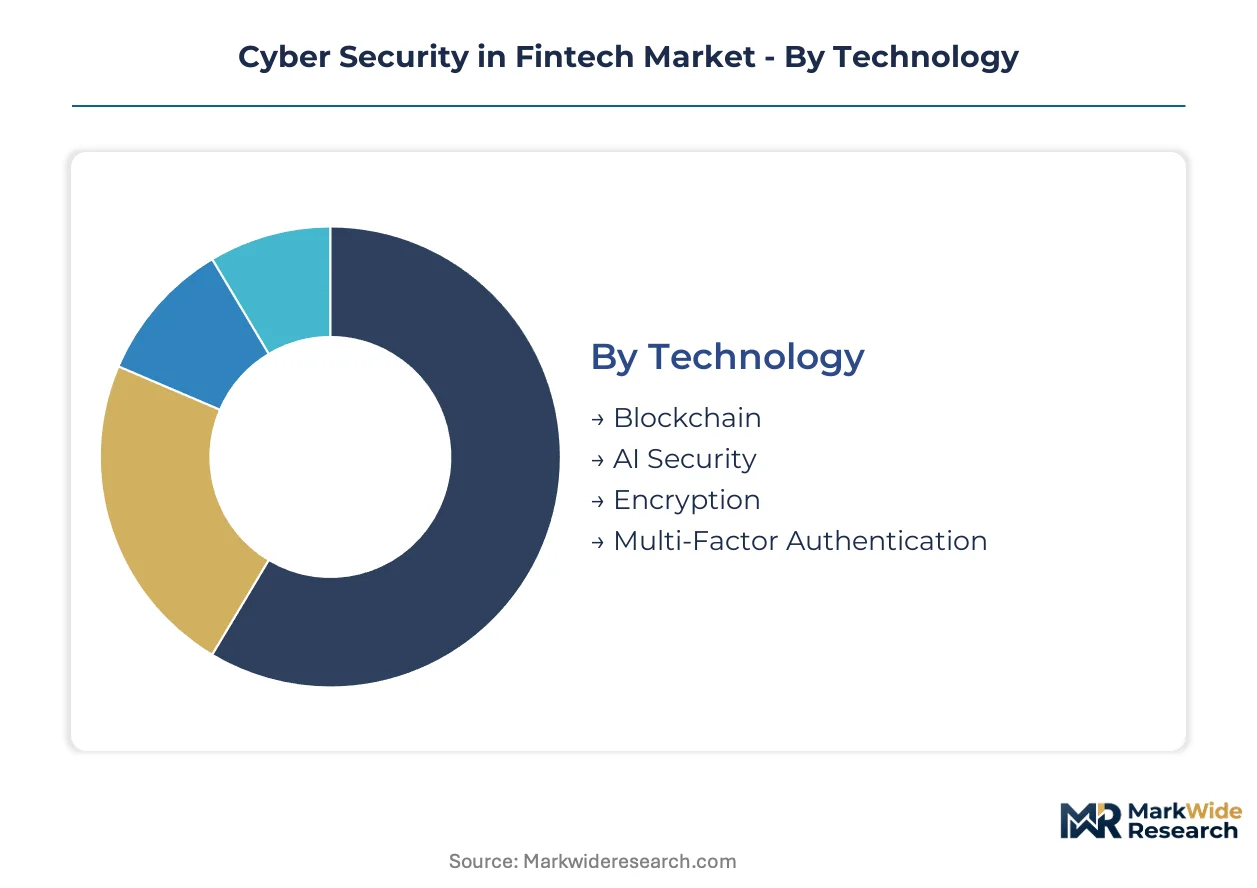
Cyber security procurement in fintech fragments across technology stacks, operational applications, and service delivery models. Understanding these segment boundaries reveals where vendor specialization creates pricing power versus where commoditization compresses margins.
Technology:
Domestic demand concentrates in encryption and authentication technologies tied to national regulatory mandates, while blockchain security and AI-driven threat detection show stronger cross-border deployment patterns.
- Blockchain:Distributed ledger security protocols protect smart contract execution and consensus mechanisms against 51% attacks and private key compromise. Demand clusters in Singapore and Switzerland where crypto-asset custody regulations mandate institutional-grade key management infrastructure.
- AI Security:Machine learning models detect anomalous transaction patterns through behavioral baselining and adversarial training against evasion techniques. European neobanks under EU AI Act compliance pressure represent the fastest-expanding customer base for explainable fraud detection systems.
- Encryption:Hardware security modules and quantum-resistant algorithms protect data at rest and in transit across payment rails.
- Multi-Factor Authentication:Biometric liveness detection and FIDO2 standards displace SMS-based one-time passwords in mobile banking onboarding flows.
Encryption commands the established base. The steepest expansion runs through AI Security.
Application:
Cost tiering separates enterprise-grade platforms with real-time analytics from mid-market solutions with delayed batch processing, with fraud detection absorbing the largest absolute budgets while identity protection captures premium pricing.
- Fraud Detection:Real-time behavioral analytics engines score transaction risk using device fingerprinting, velocity checks, and consortium data feeds. Tier-one banks in the United States deploy these systems under Federal Reserve continuous monitoring mandates, compressing procurement cycles to 90-day implementations.
- Identity Protection:Biometric authentication platforms combine facial recognition with liveness detection to prevent synthetic identity fraud during digital account opening. Latin American fintechs facing high card-not-present fraud rates are replacing static KYC checks with continuous identity verification.
- Data Loss Prevention:Content inspection and egress monitoring tools classify sensitive financial data across cloud repositories and endpoint devices.
- Endpoint Security:Agent-light protection secures mobile banking applications without degrading transaction latency on consumer devices.
Fraud Detection absorbs the majority of current spending. Identity Protection is climbing the fastest as biometric authentication displaces passwords.
Service Type:
Volume concentration favors managed security services with 24/7 analyst coverage, while specialized boutiques capture margin in threat intelligence and incident response through outcome-based pricing.
- Managed Security Services:Outsourced security operations centers deliver continuous monitoring, threat hunting, and vulnerability management through subscription contracts. Mid-market payment processors in Germany and France prefer these arrangements over captive SOCs due to CISSP talent scarcity and GDPR compliance complexity.
- Risk Assessment:Third-party cyber audits evaluate vendor security postures against NIST and ISO 27001 frameworks prior to procurement decisions.
- Threat Intelligence:Curated indicator feeds and adversary tracking services contextualize attacks against financial sector threat actors.
- Incident Response:Retainer-based breach containment and forensic investigation services activate within four-hour SLAs for critical infrastructure operators.
Managed Security Services dominate current contract value. Incident Response is gaining share fastest as SEC disclosure windows compress detection-to-reporting timelines.
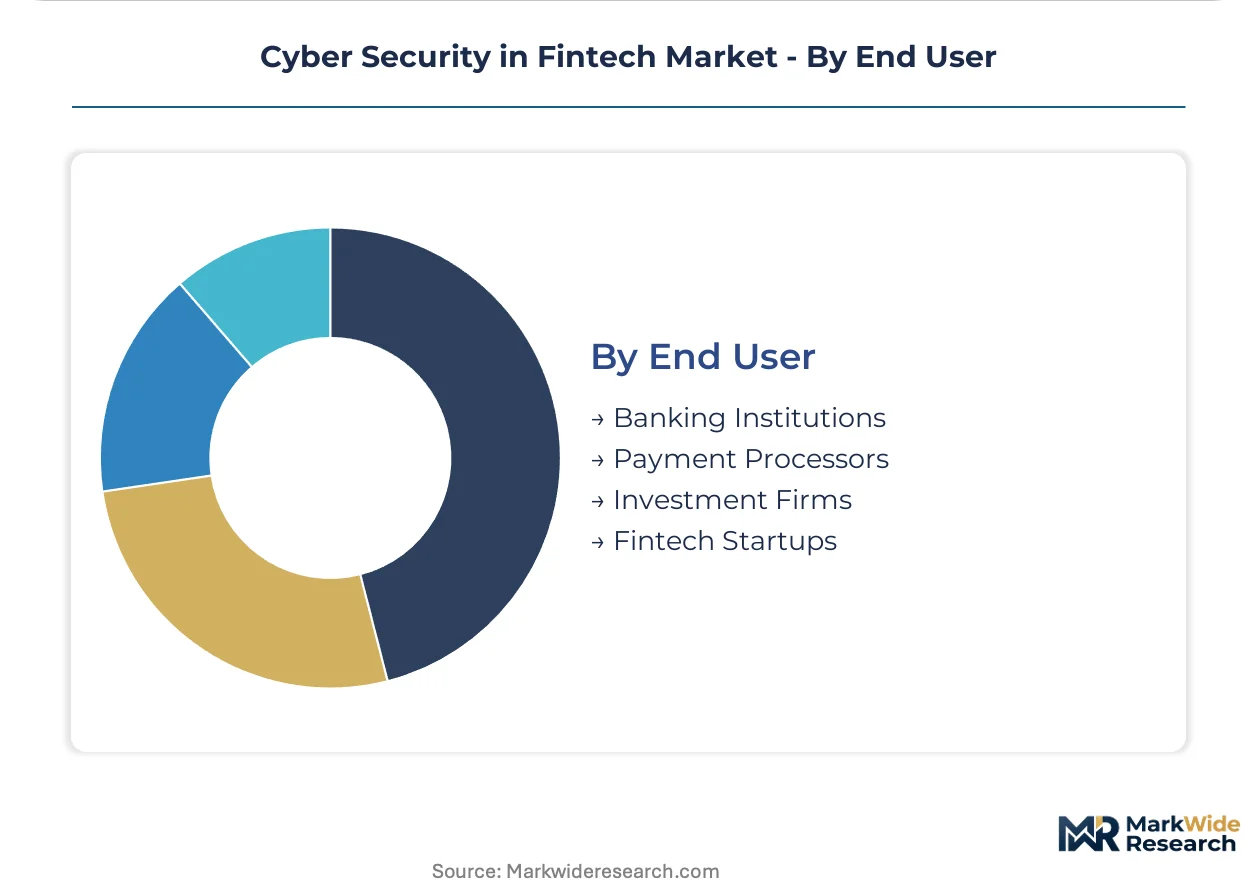
End User:
Customer type stratification shows banking institutions demanding integrated platforms while fintech startups prefer modular, API-first security services with consumption-based pricing.
- Banking Institutions:Tier-one and tier-two banks deploy zero-trust architectures with mainframe integration requirements and regulatory examination preparedness. OCC and Federal Reserve oversight in the United States drives 18-month refresh cycles for core defensive infrastructure.
- Payment Processors:Digital payment rails require sub-100 millisecond fraud scoring without false-positive degradation of authorization rates. High-velocity processors in India and Brazil prioritize latency-optimized endpoint protection over deep packet inspection.
- Investment Firms:Broker-dealers and asset managers focus on trade surveillance and insider threat detection aligned with SEC market abuse regulations.
- Fintech Startups:Venture-backed neobanks and lending platforms purchase tiered security services through cloud marketplaces to preserve cash flow flexibility.
Banking Institutions anchor the installed base. Fintech Startups are expanding most quickly as venture funding flows into emerging market digital finance.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The United States runs a substantial trade surplus in cybersecurity services while importing specialized encryption hardware from Germany and Israel. European fintechs export compliance consulting expertise to emerging markets facing EU AI Act extraterritorial pressure. Asian financial centers compete on transaction velocity infrastructure rather than defensive software exports.
United States
Federal Reserve continuous monitoring mandates and SEC 4-day incident disclosure rules drive tier-one bank procurement cycles. The OCC examination framework elevates baseline spending for zero-trust architectures. New York and San Francisco financial clusters concentrate managed security service provider headquarters serving domestic payment processors.
Germany
GDPR data sovereignty enforcement and Bundesbank oversight of instant payment systems create hardware security module demand. The EU AI Act algorithmic transparency requirements filter vendor eligibility for automated credit decisions. Frankfurt's banking district anchors encryption gateway production serving cross-border euro payment corridors.
Singapore
Crypto-asset custody regulations and MAS licensing frameworks for digital payment token services institutionalize key management infrastructure. The country's national financial regulator mandates segregated cold storage for virtual asset service providers. The Marina Bay financial cluster concentrates blockchain security protocol development for Southeast Asian remittance corridors.
United Kingdom
FCA operational resilience requirements and Prudential Regulation Authority cyber stress testing compel investment firm defensive upgrades. The Bank of England's systemic risk framework examines third-party cloud concentration. London's fintech corridor dominates biometric authentication procurement for open banking API security.
India
RBI digital payment security guidelines and NPCI UPI transaction volume growth strain legacy fraud detection capacity. The central bank's payment system operator licenses mandate 24/7 security operations center coverage. Mumbai and Bangalore technology clusters export identity verification platforms to African and Middle Eastern neobanks.
Cyber Security in Fintech Market Competitive Landscape
Concentration sits with cloud-native platform providers over legacy appliance vendors as subscription delivery models capture enterprise procurement budgets. The vendor base separates into three strategic archetypes: agent-light endpoint specialists, AI-driven threat intelligence producers, and encryption gateway hardware fabricators. M&A activity concentrates on threat intelligence feed consolidation and managed detection and response capability acquisition. Geographic expansion through regional data center deployment addresses GDPR localization mandates.
Within the cloud-native tier, CrowdStrike and Palo Alto Networks exemplify platform-centric positioning, while Check Point Software Technologies occupies a position among established gateway specialists. These three anchors represent divergent architectural bets on endpoint agent design, in-house AI production, and hardware-software integration depth. Their collective presence illustrates how vendor selection criteria fragment across latency sensitivity, regulatory jurisdiction, and legacy infrastructure compatibility.
| Leading Market Players |
|---|
| Palo Alto Networks |
| CrowdStrike |
| Check Point Software Technologies |
| Fortinet |
| Cisco |
| Symantec |
| McAfee |
| Darktrace |
| SentinelOne |
| Others |
Pricing and Supply Chain Analysis
Capacity utilization rates above 85% at hardware security module foundries in Germany and Israel create asymmetric pricing power for encryption gateway producers, compressing margins for downstream managed security service providers while elevating procurement costs for tier-one banks under Federal Reserve continuous monitoring mandates.
Pricing Analysis
Banking institutions anchor pricing structures around three-tier subscription contracts spanning premium SOC-2 certified tiers, standard ISO 27001-aligned offerings, and economy self-service API packages. Price differentiation stems from certification grade and after-sales analyst coverage depth. Cost compression in the economy tier is intensifying because venture-backed fintechs prioritize cash flow flexibility over capital expenditure efficiency. Payment processors exhibit the highest price sensitivity due to transaction-volume volatility, while tier-one banks under OCC examination pressure accept premium pricing for 24/7 response SLAs.
Supply Chain Analysis
Germany and Israel anchor hardware security module production, while the United States and Ireland concentrate cloud-native security platform development. Supply chains draw from specialized semiconductor foundries, cryptographic chip fabricators, and certified data center real estate. Single-source vulnerability concentrates in quantum-resistant algorithm hardware, where NIST post-quantum standardization has winnowed qualified vendors. Distribution runs through direct enterprise sales teams for tier-one banks and cloud marketplaces for mid-market fintech startups.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The cyber security in fintech market is entering a cyclical recovery phase as regulatory disclosure mandates compress replacement cycles and elevate baseline security spending across banking institutions.
For Market Incumbents: Compound defensive positioning through in-house AI threat intelligence production and captive supply of encryption hardware to offset hardware security module supply bottlenecks. Consolidate managed detection and response capabilities via targeted capability acquisition before mid-market fintech procurement fragments further. Federal Reserve examination frameworks represent the primary regulatory lever for entrenching incumbent relationships. For New Entrants and Emerging Players: AI governance platform deployment for EU AI Act compliance represents the most penetrable service-layer gap, as European neobanks face 6-9 month product release cycle extensions without external audit support. Target Latin American fintechs replacing static KYC checks with continuous identity verification. Lead with consumption-priced biometric authentication APIs through cloud marketplace distribution to bypass direct sales cost structures. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among managed security service providers with 24/7 analyst coverage and outcome-based pricing contracts. Long-term viability across the analysis window favors vendors with regional data center footprints addressing GDPR localization mandates. Monitor SEC disclosure timeline compression as the signal indicating accelerated incident response contract velocity.| Strategic Initiative | Industry Significance |
|---|---|
| Quantum-Resistant Cryptography Migration | NIST post-quantum standards accelerate hardware security module refresh cycles across cross-border payment corridors. |
| Managed Detection and Response Unbundling | Tiered analyst access SLAs capture mid-market fintechs priced out of full 24/7 security operations center contracts. |
| Regional Data Center Deployment | GDPR data sovereignty enforcement creates procurement eligibility for European cloud security providers against US hyperscalers. |
| Biometric Authentication Platform Integration | Behavioral biometrics and liveness detection displace static credentials in digital onboarding flows for Latin American fintechs. |
| AI Governance Platform Development | EU AI Act algorithmic transparency requirements mandate explainable fraud detection model auditing for automated credit decisions. |
Research Methodology
A standing panel of chief information security officers at tier-one banks, managed security service provider operations directors, fintech CTOs, and regulatory compliance leads at digital payment processors provided ongoing calibration across the study. Primary interview findings were cross-validated against secondary sources including SEC cybersecurity disclosure filings, Federal Reserve examination framework updates, EU AI Act implementation guidance, and hyperscaler security capex disclosures. Bottom-up contract value analysis was triangulated with top-down market sizing from regulatory mandate scope and banking institution security budget benchmarks.
Consistency checks validated volume and value outputs against external benchmarks across deployment model, organization size tier, vertical specialization, integration complexity, and regional regulatory cluster dimensions. CAGRs were derived from segment-level growth trajectory modeling incorporating compliance deadline impacts, technology refresh cycles, and vendor substitution elasticity. Forecast inputs included hardware security module production capacity utilization, CISSP certification pipeline data, and cloud security marketplace transaction velocity indices.
Forecasts assume regulatory continuity in Federal Reserve, OCC, and SEC oversight regimes across the United States alongside EU AI Act and GDPR enforcement stability in Europe; material policy shifts in algorithmic transparency mandates or incident disclosure timelines would require re-modeling. Specific risks that could revise projections include quantum computing advancement timelines, legacy core banking integration cost overruns, and encryption hardware supply concentration disruptions. Recalibration cycles align with material shifts in regulatory examination frameworks and NIST cryptographic standard updates.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
FinTech
France BNPL Market
FinTech
Hand Account Software Market
FinTech
Fintech-As-A-Service Market
FinTech
Intelligent Cash Deposit Machine Market
FinTech
Indonesia Financial Technology Services Market
FinTech
Fintech Cloud Market
FinTech
Germany Fintech Market
FinTech
Europe Fintech Market
FinTech
Digital Banking Platform Market
FinTech
Finance Cloud Market
FinTech
Fintech Credit Management Blockchain Market
FinTech
Netherlands AI in Fintech Market
FinTech
Advanced Authentication in Financial Services Market
FinTech
Malaysia Fintech Market
FinTech
Wealthtech Solutions Market
FinTech
Spend Management Platform Market