
 Cyber Crisis Management Market | 2026-2036
Cyber Crisis Management Market Size, Share, and Industry Trends Forecast 2026-2036
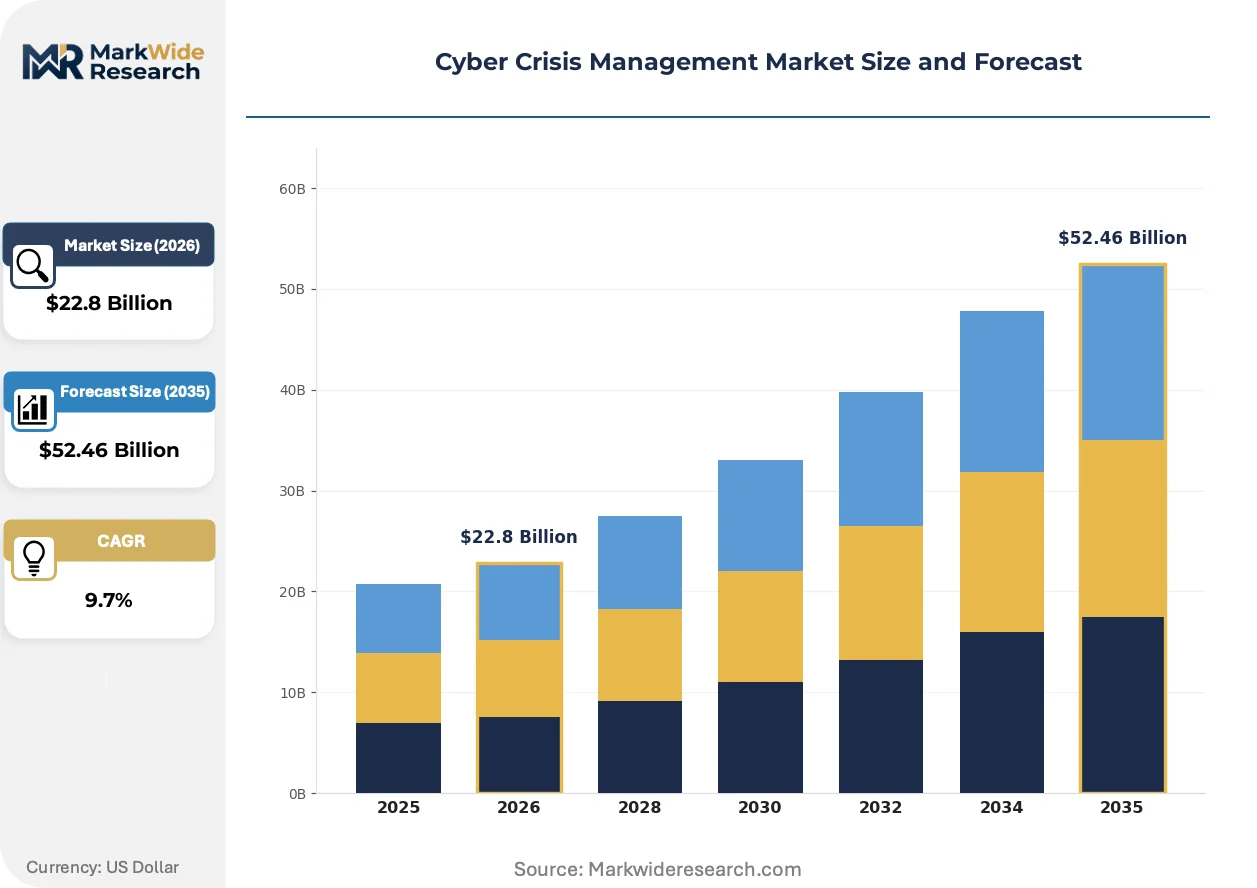
Cyber Crisis Management Market Outlook
Zero-trust architecture is tilting enterprise security investments toward continuous verification models rather than perimeter defense. Palo Alto Networks leverages integrated platform consolidation to anchor large-enterprise deployments across North America and Europe. CrowdStrike competes through native endpoint detection with embedded threat intelligence, while IBM Security sustains consulting-led crisis response engagements that extend into post-breach remediation services.
Cyber crisis management encompasses the organizational protocols, technical tools, and governance frameworks used to detect, contain, and recover from malicious cyber incidents with defined recovery time objectives typically measured in hours. Incident response services command the largest revenue pool as breach retainers convert to active engagements, while cloud-based deployment grows fastest as distributed workforces eliminate on-premises security chokepoints. Preparedness training lags in penetration among mid-market retailers but carries expanding margin potential as regulators mandate tabletop exercises.
The SEC mandates public companies disclose material cybersecurity incidents within four business days, while the EU NIS2 Directive imposes supply-chain security obligations across critical infrastructure operators. ISO 27035 provides the baseline framework for incident management procedures that enterprises align against for insurance eligibility and contractual compliance. Stakeholders must evaluate whether their crisis playbooks integrate automated containment with legal privilege preservation as regulatory scrutiny intensifies.
Market Dynamics
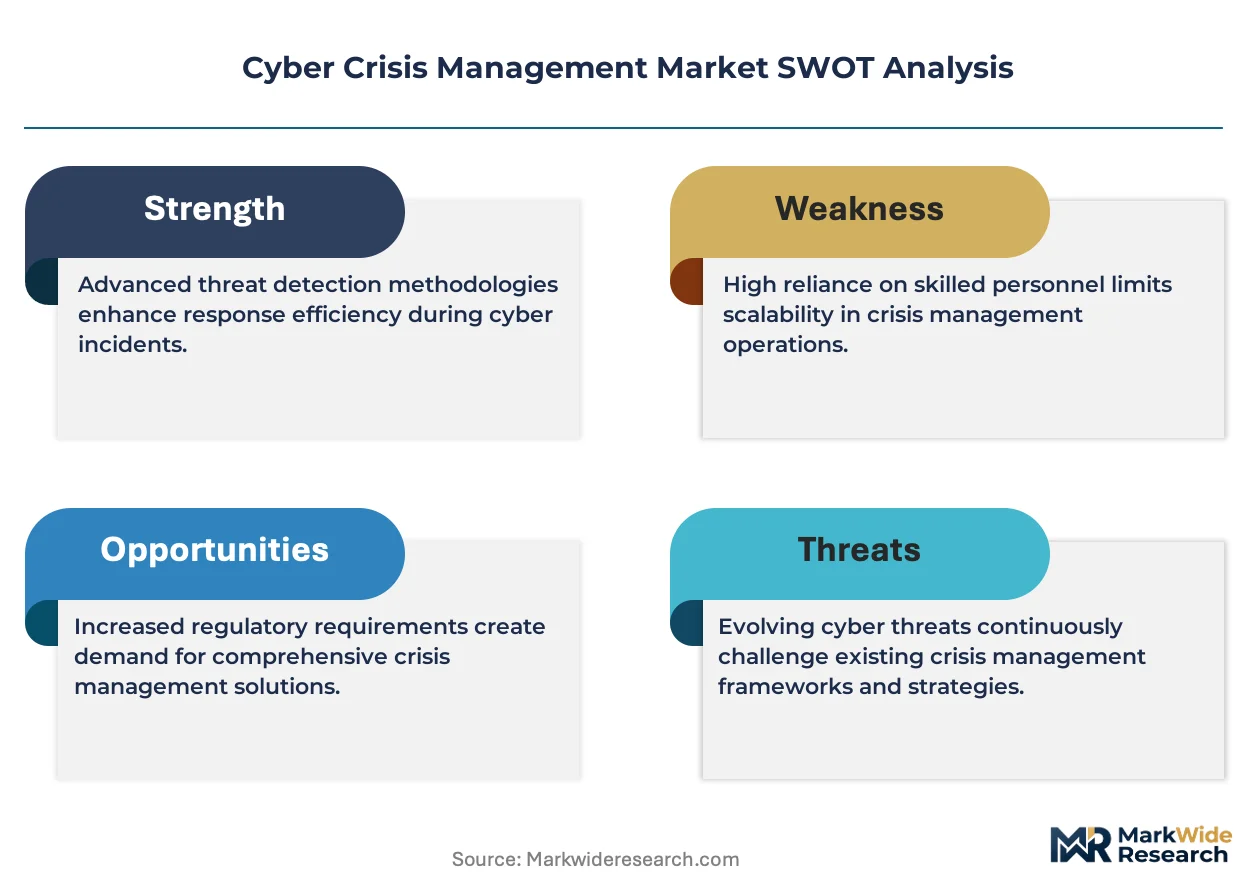
Zero-trust architecture is collapsing perimeter-based security investments as enterprises reallocate budgets toward continuous verification models and automated incident containment protocols.
Growth Catalysts
- EU NIS2 Directive:Supply-chain security obligations across critical infrastructure operators are mandating breach notification systems and tabletop exercise protocols.
- Financial Services Procurement:Banks and insurers are expanding incident response retainer contracts to meet SEC four-day disclosure requirements for material cybersecurity events.
- Cloud-Native Detection:Distributed workforces are eliminating on-premises security chokepoints and accelerating demand for cloud-based crisis management platforms.
Market Restraints
- Specialized Talent Scarcity:Shortages of certified incident responders and forensic analysts constrain service delivery capacity across retained and active engagements.
- Legacy Architecture Drag:Enterprises with entrenched perimeter-defense investments face sunk-cost barriers when migrating to zero-trust frameworks.
- Insurance Eligibility Friction:Underwriters are tightening coverage terms and demanding ISO 27035 alignment before issuing cyber risk policies.
Strategic Opportunities
- Mid-Market Retail Penetration:Preparedness training remains underdeveloped among mid-market retailers, creating margin expansion potential as regulators mandate tabletop exercises.
- AI-Enhanced Forensics:Convergence of machine learning with automated containment is enabling sub-hour recovery time objectives for ransomware events.
- Post-Breach Remediation:Crisis response engagements are extending into long-term remediation services, creating recurring revenue streams beyond initial containment.
Industry Challenges
- Privilege Preservation Complexity:Automated containment tools must integrate with legal privilege protocols to protect incident response communications from discovery.
- Cross-Border Notification Coordination:Enterprises face conflicting breach disclosure timelines between SEC four-day mandates and EU AI Act notification requirements.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cyber Crisis Management Market |
| Market Size in 2026 | $22.8 Billion |
| Market Size in 2035 | $52.46 Billion |
| CAGR (2026 – 2036) | 9.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Incident Response, Preparedness Training, Risk Assessment, Compliance Management Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Financial Institutions, Government Agencies, Healthcare Providers, Retailers Response Phase: Prevention, Detection, Containment, Recovery |
| Companies Covered | Fortinet, IBM Security, Palo Alto Networks, SentinelOne, Trellix, CrowdStrike, Cisco Systems, Check Point Software Technologies, Microsoft Security, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cyber Crisis Management Market Strategic Shifts
Security operations centers are consolidating point solutions into integrated platforms that collapse detection-to-response latency. Three developments are redefining competitive positioning.
Extended detection and response platforms are collapsing the traditional separation between endpoint, network, and identity monitoring. Mid-market enterprises are adopting these consolidated suites fastest, compressing vendor selection cycles from twelve-month evaluations to ninety-day pilots. Security teams are reallocating headcount from tool administration to threat hunting as platform automation absorbs tier-one alert triage.
The EU AI Act imposes algorithmic transparency requirements on automated threat detection systems used in critical infrastructure. Operators of essential services must document decision logic for AI-driven containment actions to satisfy national regulator audits. German energy utilities and French healthcare providers are investing in explainable AI modules to preserve automated response speed while meeting documentation mandates.
Retainer-to-engagement conversion models are reshaping how enterprises procure incident response capabilities. Fixed-fee retainers with defined response time guarantees are displacing hourly consulting arrangements, particularly among publicly traded companies facing SEC disclosure pressure. This shift is most pronounced in United Kingdom financial services, where boards are pre-approving crisis response budgets to eliminate procurement delays during active breaches.
Cyber Crisis Management Market Segmentation
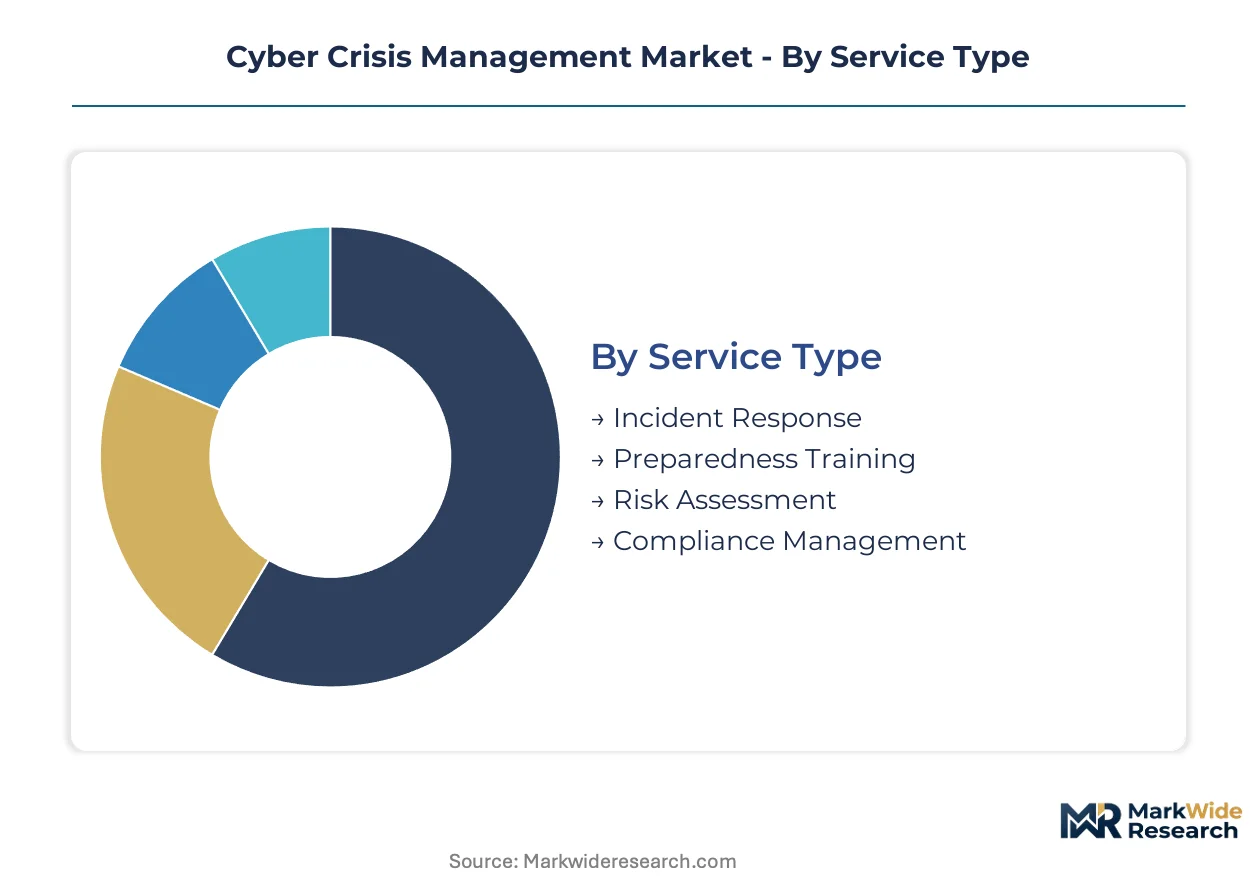
Segmentation in cyber crisis management reveals how procurement cycles, regulatory mandates, and technical architectures reshape vendor-client relationships. Service type determines contract renewal velocity. Deployment model dictates infrastructure overhaul timelines. Understanding these divisions exposes where margin concentrates and where commodification threatens pricing power.
Service Type:
Incident response contracts convert from retainer to active engagement fastest, while compliance management cycles stretch across multi-year audit calendars. Preparedness training sits between these extremes with annual renewal patterns tied to regulatory exercise mandates.
- Incident Response:Active breach containment and forensic investigation services triggered under pre-negotiated retainers. Financial institutions in the United Kingdom and Germany convert these fastest under SEC and NIS2 disclosure pressure. Contract velocity accelerates as four-day notification windows compress procurement decisions.
- Preparedness Training:Tabletop exercises and crisis simulation protocols delivered through recurring workshops. Mid-market retailers in France lag adoption despite ANSM and CNIL guidance, creating expansion headroom as supervisors mandate documented rehearsal protocols.
- Risk Assessment:Vulnerability scanning and threat landscape evaluation services preceding policy underwriting. ISO 27035 alignment requirements tighten scope definitions.
- Compliance Management:Continuous audit preparation and regulatory documentation maintenance spanning GDPR, NIS2, and sector-specific mandates. Energy utilities stretch procurement cycles across three-year regulatory intervals.
Incident response dominates installed base. Preparedness training is where expansion concentrates.
Deployment Model:
Cost tier separation runs from capital-intensive on-premises builds through variable-cost cloud subscriptions to premium managed service fees. Hybrid deployments capture mid-tier budgets seeking staged migration paths.
- Cloud-Based:SaaS-delivered detection platforms with API-native orchestration and elastic compute scaling. Distributed workforces across United States technology firms eliminate perimeter chokepoints fastest here. Procurement cycles compress from twelve-month evaluations to ninety-day pilots.
- Managed Services:Fully outsourced security operations with defined recovery time objectives and staffing guarantees. Healthcare providers in Germany adopt these under BSI and regional hospital association pressure to address certified responder scarcity.
- On-Premises:Air-gapped or sovereign-hosted infrastructure for classified or critical control system environments. Defense contractors and nuclear operators sustain this model despite higher total cost of ownership.
- Hybrid:Segmented architecture with sensitive workloads on-premises and commodity detection in cloud. Mid-market enterprises favor this for staged zero-trust migration without full infrastructure replacement.
On-premises retains highest customer lifetime value. Cloud-based deployments are climbing the fastest as remote workforce architectures normalize.
End User:
Application severity separates these segments: financial services face continuous active threat exposure, while healthcare contends with legacy system fragility and patient safety consequences.
- Financial Institutions:Banks, insurers, and payment processors with SEC four-day disclosure mandates and systemic risk oversight. United States and United Kingdom firms expand retainer coverage fastest under supervisory pressure.
- Healthcare Providers:Hospitals, clinics, and health systems managing HIPAA obligations and medical device vulnerability. German university hospitals and French public health networks invest in AI-enhanced forensics for ransomware recovery.
- Government Agencies:Civilian and defense departments with classified information handling and supply-chain security mandates. NIS2 critical infrastructure classification expands procurement scope.
- Retailers:Physical and digital commerce operators with payment card industry compliance and customer data exposure risks. Mid-market penetration remains underdeveloped relative to mandated exercise requirements.
Financial institutions dominate active engagement revenue. Healthcare providers represent the steepest expansion trajectory as medical device connectivity multiplies attack surfaces.
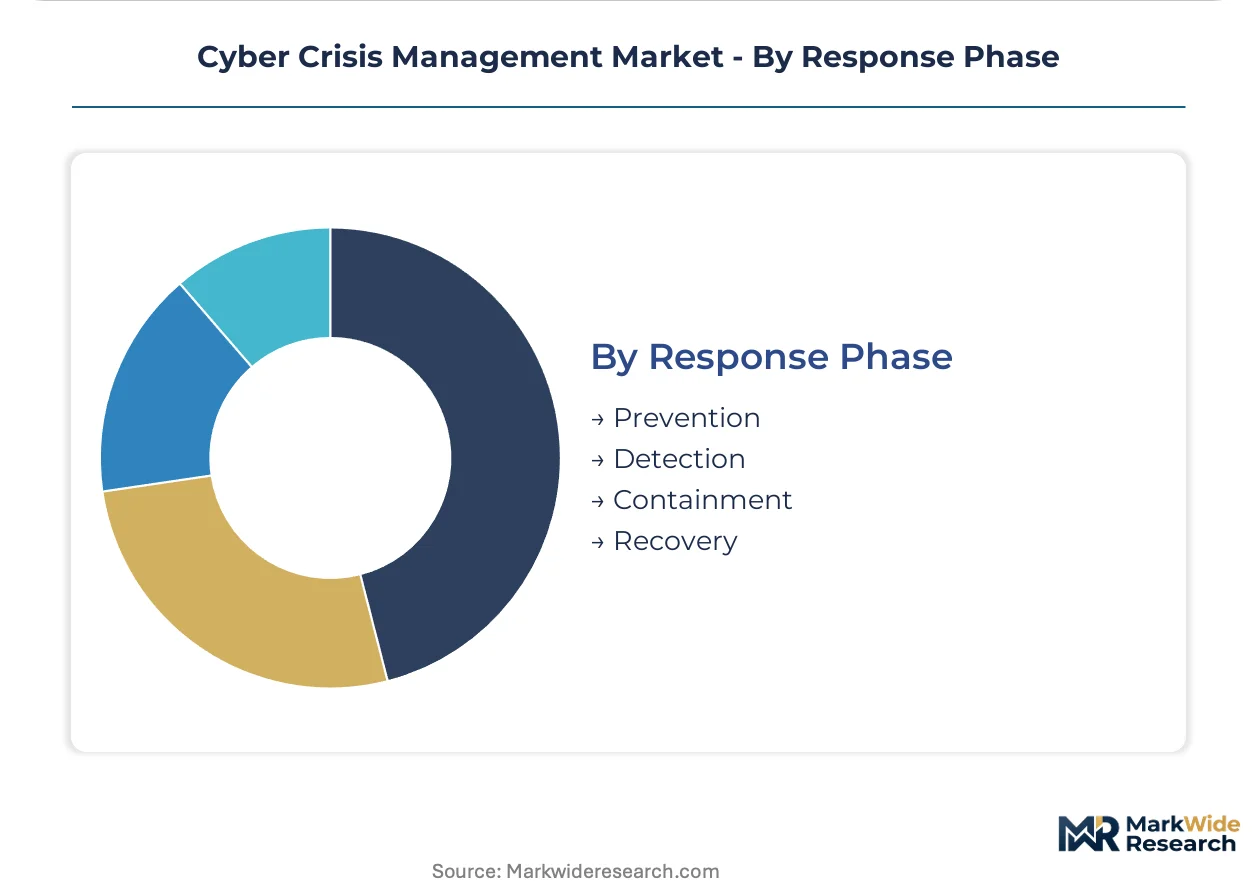
Response Phase:
Maturity gradient separates prevention investments (long-established, budgeted annually) from recovery services (emerging, outcome-priced, margin-rich).
- Detection:Real-time monitoring and alert correlation across endpoint, network, and identity layers. Extended detection and response platforms consolidate this phase fastest among mid-market enterprises.
- Containment:Automated isolation protocols and lateral movement blocking with legal privilege preservation. EU AI Act transparency requirements reshape tooling for critical infrastructure operators.
- Prevention:Perimeter hardening, access controls, and vulnerability management preceding any incident. Sunk-cost legacy investments here create migration friction toward zero-trust architectures.
- Recovery:System restoration, data integrity verification, and business continuity execution post-containment. Post-breach remediation services extend into recurring revenue streams beyond initial crisis response.
Prevention commands largest historical spend share. Recovery is gaining share fastest as outcome-based pricing and long-term remediation contracts displace hourly consulting.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States-based cyber crisis management vendors export incident response services to financial institutions across the United Kingdom and Germany. Cross-border retainer contracts accelerate as SEC disclosure mandates synchronize with EU NIS2 notification windows.
United States
Financial institutions in New York and California expand incident response retainers under SEC four-day disclosure mandates. The Federal Reserve coordinates with state regulators to enforce operational resilience standards for systemically important banks. Silicon Valley technology firms pilot cloud-native detection platforms with ninety-day procurement cycles.
Germany
Energy utilities and automotive manufacturers invest in automated containment protocols under BSI critical infrastructure classifications. The EU NIS2 Directive mandates supply-chain security documentation for operators of essential services. Munich and Frankfurt anchor the largest concentration of managed security service providers serving DAX-listed corporations.
United Kingdom
London-based insurers and investment banks pre-approve crisis response budgets to eliminate procurement delays during active breaches. The Financial Conduct Authority enforces operational resilience rules with March 2025 compliance deadlines. The Thames Valley corridor hosts specialized forensic consulting clusters serving FTSE 100 firms.
France
Healthcare providers in Paris and Lyon deploy AI-enhanced forensics for ransomware recovery under ANSM medical device security guidance. The CNIL coordinates with EU AI Act transparency requirements for automated threat detection. Mid-market retailers in the Île-de-France region lag in tabletop exercise adoption despite supervisor mandates.
Japan
Tokyo-based financial conglomerates integrate incident response platforms with METI cybersecurity framework requirements. The country's national financial regulator mandates supply-chain risk assessments for critical technology vendors. Osaka manufacturing clusters invest in hybrid deployment models for staged zero-trust migration.
Cyber Crisis Management Market Competitive Environment
Channel-controlling players compete with product-specialist players across three distinct tiers. Consolidation pressures intensify as extended detection and response platforms absorb standalone point solutions. Strategic archetypes separate into integrated platform consolidators, native endpoint specialists, and consulting-led remediation providers. Dominant competitive moves include M&A for threat intelligence assets and strategic partnerships for cloud-native orchestration capabilities.
Within the integrated platform tier, Palo Alto Networks and Cisco Systems exemplify channel-controlling positions through consolidated security stacks. CrowdStrike occupies a specialist position exemplifying native endpoint detection with embedded intelligence. These three anchors represent how vendor selection cycles compress from twelve-month evaluations to ninety-day pilots as platform automation absorbs tier-one alert triage.
| Leading Market Players |
|---|
| Fortinet |
| IBM Security |
| Palo Alto Networks |
| SentinelOne |
| Trellix |
| CrowdStrike |
| Cisco Systems |
| Check Point Software Technologies |
| Microsoft Security |
| Others |
Value Chain & Pricing Dynamics
Concentration of certified incident responders in the United States and United Kingdom creates margin asymmetry between retainer pricing and active breach engagement rates. Platform vendors with captive threat intelligence feeds extract premium SaaS pricing from financial institutions facing SEC disclosure deadlines.
Pricing Analysis
Next-generation AI-enhanced forensics platforms command 40-60% subscription premiums over legacy signature-based detection tools. Three-tier pricing structure across enterprise, mid-market, and managed service tiers reflects ISO 27035 certification requirements and response time guarantees. Pricing pressure stems from cloud-native entrants compressing pilot-to-deployment cycles from twelve months to ninety days. Mid-market retailers exhibit highest price sensitivity due to unmandated tabletop exercise budgets, while systemically important banks accept premium retainer rates for sub-four-hour response commitments.
Supply Chain Analysis
Supply-chain finance facilities from Palo Alto Networks and CrowdStrike extend payment terms to channel partners, tightening distributor liquidity for smaller platform vendors. Critical threat intelligence feeds concentrate in the United States, Israel, and United Kingdom, with raw data sourcing from dark web monitoring, honeypot networks, and government CERT partnerships. Single-source vulnerability in specialized forensic hardware creates procurement risk for air-gapped deployments. Distribution runs through value-added resellers serving regulated verticals, direct enterprise sales for cloud-native platforms, and managed security service providers addressing certified responder scarcity.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a defensive-moat business where regulatory entrenchment protects incumbent positions. Switching costs escalate as crisis playbooks integrate with client-specific compliance documentation and legal privilege protocols.
For Market Incumbents: Entrench platform consolidation advantages by acquiring niche threat intelligence assets and embedding automated containment with legal privilege preservation. Cloud-native entrants with ninety-day deployment cycles threaten retainer-to-engagement conversion rates. Vertical integration into sovereign-hosted infrastructure addresses German BSI and French ANSM data residency requirements. For New Entrants and Emerging Players: Build out mid-market retail penetration where tabletop exercise mandates outpace vendor supply. French Île-de-France retailers and German mid-tier automotive suppliers represent the most penetrable segments. Go-to-market execution should anchor on channel partnerships with existing compliance consulting firms rather than direct sales overhead. For Investors and Strategic Acquirers: Capital-intensity ratios are inflecting upward across AI-enhanced forensics sub-segments as explainable AI documentation requirements expand engineering headcount. Long-term viability favors platforms with embedded threat intelligence and automated response orchestration. Acquisition targets should demonstrate NIS2-aligned compliance documentation and active engagements in United Kingdom financial services. The signal to watch is retainer-to-engagement conversion velocity as SEC disclosure windows compress procurement decisions.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Palo Alto Networks consolidates detection-to-response latency for Fortune 500 CISOs. |
| Acquisition of Specialist Firm | Threat intelligence assets anchor differentiated pricing in retainer negotiations. |
| Strategic Partnership | Cloud-native orchestration partnerships address distributed workforce security gaps. |
| Geographic Expansion | German energy utilities demand BSI-compliant automated containment protocols. |
| Product Launch | Explainable AI modules satisfy EU AI Act transparency mandates for critical infrastructure. |
Study Parameters
Initial hypotheses were tested against primary input from CISOs, incident response directors, regulatory compliance officers, and cyber insurance underwriters and refined through secondary validation. Primary fieldwork encompassed structured interviews across financial services, healthcare, and critical infrastructure operators in the United States, Germany, United Kingdom, and France. Secondary sources included SEC disclosure filings, EU NIS2 implementation guidance, ISO 27035 certification databases, and cyber insurance policy term sheets. Bottom-up service revenue estimates and top-down market sizing were triangulated against platform vendor booking disclosures.
Demand-supply balance modeling anchored forecast construction across the projection horizon. Segmentation dimensions encompassed service type, deployment model, end-user vertical, and response phase maturity. CAGRs were derived from fitted growth curves against historical retainer conversion patterns and regulatory mandate implementation timelines. Industry-specific inputs included NIS2 supply-chain security obligation rollout schedules and SEC four-day disclosure compliance rates among S&P 500 constituents.
Sensitivities concentrate around EU AI Act enforcement intensity and certified responder labor supply elasticity. Forecasts embed assumptions regarding regulatory harmonization between SEC and EU notification windows. Macroeconomic, regulatory, or technological deviation would prompt revision.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Emergency and Disaster Management
Advanced Disaster Management Simulator Market
Emergency and Disaster Management
Emergency Lighting Market
Emergency and Disaster Management
Disaster Restoration Services Market
Emergency and Disaster Management
Lifeboat Market
Emergency and Disaster Management
Asia-Pacific Process Safety Services Market
Emergency and Disaster Management
Emergency and Disaster Response Market
Emergency and Disaster Management
Emergency Blankets Market
Emergency and Disaster Management
EHS Market
Emergency and Disaster Management
Emergency Location Transmitter Market
Emergency and Disaster Management
Automatic Floodgate Market
Emergency and Disaster Management
Free Fall Lifeboats Market
Emergency and Disaster Management
Hazard Control Market
Emergency and Disaster Management
North America Emergency Shower and Eye Wash Station Market
Emergency and Disaster Management
North America Homeland Security and Emergency Management Market
Emergency and Disaster Management
Incident and Emergency Management Market
Emergency and Disaster Management
Crisis Emergency and Incident Management Platform Market