
 Cyber Attack Simulation Software Market | 2026-2036
Cyber Attack Simulation Software Market Size, Share, and Industry Trends Forecast 2026-2036
Cyber Attack Simulation Software Market Analysis
The certified red-team talent pool is rotating toward automated simulation platforms as enterprises face persistent shortages of offensive security practitioners. AttackIQ leverages continuous validation architectures to anchor its position among Fortune 500 defenders. Cymulate competes through modular threat exposure management that extends across email, endpoint, and cloud attack paths. SafeBreach specializes in breach method libraries spanning hundreds of attacker techniques, sustaining R&D intensity that differentiates its offering from commodity scanning tools.
Cyber attack simulation software orchestrates controlled adversary emulations against production infrastructure to quantify defensive control efficacy without operational disruption. These platforms execute native attack techniques—lateral movement, credential dumping, and payload delivery—through read-only or low-impact agents that map exploit paths while preserving system stability. Cloud-based deployment models lead current uptake among mid-market buyers seeking elastic compute for large-scale simulations, while hybrid architectures capture margin pools from regulated enterprises requiring on-premises data sovereignty. The financial services end-user segment dominates absolute spending as institutions operationalize frameworks like NIST SP 800-53 and PCI-DSS 4.0 through automated control validation.
The National Institute of Standards and Technology, the European Union Agency for Cybersecurity, and the Payment Card Industry Security Standards Council shape demand through mandatory control-testing intervals and attestation requirements. ENISA's Cybersecurity Act and emerging EU critical infrastructure directives compel operators of essential services to adopt continuous validation regimes, tightening procurement specifications for simulation vendors. Stakeholders must monitor convergence between attack simulation and cyber insurance underwriting, as carriers increasingly mandate automated breach evidence for policy pricing and renewal decisions.
Market Dynamics
Continuous validation architectures are displacing point-in-time penetration testing across enterprise security operations, compressing assessment cycles from annual audits to weekly or daily automated emulations that quantify control efficacy against live attacker techniques.
Growth Catalysts
- NIST SP 800-53:Federal agencies and their contractors must operationalize automated control validation to satisfy mandatory assessment intervals, creating baseline procurement pull across defense and civilian sectors.
- Financial services stress-testing:The European Banking Authority mandates breach-and-attack simulation for operational resilience, compelling institutions to deploy continuous adversary emulation platforms.
- Cloud migration velocity:Elastic compute infrastructure enables large-scale parallel attack simulations without on-premises hardware constraints, accelerating mid-market adoption of SaaS-delivered validation tools.
Market Restraints
- Specialized talent scarcity:Certified red-team practitioners command premium compensation, constraining vendor expansion and enterprise self-managed deployment feasibility.
- Legacy system integration friction:Mainframe and operational technology environments resist agent-based simulation deployment, limiting addressable infrastructure scope.
- Data sovereignty requirements:Regulated enterprises in Germany, France, and Switzerland demand on-premises or sovereign cloud architectures, compressing margins relative to multi-tenant SaaS delivery.
Strategic Opportunities
- Critical infrastructure operators:EU Cybersecurity Act expansion compels energy, transport, and healthcare operators to adopt continuous validation regimes, opening new vertical segments.
- Cyber insurance underwriting convergence:Carriers increasingly mandate automated breach evidence for policy pricing, creating channel partnerships between simulation vendors and insurance brokers.
- API security integration:Convergence between attack simulation and API posture management enables unified validation of cloud-native application attack surfaces.
Industry Challenges
- Attacker technique currency:Vendors must sustain R&D intensity to maintain exploit libraries against evolving adversary tradecraft, compressing product lifecycles.
- Production environment safety:Read-only agent architectures require sophisticated orchestration to prevent operational disruption, elevating engineering complexity and support costs.
- Attribution and evidence standards:Forensic admissibility requirements for simulation-generated breach evidence vary across jurisdictions, complicating cross-border deployment.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cyber Attack Simulation Software Market |
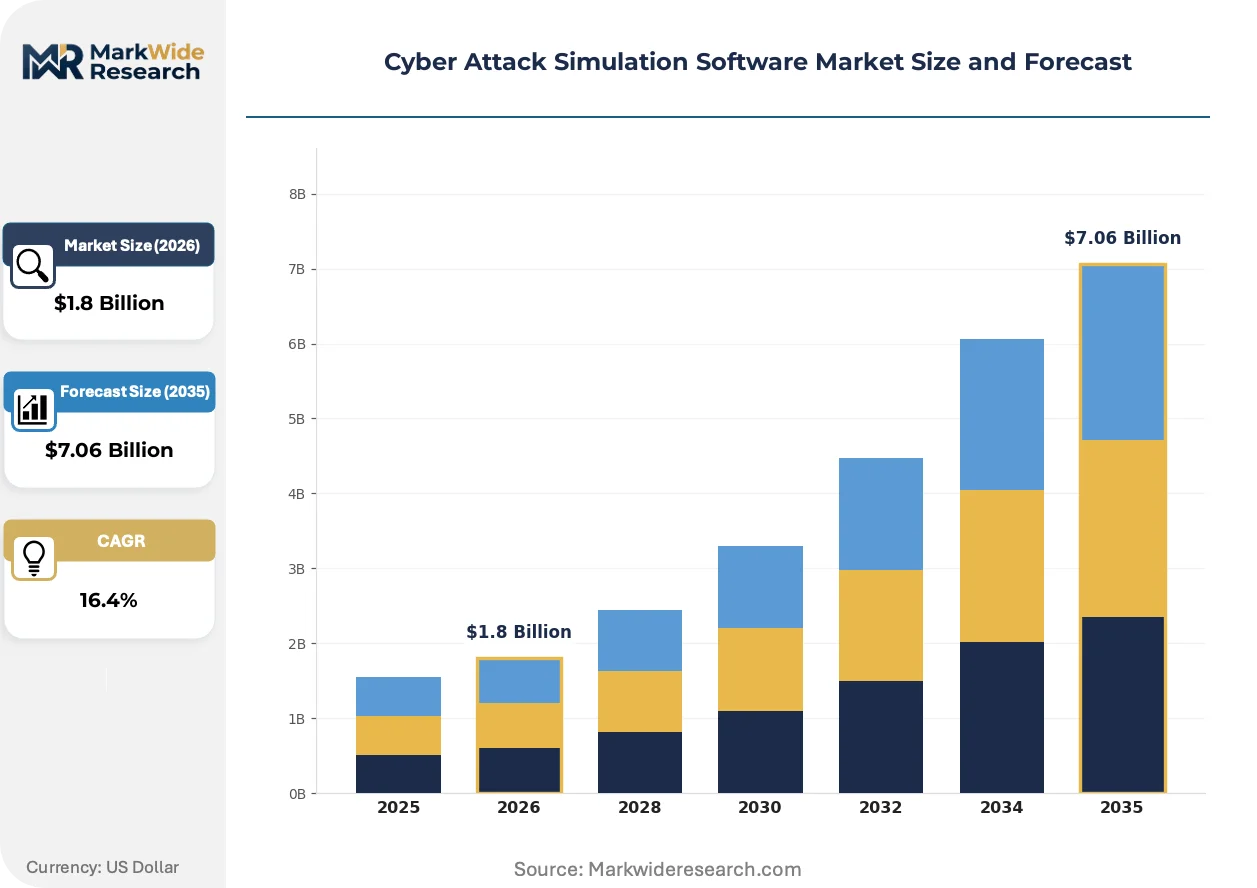
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $7.06 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Cloud-Based, On-Premises, Hybrid, Open-Source End User: Government, Financial Services, Healthcare, Education Deployment Model: Infrastructure, Platform, Software, Managed Services Feature: Real-Time Alerts, Phishing Simulation, Vulnerability Assessment, Analytics Dashboard |
| Companies Covered | AttackIQ, Cymulate, XM Cyber, SafeBreach, Picus Security, Rapid7, Pentera, Keysight Technologies, Mandiant, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cyber Attack Simulation Software Market Emerging Trajectories
Agentless reconnaissance and ephemeral infrastructure emulation are compressing deployment timelines while expanding simulation scope to encompass supply chain and third-party attack paths previously invisible to perimeter-focused testing.
Agentless breach simulation is displacing persistent endpoint agents in cloud-native environments. DevSecOps teams at SaaS providers now deploy ephemeral attack containers that execute adversary techniques without permanent infrastructure footprint. This architecture eliminates agent maintenance overhead while enabling continuous validation of containerized workloads and serverless functions.
The EU AI Act and emerging algorithmic accountability requirements are reshaping procurement specifications for automated security tools. Financial institutions in Frankfurt, Paris, and Amsterdam now demand explainable attack path reporting to satisfy model risk management frameworks. Vendors are responding with deterministic rule engines that supplement machine-learning prioritization with auditable decision trails.
Security procurement committees are consolidating vendor relationships around integrated threat exposure management platforms. CISOs at Fortune 500 manufacturers are replacing standalone penetration testing contracts with multi-year simulation subscriptions that bundle continuous validation, attack surface management, and control gap remediation. This concentration is most visible in US industrial conglomerates with distributed operational technology footprints.
Cyber Attack Simulation Software Market Segmentation
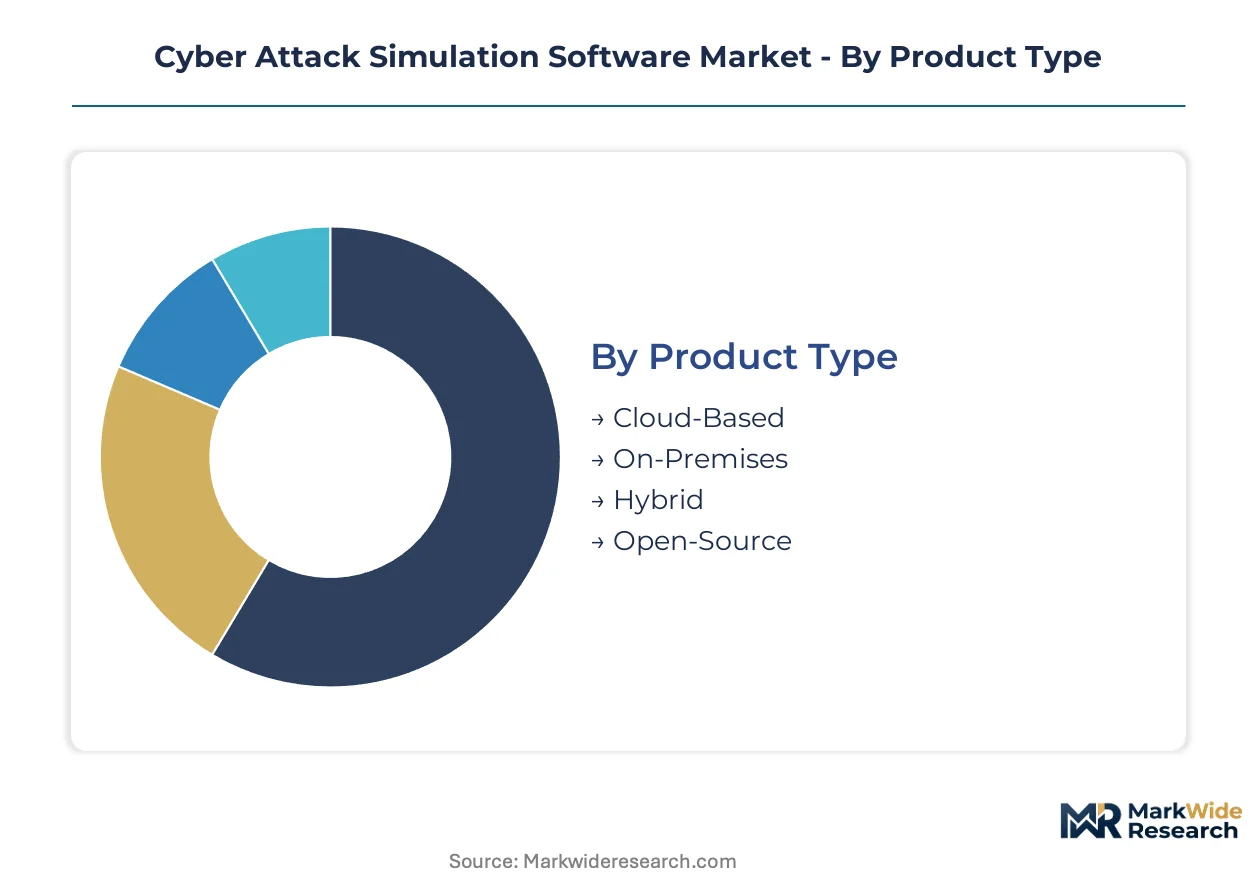
Segmentation in cyber attack simulation software reveals how procurement committees prioritize control validation architectures. Buyers distinguish platforms by deployment sovereignty, operational tempo, and integration depth with existing security stacks.
Product Type:
Cloud-based offerings face substitution pressure from hybrid architectures as regulated enterprises reclaim data sovereignty without sacrificing elastic compute.
- Cloud-Based:Multi-tenant SaaS architectures deliver elastic compute for parallel attack emulations without hardware procurement cycles. Financial services institutions in Singapore and the Netherlands favor this model for rapid deployment of continuous validation programs. The European Banking Authority's operational resilience deadlines compress procurement timelines toward cloud-native solutions.
- On-Premises:Air-gapped deployments satisfy data residency mandates from Germany's BSI and France's ANSSI for critical infrastructure operators. Sovereign cloud requirements in Switzerland and Austria sustain demand despite higher total cost of ownership. Engineering complexity elevates support costs relative to SaaS alternatives.
- Hybrid:Split architectures partition sensitive control validation on-premises while routing non-critical simulations to public cloud. Energy sector operators in Norway and Denmark deploy this model to protect SCADA telemetry.
- Open-Source:Community-maintained frameworks like Atomic Red Team and Caldera attract resource-constrained security teams at mid-market manufacturers. Limited commercial support constrains enterprise adoption.
Cloud-based deployments anchor the volume base while hybrid architectures gain share at the steepest rate.
End User:
Cost tier segmentation separates enterprise-grade platforms from scaled-down offerings as budget authority fragments across CISO and CIO functions.
- Government:Federal agencies and defense contractors mandate FedRAMP-authorized platforms with immutable audit trails. NIST SP 800-53 control validation requirements sustain multi-year procurement cycles. The US Cybersecurity and Infrastructure Security Agency shapes technical specifications through continuous diagnostics and mitigation programs.
- Financial Services:Banks, insurers, and payment processors deploy breach-and-attack simulation to satisfy PCI-DSS 4.0 and operational resilience stress-testing. The European Banking Authority's mandates in Frankfurt, Paris, and Milan accelerate platform consolidation.
- Healthcare:Hospital systems and pharmaceutical manufacturers validate HIPAA technical safeguards against ransomware attack chains. FDA cybersecurity guidance for medical devices extends simulation scope to embedded systems.
- Education:University research networks and K-12 districts adopt open-source or subsidized platforms to protect dispersed endpoint populations. Limited security staffing favors managed service overlays.
Financial services anchors the volume base while healthcare gains share at the steepest rate.
Deployment Model:
Application-centric segmentation tracks how DevSecOps teams integrate validation into CI/CD pipelines versus security operations center workflows.
- Infrastructure:Bare-metal and virtualized deployments target air-gapped environments in defense and intelligence communities. Hardware sovereignty requirements in Israel and South Korea sustain this segment despite operational friction.
- Platform:Container-native simulation executes adversary techniques against Kubernetes and serverless workloads without persistent agents. SaaS providers in Bangalore and Tel Aviv favor this model for continuous deployment velocity.
- Software:Traditional licensed deployments persist in industrial conglomerates with legacy ERP integration requirements. Perpetual licensing contracts complicate vendor transition.
- Managed Services:Third-party security providers operate simulation platforms on behalf of resource-constrained mid-market enterprises. MSSP partnerships in Canada and Australia expand addressable market reach.
Platform deployments anchor the volume base while managed services gain share at the steepest rate.
Feature:
Customer type segmentation distinguishes buyers prioritizing real-time operational tempo from those demanding forensic depth and compliance documentation.
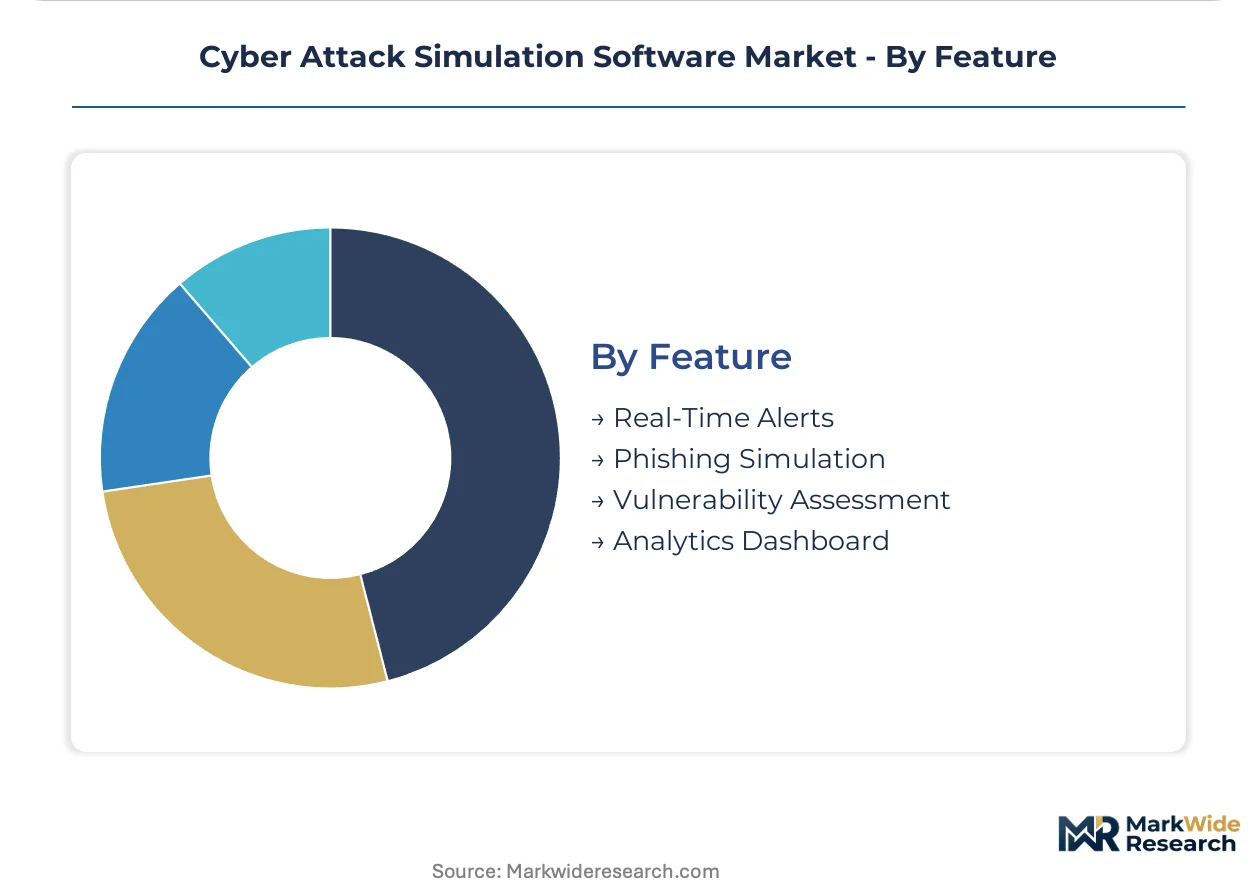
- Real-Time Alerts:Sub-second detection validation feeds security orchestration platforms for automated response playbook triggering. SOC teams at telecommunications operators in Spain and Italy prioritize this capability.
- Phishing Simulation:Controlled email attack campaigns measure user susceptibility and email gateway efficacy. Human risk quantification satisfies cyber insurance evidence requirements.
- Vulnerability Assessment:Integrated exploit verification distinguishes patchable weaknesses from theoretical CVE entries. Prioritization engines align remediation with business-critical asset exposure.
- Analytics Dashboard:Executive visualization layers translate technical control gaps into board-ready risk metrics. CISO reporting obligations under SEC disclosure rules elevate procurement priority.
Analytics dashboards anchor the volume base while real-time alerts gain share at the steepest rate.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The European Banking Authority anchors the dominant geography through operational resilience mandates that compel financial institutions to deploy continuous adversary emulation platforms. Regulators across multiple jurisdictions are tightening control-testing intervals, reshaping procurement patterns for breach-and-attack simulation vendors.
United States
Federal agencies and defense contractors mandate FedRAMP-authorized platforms with immutable audit trails. NIST SP 800-53 control validation requirements sustain multi-year procurement cycles across defense and civilian sectors. The US Cybersecurity and Infrastructure Security Agency shapes technical specifications through continuous diagnostics and mitigation programs centered in Washington DC and Northern Virginia.
Germany
Critical infrastructure operators demand air-gapped deployments satisfying data residency mandates from Germany's BSI. Sovereign cloud requirements sustain demand for on-premises architectures despite higher total cost of ownership. Engineering teams in Munich and Frankfurt operationalize automated control validation for industrial conglomerates with distributed operational technology footprints.
United Kingdom
Financial institutions in London deploy breach-and-attack simulation to satisfy operational resilience stress-testing frameworks. The Bank of England's supervisory expectations accelerate platform consolidation among major banks and insurers. CISOs at Canary Wharf headquarters replace standalone penetration testing contracts with multi-year simulation subscriptions bundling continuous validation.
Singapore
Financial services institutions favor multi-tenant SaaS architectures for rapid deployment of continuous validation programs. The Monetary Authority of Singapore's technology risk management guidelines compress procurement timelines toward cloud-native solutions. Regional headquarters in Marina Bay deploy elastic compute for parallel attack emulations without hardware procurement cycles.
Israel
SaaS providers in Tel Aviv favor container-native simulation executing adversary techniques against Kubernetes and serverless workloads. Hardware sovereignty requirements sustain infrastructure deployments despite operational friction. DevSecOps teams deploy ephemeral attack containers that execute adversary techniques without permanent infrastructure footprint.
Cyber Attack Simulation Software Market Vendor Landscape
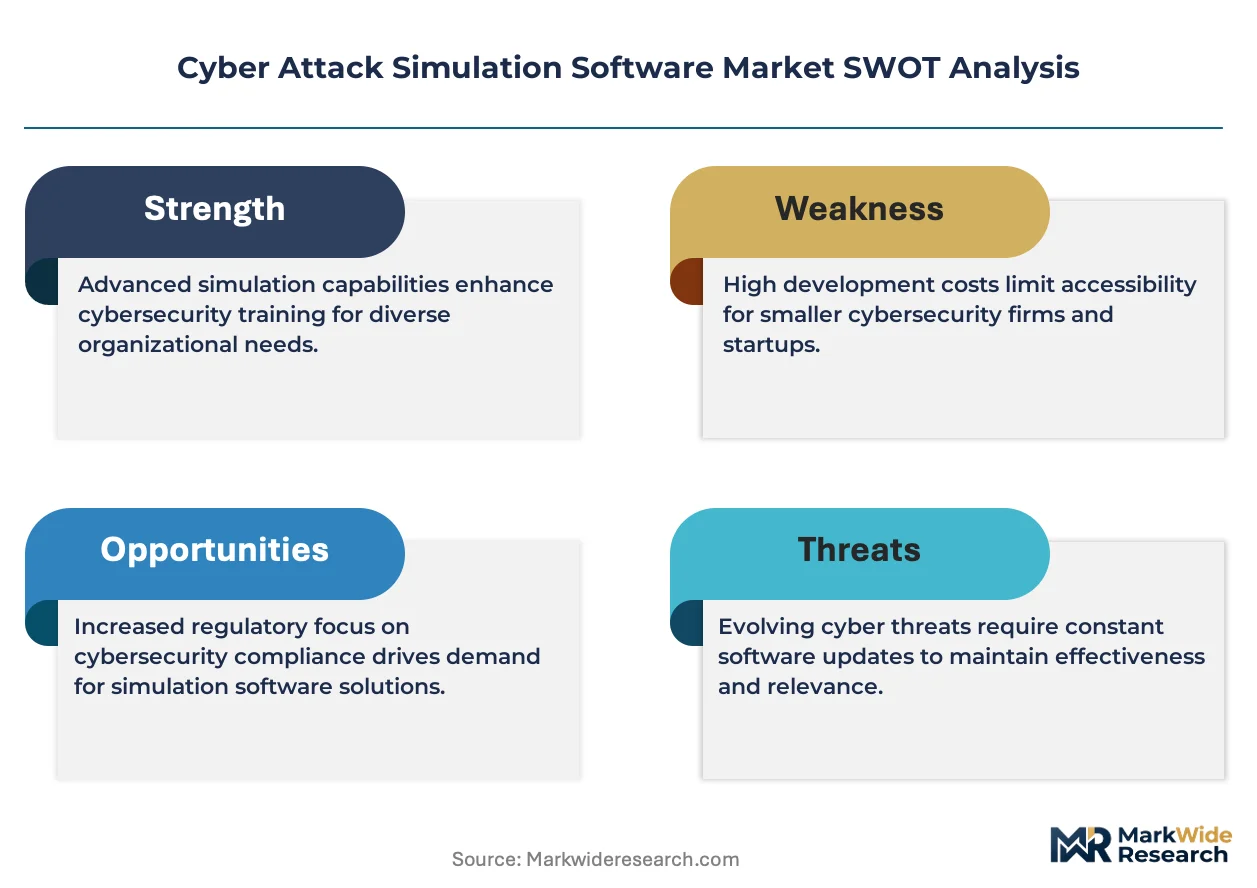
A small set of integrated leaders sits above a broader specialist tier, creating a two-tier structure where scale and R&D intensity separate the top performers from commodity scanning tools. The upper tier concentrates continuous validation architectures and modular threat exposure management capabilities. Strategic archetypes include platform-integrated suites, point-solution specialists, and managed security service overlays. Competitive moves center on API security integration and cyber insurance underwriting partnerships.
Within the continuous validation tier, AttackIQ and Cymulate exemplify divergent architectural philosophies. AttackIQ anchors its position through automated adversary emulation deployed across Fortune 500 infrastructure. Cymulate occupies a position emphasizing modular threat exposure management extending across email, endpoint, and cloud attack paths. SafeBreach represents the specialized library approach, sustaining differentiation through intensive R&D in breach method collections spanning hundreds of attacker techniques.
| Leading Market Players |
|---|
| AttackIQ |
| Cymulate |
| XM Cyber |
| SafeBreach |
| Picus Security |
| Rapid7 |
| Pentera |
| Keysight Technologies |
| Mandiant |
| Others |
Supply Flow & Price Mechanics
Ninety-day implementation cycles for on-premises deployments concentrate pricing power with vendors possessing FedRAMP and BSI certifications, while SaaS delivery compresses margins through elastic compute commoditization. Procurement committees weigh data sovereignty premiums against subscription elasticity, reshaping supplier selection across financial services and critical infrastructure verticals.
Pricing Analysis
Annual contract values diverge by a factor of three between North American SaaS buyers and European on-premises adopters facing BSI and ANSSI data residency mandates. Three-tier pricing structure across premium, standard, and economy levels segments by deployment sovereignty, integration depth, and managed service overlays. Pricing pressure stems from open-source alternatives like Atomic Red Team and Caldera attracting mid-market manufacturers with limited security staffing. Government and financial services buyers exhibit lowest price sensitivity due to regulatory compliance imperatives, while education and mid-market manufacturing segments drive hardest bargain.
Supply Chain Analysis
Certification bottlenecks at FedRAMP-authorized facilities and BSI-accredited data centers in Germany constrain vendor expansion velocity. Engineering talent concentrates in Israel, the United States, and Estonia, with adversary technique research anchored in Tel Aviv and Northern Virginia clusters. Raw material inputs comprise cloud compute credits from AWS, Azure, and GCP; threat intelligence feeds from Mandiant and Recorded Future; and red-team practitioner labor pools. Single-source vulnerability sits with hyperscaler dependency for elastic simulation infrastructure. Distribution runs through direct enterprise sales teams, MSSP partnerships, and cyber insurance broker channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Platform economics now govern competitive outcomes as CISOs consolidate vendor relationships around integrated threat exposure management suites bundling continuous validation, attack surface management, and control gap remediation. Interoperability with security orchestration platforms and SIEM architectures determines procurement survival.
For Market Incumbents: Shield market position through R&D intensity in adversary technique libraries and API security integration, countering open-source substitution pressure from Atomic Red Team and Caldera. Deepen vertical integration into threat intelligence feeds and managed service delivery to capture margin pools from resource-constrained mid-market enterprises. FedRAMP and BSI certification maintenance constitutes essential defensive moat. For New Entrants and Emerging Players: FedRAMP-Moderate fast-track authorization opens federal agency procurement channels currently dominated by AttackIQ and SafeBreach. Target healthcare verticals facing FDA cybersecurity guidance for medical devices, where simulation scope expansion to embedded systems remains underpenetrated. Pursue channel partnerships with cyber insurance brokers mandating automated breach evidence for policy pricing. For Investors and Strategic Acquirers: Carve-out targets emerge from industrial conglomerates divesting non-core cybersecurity units with established operational technology simulation capabilities. Long-term viability hinges on convergence between attack simulation and cyber insurance underwriting workflows. Monitor API security integration announcements as inflection indicator for platform consolidation momentum.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Convergence with SIEM and SOAR architectures determines enterprise procurement survival against point solutions. |
| Strategic Partnership | Cyber insurance broker alliances create distribution channels for automated breach evidence requirements. |
| Acquisition of Specialist Firm | API security posture management capabilities extend simulation scope to cloud-native application attack surfaces. |
| Product Launch | Agentless ephemeral container architectures eliminate maintenance overhead for DevSecOps continuous deployment. |
| Geographic Expansion | FedRAMP and BSI certification investments unlock federal and German critical infrastructure procurement channels. |
Methodological Framework
Two parallel data streams informed the analysis: structured primary interviews with CISOs, security operations directors, cyber insurance underwriters, and MSSP platform engineers; and secondary validation across SEC 10-K cybersecurity disclosures, FedRAMP authorization databases, ENISA threat landscape reports, and cyber insurance policy filings. Bottom-up triangulation across deployment model adoption curves and top-down reconciliation with regulatory mandate timelines anchored market sizing.
Across the analysis window, the forecasting framework modeled deployment model, organization size, vertical industry, integration complexity, and regional adoption pattern dimensions. CAGRs derived from elasticity-adjusted penetration curves and regulatory deadline clustering. Inputs included European Banking Authority operational resilience implementation schedules, NIST SP 800-53 revision cycles, and hyperscaler capex trajectories for elastic compute infrastructure.
Underlying assumptions cover continuous validation displacement of point-in-time penetration testing, with deviation risk concentrated in legacy system integration friction and data sovereignty requirement tightening. Alternative scenarios remain live as ENISA Cybersecurity Act expansion timelines and EU AI Act algorithmic accountability enforcement evolve.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Asia-Pacific Smart Doorbell Market
Security Software
US and Latin America Identity and Access Management (IAM) Market
Security Software
Global Dynamic Application Security Testing Market
Security Software
Global Cloud IAM Market
Security Software
Cloud Identity and Access Management Software Market
Security Software
Security Information and Event Management Software Market
Security Software
Video Intercom Devices Market
Security Software
Enterprise Rights Management Solution Market
Security Software
Certification Authority Market
Security Software
E Passport Market
Security Software
Anti-Money Laundering (AML) Software Solution Market
Security Software
Anomaly Detection Market
Security Software
Identity-As-A-Service (Idaas) Market
Security Software
Embedded Security Market
Security Software
DC and PKI Market
Security Software
AI Security Platforms Market