
 Crowdsourced Security Market | 2026-2036
Crowdsourced Security Market Size, Share, and Industry Trends Forecast 2026-2036
Crowdsourced Security Market Analysis
GDPR enforcement is restructuring the cost-of-entry calculus for firms offering vulnerability disclosure services to European clients. HackerOne, Inc. leverages its FedRAMP authorization to anchor federal contracting workflows in the United States. Bugcrowd, Inc. competes through managed services that sustain enterprise-grade researcher vetting at scale. Synack, Inc. differentiates via its hybrid model combining crowdsourced talent with proprietary scanning technology.
Crowdsourced security mobilizes external researchers through structured bounty programs to identify and remediate software vulnerabilities before exploitation. Platforms typically integrate triage workflows, severity scoring against CVSS standards, and direct developer ticketing to compress mean-time-to-remediation. Cloud-based deployment dominates structural growth as enterprises reject on-premise orchestration overhead for elastic researcher access. Threat intelligence services represent the fastest-expanding segment as CISOs prioritize proactive adversary tracking over reactive patching cycles. Government agencies constitute a concentrated margin pool due to stringent clearance requirements and long-term contracting vehicles that limit vendor rotation.
FDA cybersecurity guidance for connected medical devices, SEC disclosure rules for material incidents, and EU AI Act conformity assessments collectively elevate third-party security validation from optional to mandatory spend. HIPAA breach notification timelines pressure healthcare providers to compress vulnerability discovery windows through external researcher pools. Stakeholders must weigh platform specialization against vertical coverage breadth as regulatory fragmentation deepens compliance complexity across jurisdictions.
Market Dynamics
Regulatory mandates across the United States, European Union, and select Asia-Pacific jurisdictions are converting voluntary bug bounty programs into mandatory procurement categories for critical infrastructure operators and regulated enterprises.
Growth Catalysts
- FedRAMP Authorization Requirements:United States federal agencies must source crowdsourced security exclusively through FedRAMP-authorized platforms, creating a protected demand pool for compliant vendors.
- EU AI Act Conformity Assessments:High-risk AI system deployers in Europe face mandatory third-party security validation, directly expanding vulnerability disclosure service contracts.
- Healthcare IoT Expansion:FDA cybersecurity guidance for connected medical devices compels manufacturers to maintain continuous external researcher engagement for pre-market and post-market surveillance.
Market Restraints
- Researcher Talent Scarcity:Elite vulnerability discovery skills concentrate in narrow geographic clusters, creating bidding wars that inflate platform operating costs.
- Data Sovereignty Friction:GDPR Article 44 cross-border transfer restrictions complicate researcher access to European enterprise environments from non-adequate jurisdictions.
- False Positive Triage Burden:Unvetted researcher submissions generate noise-to-signal ratios that strain internal security engineering capacity at client organizations.
Strategic Opportunities
- Operational Technology Convergence:Industrial control system operators in Germany and Japan represent an underpenetrated vertical requiring specialized ICS-focused researcher certification programs.
- Automated Remediation Orchestration:Platforms integrating crowdsourced findings directly into CI/CD pipelines via API-native ticketing compress client mean-time-to-remediation.
- SEC Cybersecurity Disclosure Rules:Material incident reporting requirements for US publicly traded companies elevate proactive vulnerability discovery from cost center to risk management essential.
Industry Challenges
- Clearance Bottlenecks:Government contracting workflows require security-cleared researcher pools that take 12-18 months to credential, constraining platform scalability.
- Intellectual Property Ambiguity:Vulnerability disclosure terms of service generate disputes over exploit ownership and coordinated disclosure timing between researchers and vendors.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Crowdsourced Security Market |
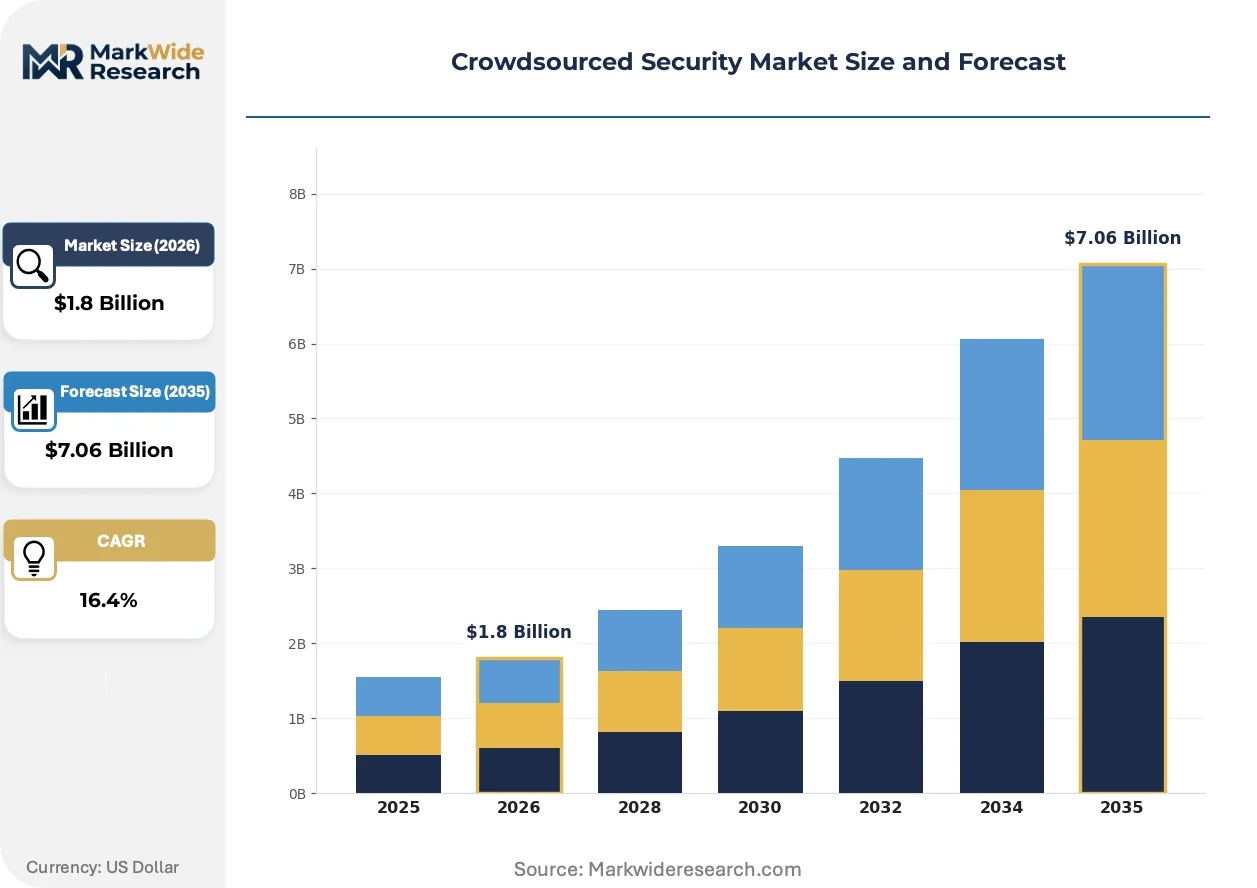
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $7.06 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Vulnerability Assessment, Penetration Testing, Incident Response, Threat Intelligence End User: SMBs, Enterprises, Government Agencies, Educational Institutions Deployment Model: On-Premise, Cloud-Based, Hybrid, Managed Services Application Type: Web Application Security, Mobile App Security, Infrastructure Protection, Compliance Monitoring |
| Companies Covered | Cobalt Security, Inc., Intigriti BV, HackerOne, Inc., Zerocopter NV, Detectify AB, Bugcrowd, Inc., YesWeHack SAS, Hacken OÜ, Synack, Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Crowdsourced Security Market Emerging Trajectories
Artificial intelligence is restructuring how crowdsourced security platforms match researcher expertise to target scope, compressing program launch timelines from weeks to hours.
Autonomous vulnerability scanning is overtaking manual reconnaissance as the dominant initial attack surface mapping methodology. Mid-market enterprises with limited security budgets adopt AI-augmented scanning to prioritize researcher attention on high-confidence findings. This compression of discovery phase timelines is overtaking traditional managed bug bounty program structures that relied on human-only triage workflows.
The EU AI Act's risk-based classification system imposes mandatory security testing obligations on providers of high-risk AI systems before market placement. European conformity assessment bodies now require documented vulnerability disclosure procedures as a condition of CE marking. Medical device manufacturers and financial services firms face the steepest compliance ramps, with many outsourcing entire program management to specialized platforms.
Enterprise buyers increasingly unbundle vulnerability discovery from full-service program management, preferring platform-as-a-service access to researcher networks with internal triage teams. This self-service model displaces traditional managed service contracts at technology companies with mature security operations centers. The shift is most pronounced in the United States, where CISOs cite cost transparency and researcher direct relationships as primary motivators.
Crowdsourced Security Market Segmentation
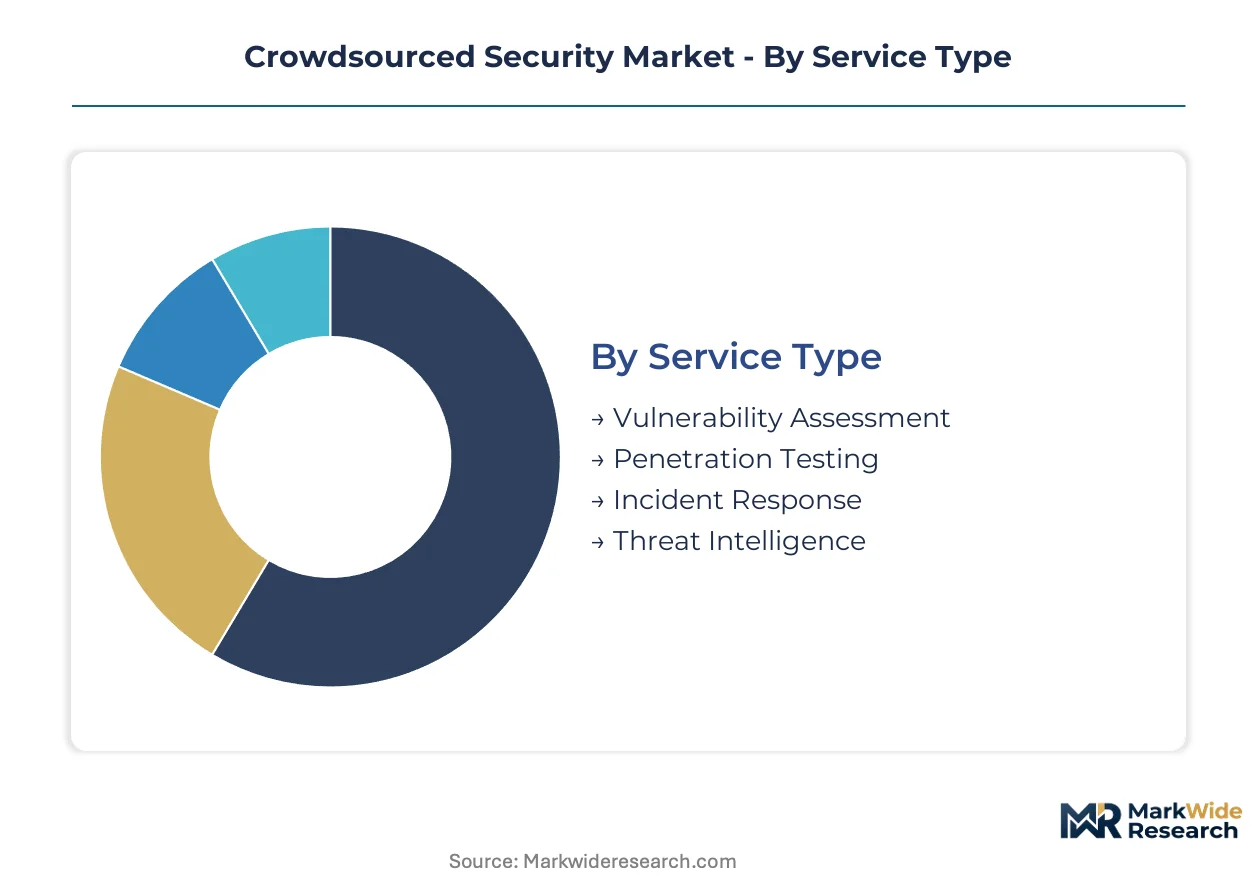
Segmentation in crowdsourced security reveals how procurement patterns split between integrated platform stacks and modular point solutions. Buyers with mature security operations centers favor unbundled researcher access, while compliance-driven organizations purchase full-service program management.
Service Type:
Standalone vulnerability discovery services operate independently of client security infrastructure, whereas embedded offerings integrate directly into existing SOC workflows and ticketing systems.
- Vulnerability Assessment:Systematic identification of security weaknesses across attack surfaces using crowdsourced researcher pools. Financial services firms in the United States deploy continuous assessment programs to satisfy SEC cybersecurity disclosure obligations. This segment commands the largest contract values due to recurring scope expansion.
- Threat Intelligence:Proactive adversary tracking and indicator-of-compromise feeds sourced from researcher-reported exploit techniques. European healthcare providers under EU AI Act conformity requirements purchase integrated threat intelligence to satisfy mandatory security validation. This service is displacing reactive patching cycles as CISOs prioritize predictive defense.
- Penetration Testing:Simulated attack exercises conducted by vetted external researchers against production environments.
- Incident Response:Rapid researcher mobilization during active breach scenarios to identify attack vectors and containment paths.
Vulnerability Assessment leads volumes today; Threat Intelligence is gaining share fastest.
End User:
Cost tier stratification separates buyers by security program maturity and available procurement budget rather than absolute organization size.
- Enterprises:Large organizations with dedicated CISO functions and multi-million-dollar security budgets. German automotive manufacturers and Japanese industrial conglomerates run persistent private bug bounty programs with exclusive researcher cohorts. These buyers drive platform R&D roadmaps through custom feature requests.
- Government Agencies:Federal, state, and municipal entities with classified or sensitive operational requirements. United States agencies mandate FedRAMP-authorized platforms, creating a protected contracting pool with 12-18 month researcher clearance timelines. Long-term contracting vehicles limit vendor rotation and concentrate margin.
- SMBs:Mid-market organizations purchasing standardized program templates with limited customization scope.
- Educational Institutions:Universities and research centers leveraging student researcher pools alongside commercial platforms.
Enterprises dominate revenue concentration; Government Agencies deliver the highest per-contract margins.
Deployment Model:
Volume distribution tracks enterprise cloud migration velocity and rejection of on-premise orchestration overhead.
- Cloud-Based:Elastic researcher access through browser-accessible platforms with API-native integrations. United States technology companies and European financial services firms prefer this model for rapid program launch without infrastructure procurement. Cloud deployment is displacing managed services at organizations with internal triage capacity.
- Managed Services:Full program administration including researcher vetting, triage, and remediation coordination. Healthcare providers under HIPAA breach notification pressure outsource entire vulnerability disclosure operations to compress discovery windows. This model sustains premium pricing through liability transfer.
- Hybrid:Split configurations with sensitive assets tested via on-premise researcher access and public-facing systems on cloud platforms.
- On-Premise:Self-hosted orchestration for air-gapped environments or strict data sovereignty requirements.
Cloud-Based deployment leads adoption today; Managed Services retains pricing power in regulated verticals.
Application Type:
Customer type differentiation separates buyers by primary asset class requiring protection and associated compliance framework.
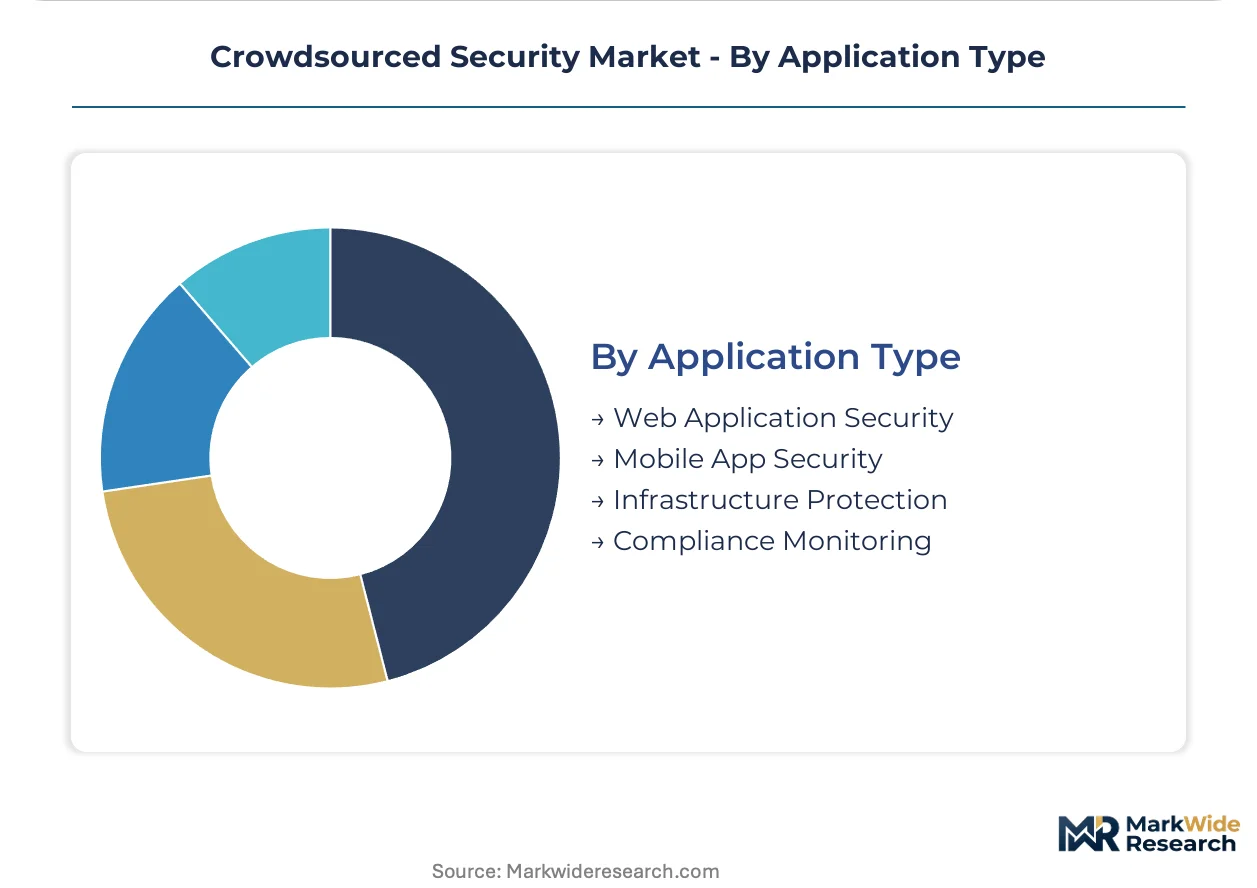
- Web Application Security:Continuous testing of public-facing web properties and APIs against OWASP Top 10 categories. E-commerce platforms and SaaS providers maintain persistent programs with rapid bounty escalation for critical findings. This application category generates the highest submission volumes due to broad attack surface exposure.
- Infrastructure Protection:Network perimeter and cloud configuration assessment through researcher-accessible scope definitions. Critical infrastructure operators in Germany and Japan adopt specialized ICS-focused certification programs for operational technology convergence. Regulatory mandates are converting voluntary programs into mandatory procurement categories.
- Mobile App Security:iOS and Android application testing including reverse engineering and runtime analysis.
- Compliance Monitoring:Continuous validation against regulatory frameworks including GDPR, EU AI Act, and SEC disclosure rules.
Web Application Security leads submission volumes; Infrastructure Protection shows the steepest expansion trajectory.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Crowdsourced security platforms originated in Silicon Valley during the early 2010s, with venture-backed startups pioneering the bug bounty model before regulatory mandates transformed the practice into enterprise procurement staple across North America, Europe, and Asia-Pacific.
United States
Federal agencies mandate FedRAMP-authorized platforms for crowdsourced security procurement, creating a protected contracting pool with stringent researcher clearance requirements. SEC cybersecurity disclosure rules pressure publicly traded companies to maintain continuous external vulnerability discovery programs. San Francisco and Washington D.C. host the densest concentrations of platform headquarters and federal contracting operations.
Germany
Industrial control system operators in automotive and manufacturing verticals drive demand for specialized ICS-focused researcher certification. The country's national cybersecurity authority enforces strict third-party security validation for critical infrastructure operators under the IT Security Act. Bavaria's automotive cluster around Munich and Stuttgart leads private bug bounty adoption among Tier-1 suppliers.
United Kingdom
Financial services firms in the City of London deploy crowdsourced programs to satisfy Prudential Regulation Authority operational resilience requirements. The National Cyber Security Centre promotes coordinated vulnerability disclosure frameworks across critical national infrastructure. London's fintech corridor generates concentrated demand for API security testing against Open Banking standards.
Japan
Industrial conglomerates and operational technology operators represent an underpenetrated vertical requiring specialized researcher pools. METI guidelines encourage proactive vulnerability disclosure for IoT and connected device manufacturers. Tokyo and Osaka house the primary enterprise security procurement decision centers for Asia-Pacific headquarters.
France
ANSSI, the national cybersecurity agency, mandates security evaluation procedures that increasingly reference crowdsourced validation for high-risk systems. Healthcare providers and medical device manufacturers face steep compliance ramps under MDR and EU AI Act conformity requirements. Paris and Lyon anchor the country's cybersecurity services procurement, with growing researcher communities in both metros.
Crowdsourced Security Market Vendor Landscape
The competitive structure tilts toward platform-scale specialists with established researcher networks and compliance certifications. Three to five vendors capture the majority of enterprise and government contract value, while regional specialists serve mid-market segments with localized program management. Two dominant archetypes emerge: FedRAMP-authorized federal contractors and European GDPR-specialized managed services providers. Competitive moves concentrate on researcher pool exclusivity arrangements and automated triage technology licensing.
Among North American platform operators, HackerOne, Inc., Bugcrowd, Inc., and Synack, Inc. occupy positions spanning the federal contracting and enterprise self-service segments. HackerOne represents the archetype of compliance-anchored platform scale, while Bugcrowd exemplifies managed service depth for regulated verticals. Synack sits within the hybrid technology-crowdsourcing intersection. European specialists including Intigriti BV and YesWeHack SAS anchor regional GDPR-compliant operations, with Intigriti exemplifying the continental managed service archetype. Detectify AB and Zerocopter NV represent Nordic-origin automation-first positioning, while Hacken OÜ anchors Eastern European researcher pool access. Cobalt Security, Inc. occupies the penetration-testing-as-a-service niche distinct from full bug bounty orchestration.
| Leading Market Players |
|---|
| Cobalt Security, Inc. |
| Intigriti BV |
| HackerOne, Inc. |
| Zerocopter NV |
| Detectify AB |
| Bugcrowd, Inc. |
| YesWeHack SAS |
| Hacken OÜ |
| Synack, Inc. |
| Others |
Supply Flow & Price Mechanics
Venture-backed platform operators with multi-stage funding cycles anchor supply-side discipline through researcher pool exclusivity contracts that simultaneously inflate talent acquisition costs and sustain premium pricing tiers for federal and enterprise clients. This financing structure concentrates pricing power among FedRAMP-authorized incumbents while forcing mid-tier competitors toward automated triage investments that compress margins.
Pricing Analysis
Three-tier pricing structure across premium, standard, and economy levels separates FedRAMP-authorized federal programs from enterprise managed services and self-service SaaS access. Certification level—specifically FedRAMP authorization and GDPR Article 44 adequacy determinations—drives price differentiation alongside researcher exclusivity arrangements. Cost compression in the standard tier is intensifying because AI-augmented scanning displaces human-only triage workflows. SMB buyers exhibit highest price sensitivity, while government agencies tolerate premium pricing for cleared researcher access.
Supply Chain Analysis
Researcher talent refurbishment flows through Eastern European and Asia-Pacific talent pipelines that platforms recycle into Western European and North American client programs via remote access infrastructure. Geographic supply concentrates in the United States, Germany, and Japan for cleared and ICS-certified researcher pools. Platform operations draw from cloud infrastructure providers, API integration middleware, and payment rails for bounty distribution. Single-source vulnerability in elite researcher geographic clusters creates bidding wars that inflate operating costs. Distribution runs through direct enterprise sales and federal contracting vehicles.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a geographic-arbitrage play where researcher talent costs in Eastern Europe and Latin America undercut Silicon Valley rates by substantial margins, while GDPR adequacy requirements restrict arbitrage into European client environments.
For Market Incumbents: Deploy researcher exclusivity lockups as the primary defensive lever against emerging AI-native scanning competitors. Anchor federal contracting positions through FedRAMP authorization maintenance while expanding automated triage licensing to mid-market clients. The threat of autonomous vulnerability discovery platforms displacing human-only programs demands accelerated CI/CD integration investments. For New Entrants and Emerging Players: EU AI Act conformity assessments in Germany and France open a window for specialized managed service offerings targeting healthcare and automotive verticals with mandatory third-party validation requirements. Industrial control system operators in Japan represent the most penetrable geography given underdeveloped ICS-focused researcher certification programs. A channel partnership strategy with European conformity assessment bodies accelerates credibility acquisition. For Investors and Strategic Acquirers: Valuations sit cheapest among regional GDPR-specialized platforms with established researcher communities but limited federal contracting access. Long-term viability hinges on AI-augmented triage technology ownership and clearance pipeline scalability. The signal to watch is FedRAMP authorization queue length as an indicator of competitive moat durability.| Strategic Initiative | Industry Significance |
|---|---|
| FedRAMP Authorization Acquisition | Unlocks protected federal contracting pool with 12-18 month researcher clearance timelines. |
| AI-Augmented Triage Integration | Compresses program launch timelines from weeks to hours for enterprise clients. |
| ICS Researcher Certification Program | Captures operational technology convergence demand in German automotive and Japanese industrial verticals. |
| GDPR Article 44 Adequacy Expansion | Enables researcher access to European enterprise environments from additional jurisdictions. |
| CI/CD Pipeline Native Ticketing | Reduces client mean-time-to-remediation through direct developer workflow integration. |
Methodological Framework
Multiple input streams — primary interviews with CISOs and federal procurement officers, platform operator executive discussions, and researcher community surveys — were reconciled against secondary validation from SEC cybersecurity disclosure filings, FedRAMP authorization databases, and EU AI Act conformity assessment body records. Bottom-up triangulation across vulnerability disclosure contract values and top-down reconciliation against enterprise security spending surveys anchored market sizing.
Data-stream reconciliation across service type, deployment model, end-user category, and regional regulatory framework generated volume and value outputs across the projection horizon. CAGRs derived from segment-level growth trajectories weighted by procurement pattern shifts toward cloud-based delivery and threat intelligence services. Researcher pool expansion rates and clearance pipeline velocity supplied industry-specific forecast inputs.
Revisions become necessary when FedRAMP authorization moratoria, GDPR adequacy determinations, or AI Act enforcement intensity shifts materialize beyond baseline assumptions. Practitioners should monitor researcher talent migration patterns and automated scanning technology licensing volumes for early signals.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
North America People Screening Market
Security and Surveillance
Middle East and Africa Cargo and Vehicle Screening Market
Security and Surveillance
Europe Cargo and Vehicle Screening Market
Security and Surveillance
North America Urban Security Screening Market
Security and Surveillance
Shock Sensor Market
Security and Surveillance
Home Security Solution Market
Security and Surveillance
Europe Security Testing Market
Security and Surveillance
Global Security Policy Management Market
Security and Surveillance
5G-Enhanced Surveillance Market
Security and Surveillance
Security Analytics Market
Security and Surveillance
Global Adaptive Security Market
Security and Surveillance
Europe Rockfall Radar Market
Security and Surveillance
Global X-Ray Security Scanner Market
Security and Surveillance
Global Acoustic Hailing Devices Market
Security and Surveillance
Global Bot Security Market
Security and Surveillance
India Electronic Security Market