
 APAC Security Testing Market | 2026-2036
APAC Security Testing Market Size, Share, and Industry Trends Forecast 2026-2036
APAC Security Testing Market Outlook
Enterprise-grade security certification is collapsing the gap between mid-market and top-tier testing capabilities across Asia-Pacific. Wipro leverages its India-centric delivery footprint to anchor penetration testing contracts for regional banks. Accenture differentiates through cloud-native security frameworks that integrate with hybrid infrastructure deployments. Cognizant competes aggressively on regulatory compliance testing, particularly for financial institutions navigating multi-jurisdiction data laws.
Security testing encompasses systematic evaluation of software, networks, and digital infrastructure to identify exploitable vulnerabilities before malicious actors can leverage them, employing methodologies that include automated static code analysis, dynamic runtime assessment, and simulated adversarial breach attempts. The primary purpose spans risk quantification, compliance verification, and defensive posture hardening for organizations operating connected systems. Penetration testing commands premium pricing due to specialized skill scarcity and high liability exposure, while cloud-based deployment models are gaining share as organizations migrate security operations to scalable, consumption-driven architectures. Network security applications retain the largest addressable base given legacy infrastructure pervasiveness, though IoT security represents the fastest-expanding segment as connected device proliferation outpaces embedded security design maturity.
India's Digital Personal Data Protection Act, Japan's Act on Protection of Personal Information amendments, and Singapore's Cybersecurity Act collectively mandate periodic third-party security assessments, creating structural demand for accredited testing services across these jurisdictions. BIS certification requirements and TRAI data security directives further tighten compliance obligations for domestic Indian enterprises handling sensitive consumer information. Stakeholders must evaluate whether to build captive security testing capabilities or deepen reliance on specialized vendors as regulatory complexity intensifies and cross-border data governance fragments.
Market Dynamics
India's Digital Personal Data Protection Act enforcement is compressing procurement cycles for security testing services as enterprises scramble to meet mandatory audit deadlines before penalties activate.
Growth Catalysts
- Digital payment fraud surge:Financial institutions across Southeast Asia are expanding security testing budgets to counter real-time transaction vulnerabilities in mobile wallet infrastructure.
- Japan's APPI amendments:Expanded third-party assessment obligations for cross-border data handlers are creating structural demand for accredited penetration testing services.
- Cloud migration acceleration:Hybrid infrastructure deployments across Australia's enterprise sector require continuous security validation that on-premise testing models cannot deliver.
Market Restraints
- Certified penetration tester scarcity:Specialized skill shortages in offensive security disciplines constrain service delivery velocity and inflate labor costs.
- Multi-jurisdiction compliance friction:Singapore's Cybersecurity Act, India's DPDP Act, and Japan's APPI create overlapping audit requirements that fragment vendor standardization.
- Legacy infrastructure technical debt:Decades-old mainframe and COBOL systems in regional banking cores resist automated vulnerability scanning integration.
Strategic Opportunities
- Indonesia's underpenetrated enterprise segment:Mid-market manufacturers and logistics operators lack mature security testing adoption, creating first-mover advantage for localized service providers.
- IoT device certification mandates:Australia's IoT Code of Practice and similar frameworks across the region will mandate pre-market security assessment for connected hardware.
- DevSecOps toolchain convergence:Integration of static application security testing with CI/CD pipelines enables subscription-based recurring revenue models.
Industry Challenges
- Offensive security talent pipeline gaps:Universities across APAC produce insufficient graduates with exploit development and adversarial simulation capabilities.
- Accreditation timeline compression:CREST and OSCP certification backlogs delay consultant deployment for time-sensitive client engagements.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | APAC Security Testing Market |
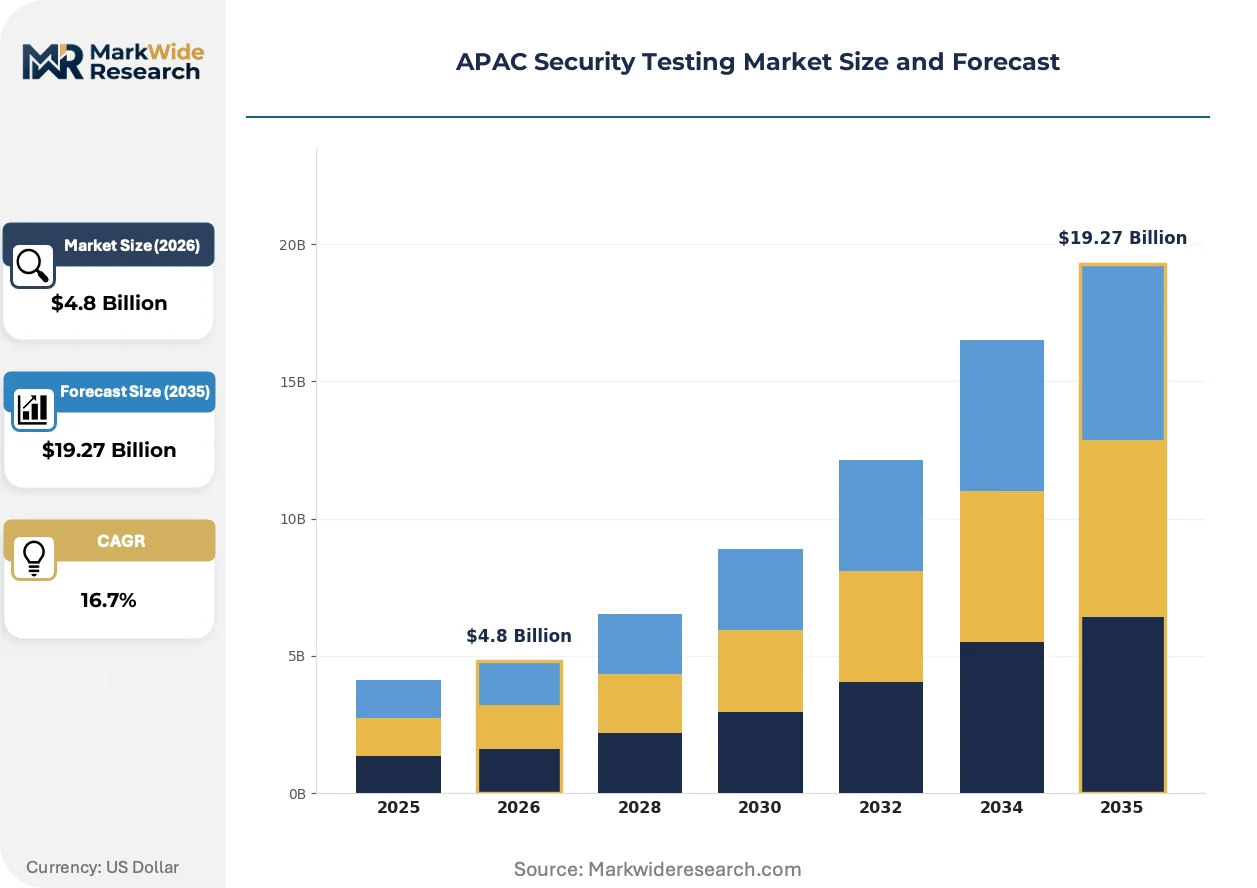
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $19.27 Billion |
| CAGR (2026 – 2036) | 16.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Test Type: Dynamic Testing, Static Testing, Penetration Testing, Regulatory Compliance Testing Deployment Model: On-Premise, Cloud-Based, Hybrid, Managed Services End User: Financial Institutions, Government Agencies, Healthcare Providers, E-Commerce Companies Application: Web Application Security, Network Security, Mobile Application Security, IoT Security |
| Companies Covered | Wipro, Capgemini, HCL Technologies, Intertek, Qualitest, Tata Consultancy Services, Cognizant, Accenture, Infosys, Others |
| Regions Covered | Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
APAC Security Testing Market Strategic Shifts
Artificial intelligence is reshaping vulnerability detection workflows while regulatory deadlines compress testing cycles across the region's fragmented compliance landscape.
Automated attack surface management platforms are fragmenting traditional penetration testing engagement models. Mid-market enterprises in Thailand and Vietnam now subscribe to continuous external reconnaissance rather than commissioning annual point-in-time assessments. This shift is compressing pricing power for project-based security consultancies while expanding total addressable volume for SaaS-native vendors.
Singapore's Cybersecurity Act amendments now mandate incident reporting timelines that render quarterly testing cycles structurally inadequate. Financial services and critical infrastructure operators must demonstrate continuous control validation or face operational license suspension. Australia's banking sector has responded by embedding security testing automation directly into operational risk frameworks.
Enterprise buyers now unbundle compliance validation from remediation services, selecting specialized auditors for regulatory attestation while retaining separate vendors for vulnerability patching. This pattern is most pronounced among Japanese automotive and electronics manufacturers with complex multi-site supply chains. Procurement teams negotiate fixed-fee certification contracts while purchasing remediation capacity on consumption-based terms.
APAC Security Testing Market Segmentation
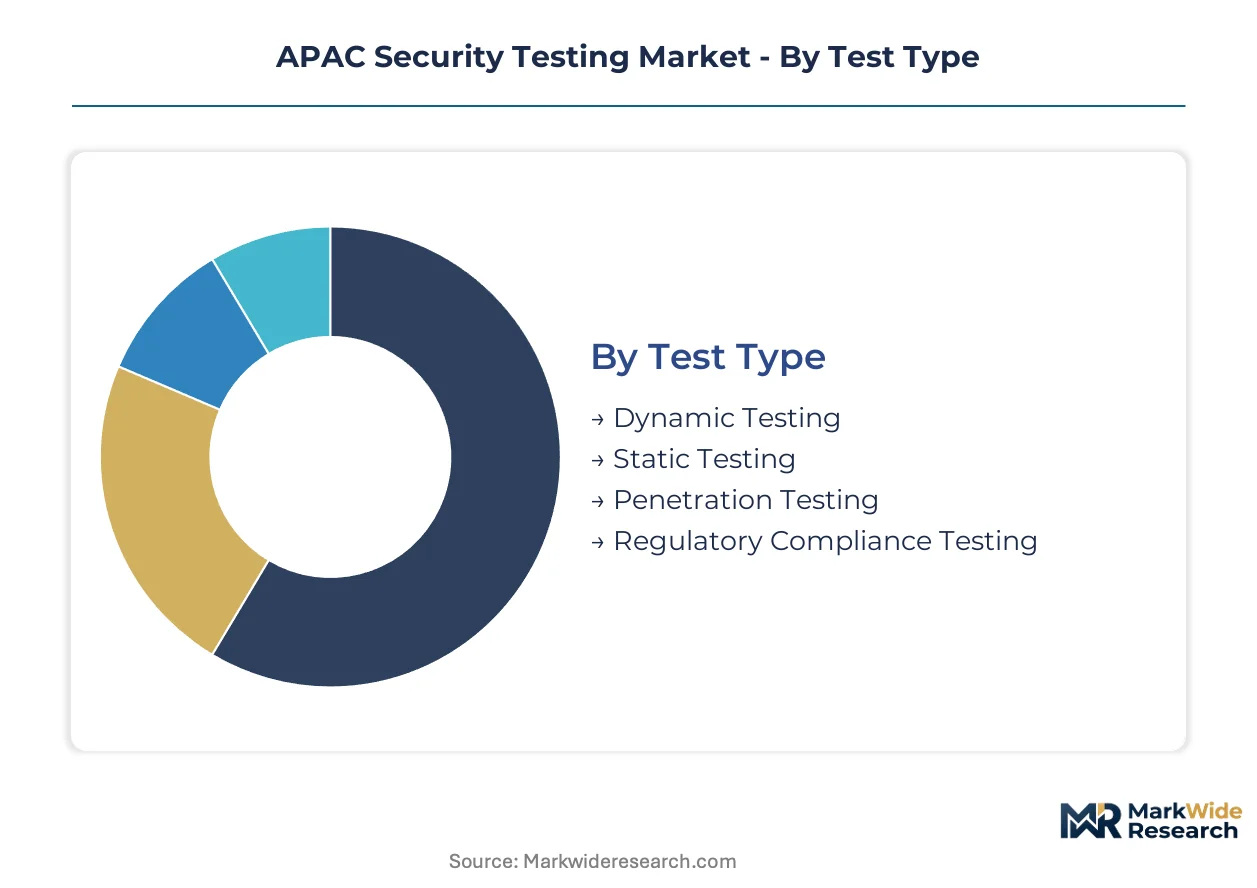
Security testing procurement across Asia-Pacific fragments across technical methodologies, infrastructure architectures, and regulatory mandates. Each segmentation dimension carries distinct pricing dynamics and vendor specialization patterns that shape competitive positioning.
Test Type:
Regulatory differentiation separates commoditized scanning from premium attestation services across India's DPDP Act, Japan's APPI amendments, and Singapore's Cybersecurity Act enforcement timelines.
- Penetration Testing:Simulated adversarial breach attempts by certified offensive security specialists command premium pricing due to OSCP and CREST certification scarcity. Financial institutions in Mumbai and Singapore commission these services under mandatory third-party assessment clauses.
- Regulatory Compliance Testing:Structured audit frameworks verify alignment with jurisdiction-specific data protection mandates. India's BIS certification requirements and TRAI directives create structural demand for accredited attestation among domestic enterprises handling consumer financial data.
- Dynamic Testing:Runtime vulnerability assessment during application execution identifies exploitable flaws in operational environments.
- Static Testing:Source code analysis without execution detects architectural weaknesses early in development pipelines.
Penetration testing handles the majority of throughput; regulatory compliance testing is the fastest mover on share.
Deployment Model:
Cost tier stratification separates capital-intensive infrastructure from consumption-driven alternatives as Australian enterprises accelerate hybrid cloud migration.
- Cloud-Based:Scalable, subscription-driven architectures enable continuous security validation without on-premise hardware investment. Australian banking operators embed these capabilities directly into operational risk frameworks.
- Managed Services:Outsourced security operations centers deliver 24/7 monitoring and incident response through specialized provider ecosystems. Mid-market manufacturers in Thailand and Vietnam adopt these models to bypass internal capability gaps.
- Hybrid:Mixed infrastructure deployments balance sensitive data retention on-premise with scalable cloud analytics.
- On-Premise:Legacy-controlled environments persist in regional banking cores with decades-old mainframe dependencies.
Cloud-based deployments command expanding budget allocation; managed services are climbing the fastest among mid-market adopters.
End User:
Application specificity drives divergent testing intensity as digital payment fraud surges reshape procurement priorities.
- Financial Institutions:Banks, insurers, and payment processors face the most stringent regulatory obligations. Southeast Asian mobile wallet operators commission continuous testing to counter real-time transaction vulnerabilities.
- Government Agencies:Critical infrastructure operators under Singapore's Cybersecurity Act amendments must demonstrate continuous control validation or face operational license suspension.
- Healthcare Providers:Patient data protection mandates drive periodic assessment requirements for hospital networks and telemedicine platforms.
- E-Commerce Companies:Transaction volume exposure and consumer trust dependencies motivate security investment among online retail operators.
Financial institutions anchor the largest addressable base; government agencies are expanding most quickly under mandatory audit compression.
Application:
Maturity gaps between legacy infrastructure and emerging attack surfaces fragment vendor specialization and pricing power.
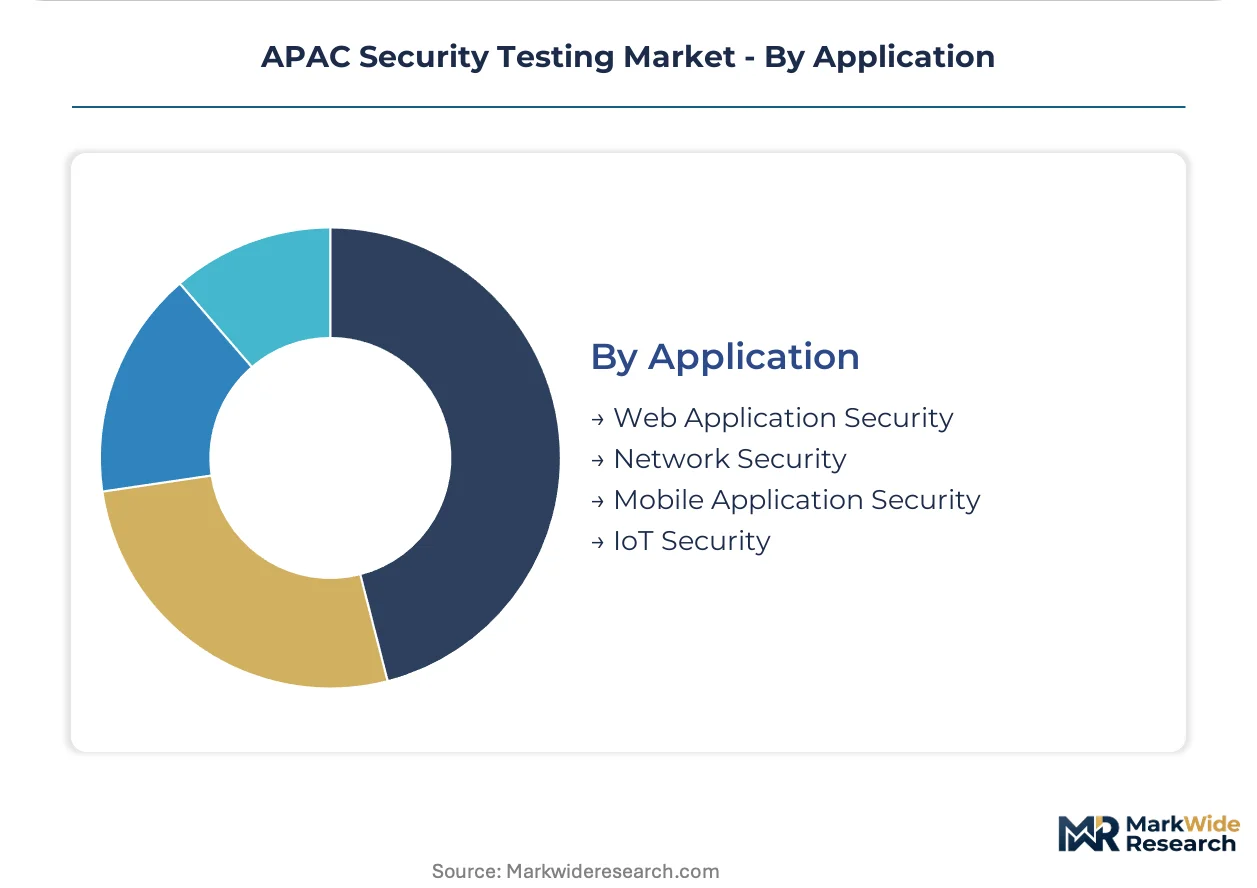
- Network Security:Perimeter and internal infrastructure assessment retains the largest installed base given legacy system pervasiveness in regional banking cores. Decades-old COBOL systems resist automated vulnerability scanning integration.
- IoT Security:Connected device proliferation outpaces embedded security design maturity. Australia's IoT Code of Practice mandates pre-market security assessment for connected hardware entering commercial distribution.
- Web Application Security:Browser-accessible platform assessment addresses the dominant customer-facing attack surface.
- Mobile Application Security:iOS and Android-specific testing targets the primary channel for digital payment and banking engagement.
Network security handles the majority of throughput; IoT security is gaining share fastest under emerging certification mandates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Export-import dynamics in security testing services remain balanced across the Asia-Pacific, with India and Singapore serving as net service exporters while Australia and Japan represent premium import destinations for specialized penetration testing capabilities.
India
Domestic IT services firms and global consultancies compete intensely for enterprise contracts in Mumbai, Bangalore, and Hyderabad. The Digital Personal Data Protection Act compels mandatory security audits, compressing procurement cycles as organizations scramble to meet enforcement deadlines. Technology hubs in Karnataka and Maharashtra anchor the highest concentration of accredited testing laboratories and certified offensive security specialists.
Singapore
Financial institutions and critical infrastructure operators face operational license suspension risks under Cybersecurity Act amendments mandating continuous control validation. The city-state's regulatory framework creates structural demand for accredited third-party assessment services. Enterprise buyers in Singapore's central business district unbundle compliance validation from remediation, selecting specialized auditors for regulatory attestation.
Japan
Automotive and electronics manufacturers with complex multi-site supply chains drive premium pricing for regulatory compliance testing. Act on Protection of Personal Information amendments expand third-party assessment obligations for cross-border data handlers. Industrial clusters in Nagoya and Osaka prefectures embed security testing automation directly into operational risk frameworks.
Australia
Banking operators commission cloud-native security frameworks that integrate with hybrid infrastructure deployments. The IoT Code of Practice mandates pre-market security assessment for connected hardware entering commercial distribution. Sydney and Melbourne enterprise sectors accelerate continuous security validation that on-premise testing models cannot deliver.
Indonesia
Mid-market manufacturers and logistics operators lack mature security testing adoption, creating first-mover advantage for localized service providers. Jakarta's expanding digital economy exposes transaction volume vulnerabilities that mobile wallet operators must address through systematic infrastructure evaluation. Domestic enterprises handling consumer financial data face tightening compliance obligations under evolving national data protection frameworks.
APAC Security Testing Market Competitive Environment
Concentration sits with diversified IT services conglomerates that leverage scale and regulatory expertise to capture enterprise mandates. The vendor base organizes across three tiers: global consultancies with cloud-native frameworks, India-centric delivery specialists, and boutique penetration testing firms with CREST accreditation. Strategic differentiation centers on DevSecOps toolchain integration and managed services capacity expansion. Competitive moves emphasize geographic footprint extension into underpenetrated Southeast Asian markets and vertical specialization for financial services compliance.
Among India-based delivery specialists, Wipro, Tata Consultancy Services, and HCL Technologies exemplify the archetype of scale-driven penetration testing providers leveraging domestic talent pools to anchor regional banking contracts. These entities occupy positions within the mid-tier segment where offshore delivery models compress project economics while maintaining OSCP-certified consultant deployment. Accenture and Cognizant represent the global consultancy tier, anchoring premium positioning through hybrid infrastructure integration capabilities and multi-jurisdiction regulatory expertise across Singapore, Japan, and Australia mandates.
| Leading Market Players |
|---|
| Wipro |
| Capgemini |
| HCL Technologies |
| Intertek |
| Qualitest |
| Tata Consultancy Services |
| Cognizant |
| Accenture |
| Infosys |
| Others |
Value Chain & Pricing Dynamics
Ninety-day certification backlogs for CREST and OSCP credentials concentrate pricing power among accredited consultancies while compressing margins for project-based penetration testing engagements. This lead-time friction shapes how buyers structure procurement—either absorbing premium rates for certified talent or accepting longer deployment windows that risk regulatory deadline slippage under India's DPDP Act and Singapore's Cybersecurity Act enforcement timelines.
Pricing Analysis
Financial institutions anchor subscription-based recurring revenue models for continuous attack surface management, displacing annual point-in-time assessments. Price differentiation hinges on certification tier—OSCP and CREST-accredited specialists command substantial premiums over uncertified resources—and geographic delivery cost, with India-centric delivery compressing project economics relative to onshore Australian or Japanese deployment. Cost compression in mid-market penetration testing is intensifying because automated SaaS reconnaissance platforms fragment traditional consultancy pricing power. Mid-market manufacturers in Thailand and Vietnam exhibit highest price sensitivity, while Singaporean critical infrastructure operators under operational license suspension risks show least sensitivity to compliance attestation fees.
Supply Chain Analysis
Just-in-time talent deployment dominates the security testing supply chain, with consultancies maintaining bench depth of certified offensive security specialists rather than strategic stockpiles of hardware or software licenses. Geographic supply concentration centers on India, Singapore, and Australia, where domestic IT services firms and global consultancies compete for enterprise mandates. The supply chain draws from specialized skill pipelines—university cybersecurity programs, military veteran transitions, and bootcamp certifications—rather than raw material inputs. Single-source vulnerability in CREST and OSCP accreditation backlogs constrains service delivery velocity. Distribution runs through direct enterprise sales teams and hyperscaler marketplace integrations for cloud-native security validation tools.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The acute shortage of exploit development and adversarial simulation capabilities creates structural bottlenecks that reshape competitive positioning across the Asia-Pacific security testing landscape. This talent pipeline gap favors organizations that can secure, develop, or acquire certified offensive security expertise at scale.
For Market Incumbents: Secure CREST and OSCP certification pipelines through captive training academies and veteran recruitment programs to defend against boutique penetration testing firms poaching accredited consultants. Deepen vertical integration into DevSecOps toolchain development, embedding static application security testing directly into CI/CD platforms to lock in subscription recurring revenue and displace point-in-time project competitors. For New Entrants and Emerging Players: Lead with Indonesia's underpenetrated mid-market manufacturing and logistics segment, where localized service providers can establish first-mover advantage before global consultancies extend geographic footprint. Target Australia's IoT Code of Practice compliance mandates for connected hardware pre-market assessment, a segment where established players lack specialized device security expertise. Pursue channel partnerships with hyperscaler marketplaces to bypass direct enterprise sales infrastructure requirements. For Investors and Strategic Acquirers: Carve-out targets emerge from diversified IT services conglomerates seeking to divest non-core security testing units amid margin pressure from SaaS-native competitors. Long-term viability rests on recurring revenue mix and DevSecOps integration depth rather than project-based penetration testing volume. Acquisition candidates with managed services capacity expansion and hybrid cloud security framework capabilities offer defensive positioning. Watch CREST certification backlog duration as inflection indicator—compression signals talent supply recovery and pricing power erosion, while extension validates scarcity-premium sustainability.| Strategic Initiative | Industry Significance |
|---|---|
| Managed Services Capacity Expansion | 24/7 security operations centers address mid-market capability gaps in Thailand and Vietnam. |
| DevSecOps Toolchain Integration | Embedding SAST into CI/CD pipelines enables subscription-based recurring revenue models. |
| CREST Certification Pipeline Investment | Captive training academies secure scarce offensive security talent against boutique poaching. |
| IoT Security Assessment Specialization | Australia's IoT Code of Practice mandates pre-market certification for connected hardware. |
| Geographic Footprint Extension | Indonesia's underpenetrated enterprise segment offers first-mover advantage for localized providers. |
Study Parameters
Cross-validation between primary interviews with CISOs, security procurement officers, penetration testing team leads, and regulatory compliance directors and secondary validation through SEC filings, hyperscaler security marketplace disclosures, and CREST certification registry data anchors the qualitative findings. Bottom-up triangulation aggregates service line revenue disclosures from IT services conglomerates with top-down demand modeling from regulatory mandate enforcement timelines across India, Singapore, Japan, and Australia.
Sensitivity analysis across the projection horizon tests forecast robustness against penetration tester certification backlog duration, cloud migration velocity in Australian banking, and IoT device certification mandate expansion. Segmentation dimensions modeled include test type, deployment model, end-user vertical, and application surface, with CAGRs derived from regulatory deadline compression effects and continuous security validation adoption curves. Industry-specific inputs incorporate DPDP Act enforcement phase transitions and Cybersecurity Act amendment implementation timelines.
The analysis sits within stated boundaries; outcomes outside sustained regulatory enforcement intensity and cloud-native security framework adoption would require recalibration. Forecasts reflect assumptions regarding certification pipeline expansion, hyperscaler marketplace penetration, and mid-market SaaS displacement of project-based engagements. Revision becomes warranted when CREST and OSCP certification backlog duration crosses twelve-month thresholds or when automated attack surface management platform pricing compresses mid-market penetration testing margins beyond sustainable levels.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Europe Security Assurance Market
Security and Surveillance
Asia-Pacific Urban Security Screening Market
Security and Surveillance
Home Security Sensors Market
Security and Surveillance
North America Urban Security Screening Market
Security and Surveillance
Threat Detection Systems Market
Security and Surveillance
Europe Cargo and Vehicle Screening Market
Security and Surveillance
Residential Security Market
Security and Surveillance
Integrated Security Solutions Market
Security and Surveillance
Europe Urban Security Screening Market
Security and Surveillance
Global Security Advisory Services Market
Security and Surveillance
Europe Security Testing Market
Security and Surveillance
Global Firearm Sight Market
Security and Surveillance
Consumer Security Market
Security and Surveillance
Global Wireless Doorbells Market
Security and Surveillance
Europe Security Services Market
Security and Surveillance
Latin America Electronics Security Market